ntqueueapcthreadex-ntdll-gadget-injection

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…

CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…

A productionized greedy coordinate gradient (GCG) attack tool for large language models (LLMs)

Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment

See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)

Purpleteam scripts simulation & Detection - trigger events for SOC detections

PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…

reverse engineering SynthID for text

Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.

Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.

Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org

Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post

Crystal Palace library for proxying Nt API calls via the Threadpool

Modern PIC implant for Windows (64 & 32 bit)

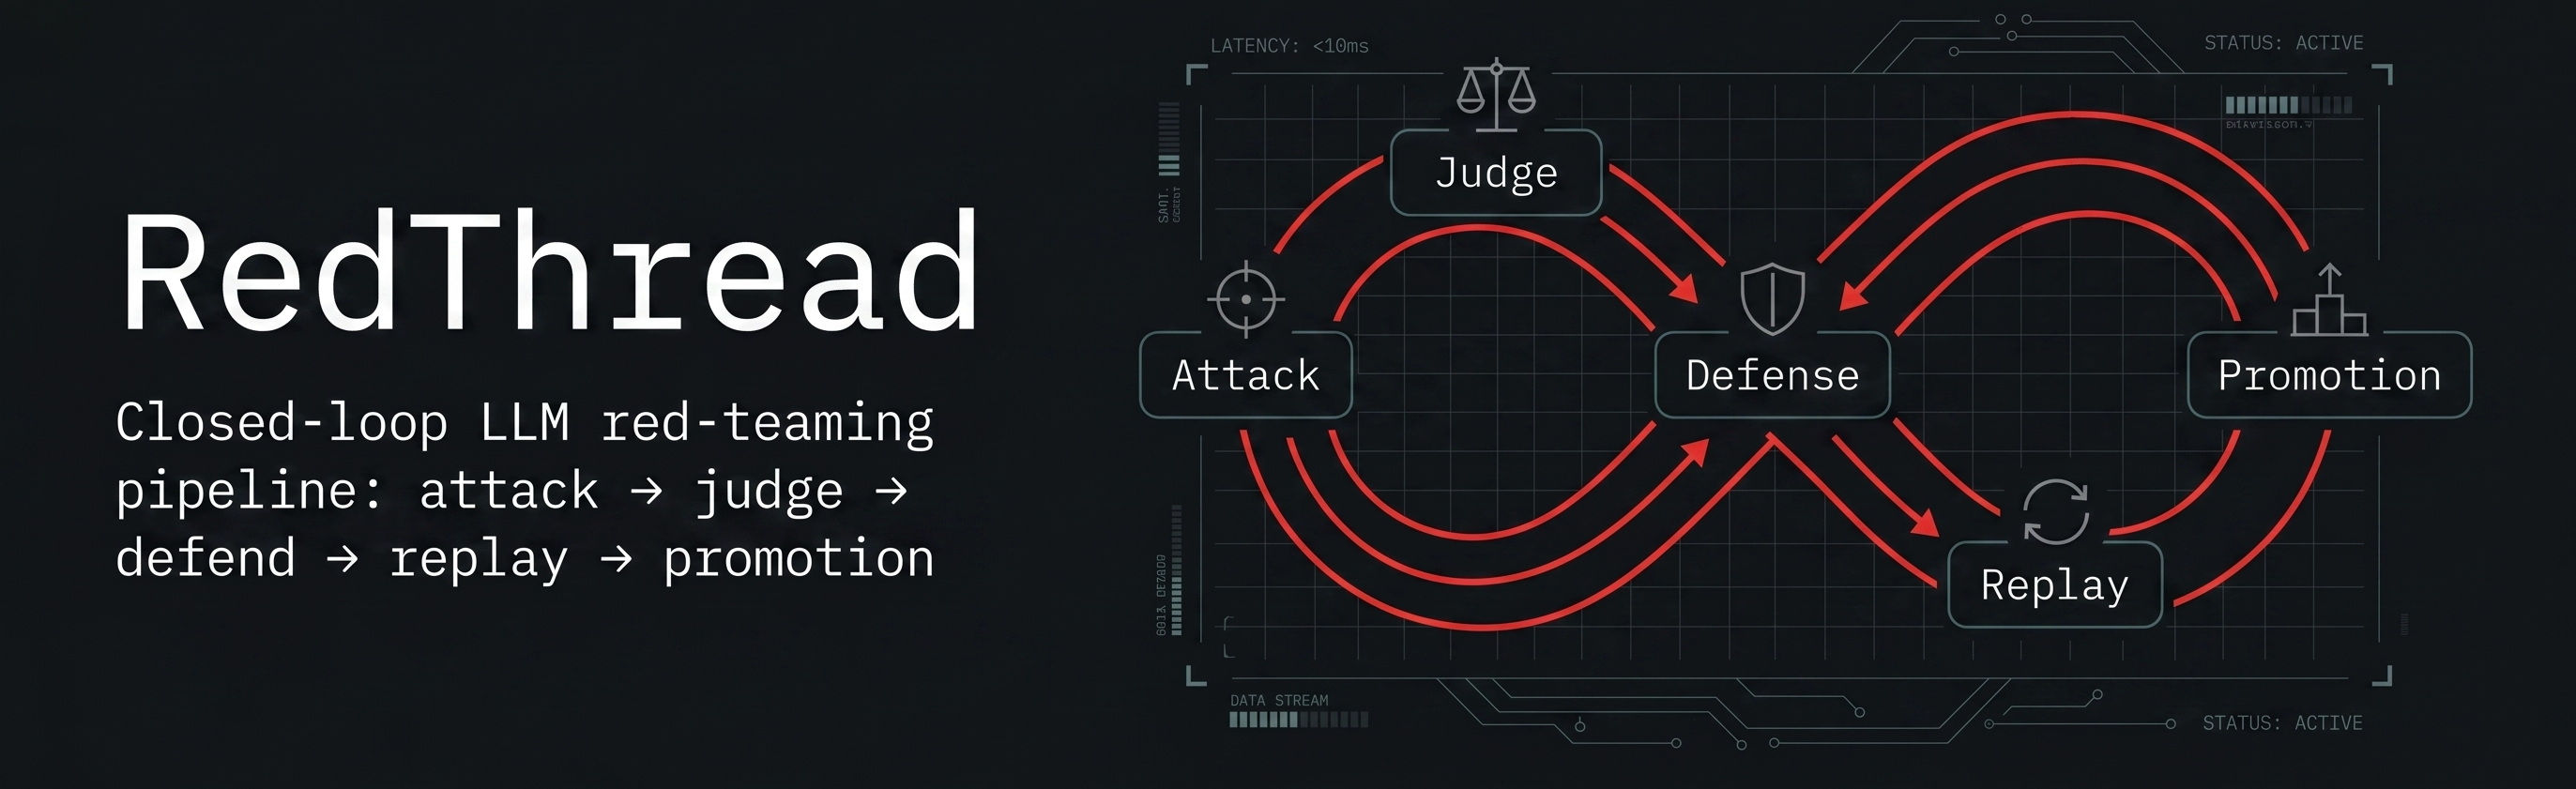
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…

A new simple and powerfull packer for malware

PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…

PISmith: Reinforcement Learning-based Red Teaming for Prompt Injection Defenses