
Voidgate
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
adversarial-attackdebuggersids-ips-evasion+3
598
vxcrypt0r/voidgateA technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 keyvaluesoftwaresystems/agent-opfor
Open-source adversary emulation for AI agents and MCP servers.
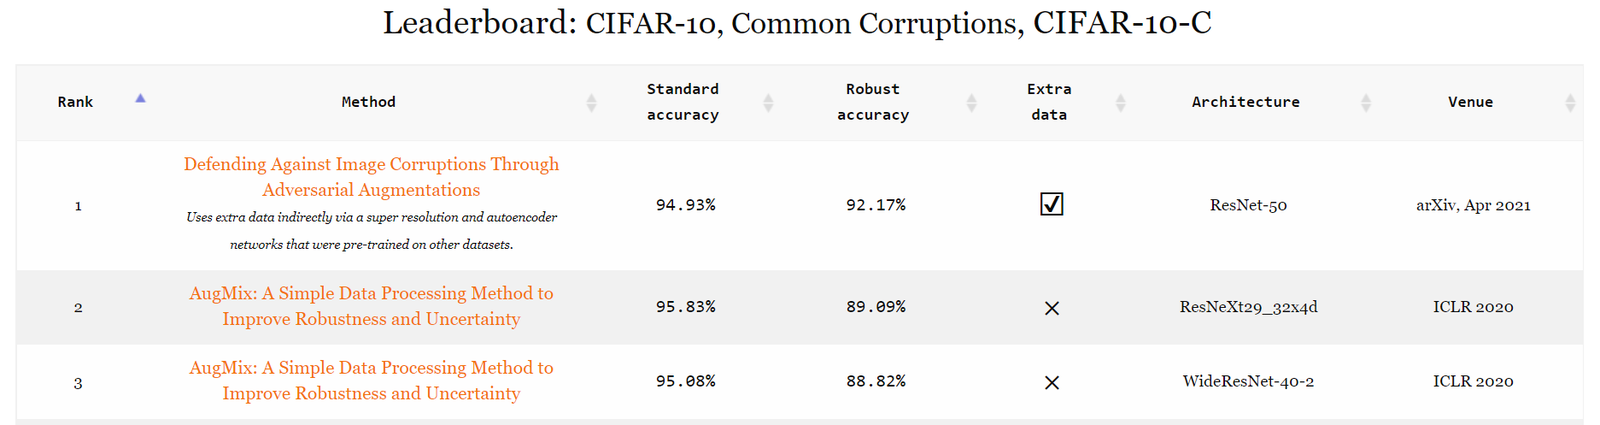 robustbench/robustbench
Standardized adversarial robustness benchmark with a public leaderboard and downloadable model zoo for evaluating ML models against Lp attacks and…
 sbasu7241/aws-threat-simulation-and-detection
Playing around with Stratus Red Team (Cloud Attack simulation tool) and SumoLogic
 praetorian-inc/augustus
LLM security testing framework for detecting prompt injection, jailbreaks, and adversarial attacks — 190+ probes, 28 providers, single Go binary
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
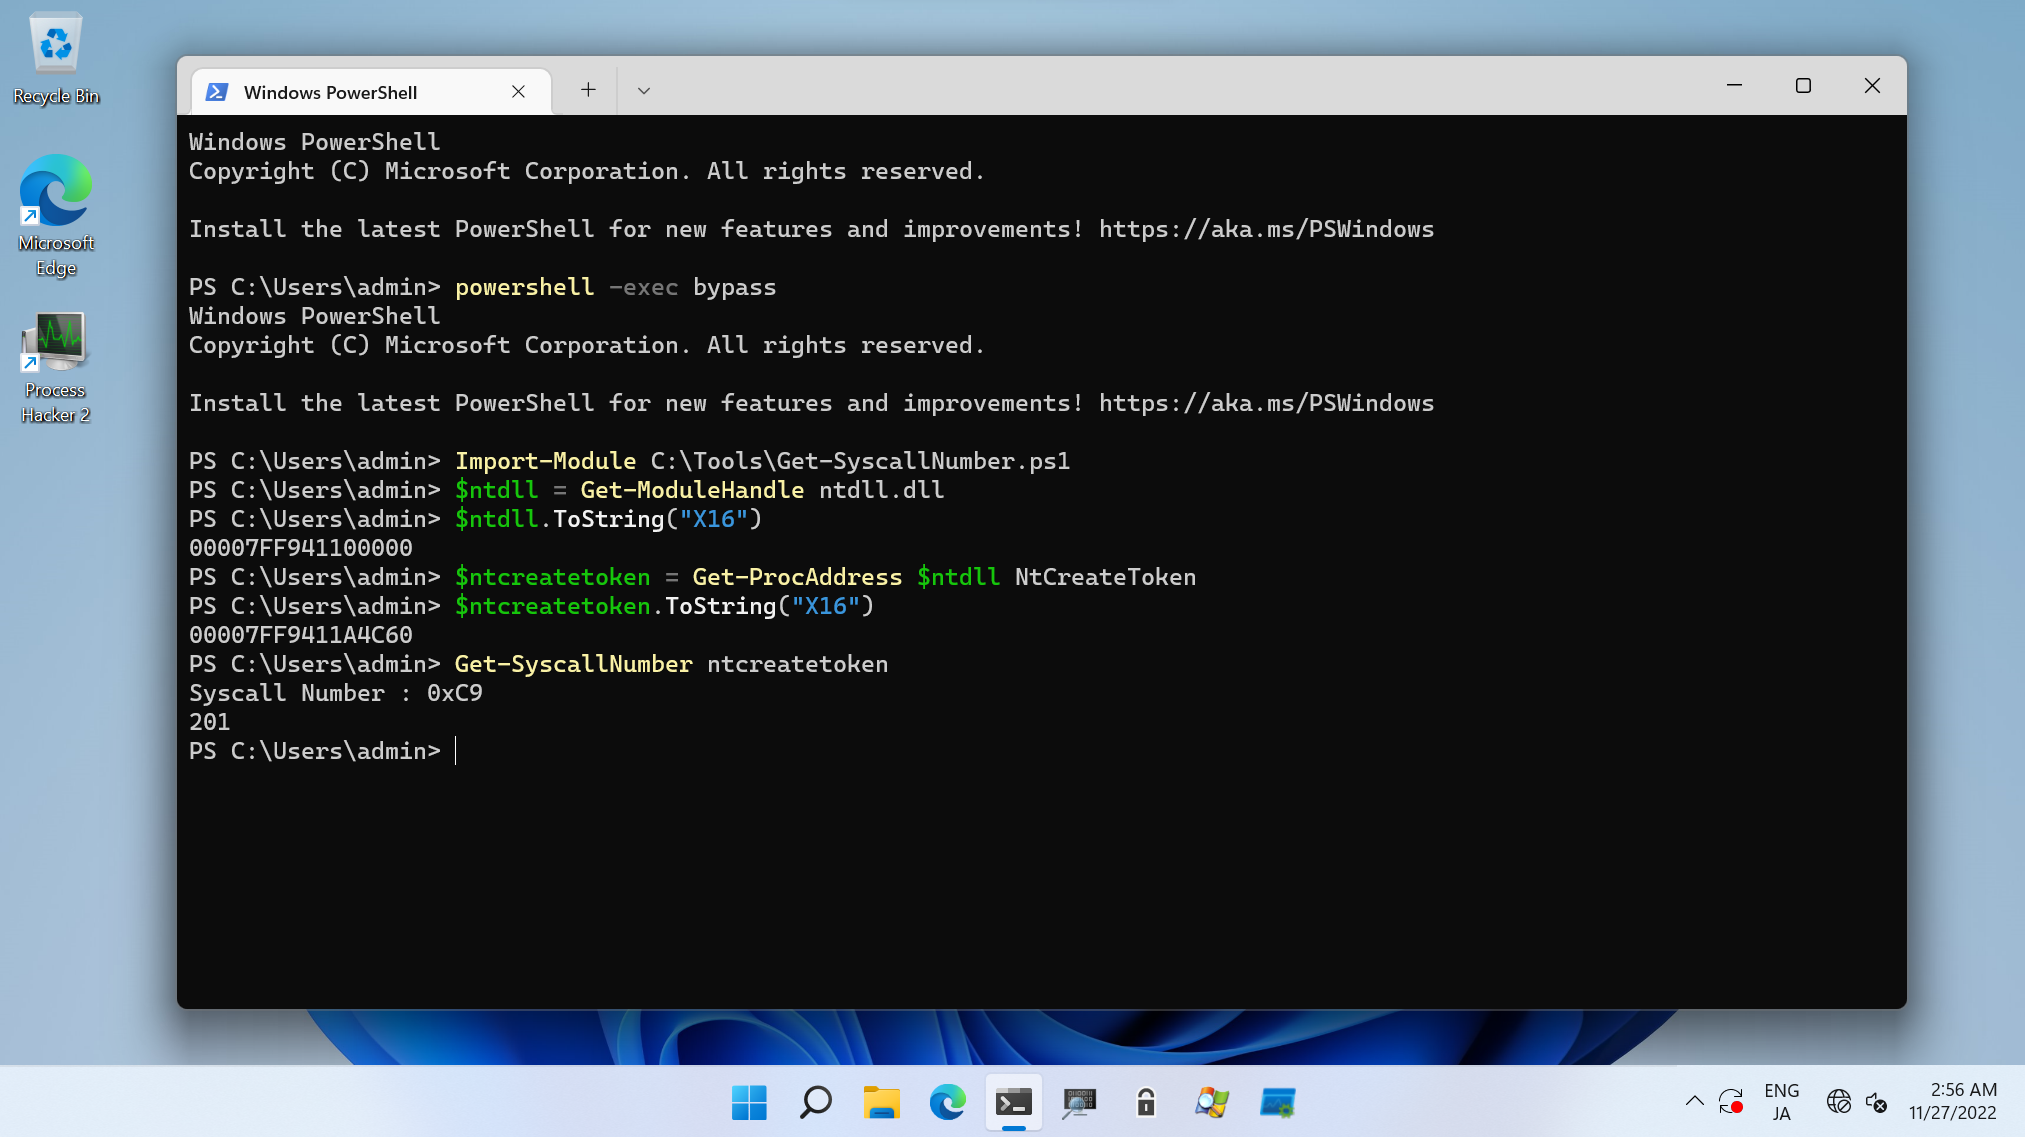 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
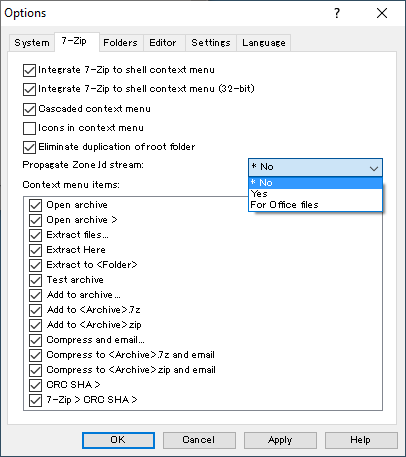 nmantani/archiver-motw-support-comparison
Compares Windows archiver support for Mark of the Web propagation, helping teams assess which tools preserve MOTW and mitigate macro-based malware…
 trinib/zorg-jailbreak-prompt-text
Bypass restricted and censored content on AI chat prompts 😈
 doctoreww/evilfonttool
A font-based deception tool for red teaming, security research, and whatever else.
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 saadahla/unhookingpatch
Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
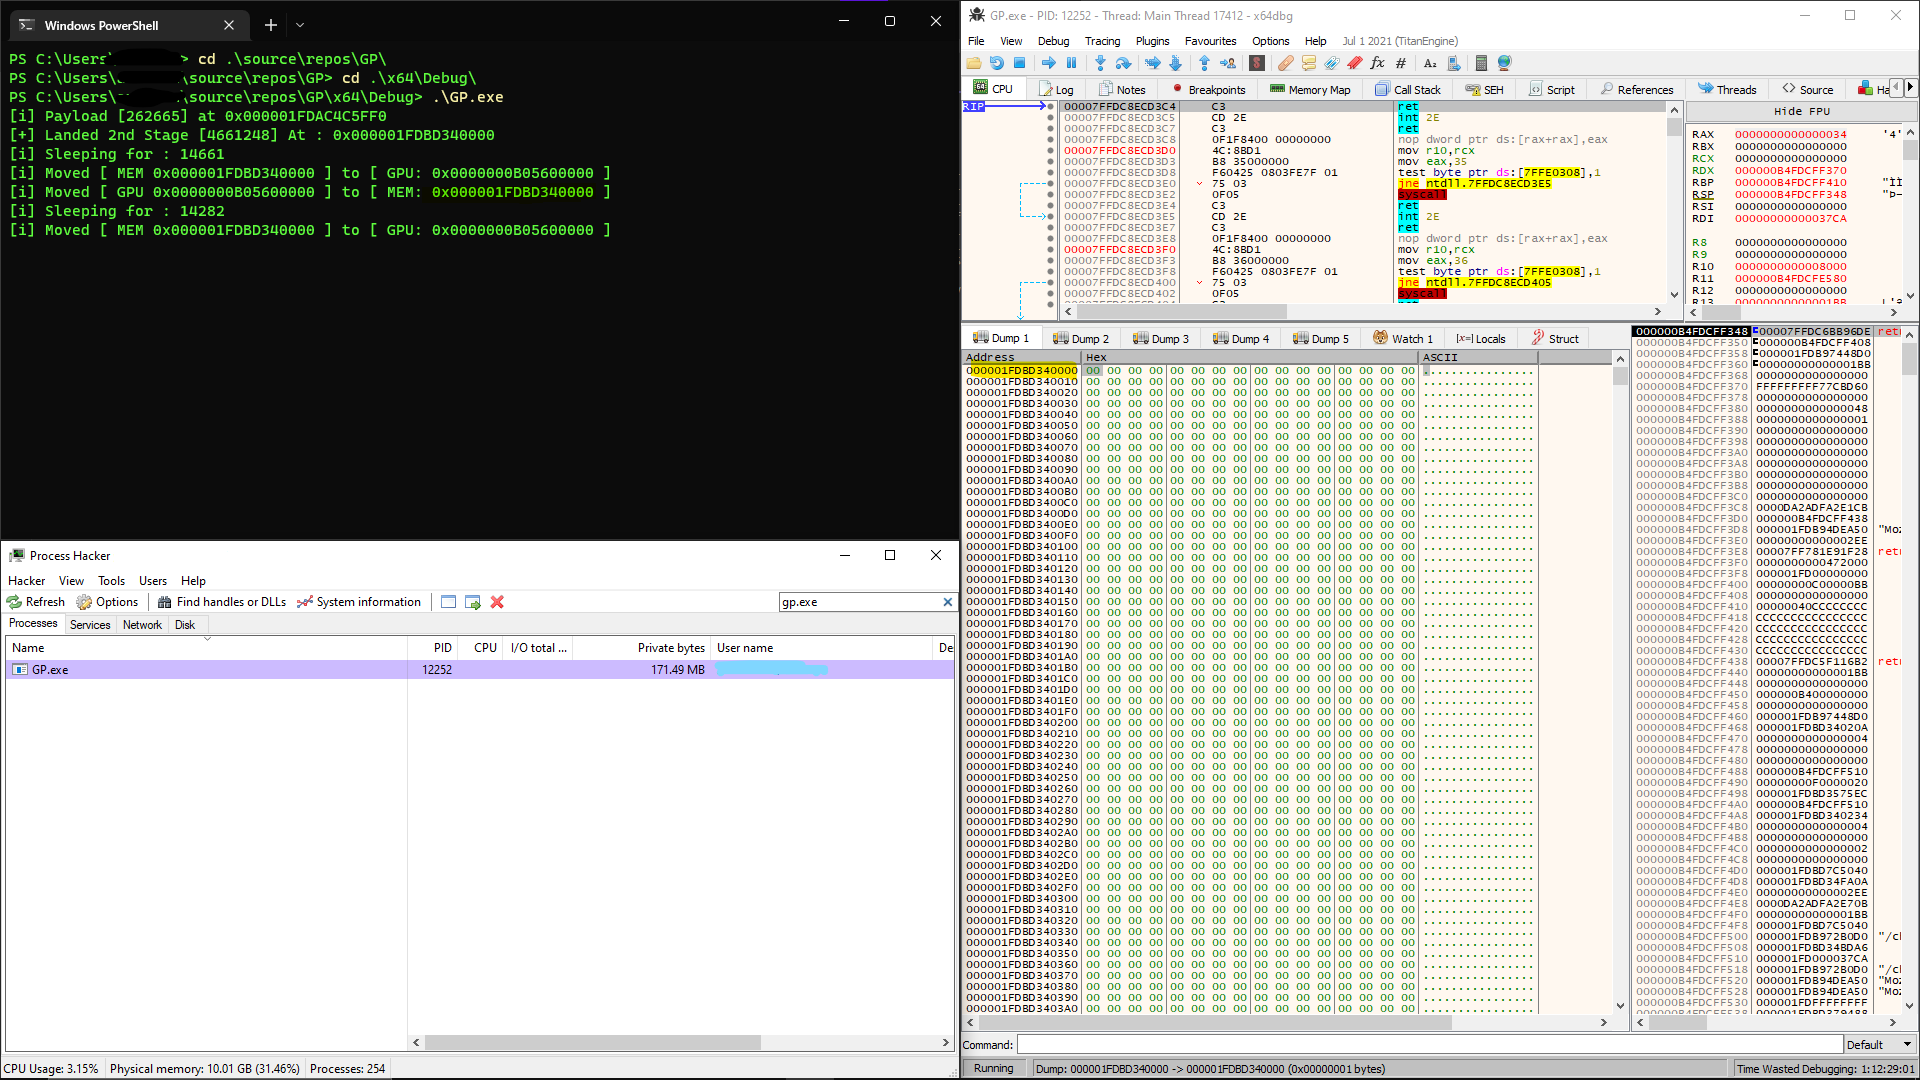 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…
 xforcered/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 alteredsecurity/disable-tamperprotection
A POC to disable TamperProtection and other Defender / MDE components