
RingReaper
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
adversarial-attackcommand-and-controldata-exfiltration+5
383
matheuzsecurity/ringreaperLinux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 asset-group/ghostsplice
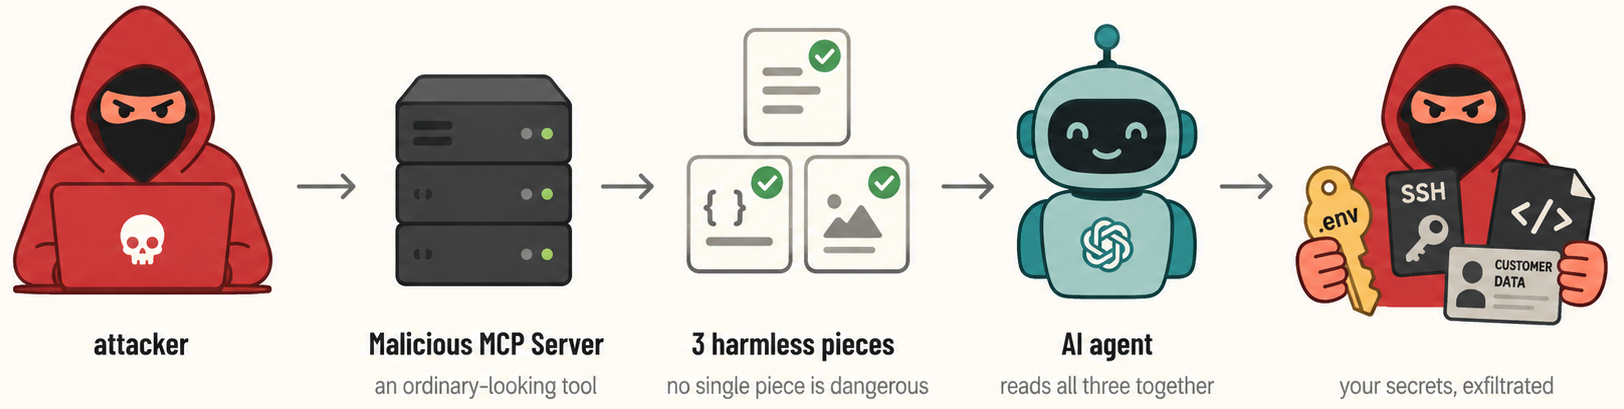
Ghostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
 hanxi19/black_hole_attack_for_vector_database
Research implementation of the Black-Hole Attack that poisons vector database indexes via centrality-driven hubness, with FAISS pipelines and…
 jiep/offensive-ai-compilation
A curated list of useful resources that cover Offensive AI.
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 zeromemoryex/terminator
Reproducing Spyboy technique to terminate all EDR/XDR/AVs processes
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
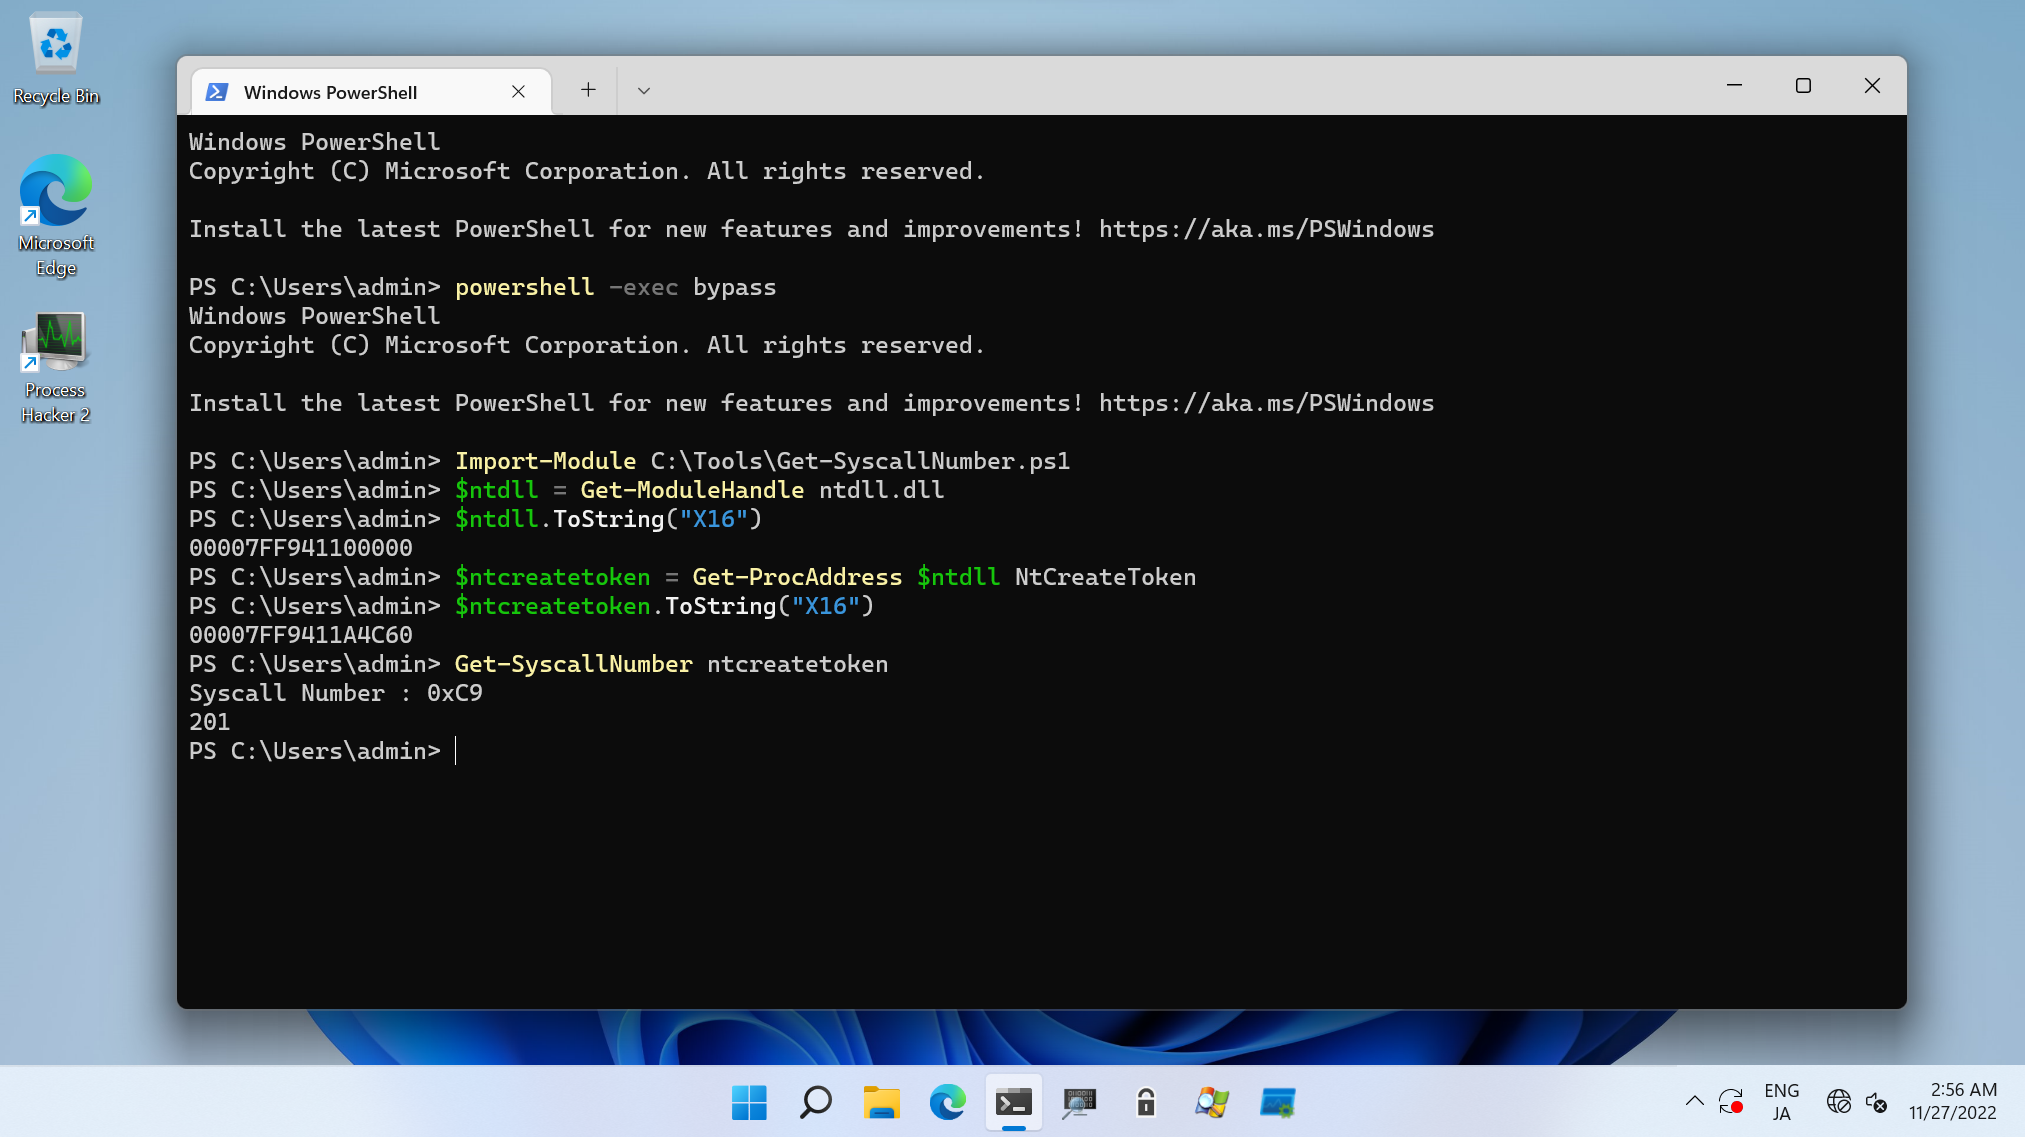 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
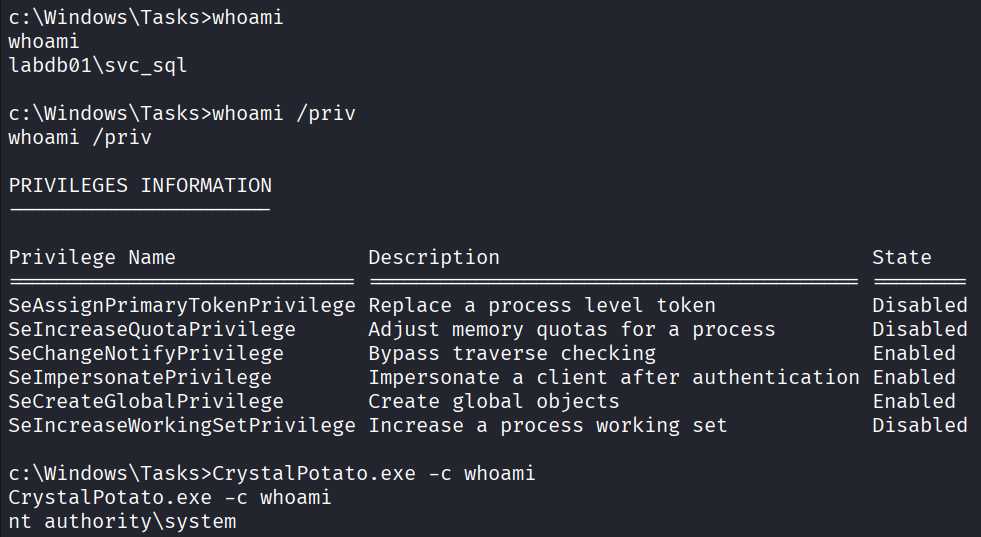 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 aloshdenny/reverse-synthid-text
reverse engineering SynthID for text
 deepinstinct/shimme
PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…
 vozzie/uacscript
Windows 7 UAC Bypass Vulnerability in the Windows Script Host
 s3cur3th1ssh1t/nimshellcodefluctuation
ShellcodeFluctuation PoC ported to Nim
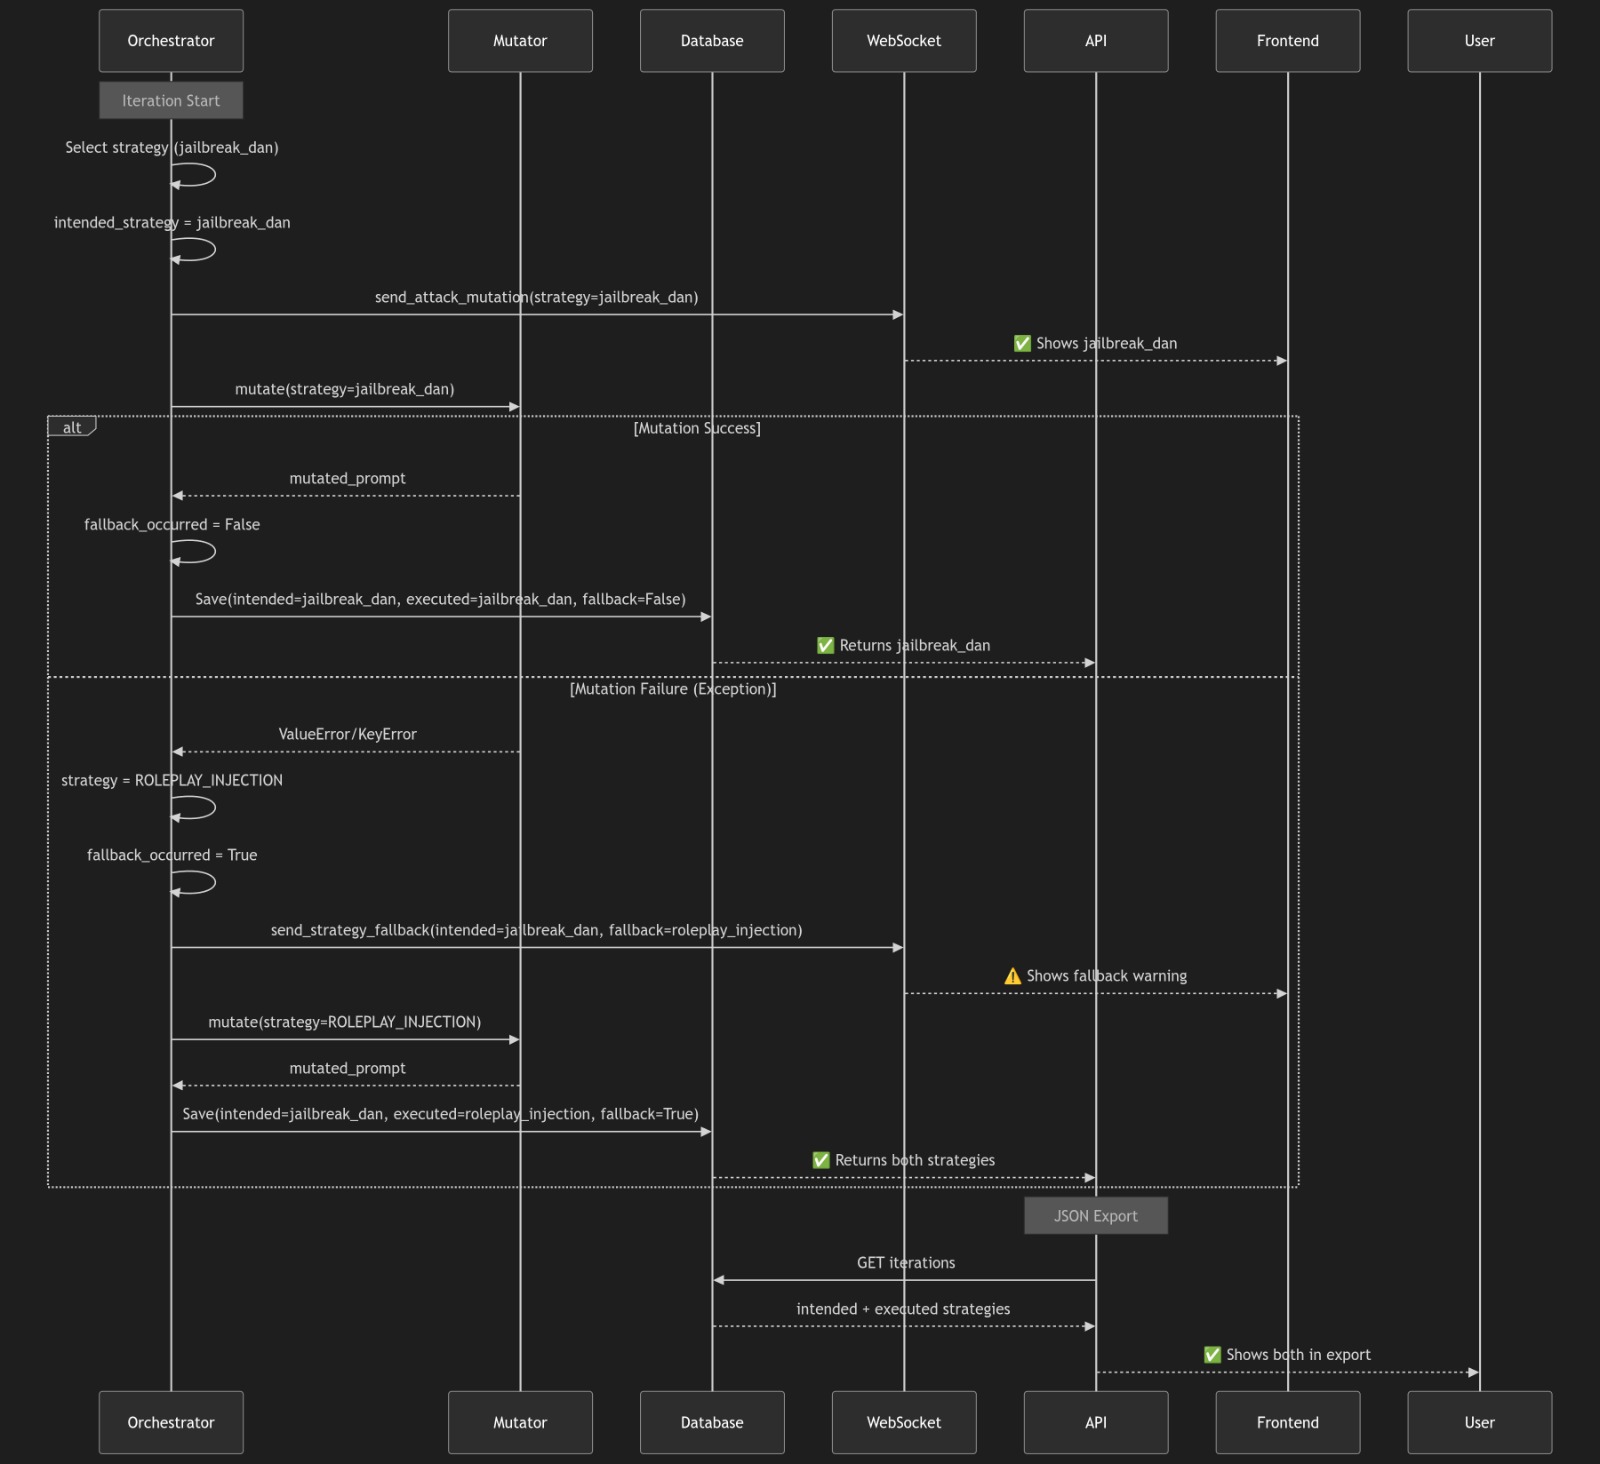 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation