
EDRSilencer
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
adversarial-attackids-ips-evasionpost-exploitation+1
1.9k
netero1010/edrsilencerA tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
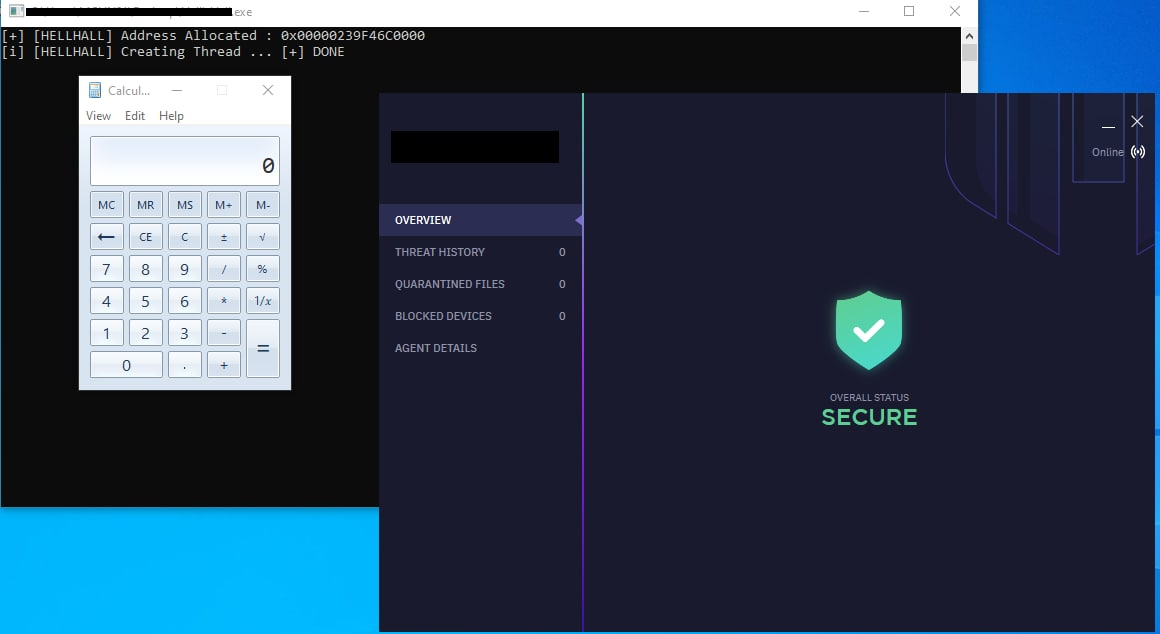 maldev-academy/hellhall
Performing Indirect Clean Syscalls
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 kudaes/unwinder
Call stack spoofing for Rust
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
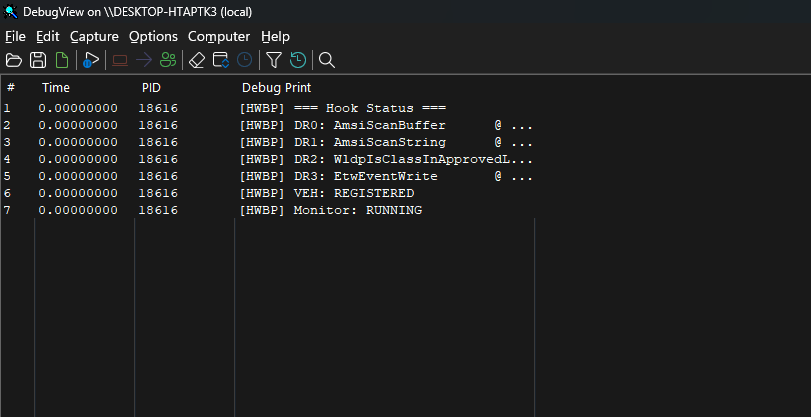 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
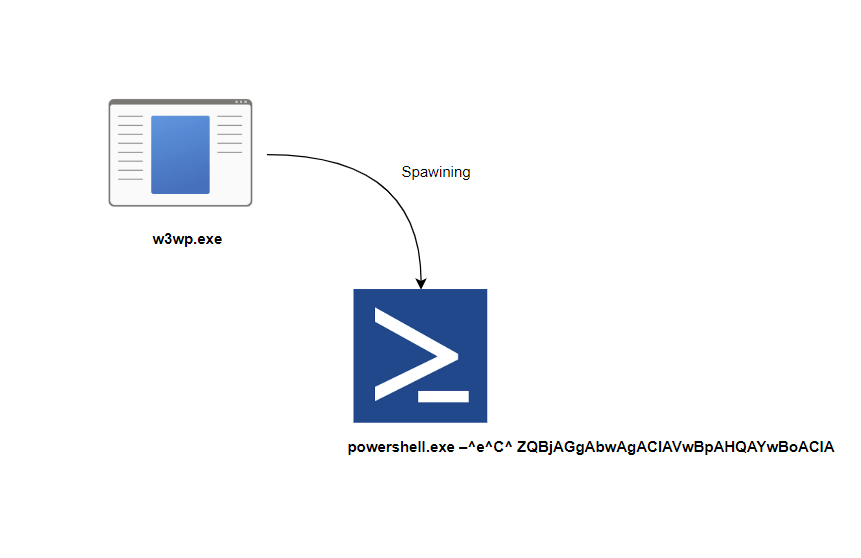 alwashali/detection-validation
Detection rule validation
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 marcgoam/cve-2026-54121-certighost
CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
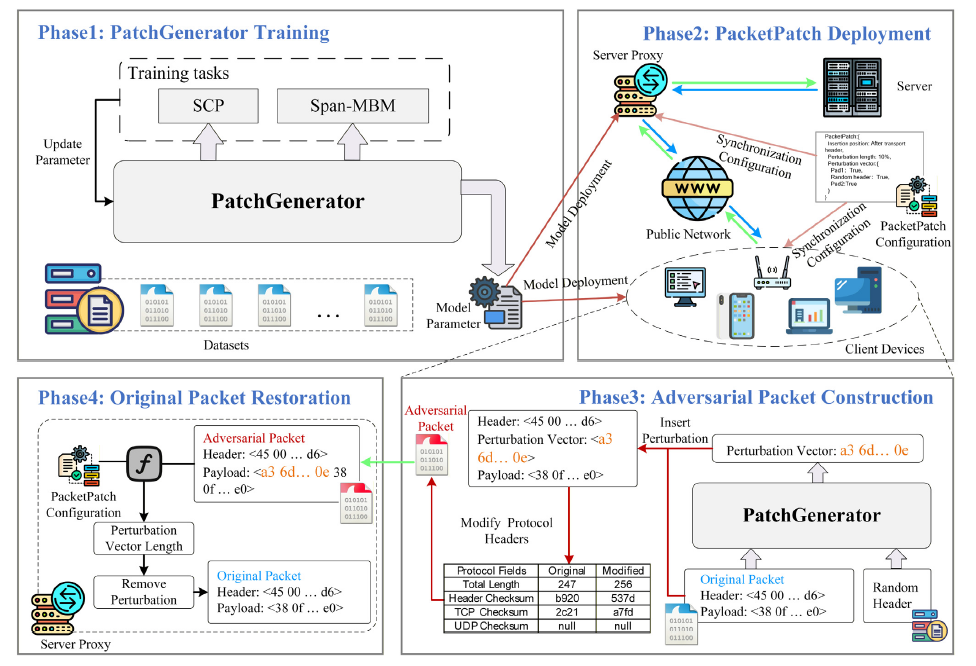 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.