
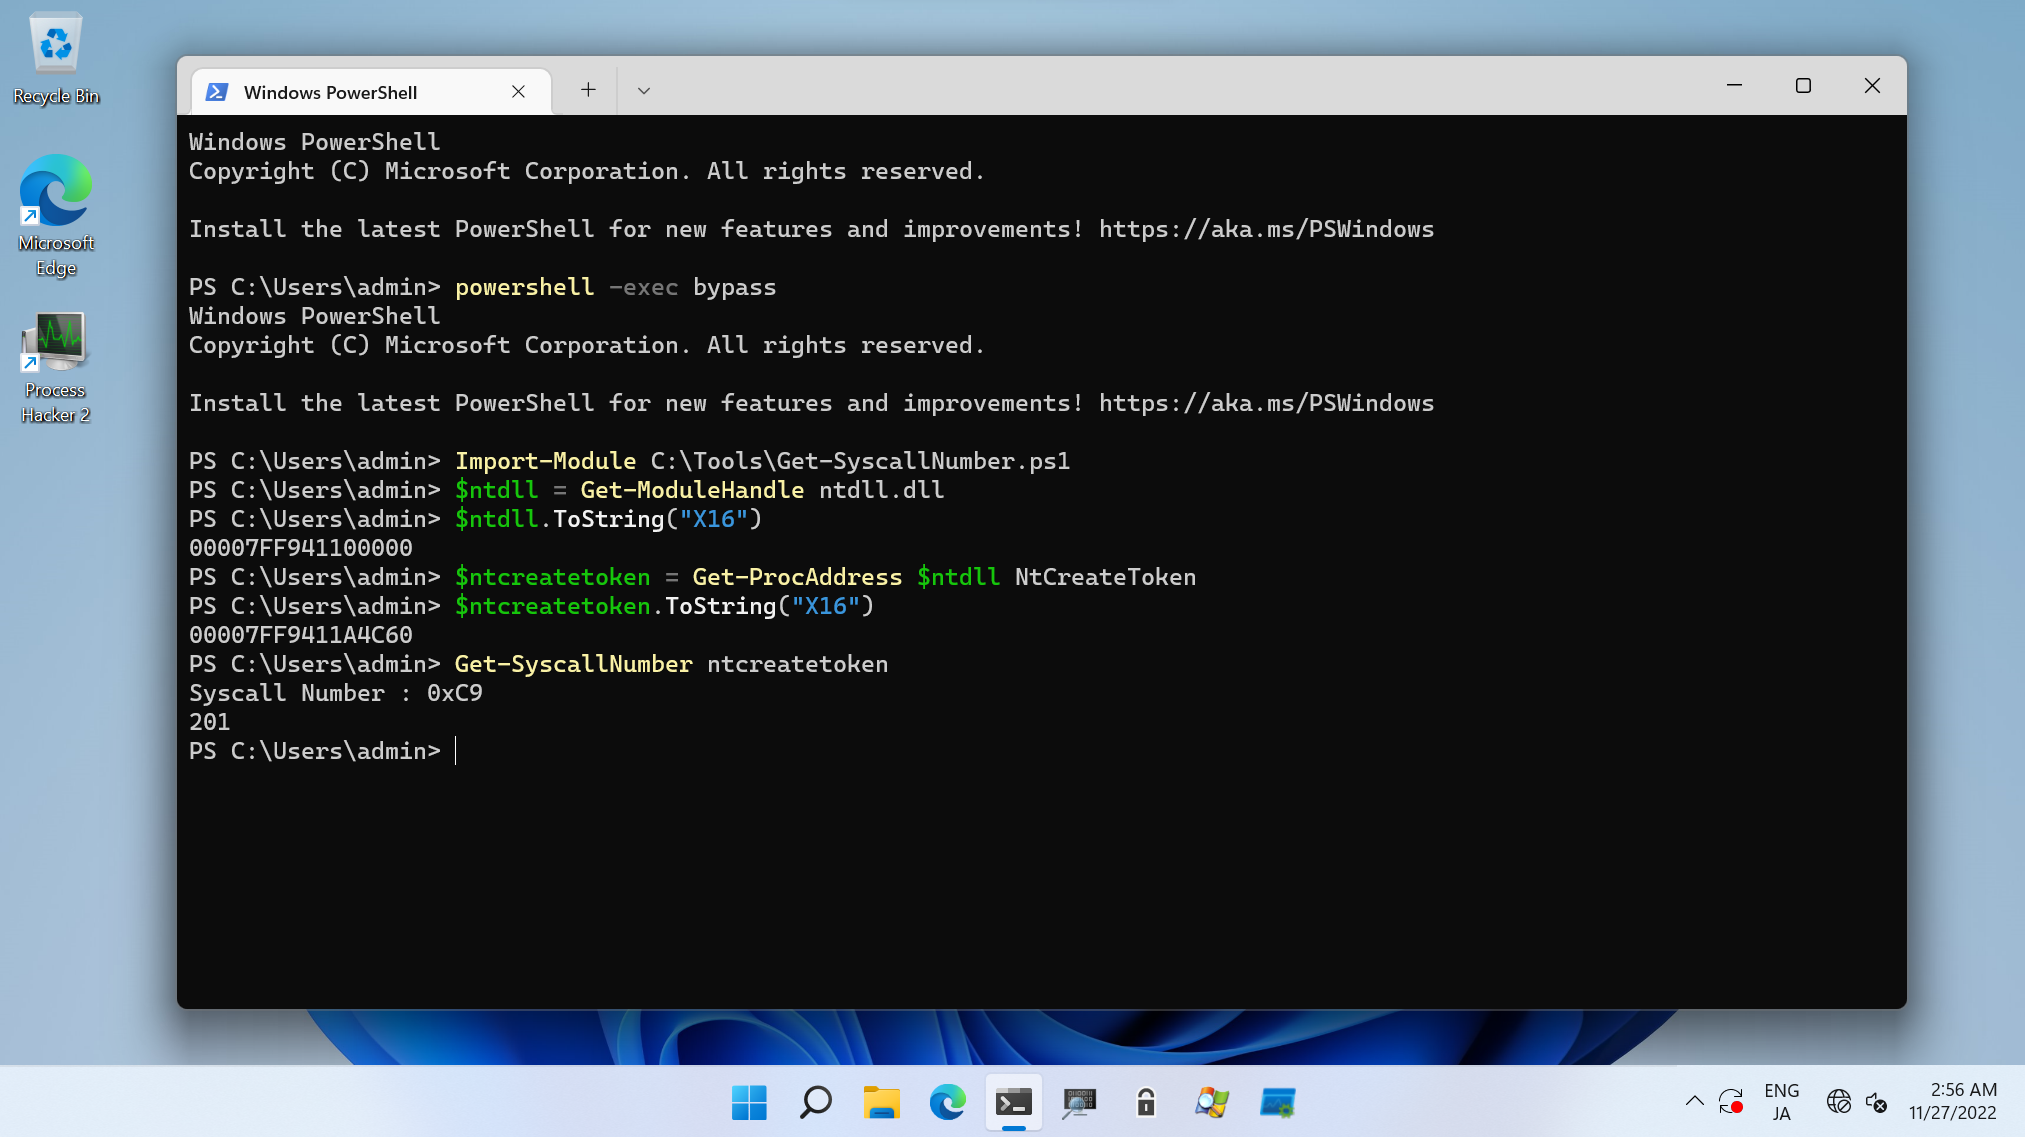
AtomicSyscall
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
adversarial-attackbinary-analysiseducation+3
365
daem0nc0re/atomicsyscallTools and PoCs for Windows syscall investigation.
 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 sensepost/impersonate
A windows token impersonation tool
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
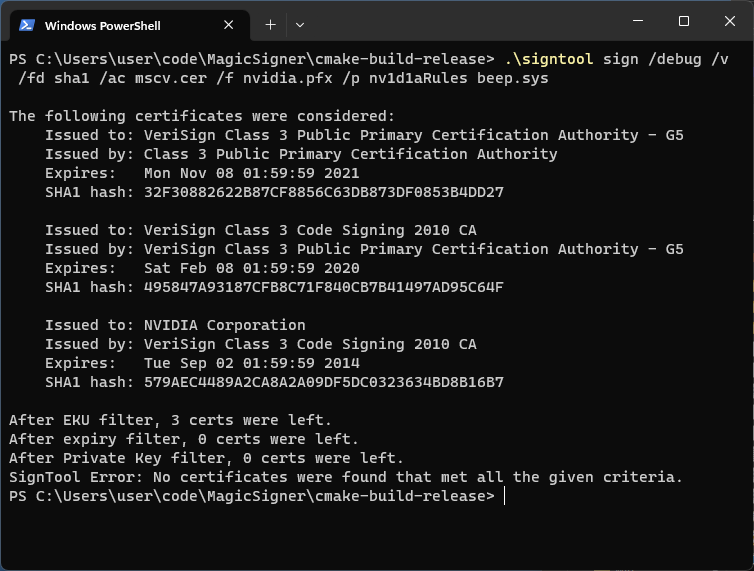 namazso/magicsigner
Signtool for expired certificates
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
 george0papasotiriou/cve-2026-21010-voip-sip-digest-authentication-replay
Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…