
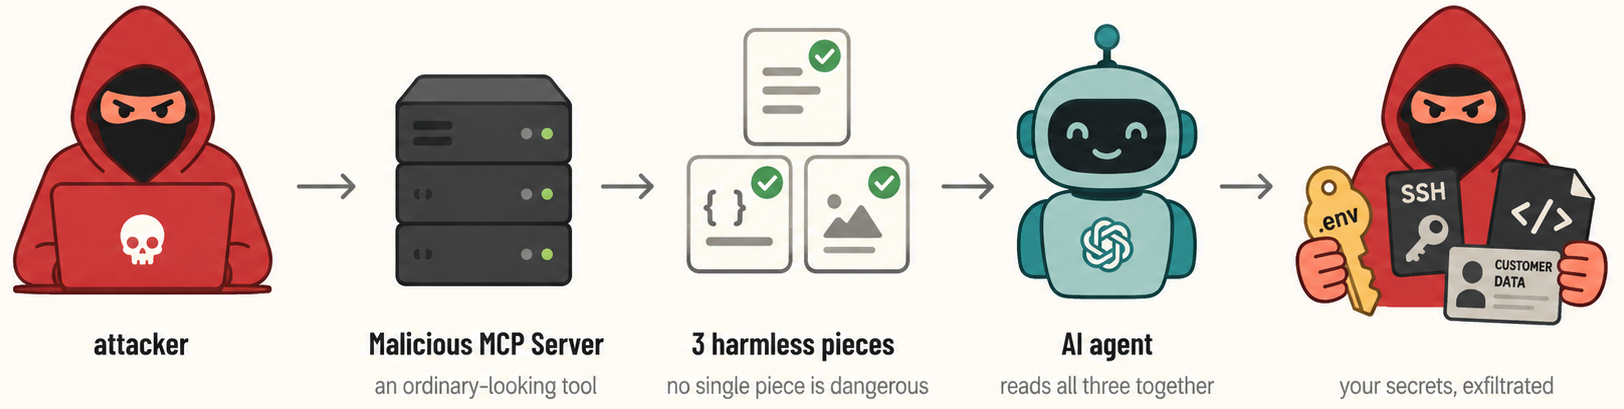
ghostsplice
 asset-group/ghostsplice
Ghostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
adversarial-attackai-securitydata-exfiltration+3
91 month ago
asset-group/ghostspliceGhostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
 jpoindexter/interrogation-game
Voice-based detective interrogation game. Mistral Large 3 + Voxtral STT + ElevenLabs TTS. Built for the Mistral Worldwide Hackathon 2026.
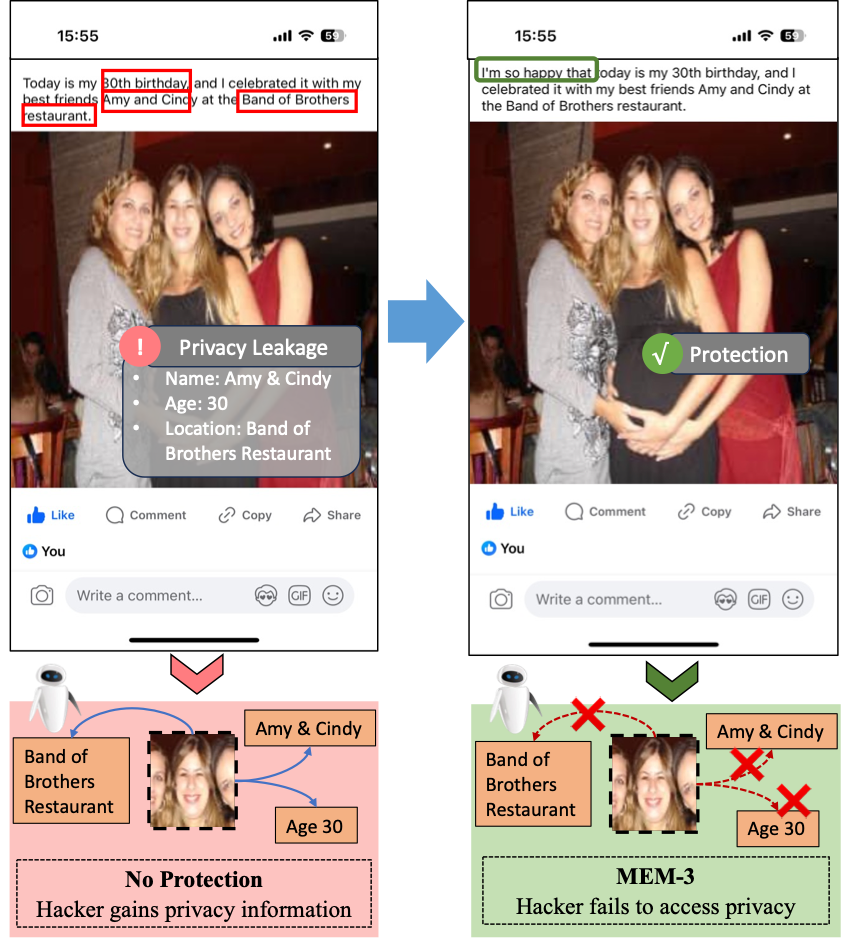 thinwayliu/multimodal-unlearnable-examples
The code for ACM MM2024 (Multimodal Unlearnable Examples: Protecting Data against Multimodal Contrastive Learning)
 yeasen-z/leakgauge
Detects LLM context-leakage attacks by training lightweight behavior probes on log-probabilities, with vLLM offline/server detection pipelines.
 loophole-llc/fish-live-in-trees
Gemini - Production LLM Runtime Alignment Context Injection
 siyuanli00/intact
Research code reproducing multi-turn LLM jailbreak experiments (FITD, MRCJ, ActorAttack, X-Teaming) from the SoK intent-oriented systematization…
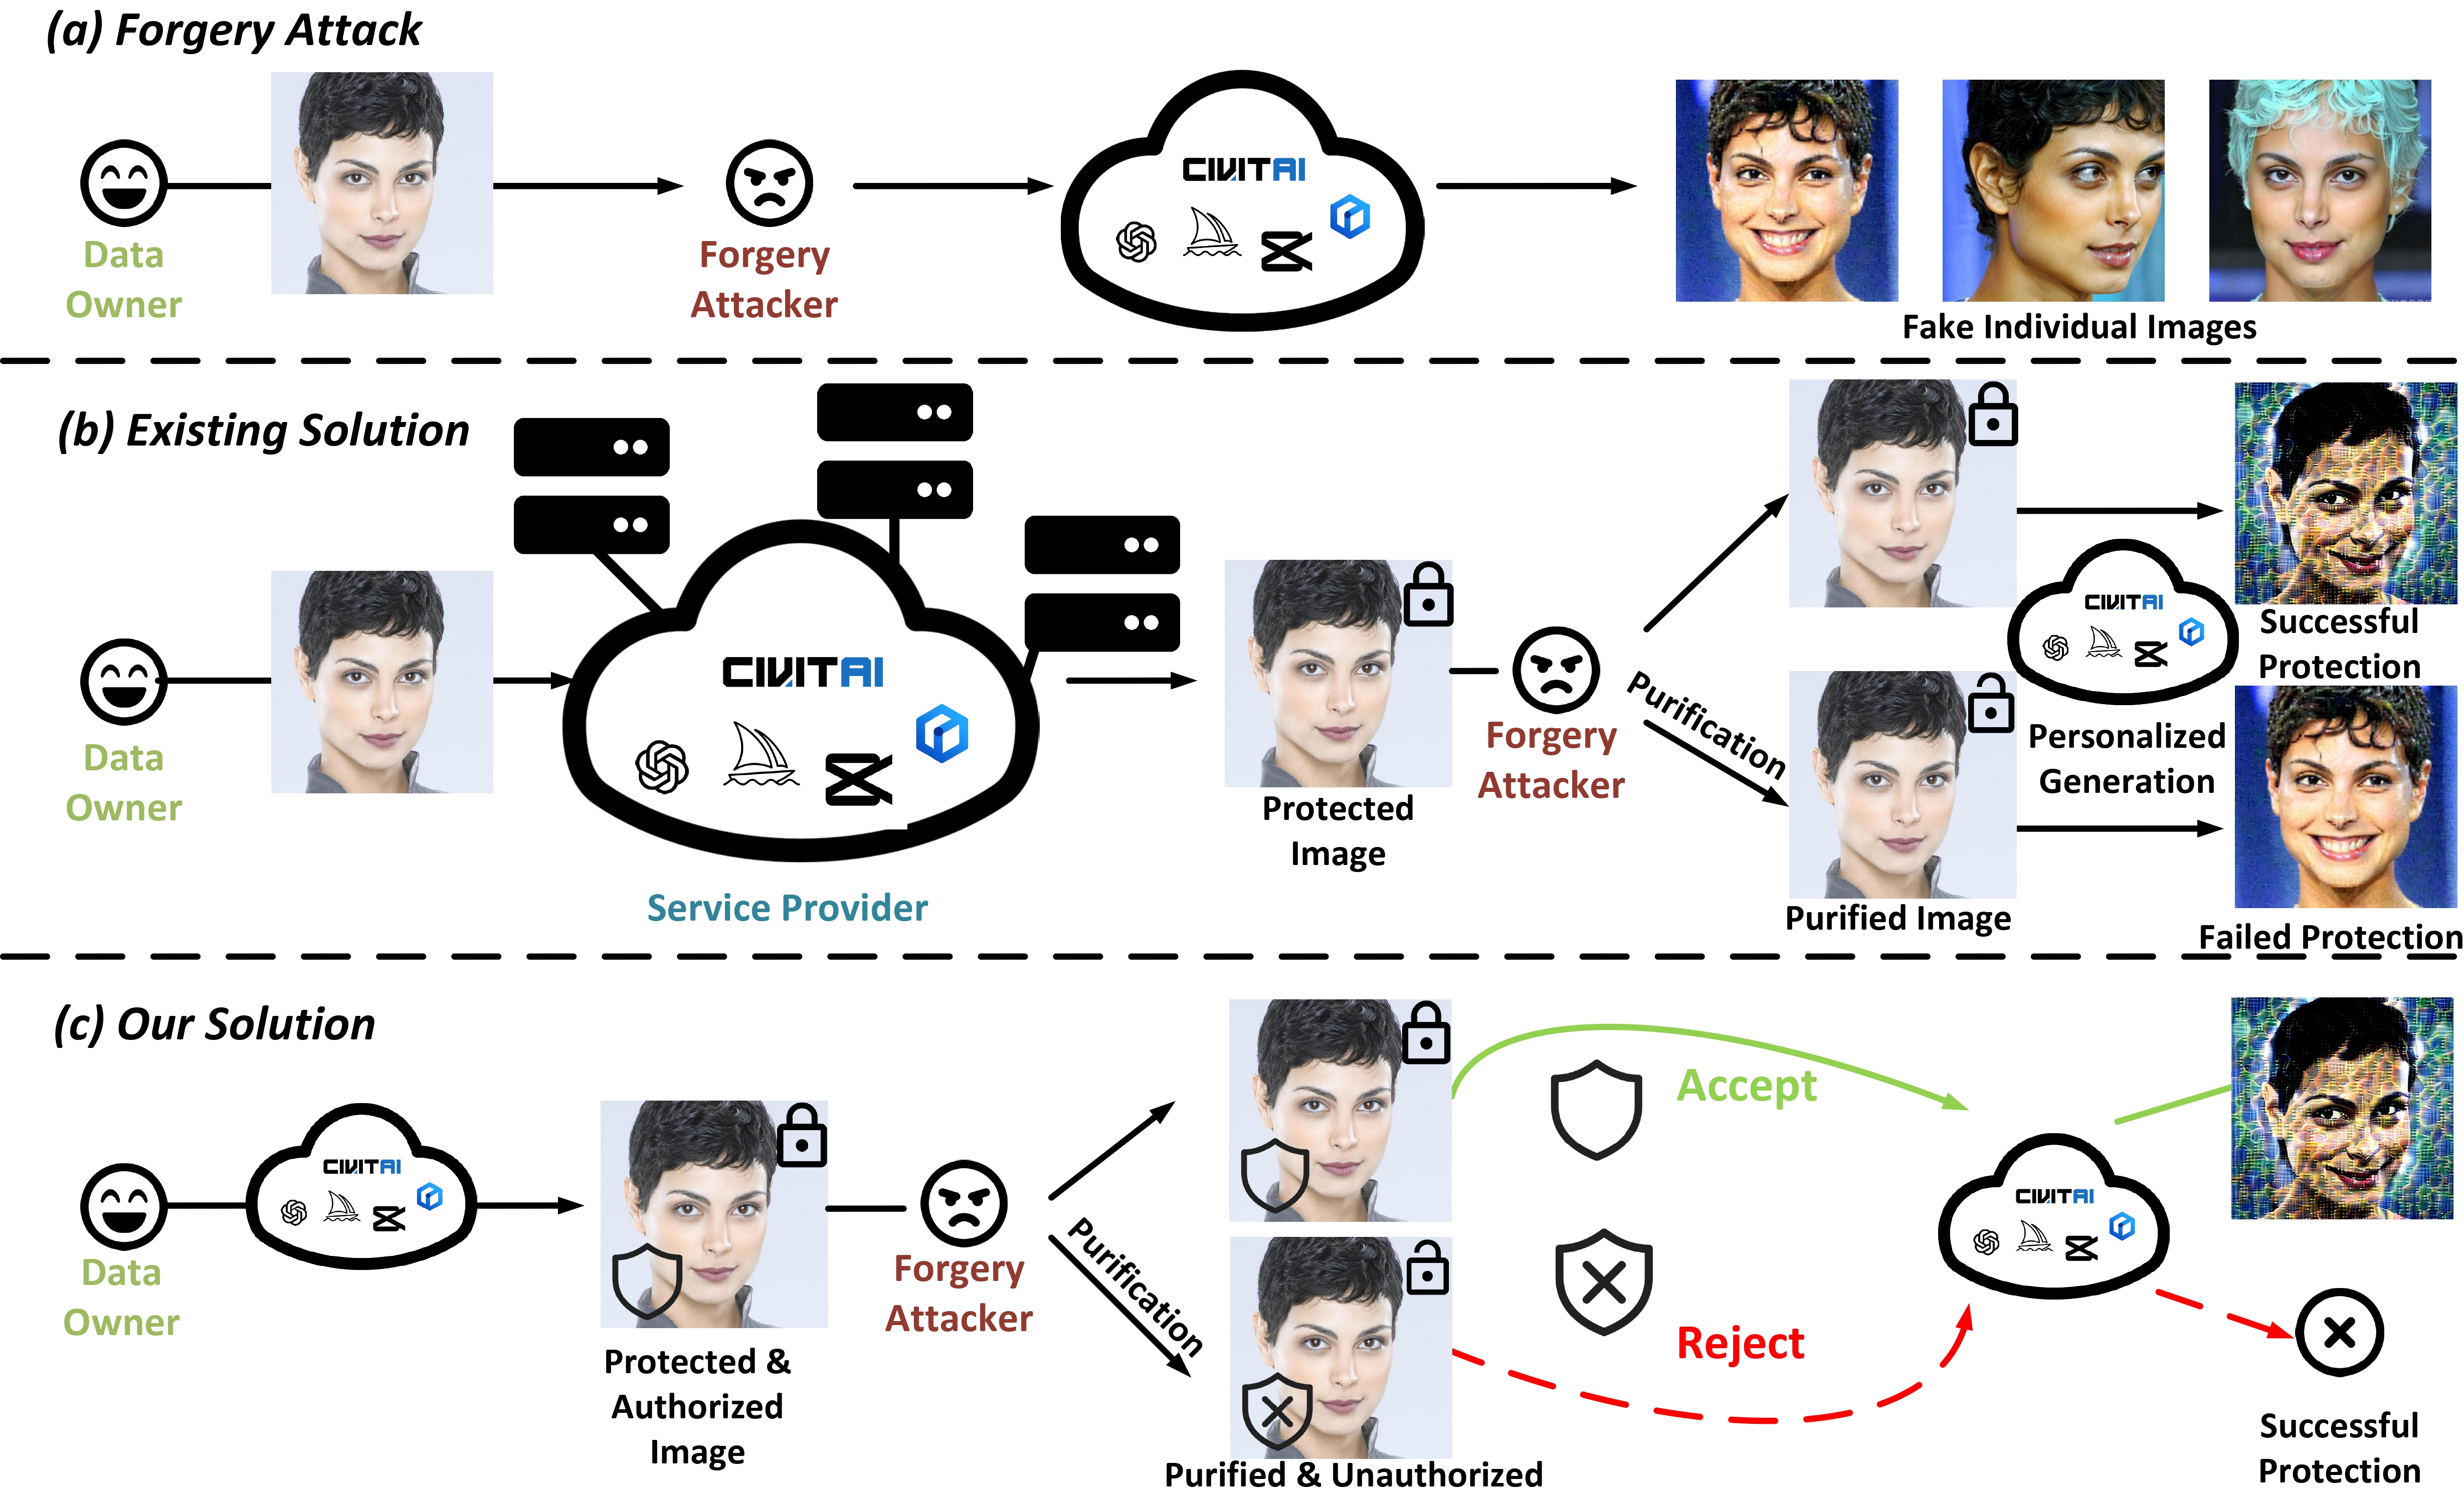 seeyn/anti-tamper-perturbation
[ICCV 2025] Anti-Tamper Protection for Unauthorized Individual Image Generation
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.
 hackspeak/cve-2026-64638
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE PoC mirror — WordSec, MIT; for authorized security testing
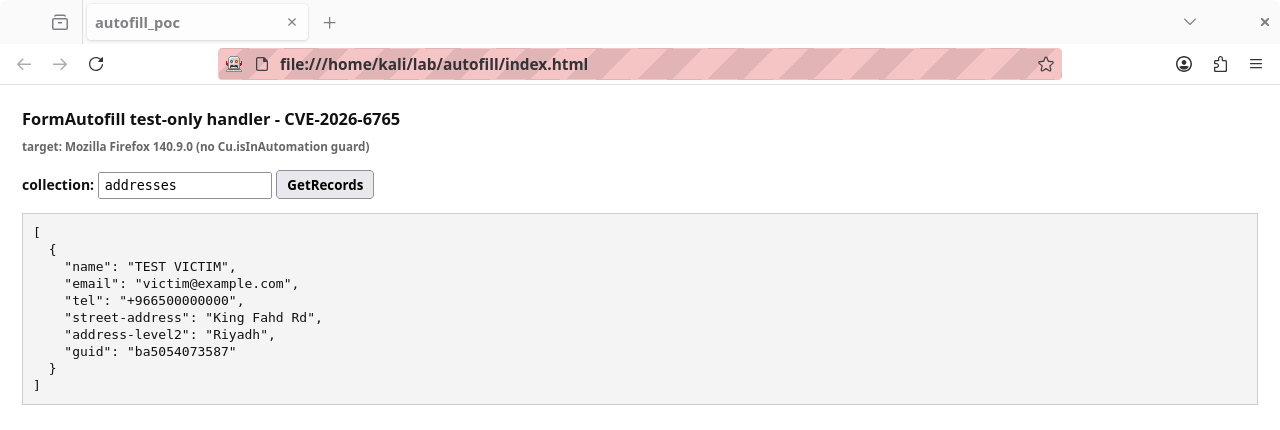 defineid/skeletonkey
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
 ragib-amin-nihal/pe-coa
Code Implementation of "Pattern Enhanced Multi-Turn Jailbreaking: Exploiting Structural Vulnerabilities in Large Language Models"
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
 george0papasotiriou/cve-2026-0101-ble-address-spoofing-via-weak-resolvable-private-address
Python PoC for CVE-2026-0101 demonstrating BLE address spoofing via replay of a captured Resolvable Private Address to impersonate a trusted…
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…

 cognitive-functors/c4-meta-system
Production AI defense with 7-layer protection: mathematical constraints, object-capability access, distributed O2 consensus, SVETILO ethics. First…
 sonnelon/cve-2026-23744-poc
The poc of CVE-2026-23744
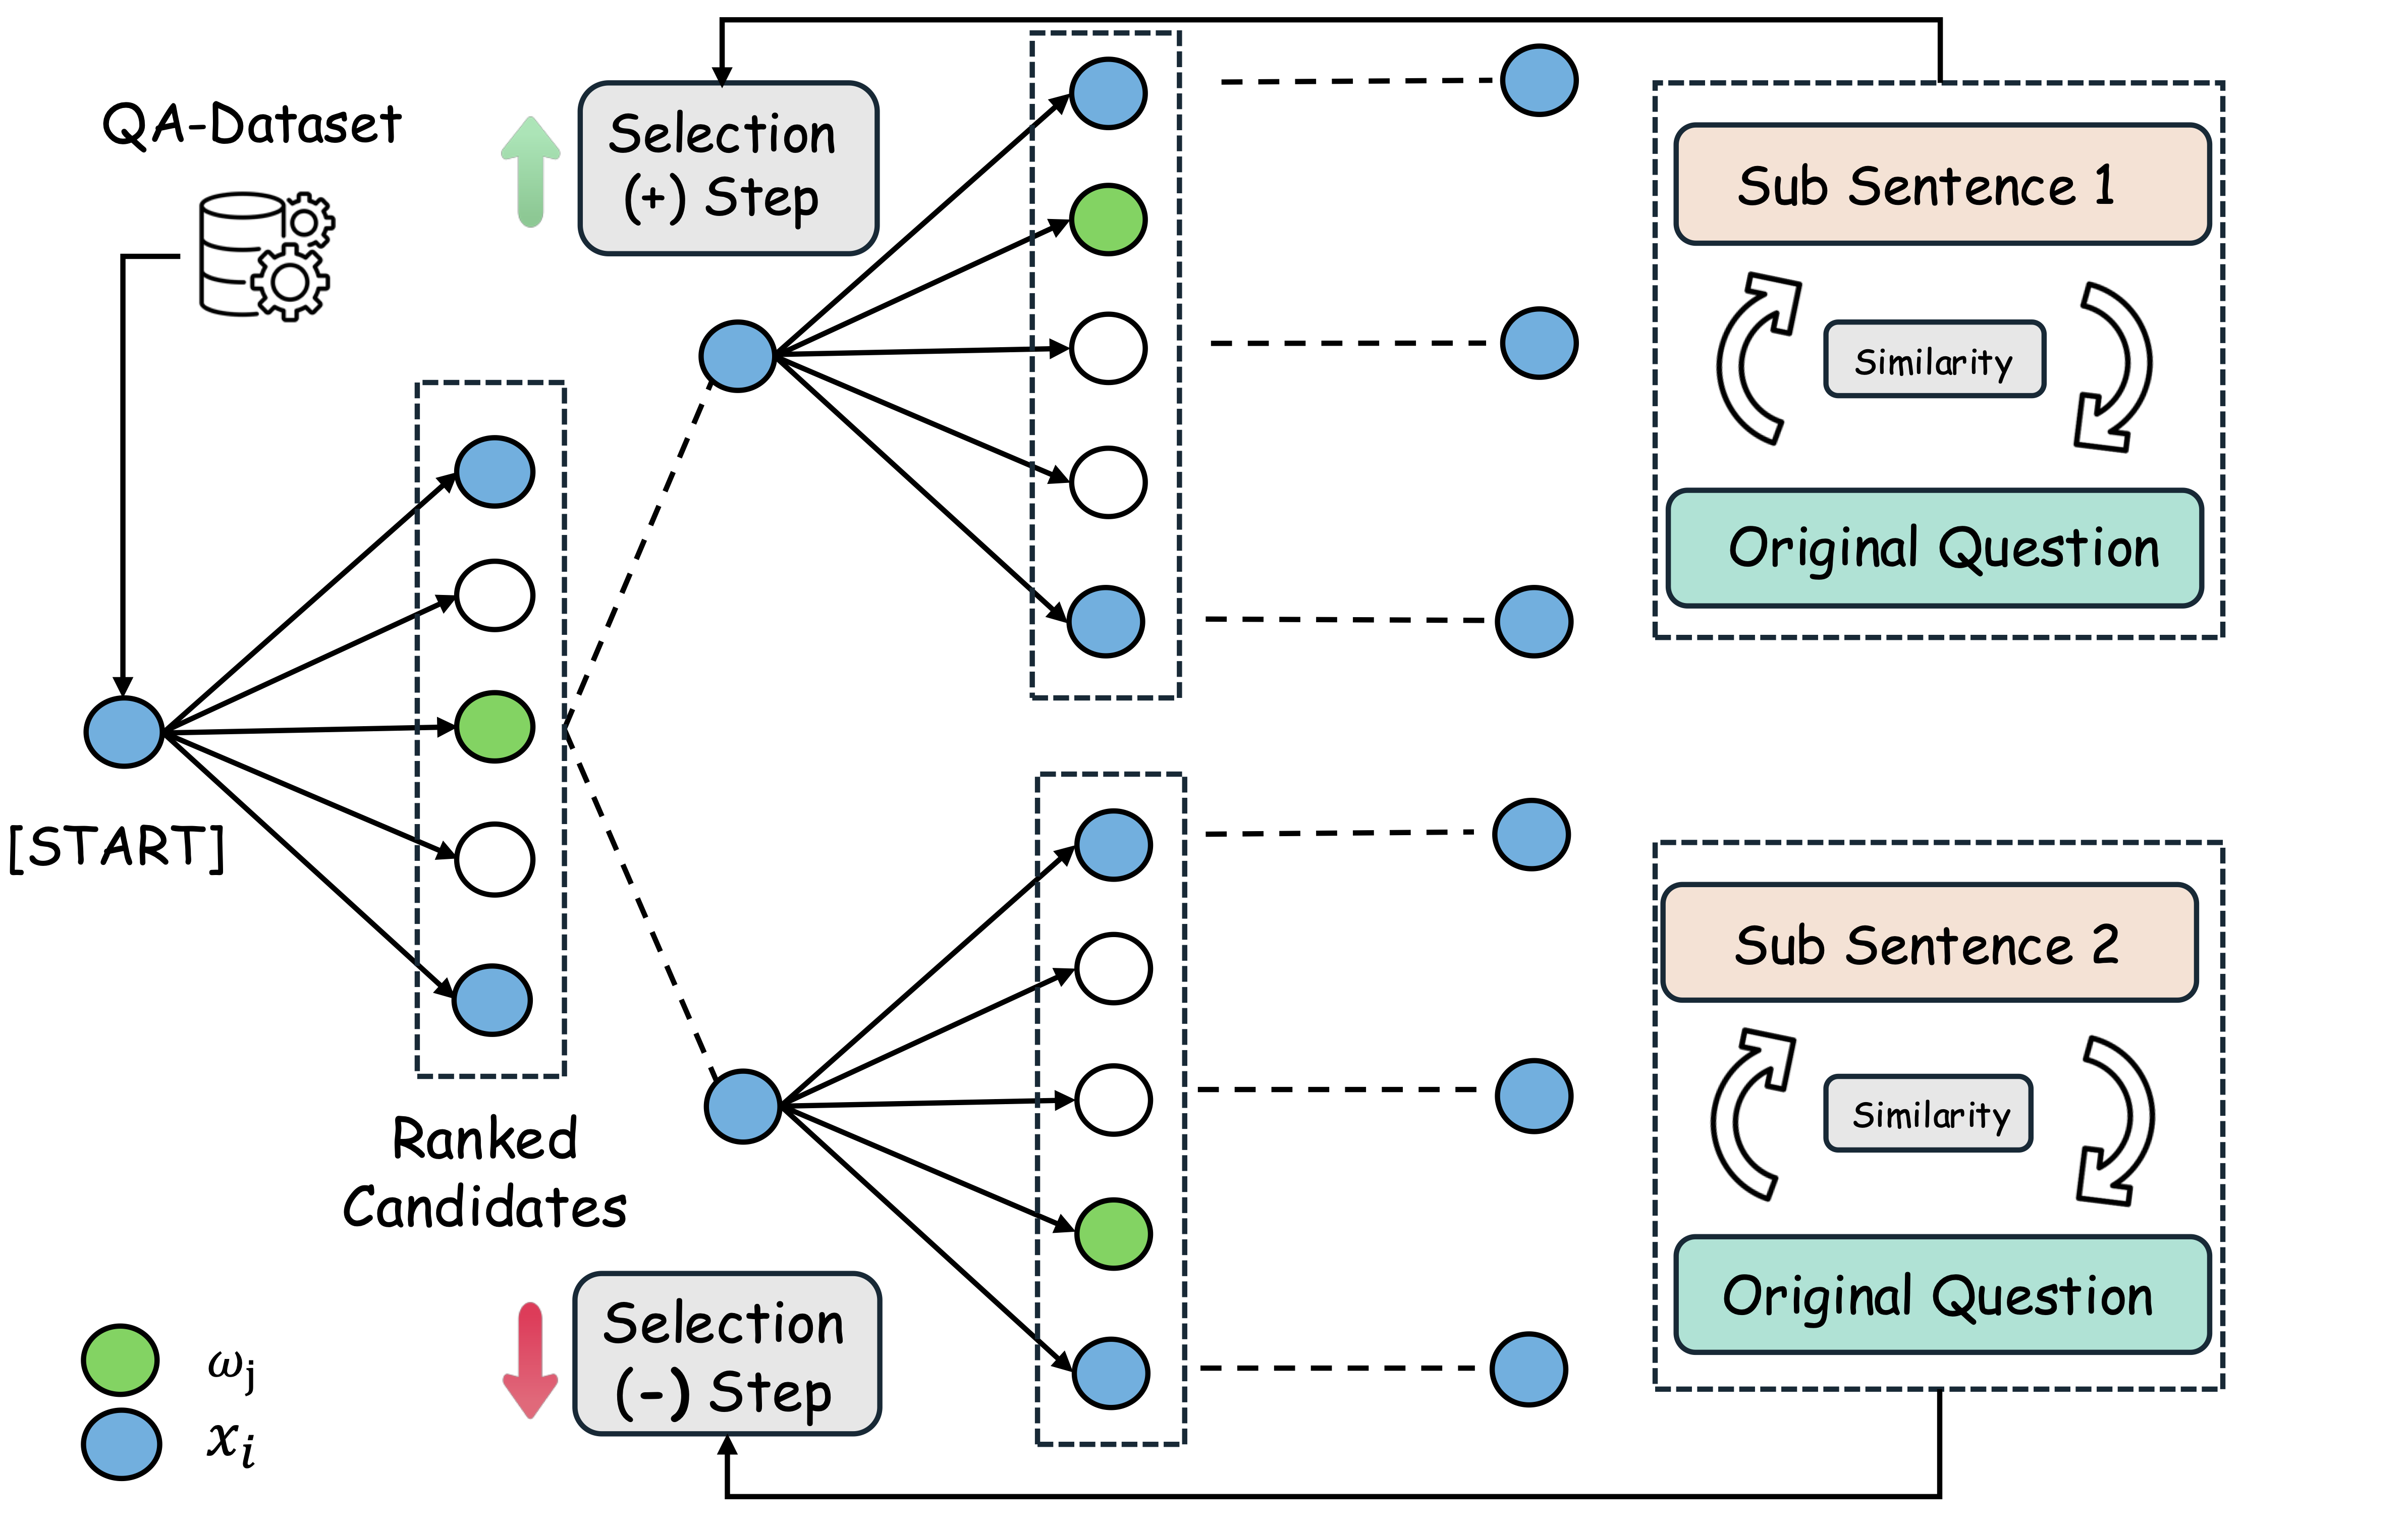 franz-chang/adaptive_greedy_local_search
AGLS
 horkimhab/cve-2026-20685
CVE-2026-20685 - Draft or TODO