
process-inject-kit
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
adversarial-attackexploit-frameworkspayload-development+2
193
rasta-mouse/process-inject-kitPort of Cobalt Strike's Process Inject Kit
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 thebabush/llvm-jutsu
Anti-LLM obfuscation via finger counting
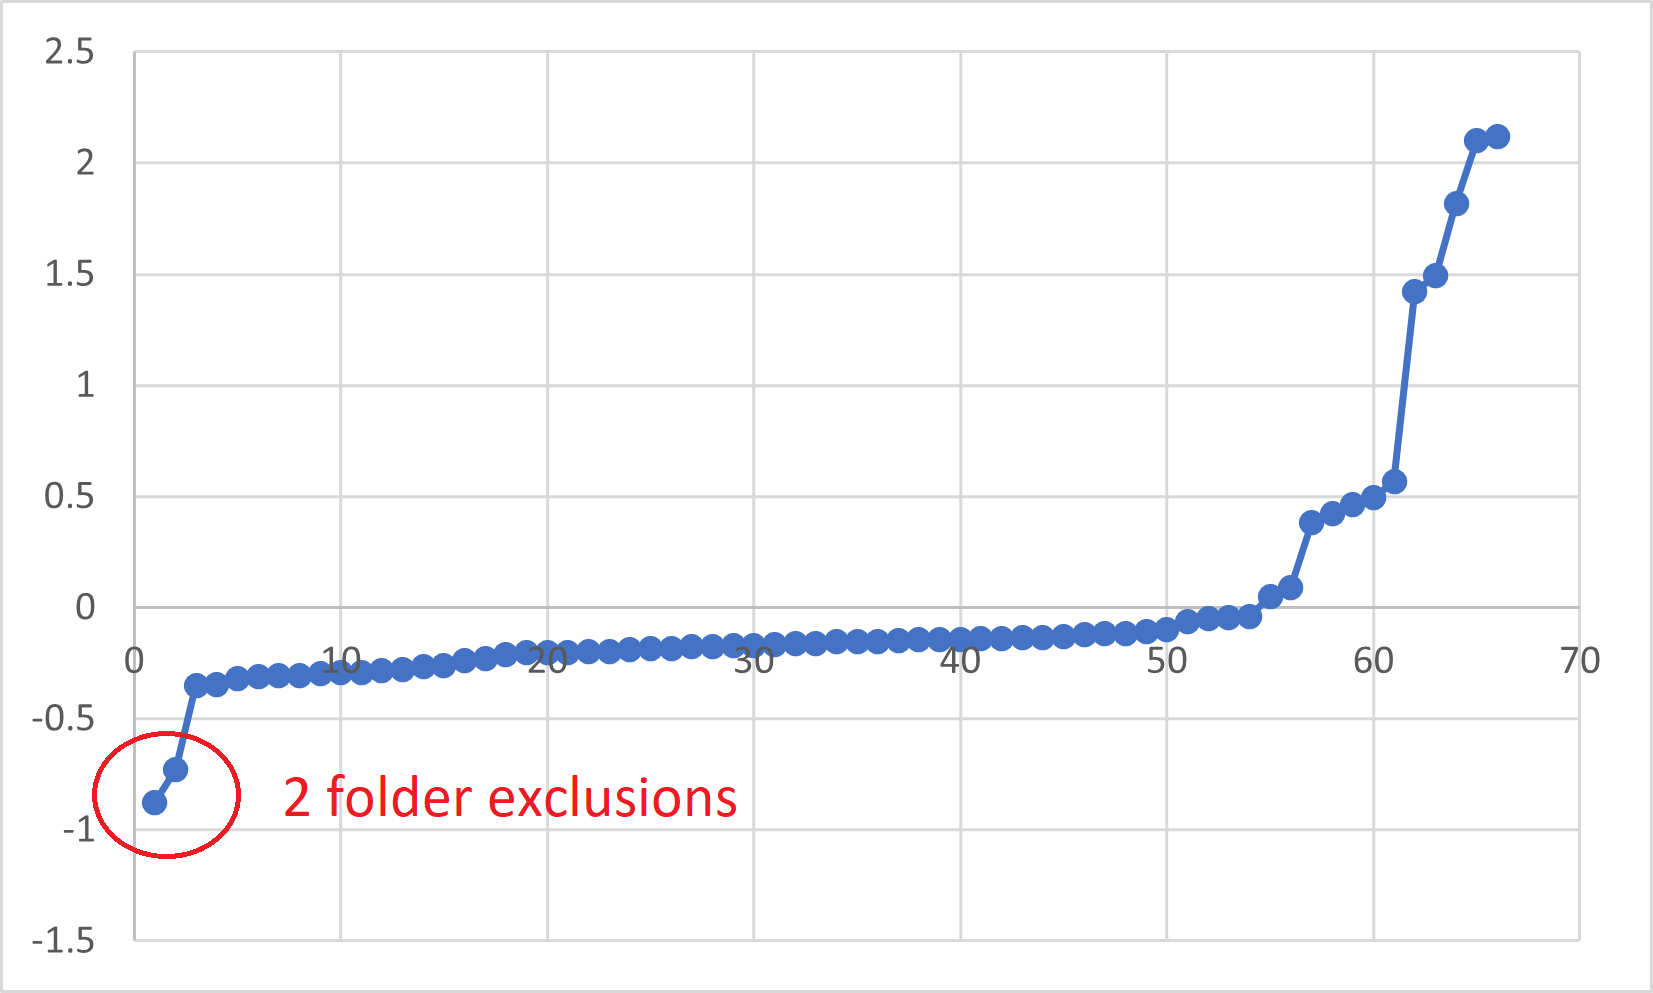 bananabr/timeexception
A tool to find folders excluded from AV real-time scanning using a time oracle
 bishopfox/brokenhill
A productionized greedy coordinate gradient (GCG) attack tool for large language models (LLMs)
 nul0x4c/etwsessionhijacking
A Poc on blocking Procmon from monitoring network events
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 jwillyamz/ezemu
See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 vozzie/uacscript
Windows 7 UAC Bypass Vulnerability in the Windows Script Host
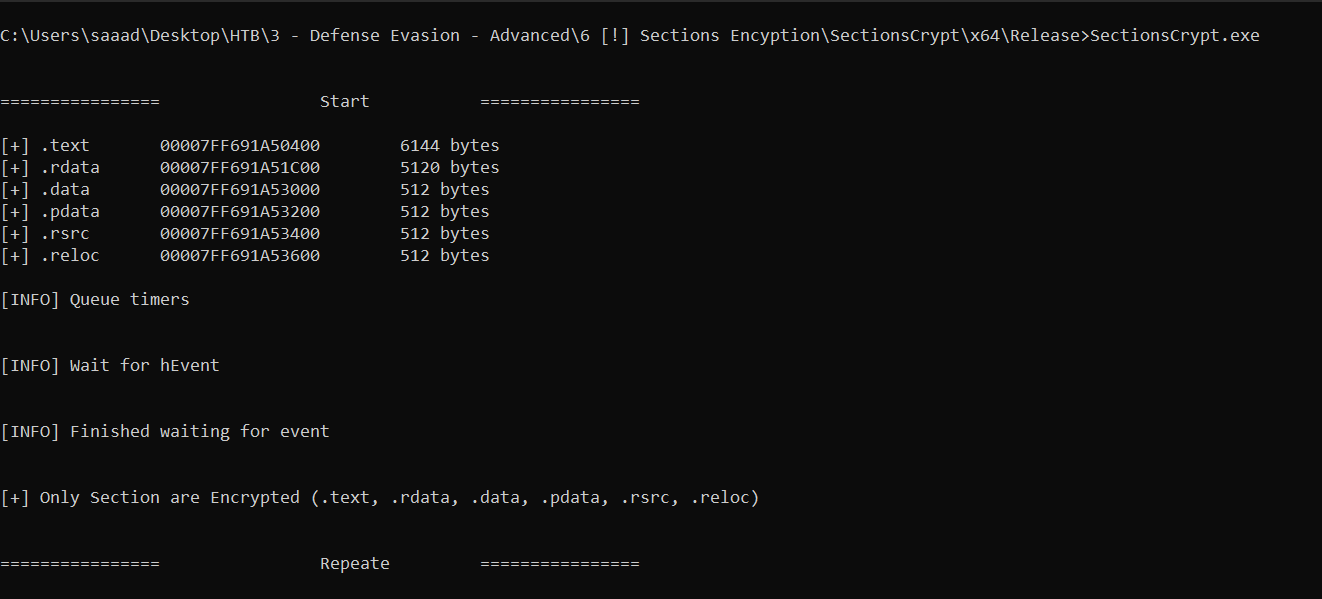 saadahla/d1rksleep
Improved version of EKKO by @5pider that Encrypts only Image Sections
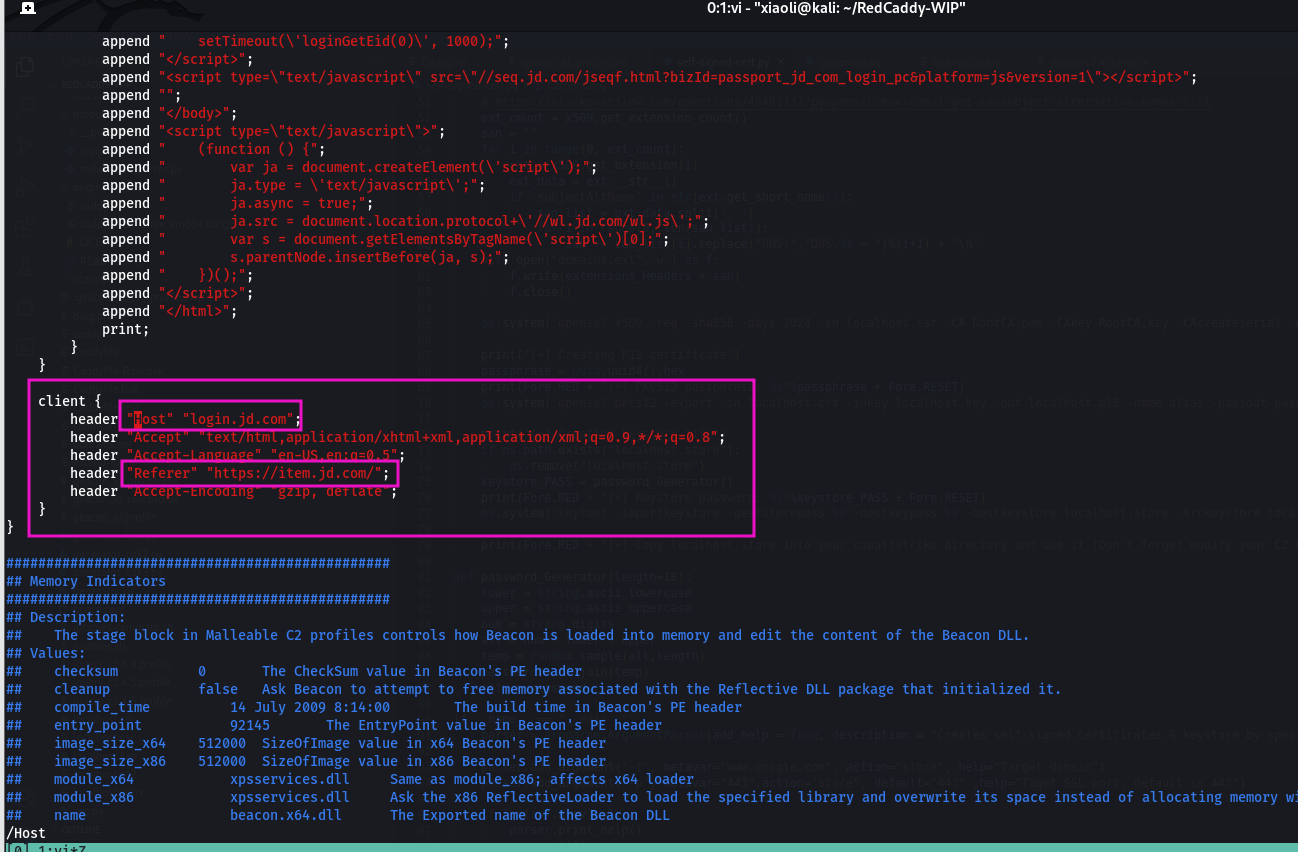 xiaolichan/redcaddy
C2 redirector base on caddy
 kudaes/bin-finder
Detect EDR's exceptions by inspecting processes' loaded modules
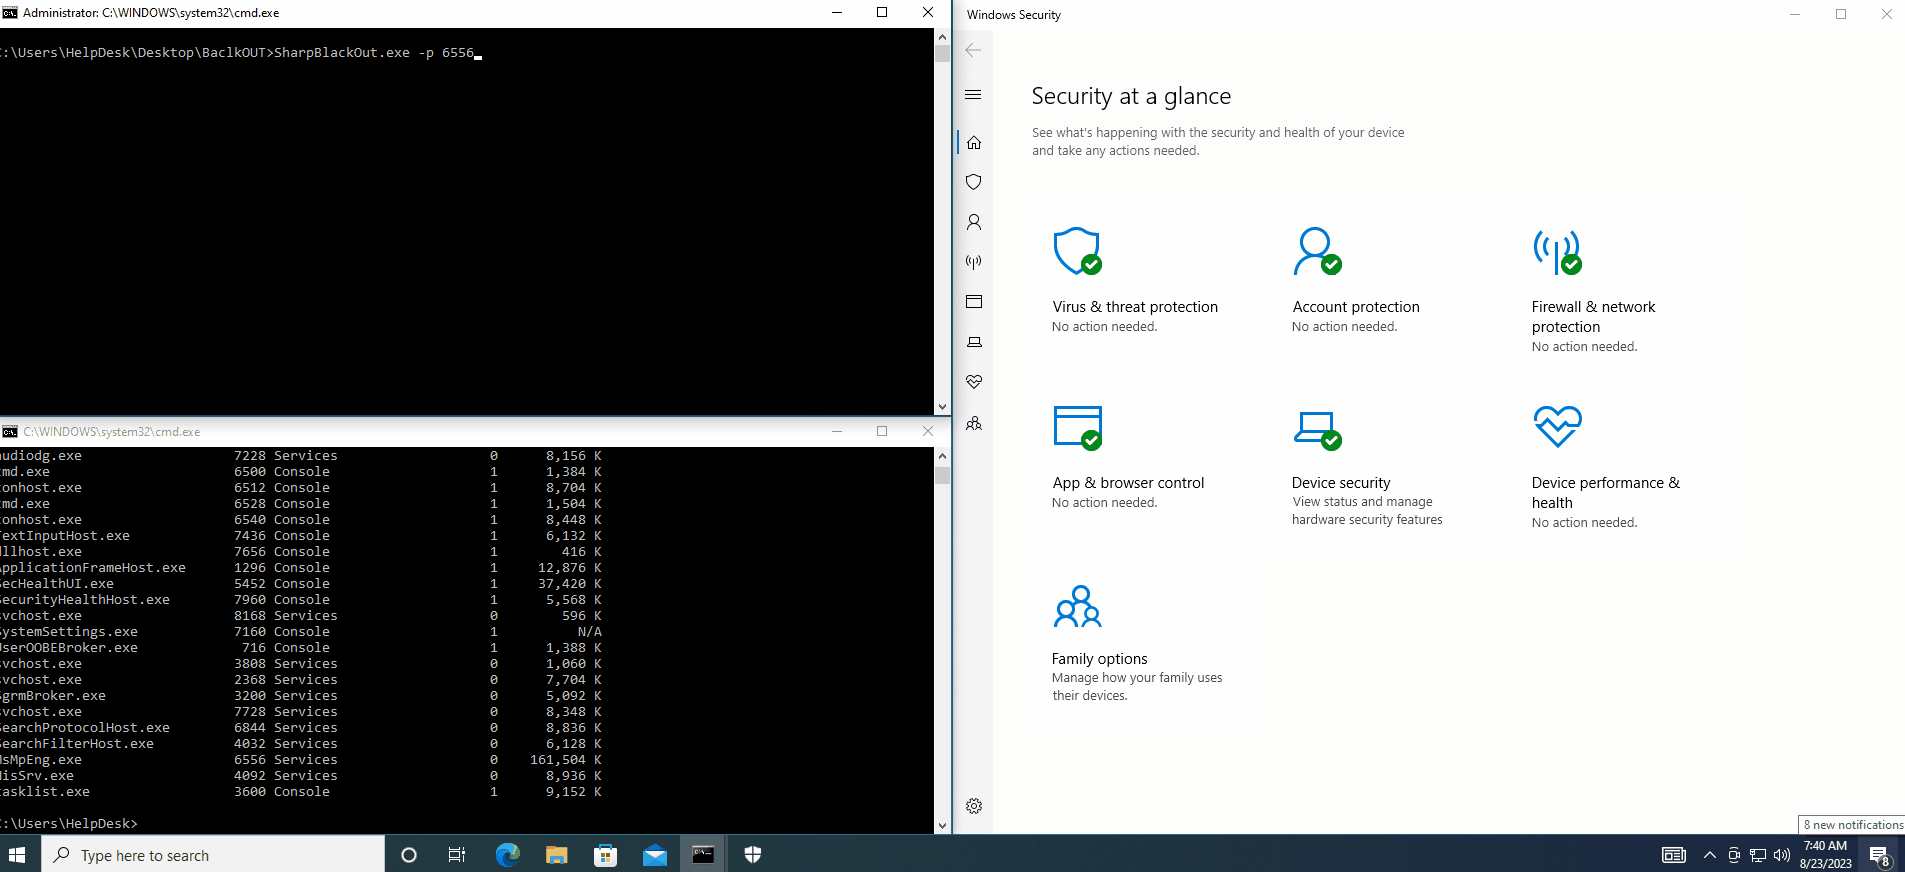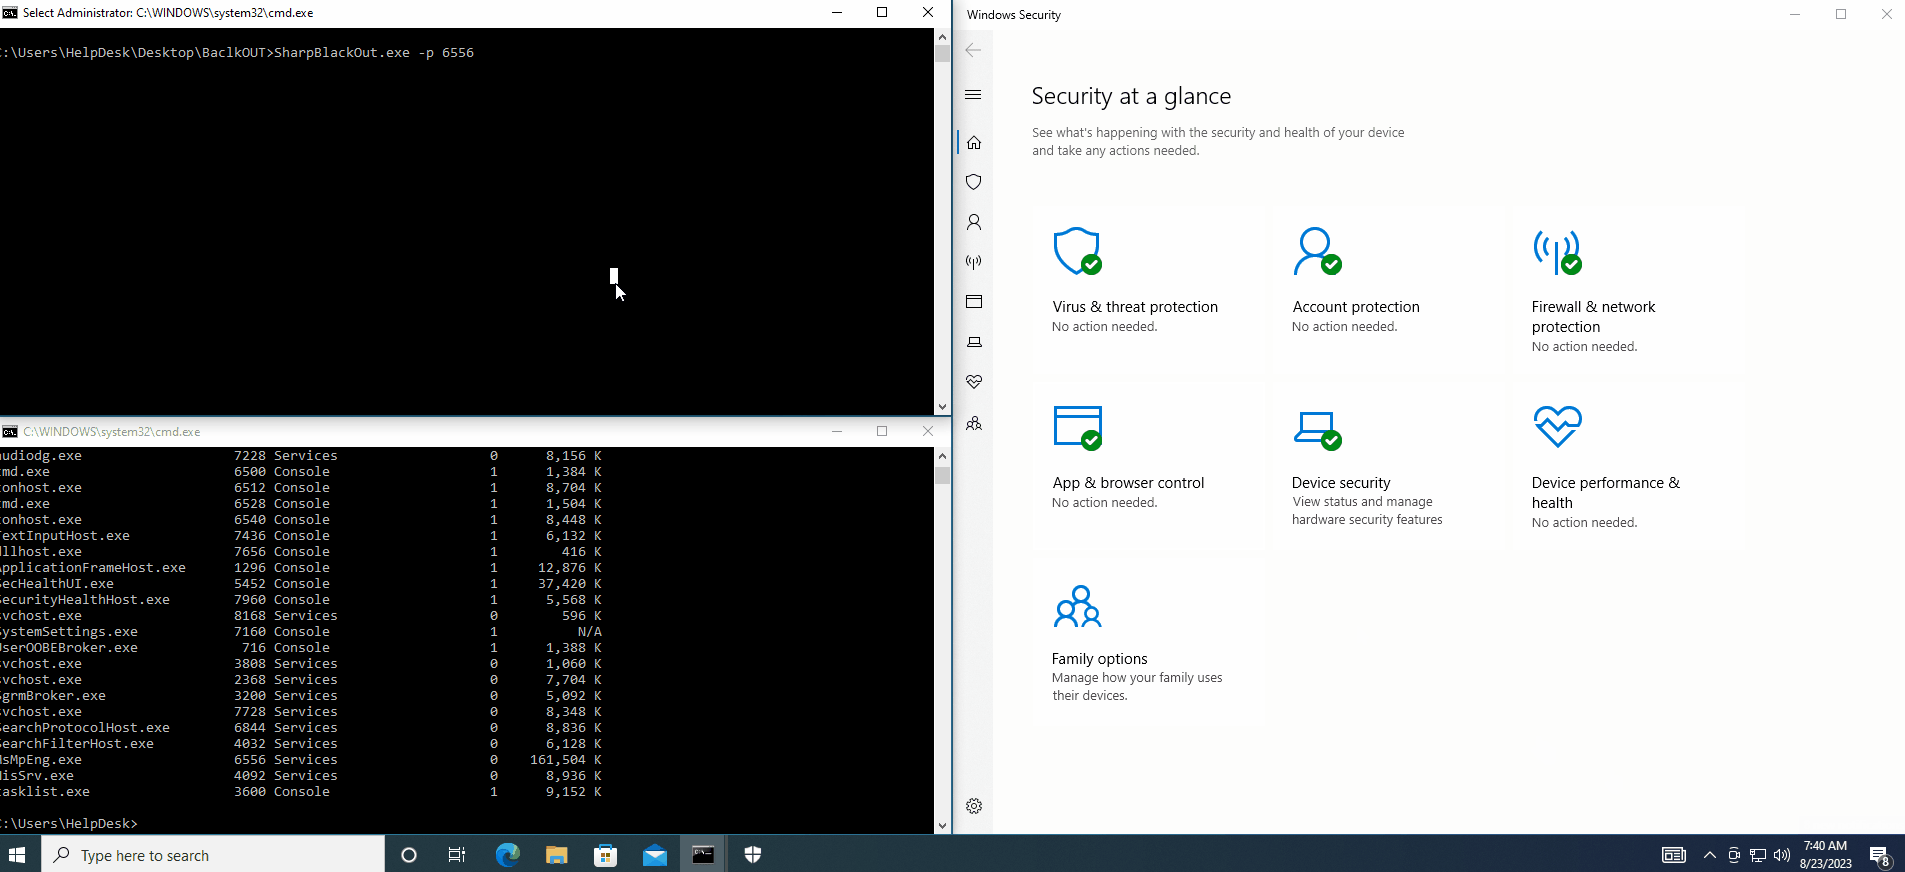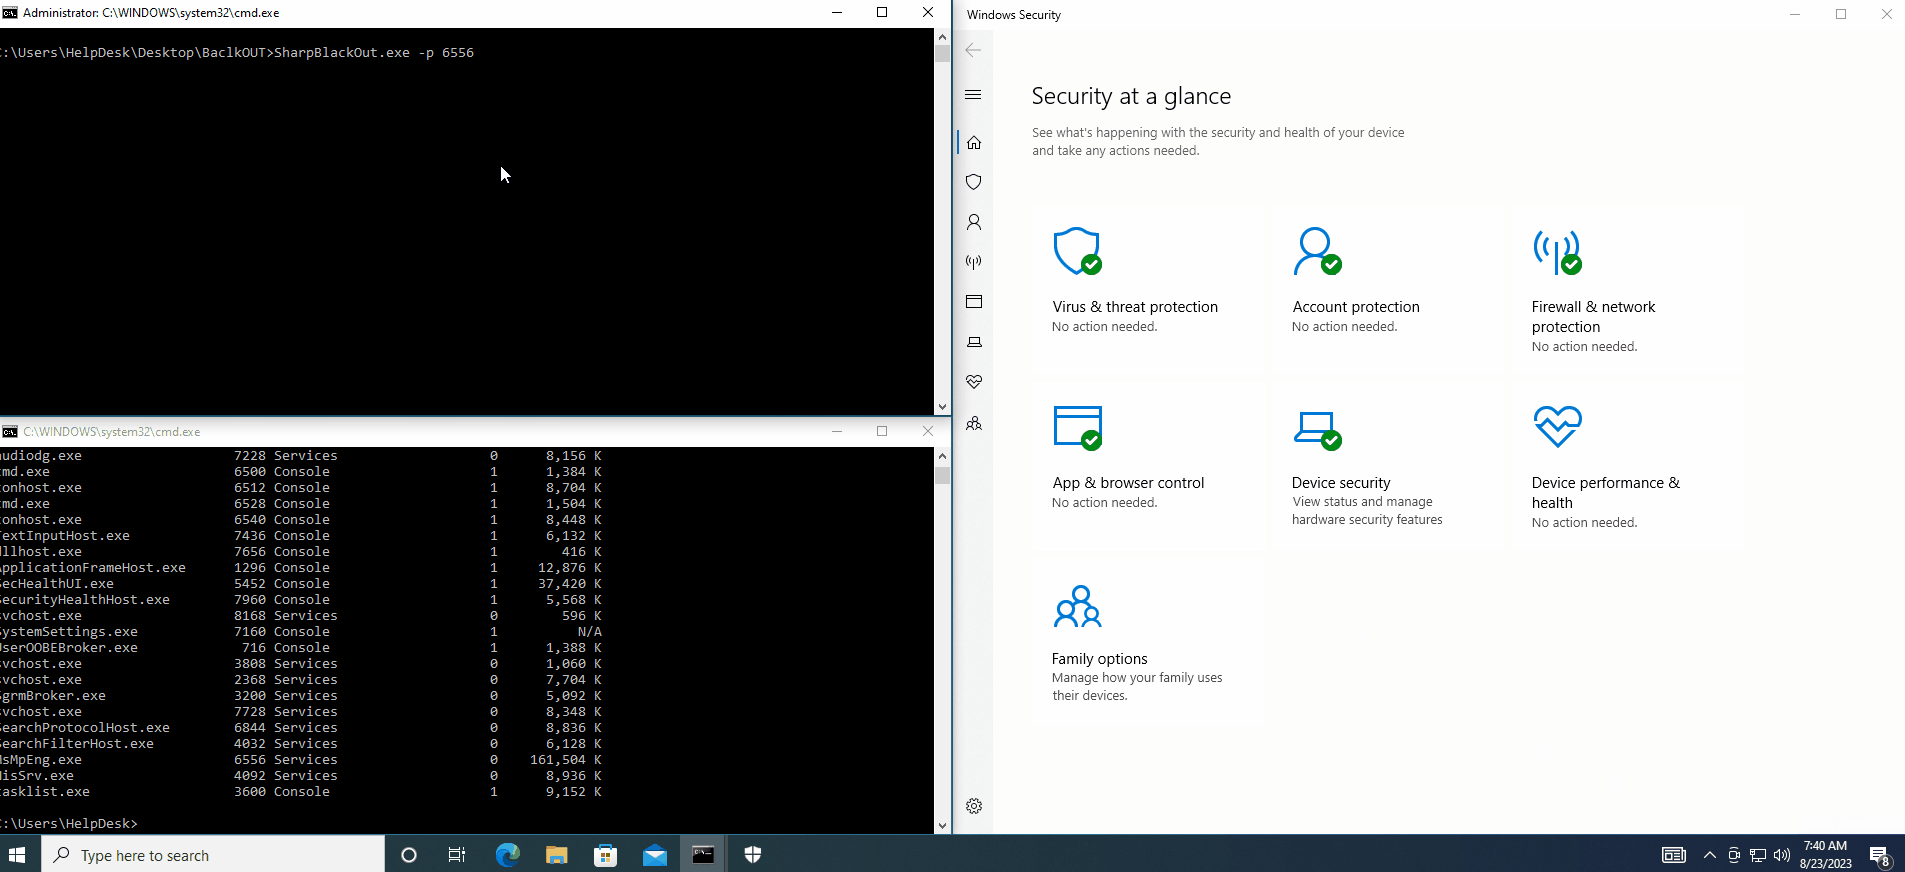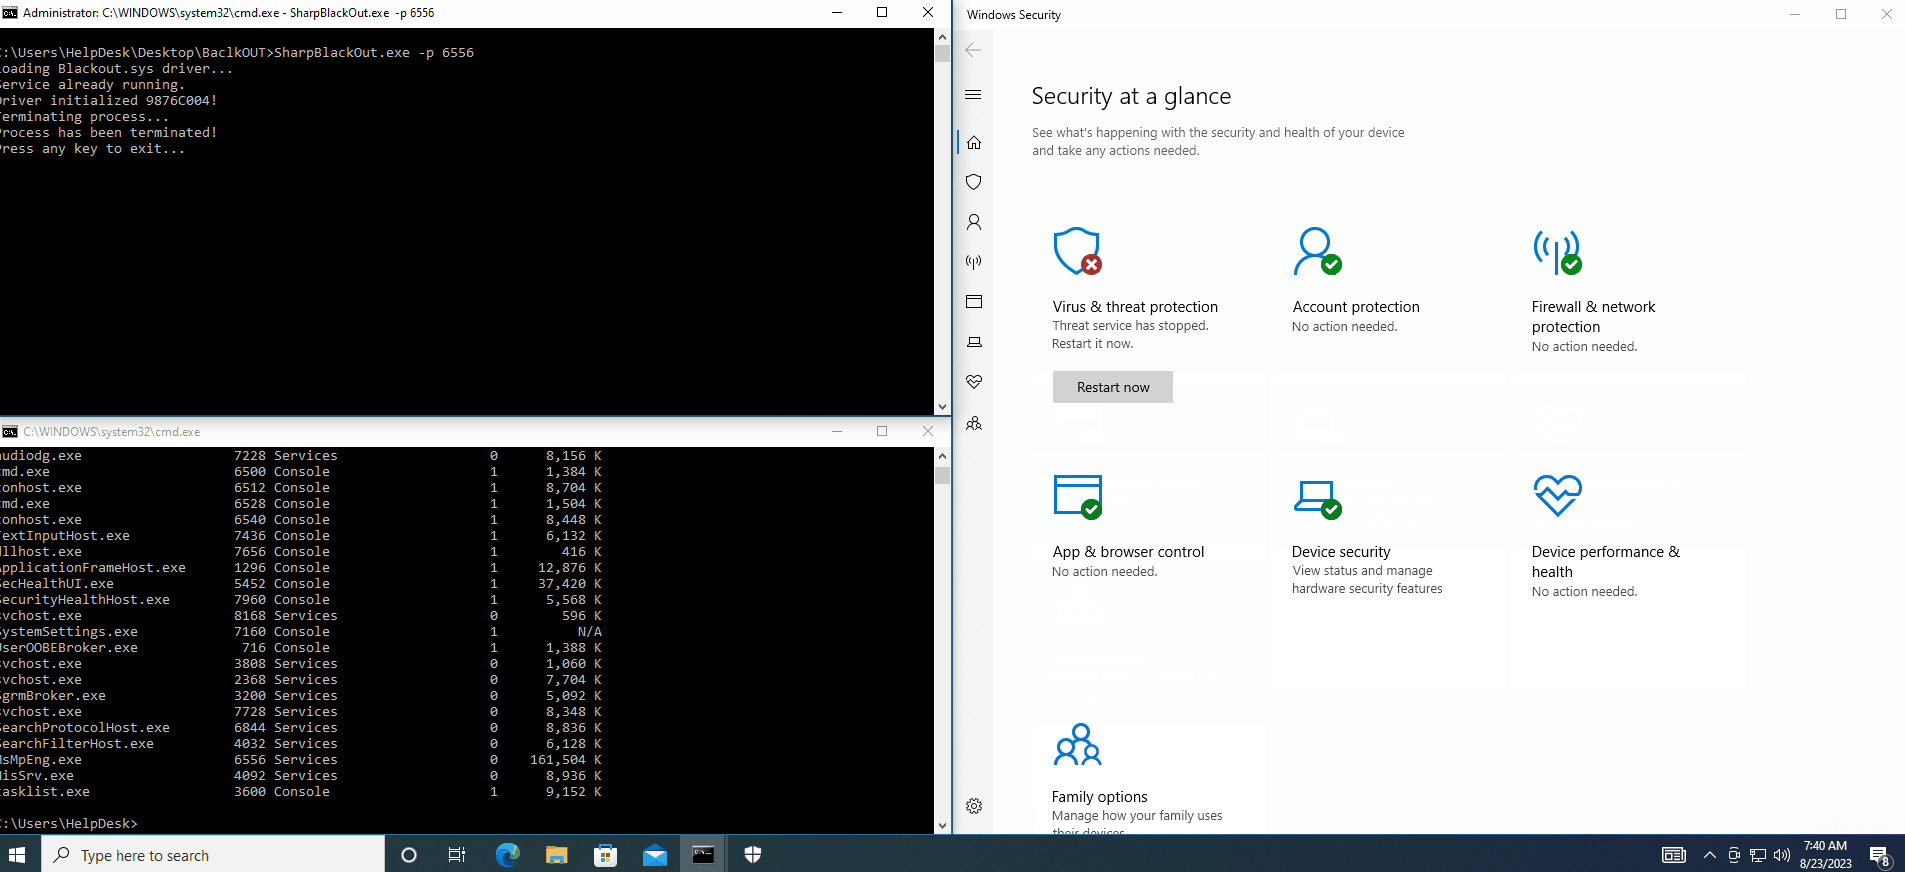 dmcxblue/sharpblackout
Terminate AV/EDR leveraging BYOVD attack
 secdev02/easytokens
Kali365 - EvilTokens Replica
 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post