

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
722
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 rasta-mouse/crystal-kit
Evasion kit for Cobalt Strike
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 bishopfox/sliver
Adversary Emulation Framework
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
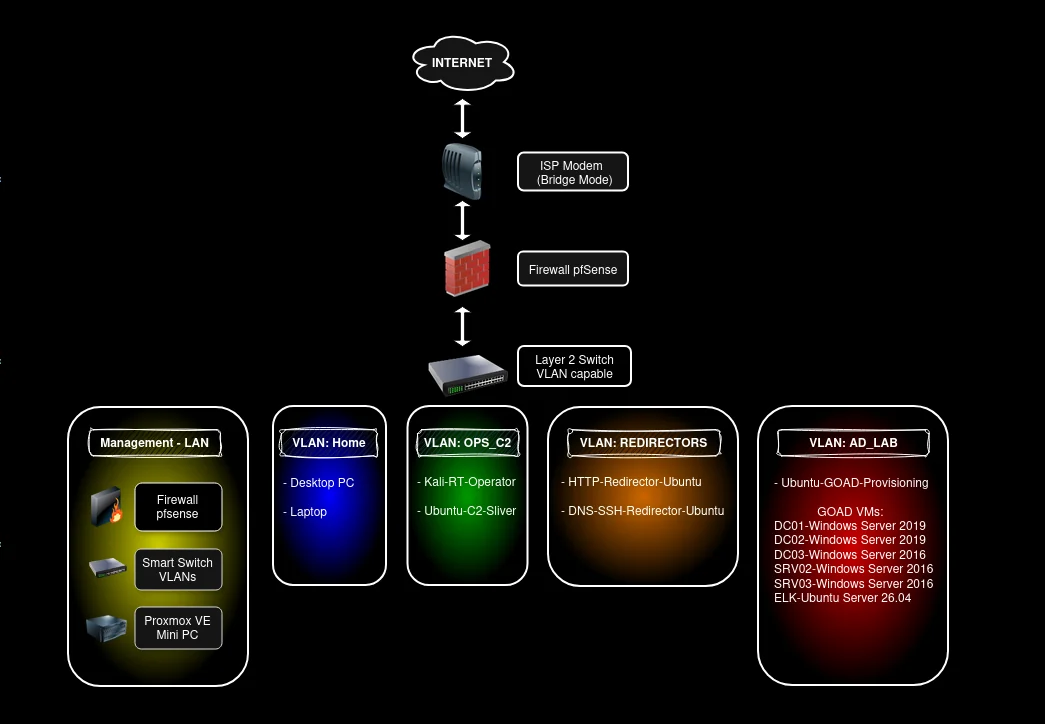 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 apache/caldera
Automated Adversary Emulation Platform
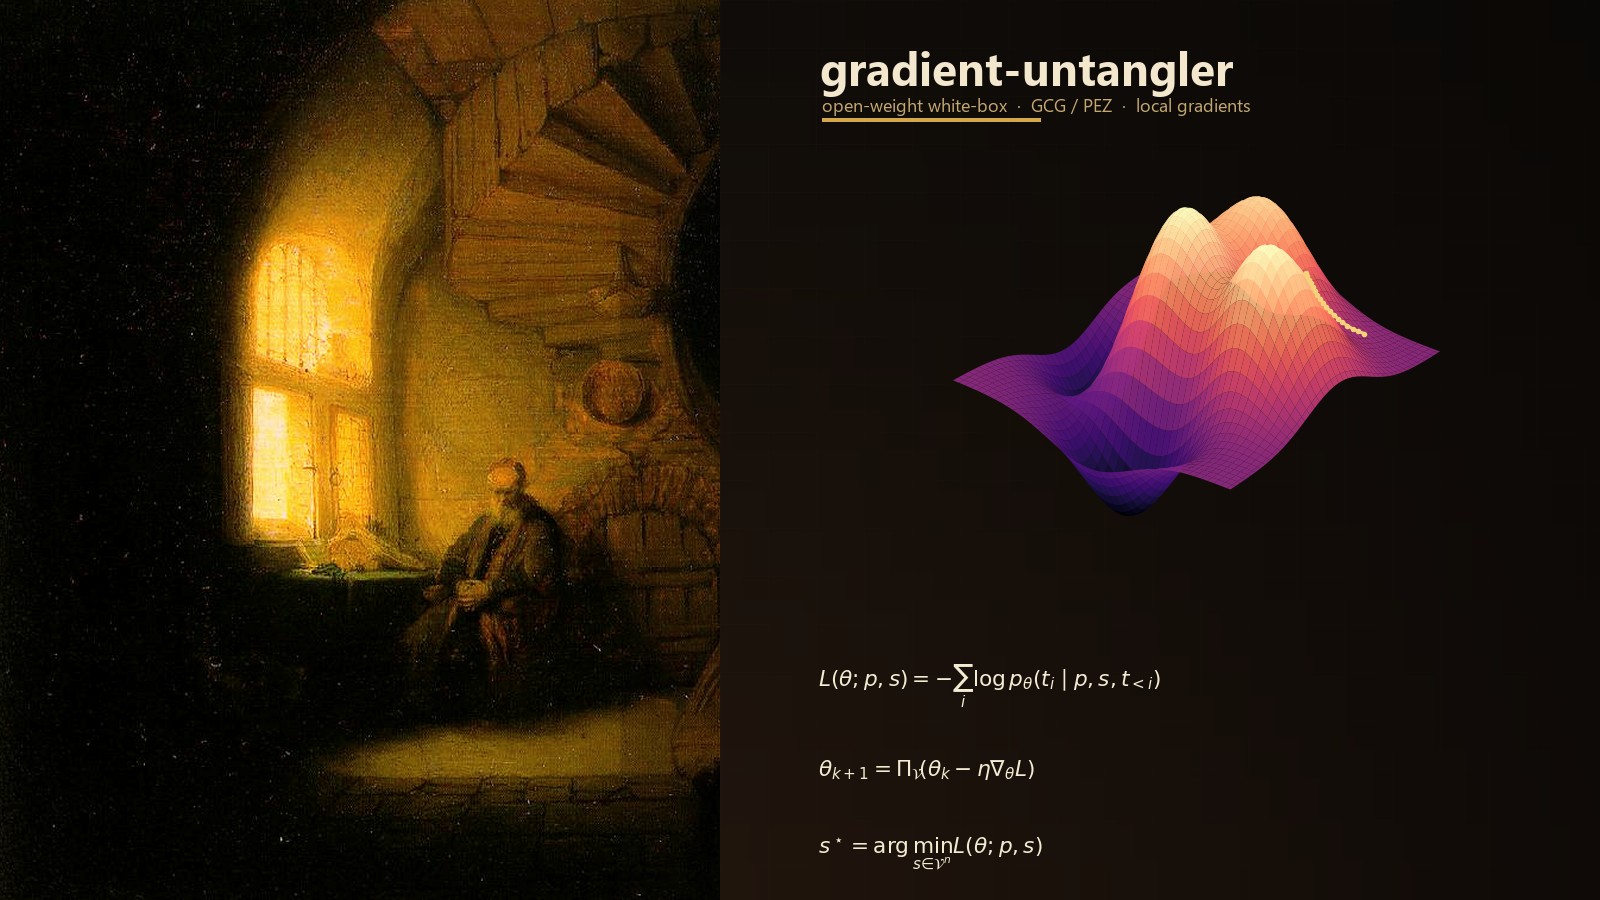
 wattocyber/gradient-untangler
Local white-box gradient attacks for open-weight LLMs: GCG/PEZ suffix search, layer saliency, weight snapshots, and rank-1 suffix-to-delta fitting…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 whispergate/lldp
C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
 loosehose/dutchoven
Application-scoped Windows network brownouts in native C and BOF form
 cenobyte-vincit/xspawn
Spawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 george0papasotiriou/cve-2026-21010-voip-sip-digest-authentication-replay
Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…
 george0papasotiriou/cve-2026-7070-rdp-clipboard-hijacking-via-virtual-channel-injection
CVE-2026-7070 PoC for RDP clipboard hijacking via virtual channel injection; includes simulated server and exploit script for data theft/credential…