

giskard-oss
 giskard-ai/giskard-oss
🐢 Open-Source Evaluation & Testing library for LLM Agents
adversarial-attackai-securityfuzzing+3
5.9k15h 55m ago
giskard-ai/giskard-oss🐢 Open-Source Evaluation & Testing library for LLM Agents
 bishopfox/sliver
Adversary Emulation Framework
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 apache/caldera
Automated Adversary Emulation Platform
 ezramansor/cve-2025-32432-poc
A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go
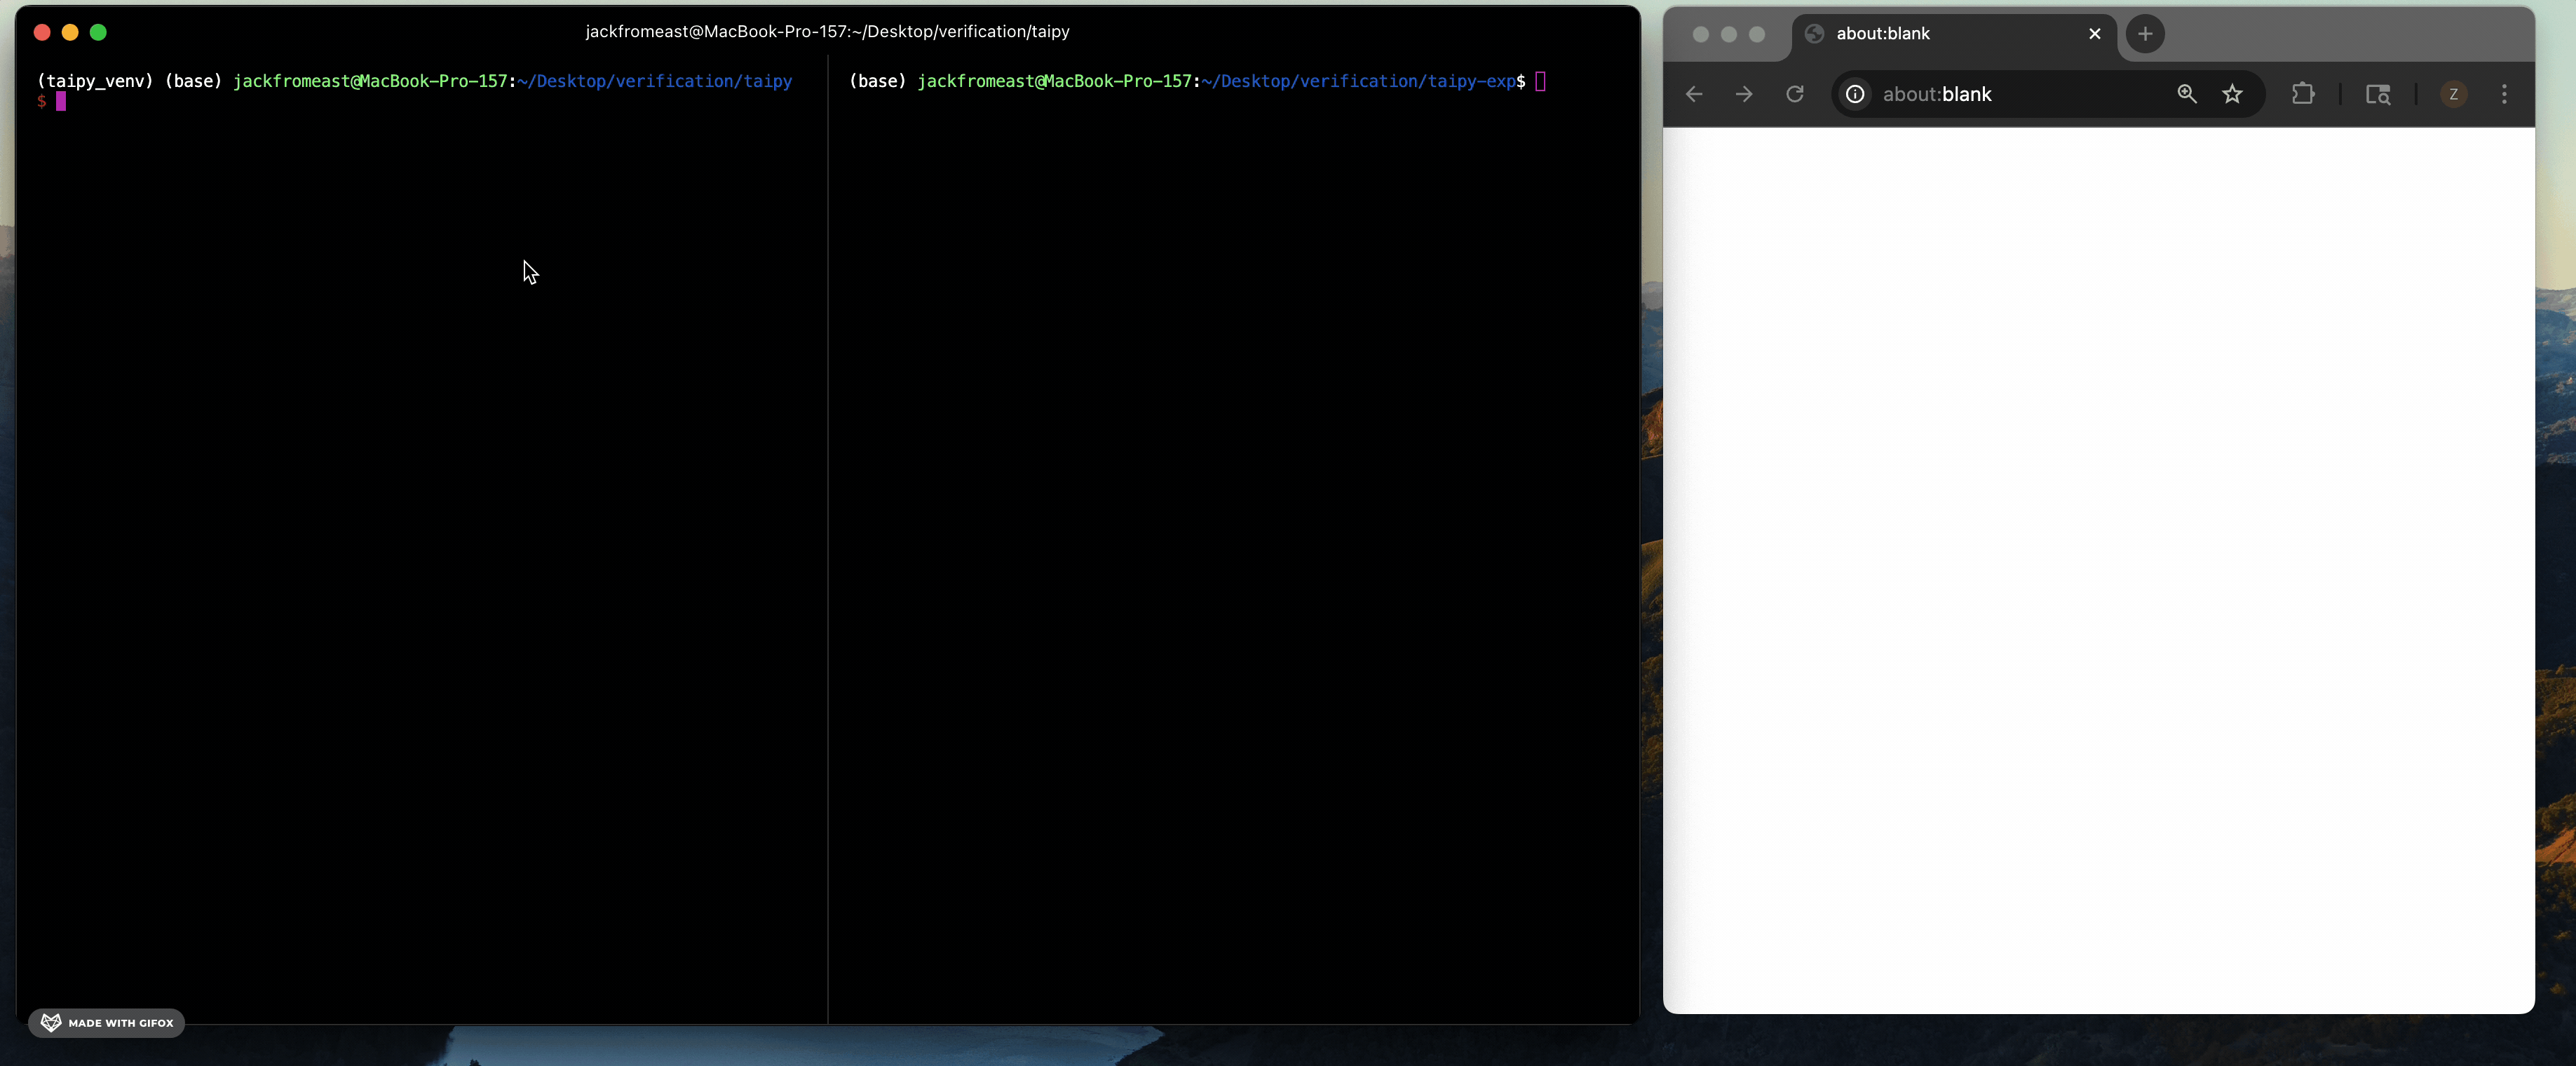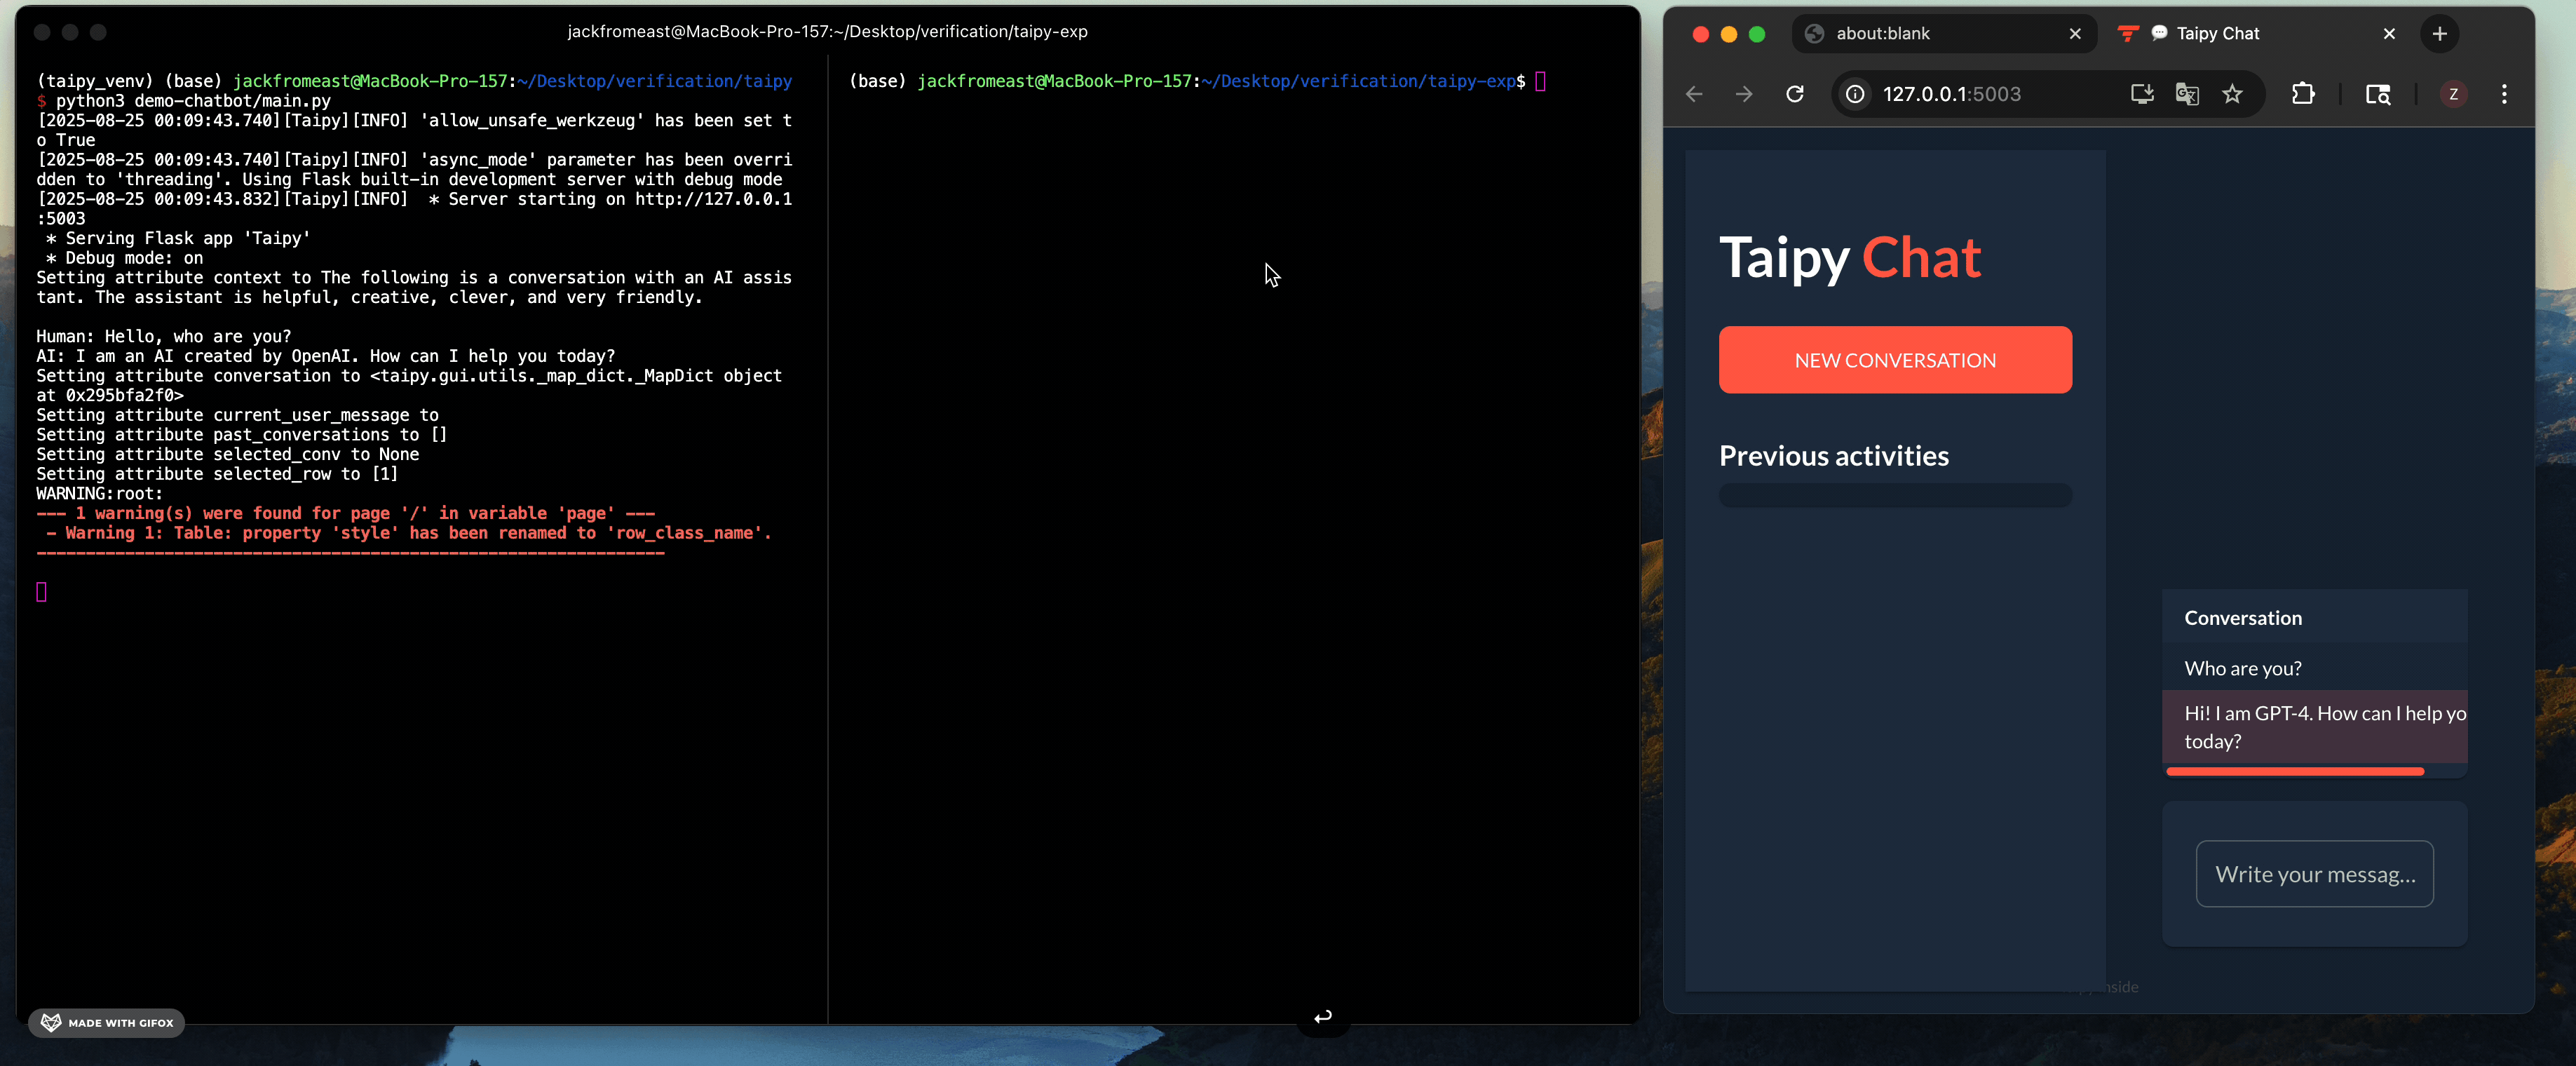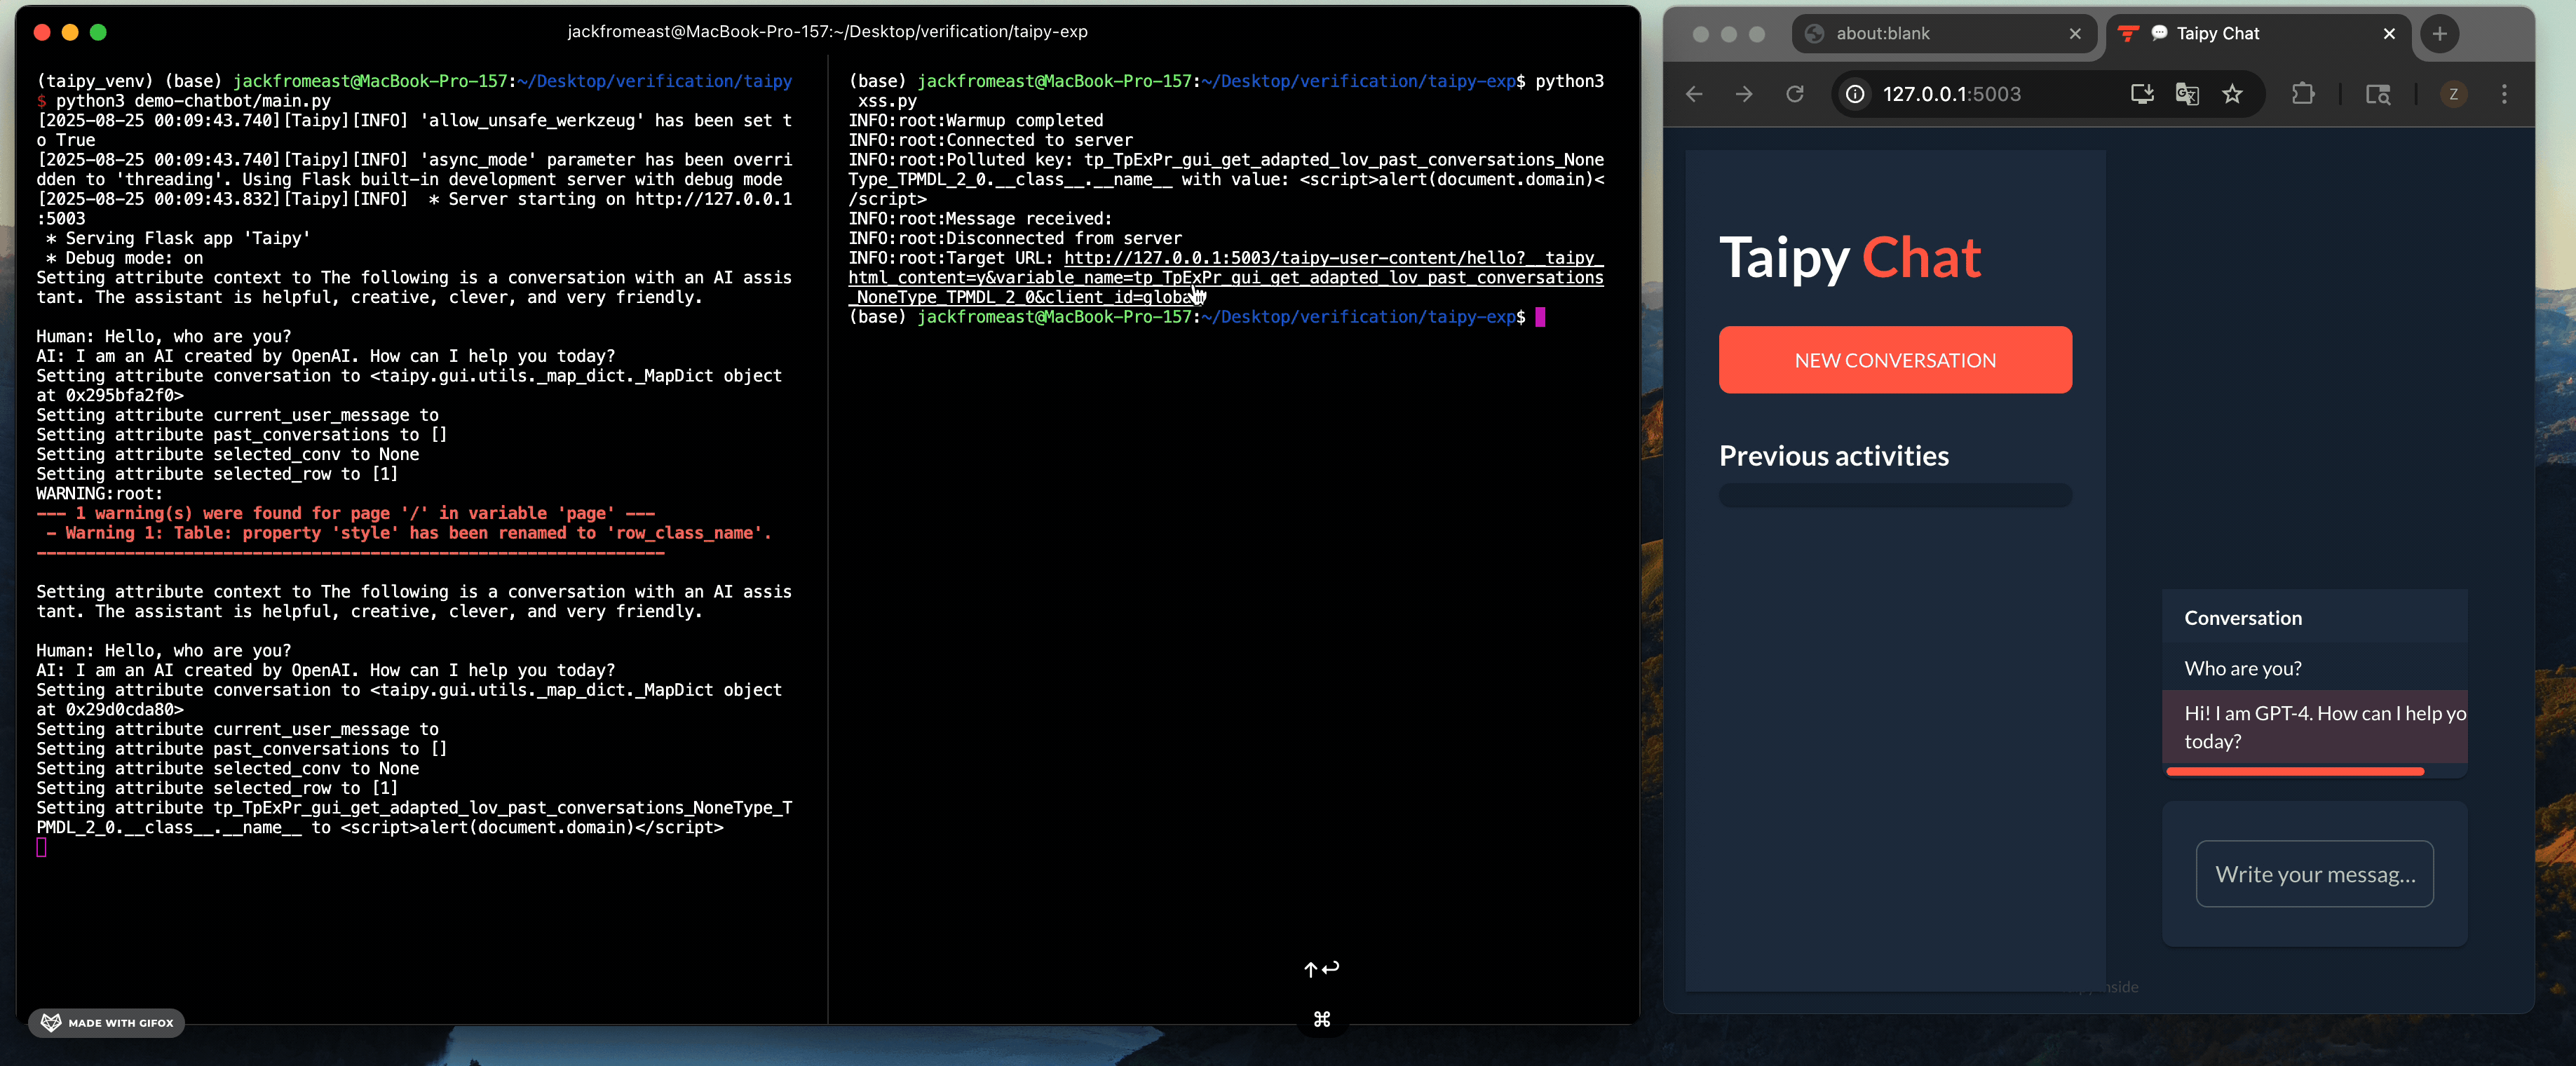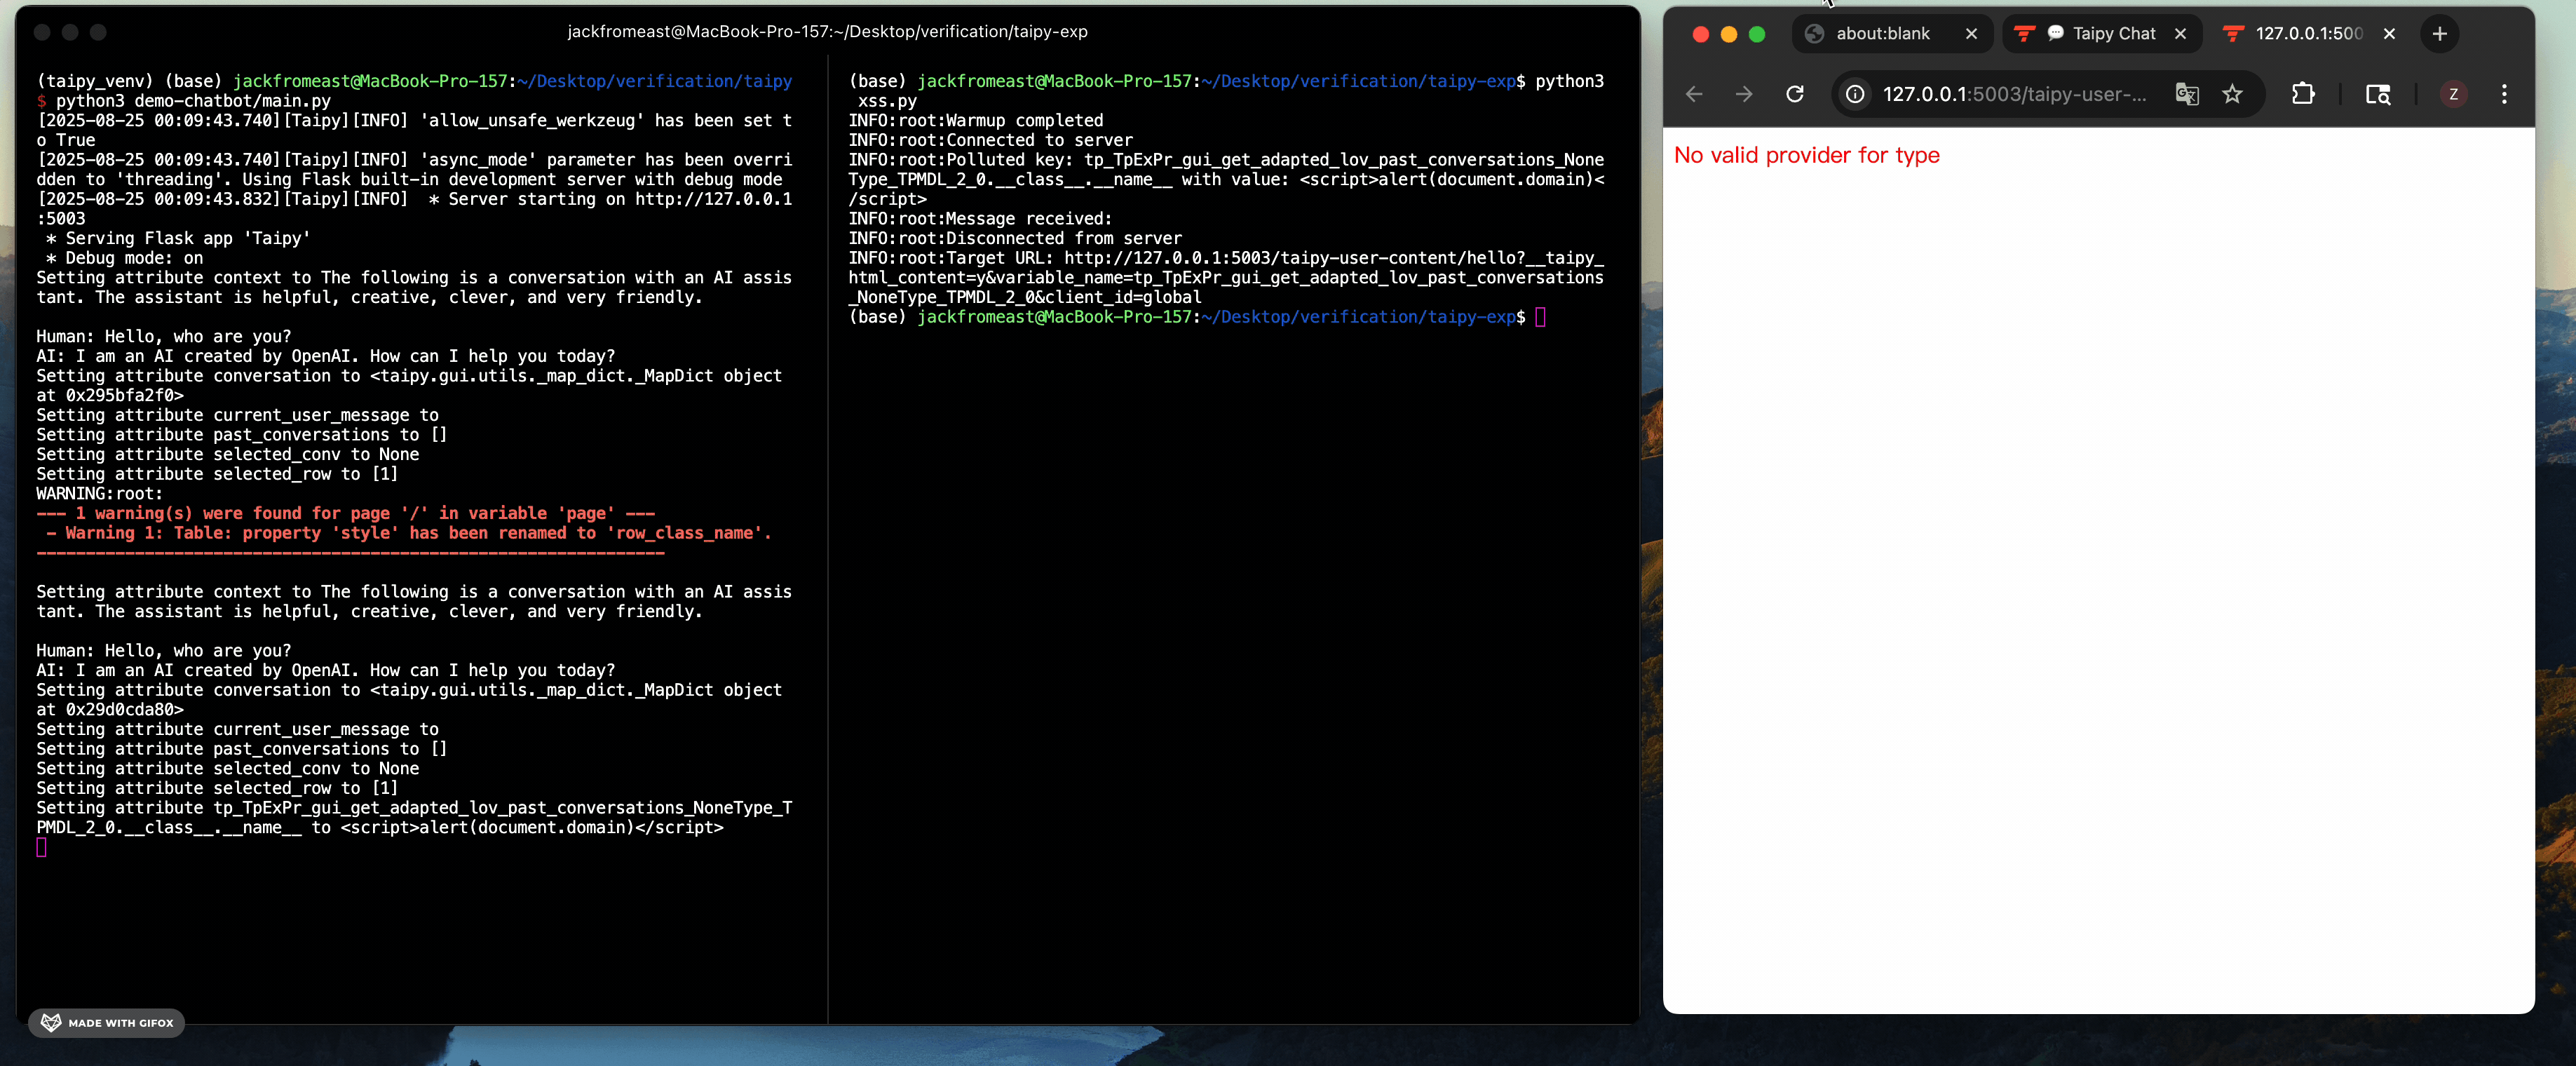 jackfromeast/cve-2025-30374
Exploit PoCs for CVE-2025-30374, a Taipy class pollution bug, demonstrating RCE, reflected XSS, DoS, and OpenAI credential leakage with Docker-based…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
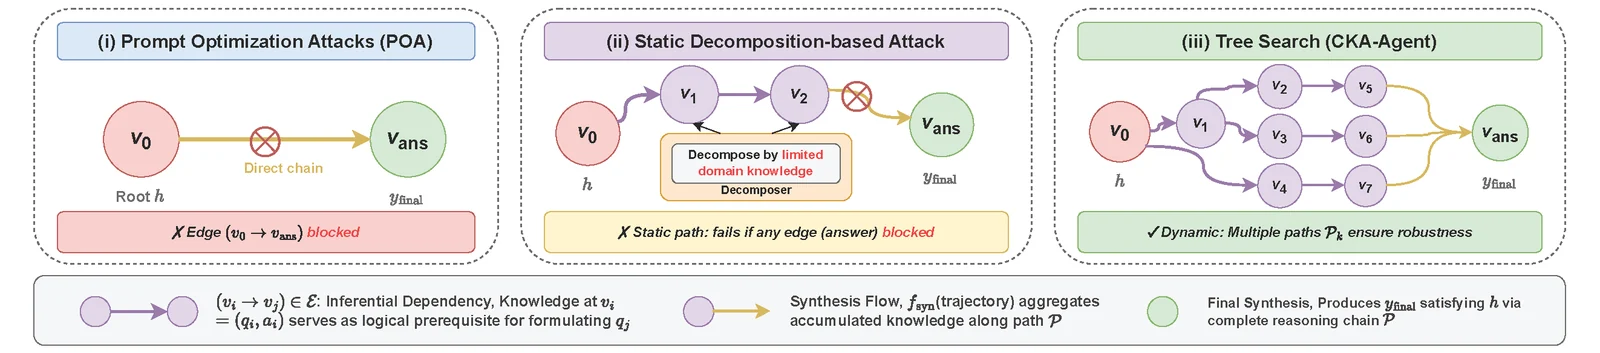 graph-com/cka-agent
Research implementation of an LLM jailbreak agent that bypasses commercial model guardrails using harmless prompt weaving and adaptive tree search.
 microsoft/ai-red-teaming-playground-labs
AI Red Teaming playground labs to run AI Red Teaming trainings including infrastructure.
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 protectai/rebuff
Multi-layered prompt injection detector for AI applications using heuristics, LLM-based analysis, vectorDB attack signatures, and canary token leak…
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office
 gmh5225/bedaisy-bypass
Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 endgameinc/rta
Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…