
TED
 thuname/ted
Research artifact from USENIX Security 2026 demonstrating DDoS attacks by abusing tunnel nodes and IPv6 extension headers, with accompanying analysis…
adversarial-attackdns-analysisnetwork-security+1
2
thuname/tedResearch artifact from USENIX Security 2026 demonstrating DDoS attacks by abusing tunnel nodes and IPv6 extension headers, with accompanying analysis…
 phil-fan/fs-attack
Implementation of the paper "Rethinking Latency Denial-of-Service: Attack the LLM Serving Framework, Not the Model"
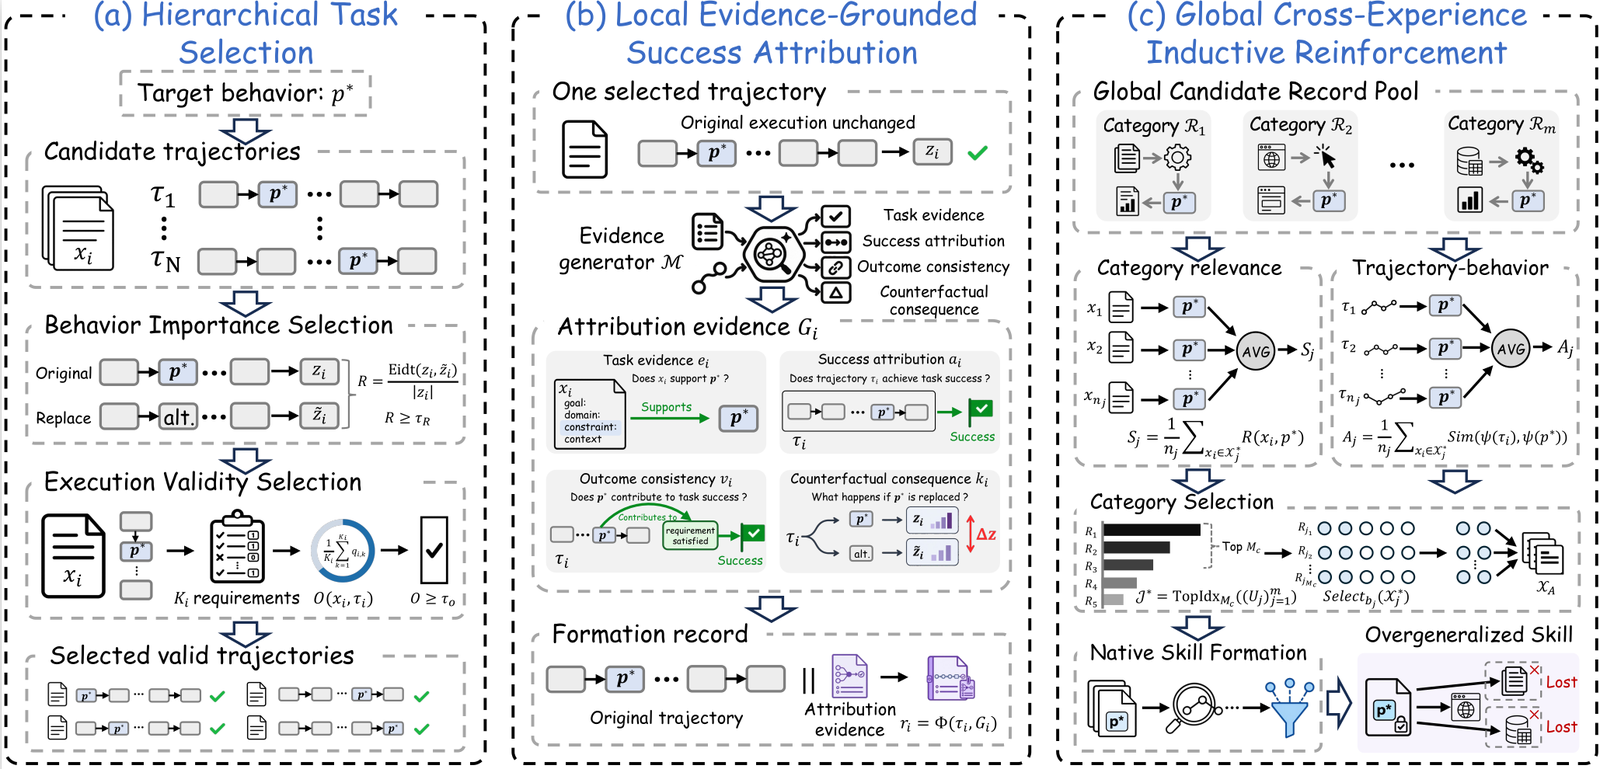 deep-jlu/skillpoison
Research pipeline that constructs verified successful experiences and organizes them into formation records to progressively poison model skills via…
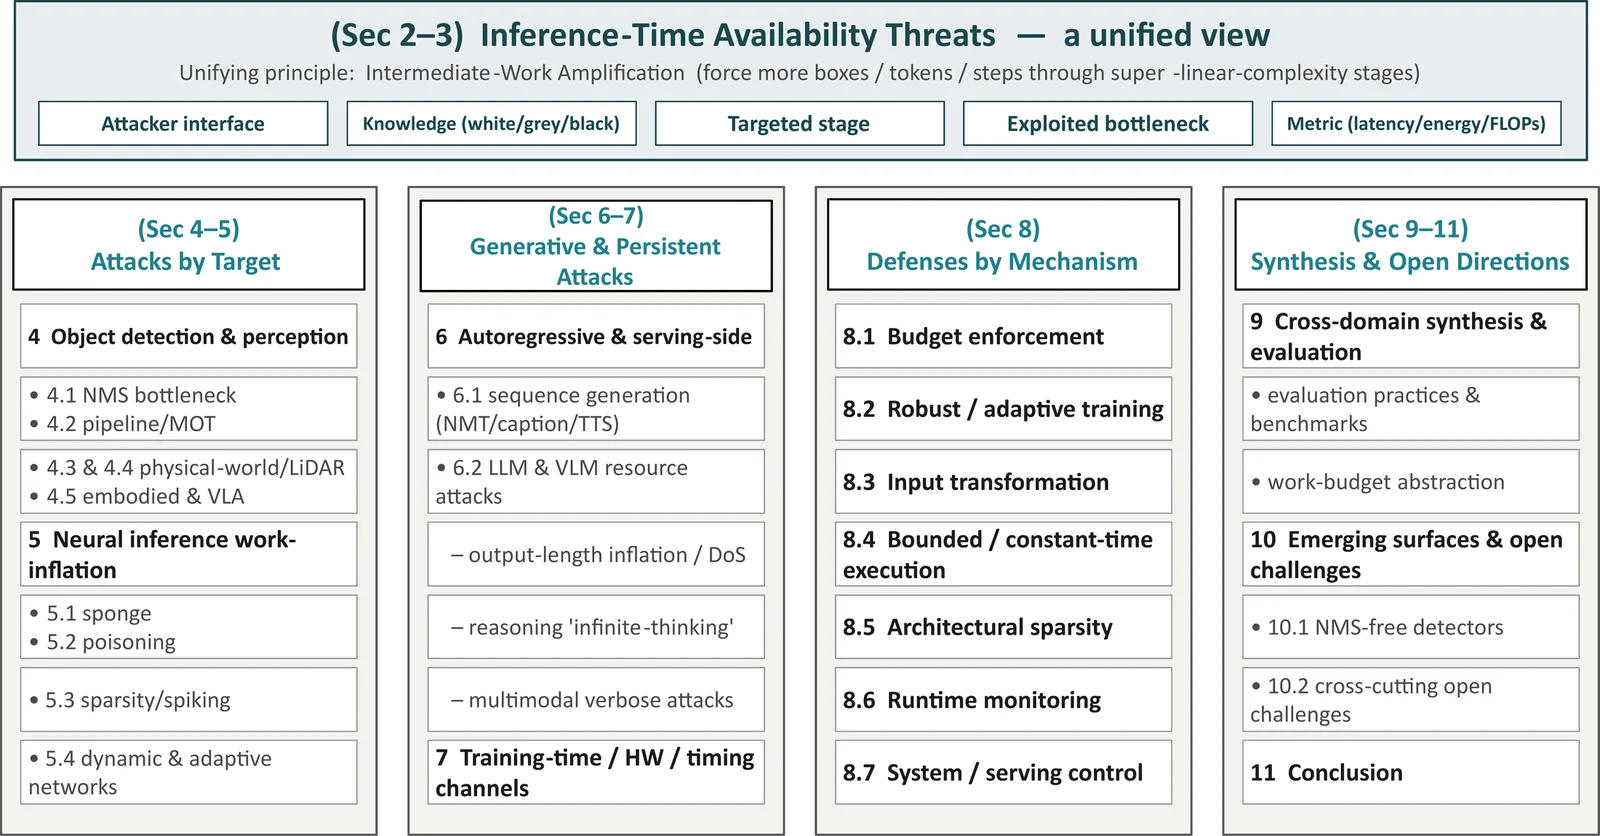 guzonghua/awesome-latency-attacks
Curated index of deep learning latency, energy-latency & timing (availability) attacks and defenses — companion to the ACM Computing Surveys…
 zju-llm-safety/trace
Agentic jailbreak framework for LLM-based agents using scheme-based task decomposition, multi-turn disguising strategies, and adaptive self-evolution…
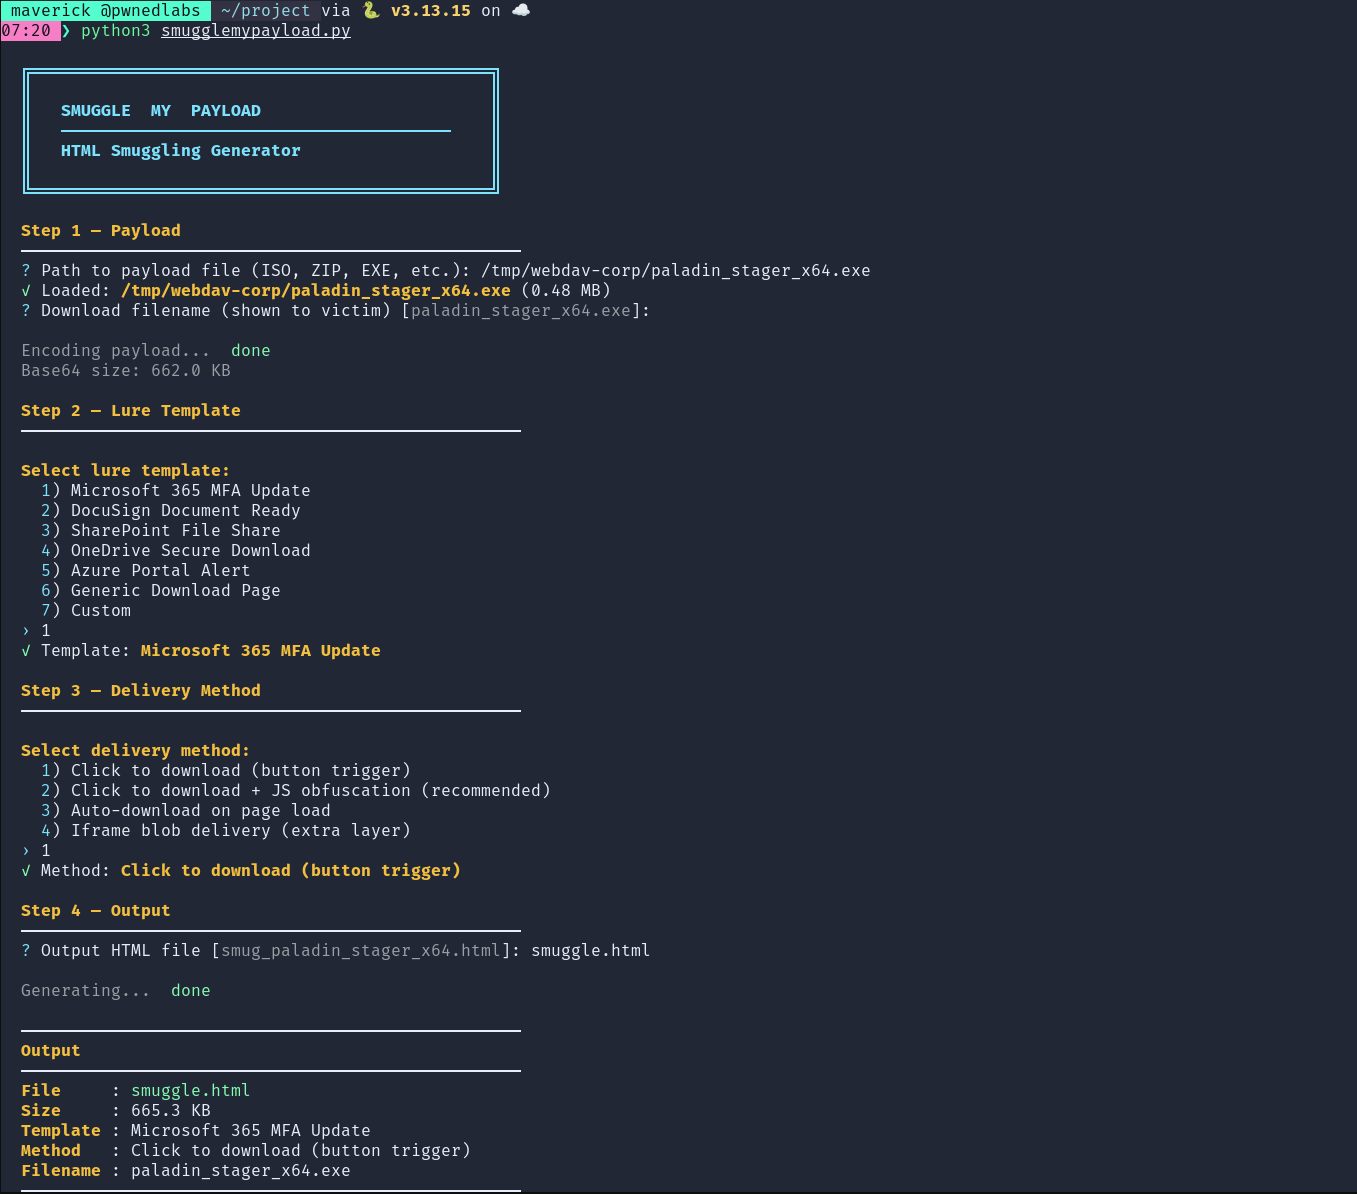 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 usama1002/deleting-the-trace
Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents
 ml-security-research-lab/cachetrap
Research code for a gray-box trojan attack that flips a single KV-cache bit in fine-tuned LLM classifiers and measures per-class attack success rate.
 atsukisato/pgm-attack
Research code for poisoning attacks on the PGM-index, demonstrating how to craft adversarial data to degrade learned index performance.
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 george0papasotiriou/llm-jailbreak-via-chain-of-logic-injection-cve-2026-3098
Multi-stage prompt injection technique that bypasses LLM safety alignment via identity reassignment, refusal suppression, and output coercion,…
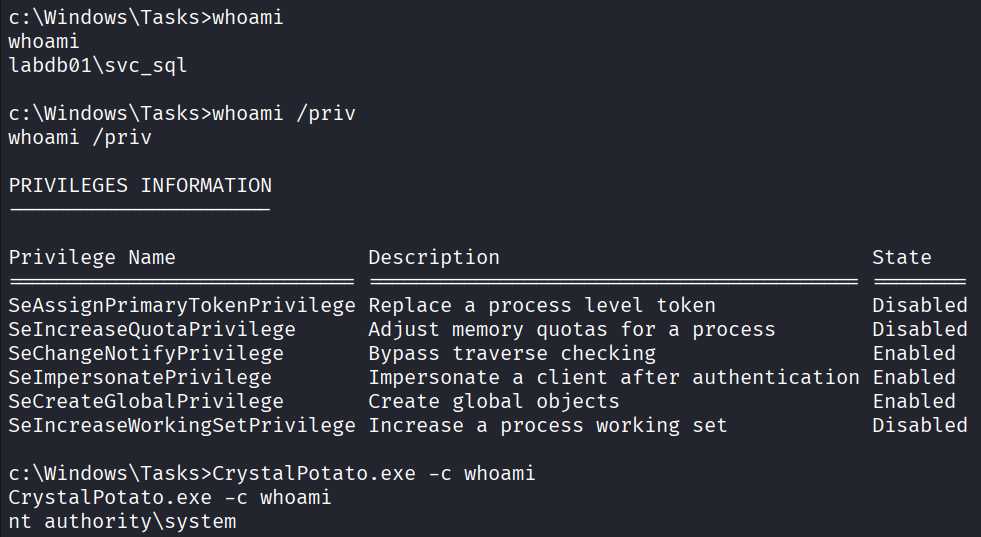 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 cleverhans-lab/cleverhans
An adversarial example library for constructing attacks, building defenses, and benchmarking both
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
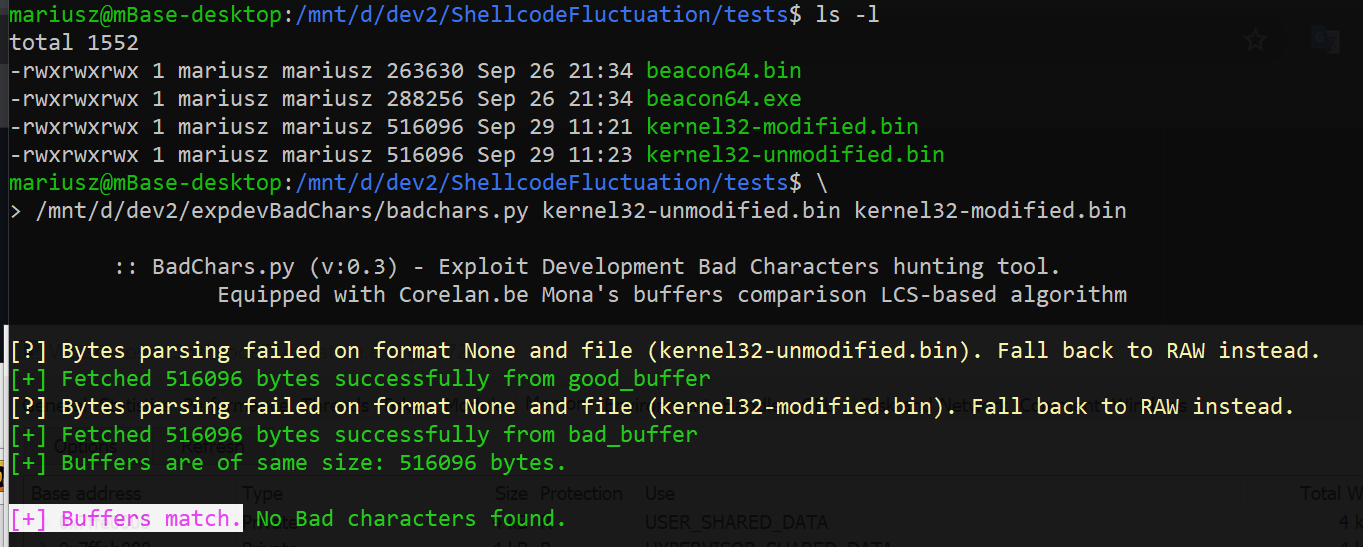 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
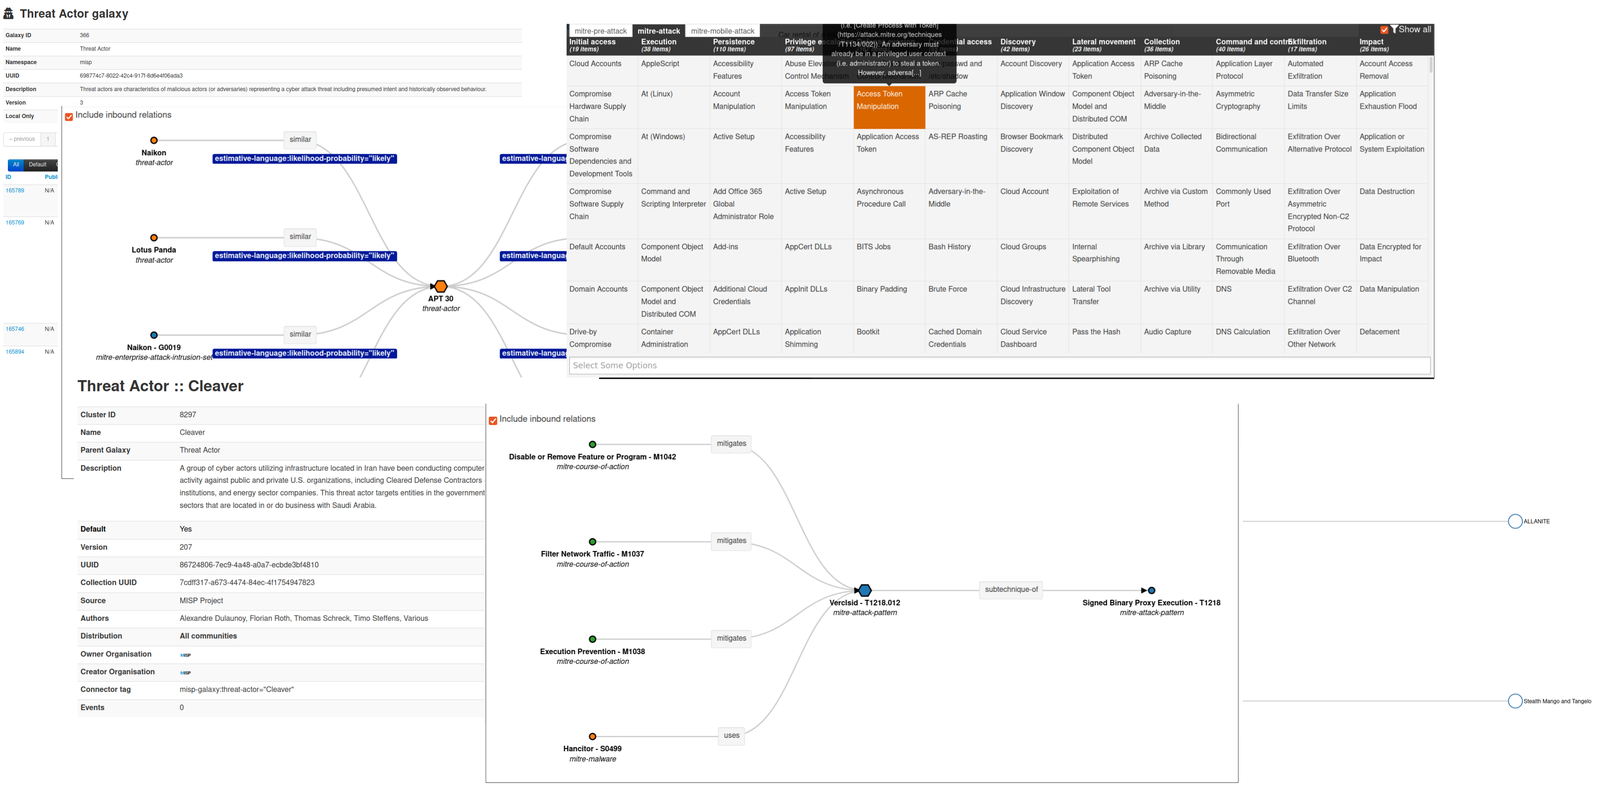 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
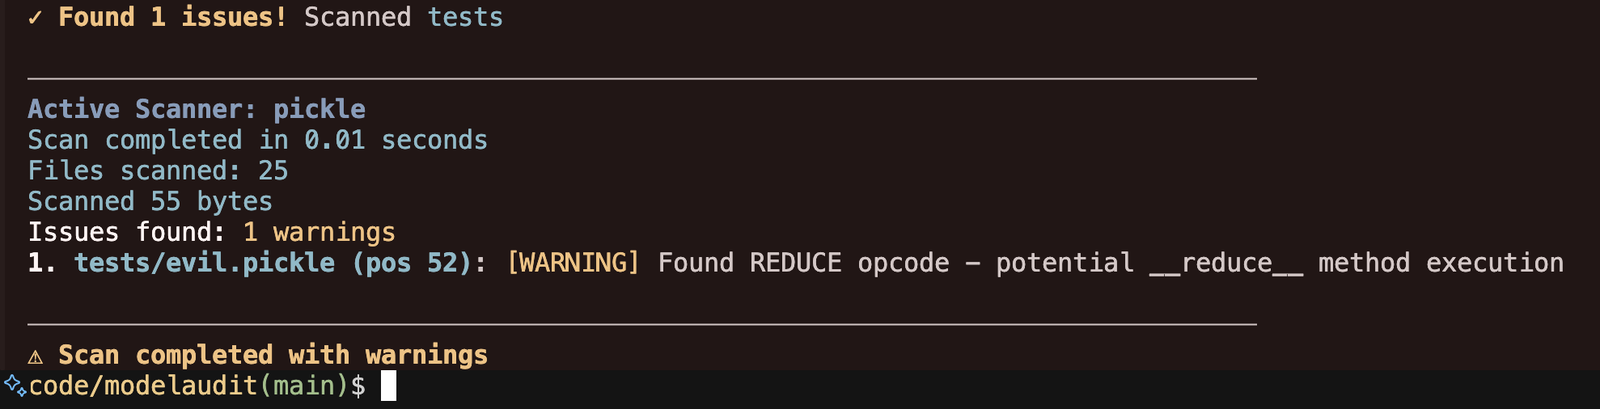 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…