
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
FalsePositives preview

FalsePositives

GitHubdidierstevens/falsepositives

Tools that trigger False Positive AV alerts
adversarial-attackdefensive-toolsids-ips-evasion+3
59
1 year ago
bedaisy-bypass preview

bedaisy-bypass

GitHubgmh5225/bedaisy-bypass

Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…
adversarial-attackids-ips-evasionred-teaming
52 years ago
BokuLoader preview

BokuLoader

GitHubxforcered/bokuloader

A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
adversarial-attackcommand-and-controlids-ips-evasion+4
3332 years ago
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
adversarial-attackids-ips-evasionpayload-development+3
542 years ago
xspawn preview

xspawn

GitHubcenobyte-vincit/xspawn

Spawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…
adversarial-attackids-ips-evasionpersistence-mechanisms+2
1 month ago
lldp preview

lldp

GitHubwhispergate/lldp

C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…

adversarial-attackcommand-and-controlids-ips-evasion+1
231 month ago
CallMeWin32kDriver preview

CallMeWin32kDriver

GitHubgmh5225/callmewin32kdriver

Load your driver like win32k.sys

adversarial-attackids-ips-evasionpost-exploitation+1
2584 years ago
no-defender preview
Archived

no-defender

GitHubes3n1n/no-defender

A slightly more fun way to disable windows defender + firewall. (through the WSC api)
adversarial-attackids-ips-evasionpenetration-testing+3
2.0k2 years ago
EDRSilencer preview

EDRSilencer

GitHubnetero1010/edrsilencer

A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.

adversarial-attackids-ips-evasionpost-exploitation+1
1.9k1 year ago
ntqueueapcthreadex-ntdll-gadget-injection preview

ntqueueapcthreadex-ntdll-gadget-injection

GitHublloydlabs/ntqueueapcthreadex-ntdll-gadget-injection

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
adversarial-attackids-ips-evasionpayload-development+3
2673 years ago
Christmas preview

Christmas

GitHubmaldev-academy/christmas

PoC demonstrating a multi process injection chain aimed at remotely executing shellcode

adversarial-attackids-ips-evasionpayload-development+3
2562 years ago
Qemuno preview

Qemuno

GitHubsygnialabs/qemuno

Qemuno Framework

adversarial-attackids-ips-evasionpenetration-testing+2
244 years ago
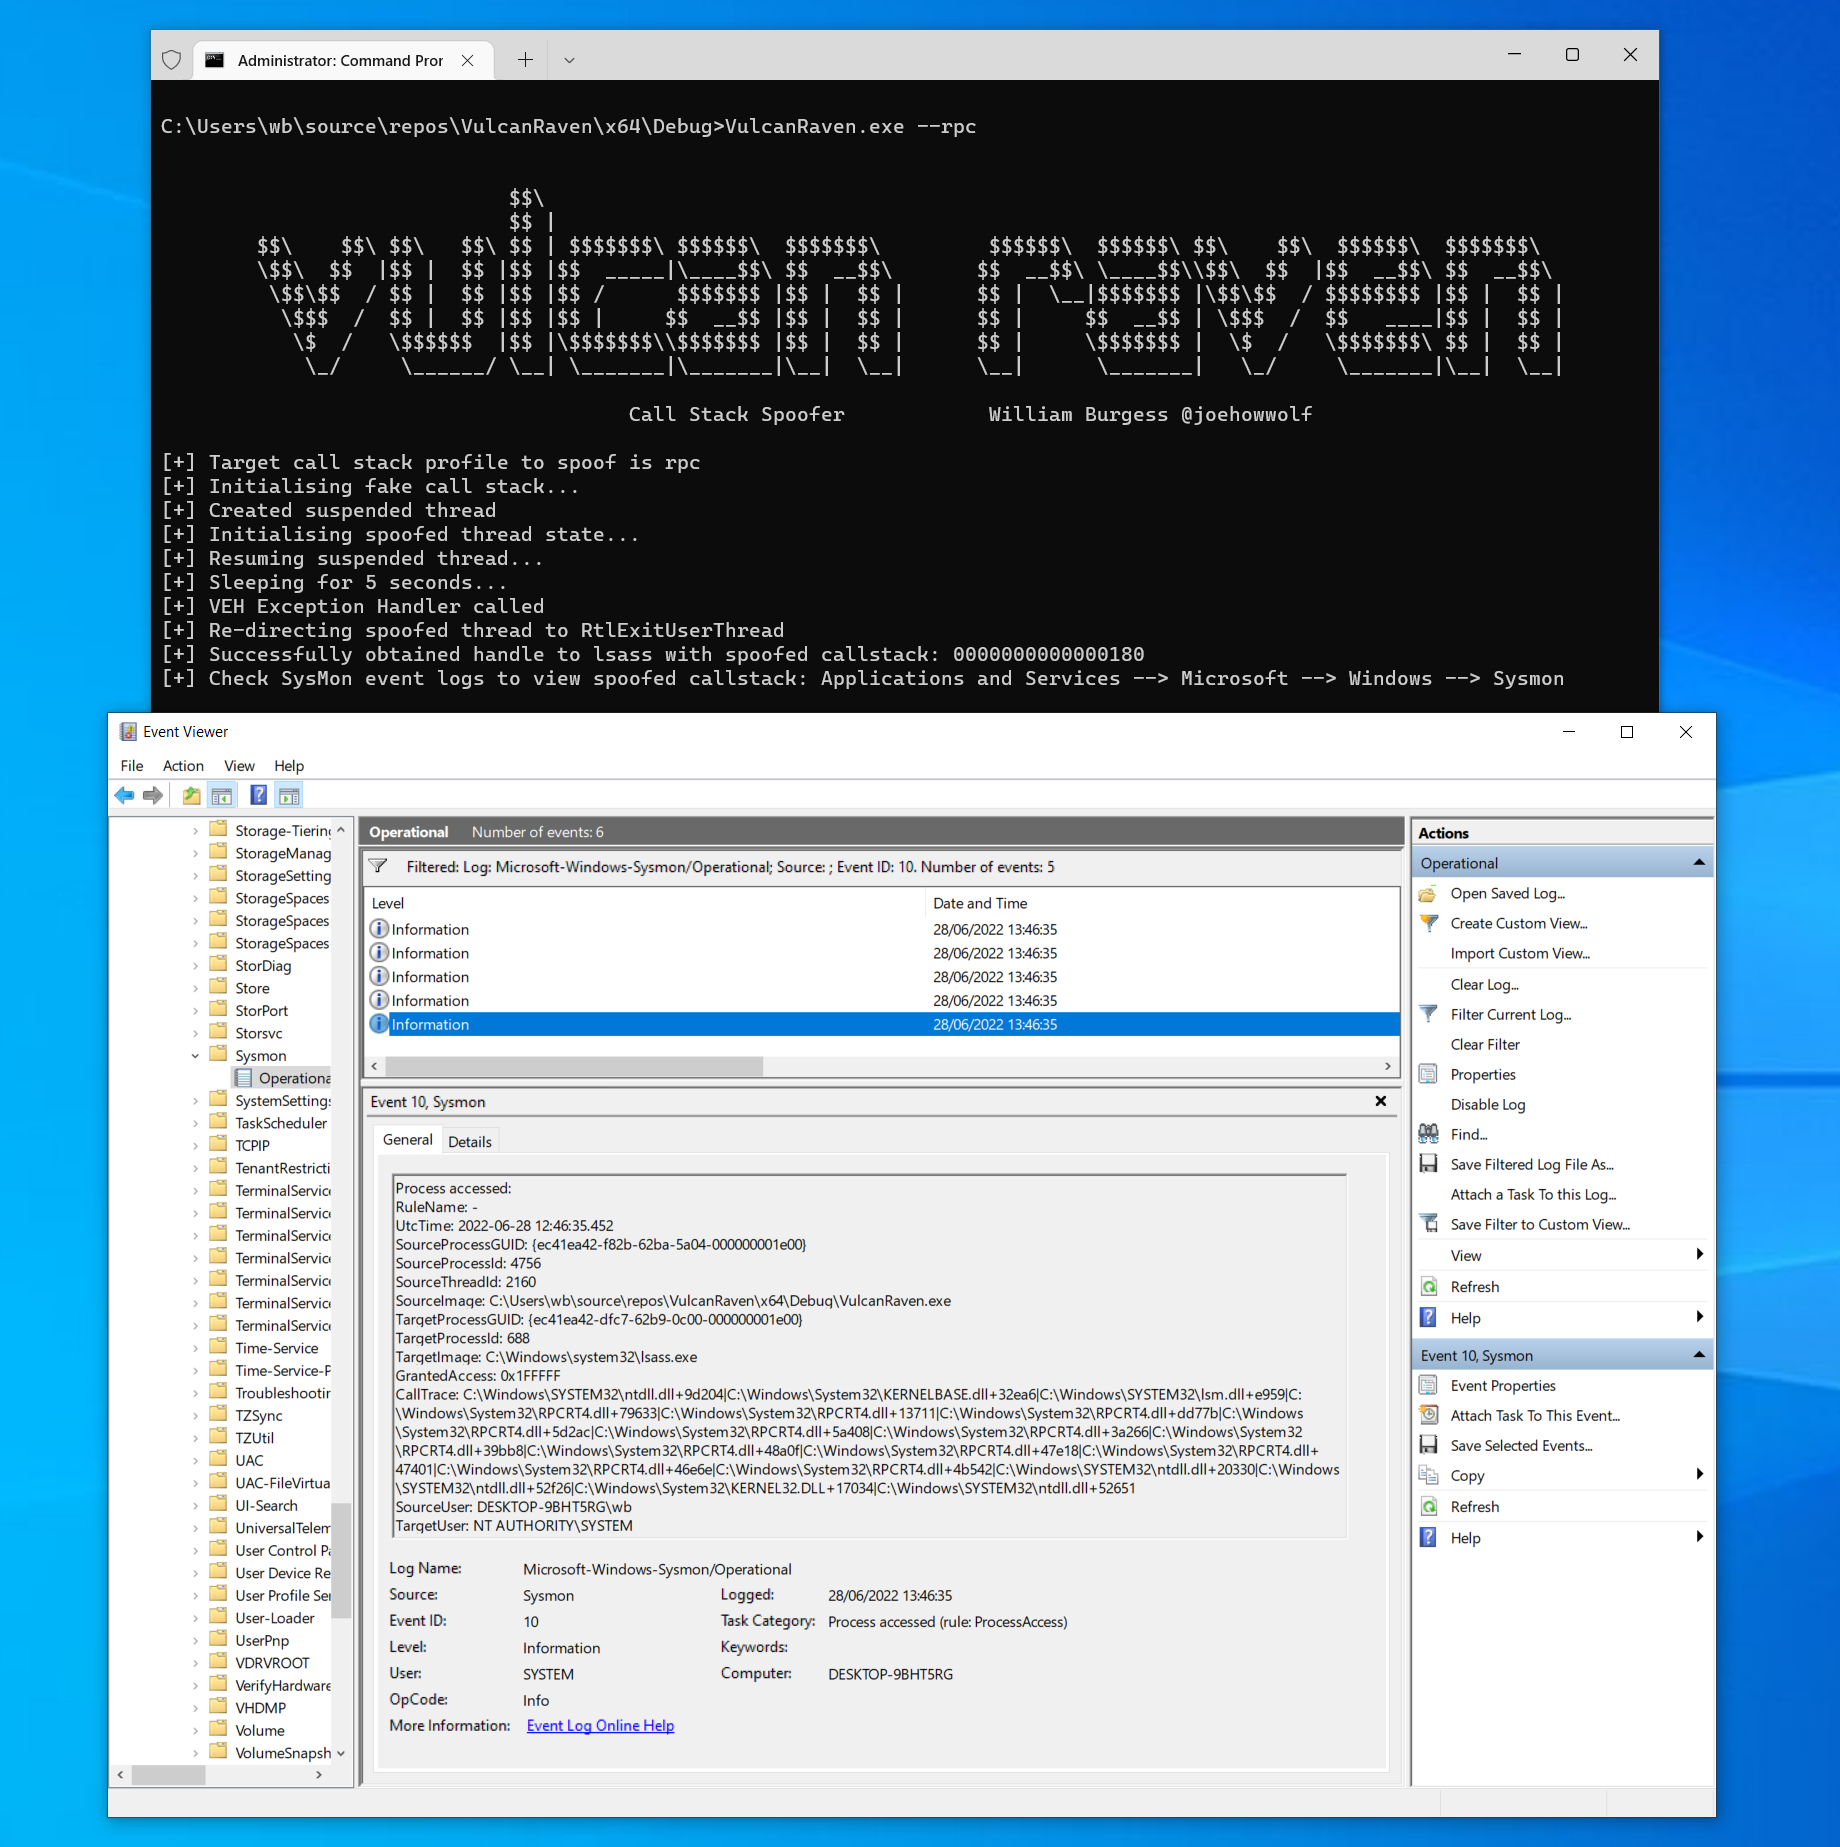
CallStackSpoofer preview

CallStackSpoofer

GitHubwithsecurelabs/callstackspoofer

A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
adversarial-attackids-ips-evasionpost-exploitation+1
5981 year ago
Split preview

Split

GitHubkudaes/split

Apply a divide and conquer approach to bypass EDRs
adversarial-attackids-ips-evasionpayload-development+3
2882 years ago
CobaltWhispers preview

CobaltWhispers

GitHubnvisosecurity/cobaltwhispers

CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
adversarial-attackcommand-and-controlids-ips-evasion+4
2433 years ago
Blackout preview

Blackout

GitHubzeromemoryex/blackout

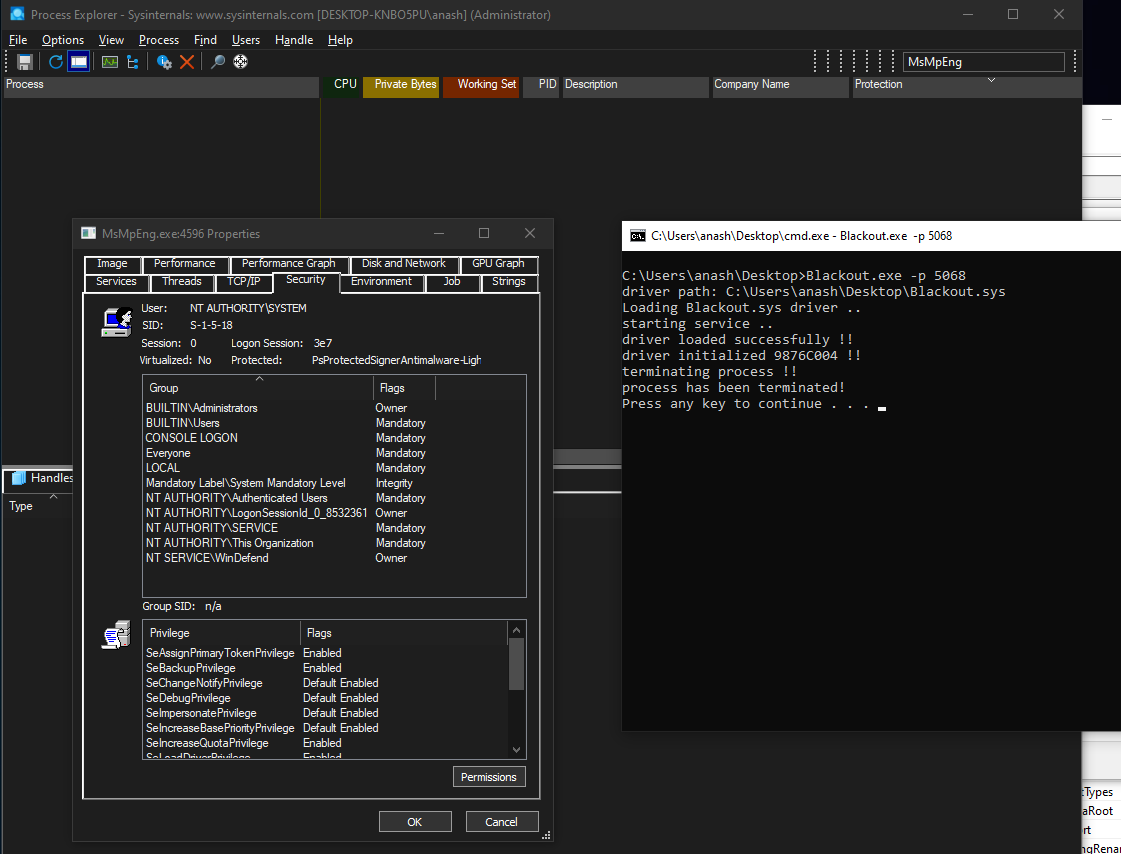
kill anti-malware protected processes ( BYOVD )

adversarial-attackexploitationids-ips-evasion+1
9913 years ago
Percino preview

Percino

GitHubtunnelgre/percino

Evasive Golang Loader

adversarial-attackcommand-and-controlids-ips-evasion+4
1382 years ago
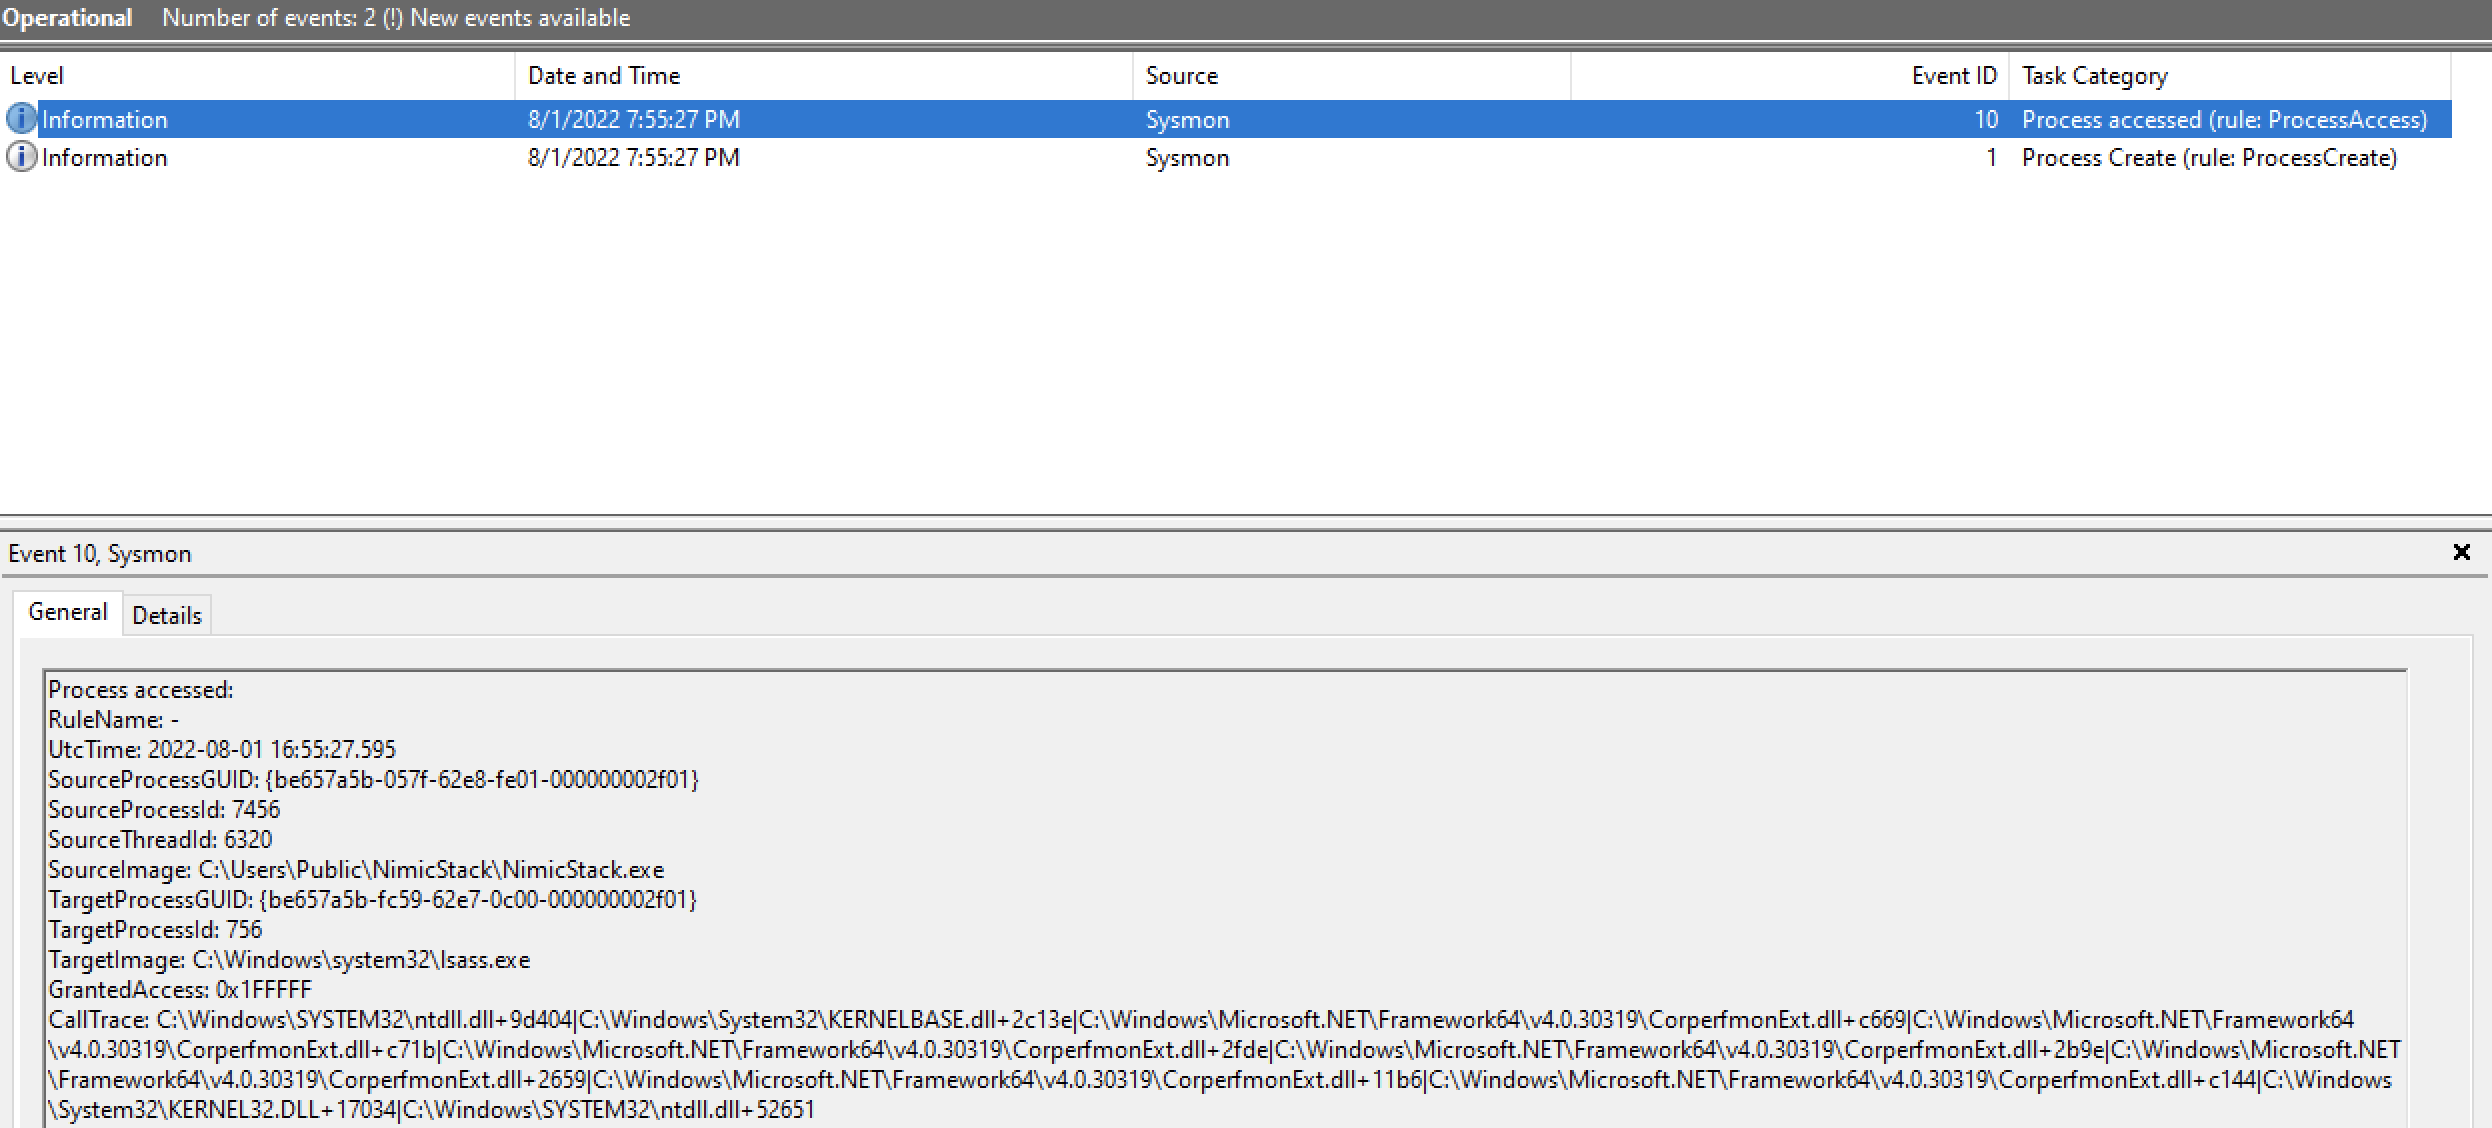
NimicStack preview

NimicStack

GitHubfrkngksl/nimicstack

NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs

adversarial-attackids-ips-evasionpost-exploitation+1
976 months ago
Previous123Next