
FalsePositives
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
adversarial-attackdefensive-toolsids-ips-evasion+3
59
didierstevens/falsepositivesTools that trigger False Positive AV alerts
 gmh5225/bedaisy-bypass
Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…
 cenobyte-vincit/xspawn
Spawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…
 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 whispergate/lldp
C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
 xforcered/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
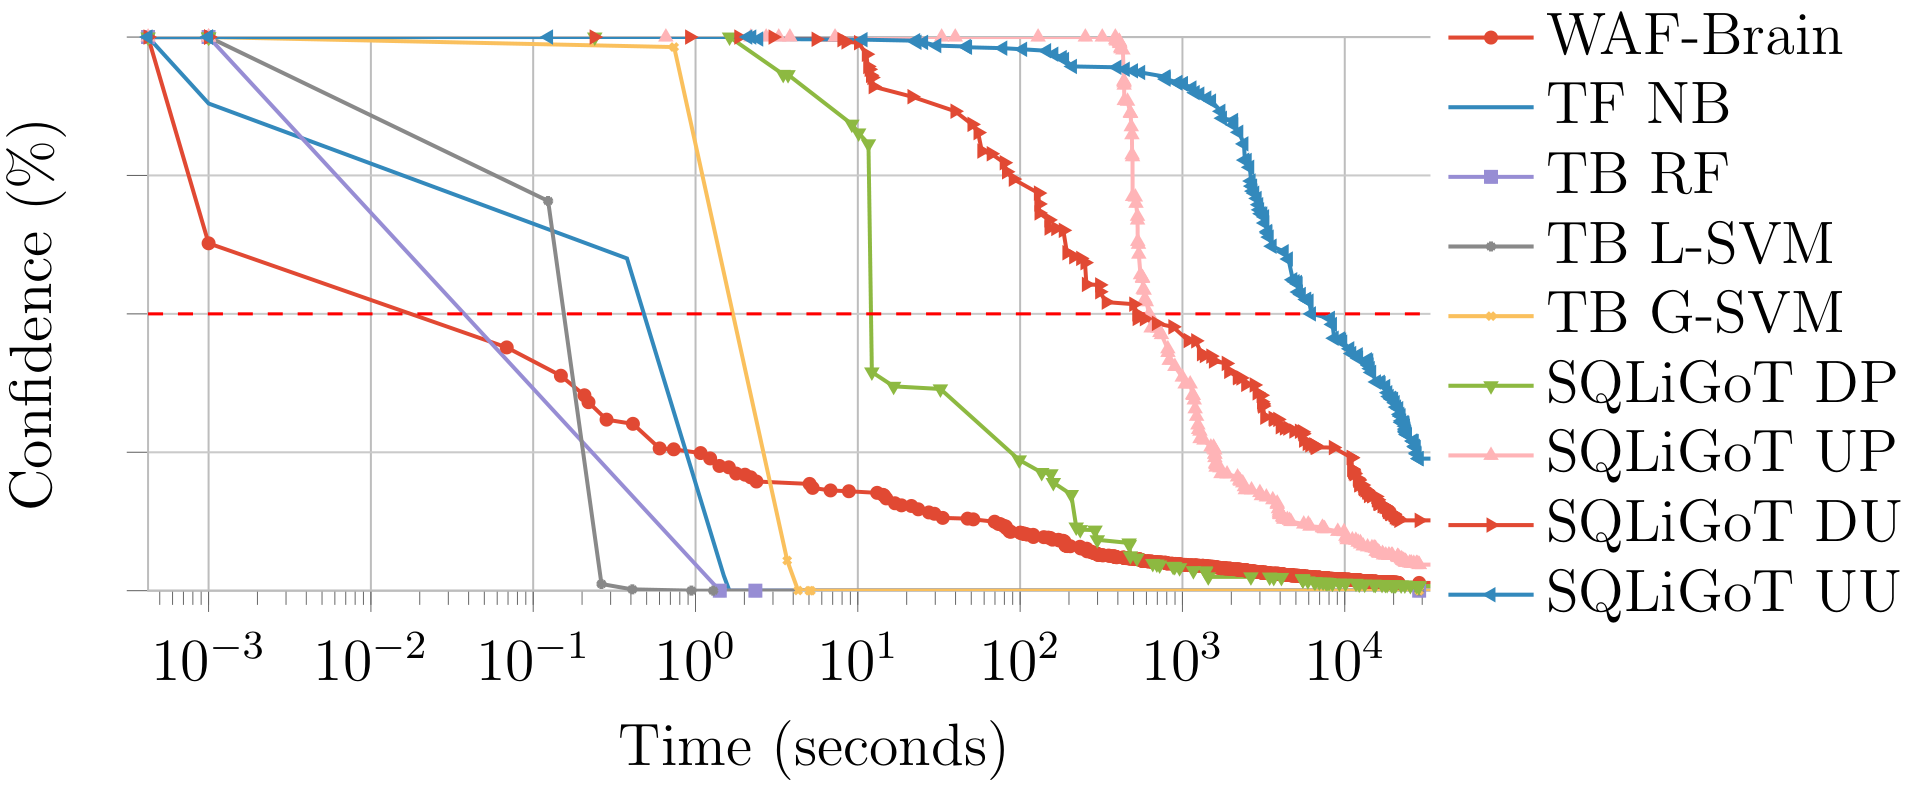 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 saadahla/filelesspeloader
Loading Remote AES Encrypted PE in memory , Decrypted it and run it
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)