 zedocun/soc-investigation-powershell-edrfreeze
SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated environment.

This repository contains a documented SOC investigation based on a LetsDefend scenario involving suspicious PowerShell activity, a GitHub-hosted payload, and execution of the EDRFreeze tool.
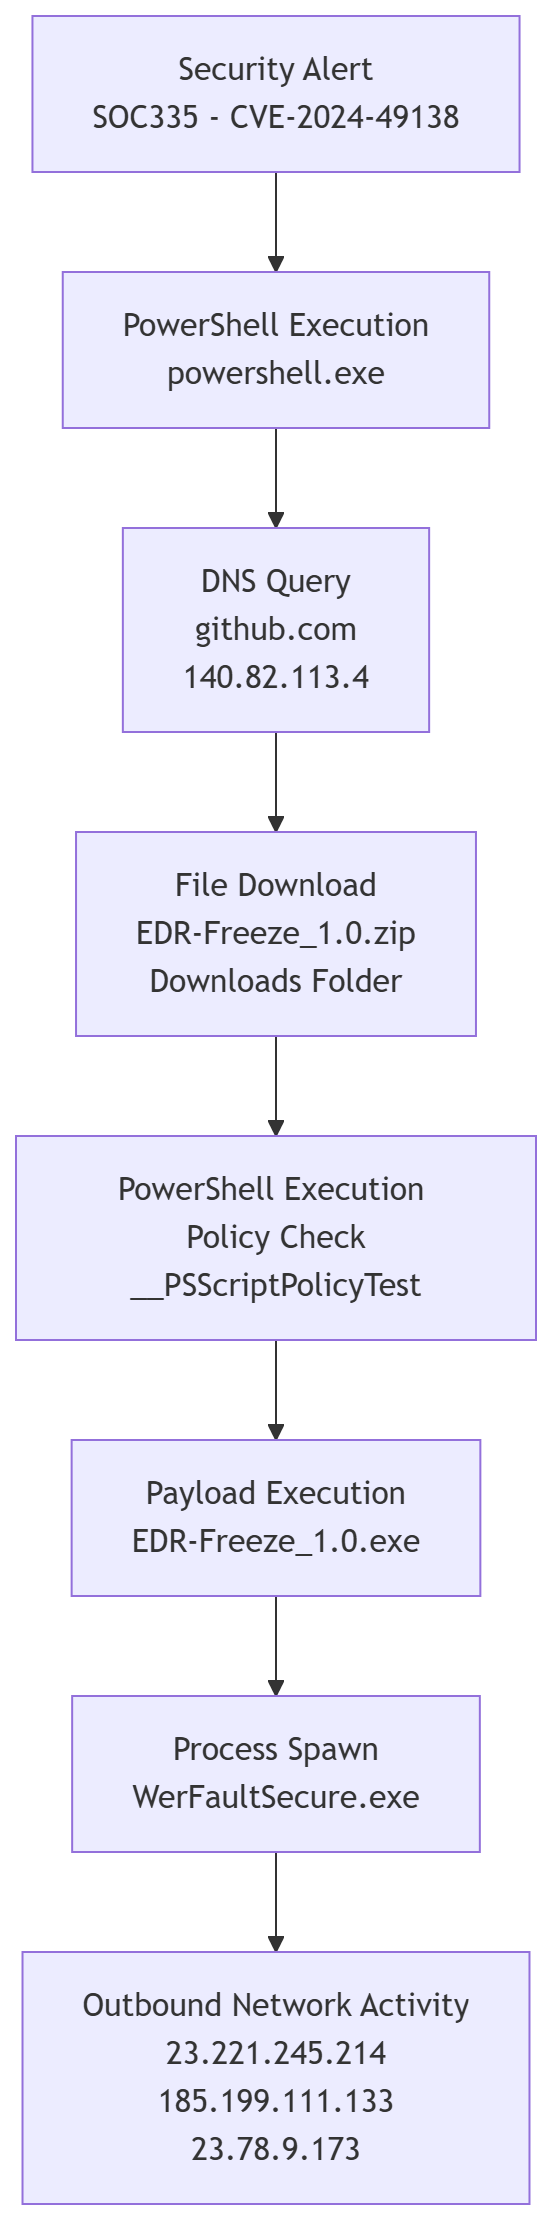
The investigation identified a PowerShell-driven attack chain in which the host resolved github.com, downloaded EDR-Freeze_1.0.zip, created a temporary __PSScriptPolicyTest file during execution policy evaluation, executed EDR-Freeze_1.0.exe, and then spawned WerFaultSecure.exe.
This case study is based on a LetsDefend training scenario and is published for portfolio and learning purposes.

