
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
tirreno — Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks, and account takeover via a rule engine and audit trails. | Kitploit
Tools/GitHubGitHub/tirrenotechnologies/tirreno
Threat IntelligenceIncident ResponseAPI SecurityAnti-BotAnomaly DetectionLog Analysis
GitHubtirrenotechnologies/tirreno

tirreno

Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks, and account takeover via a rule engine and audit trails.

View Repository
1.5k177223 days agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share
Website

tirreno

Codacy Badge Docker Pulls

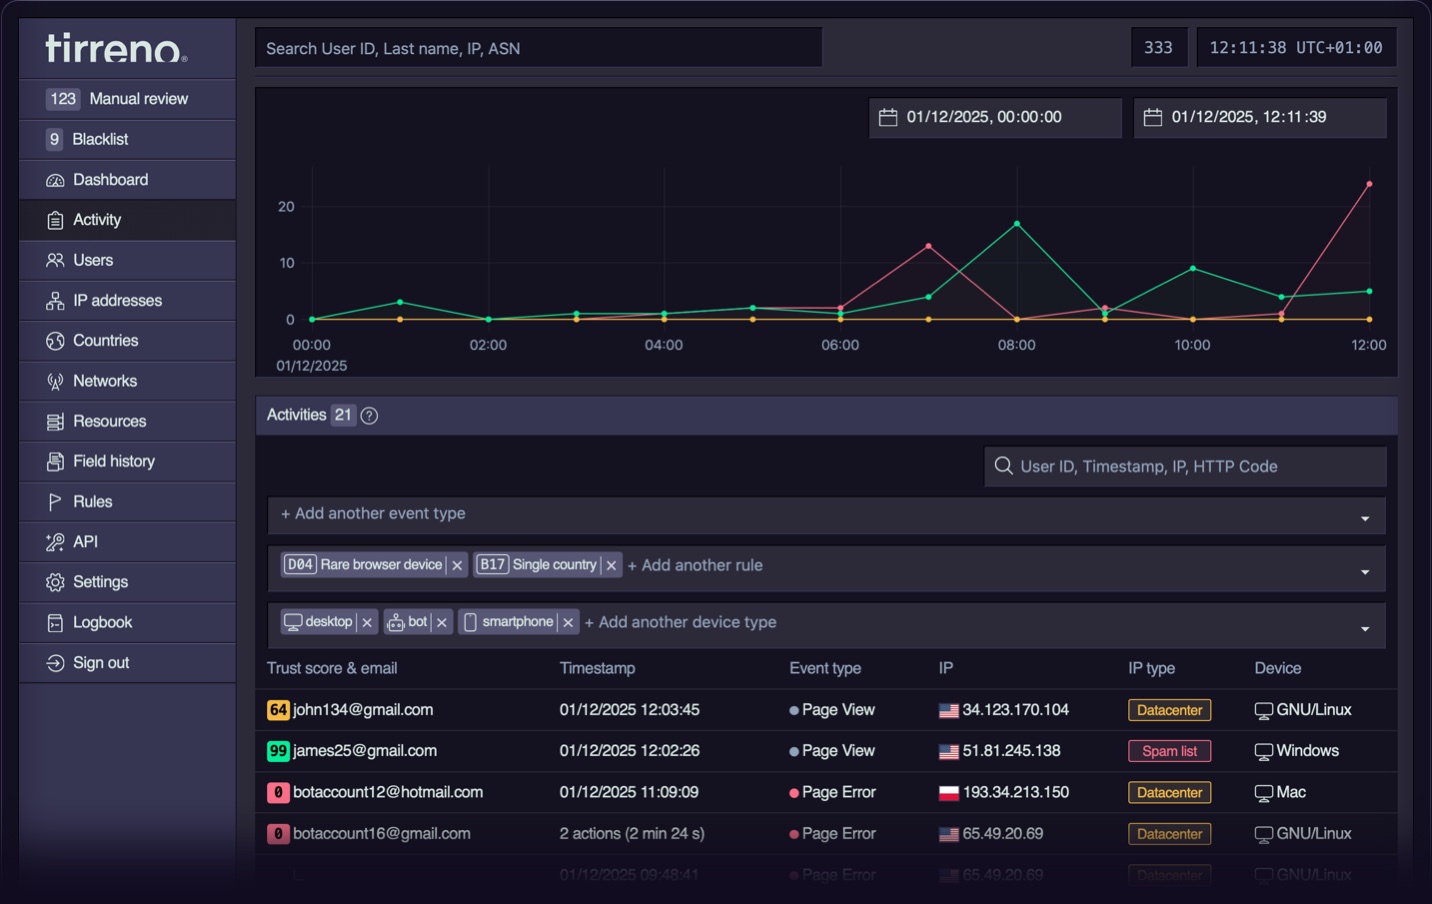
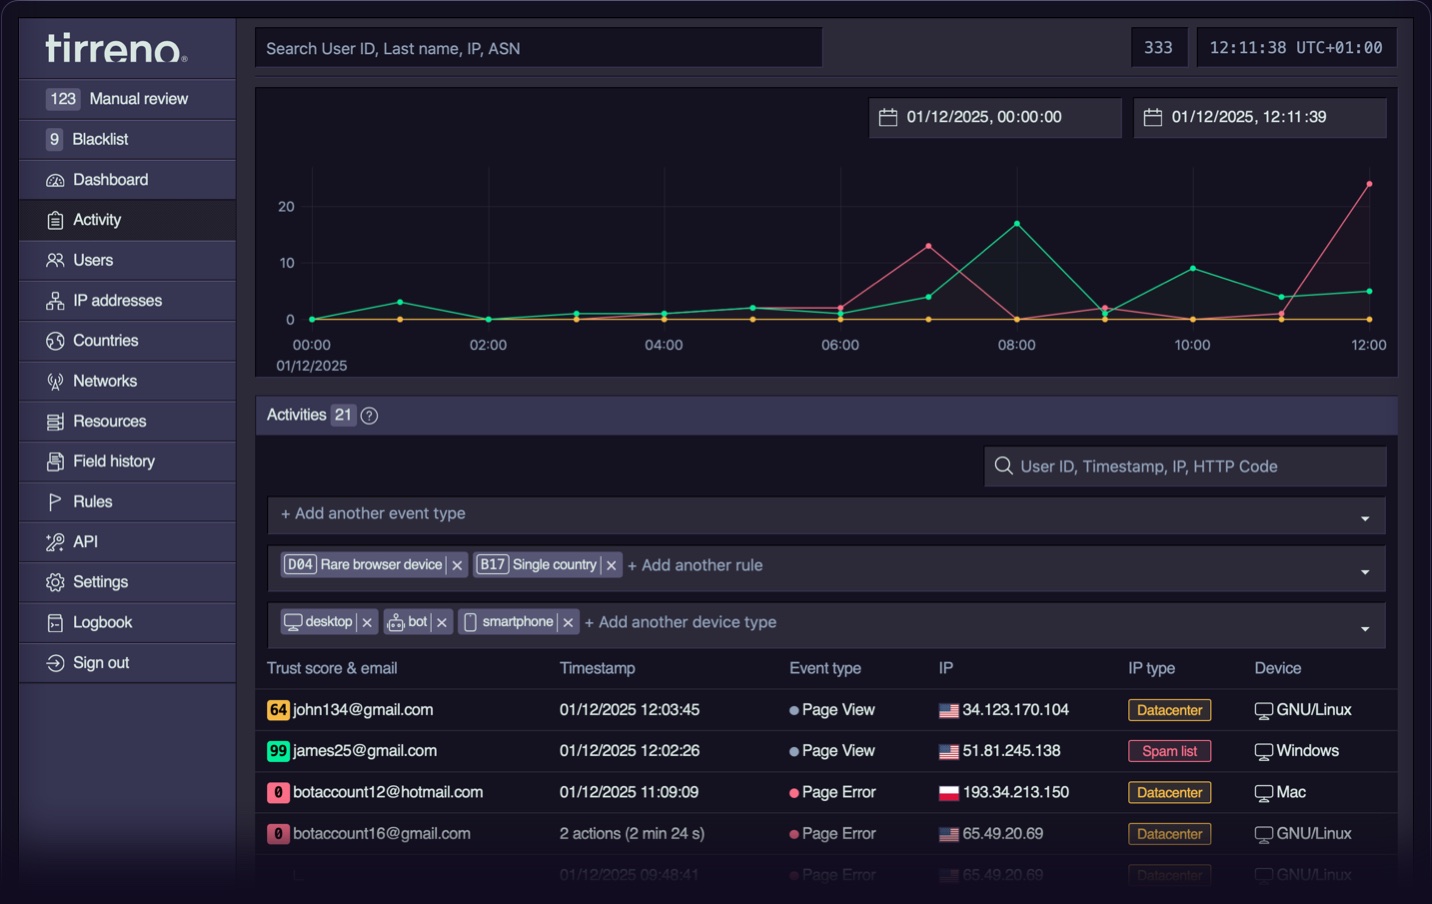
tirreno screenshot

tirreno is a security framework.

tirreno [tir.ˈrɛ.no] helps understand, monitor, and protect your product from threats, fraud, and abuse. While classic cybersecurity focuses on infrastructure and network perimeter, most breaches occur through compromised accounts and application logic abuse that bypasses firewalls, SIEM, WAFs, and other defenses. tirreno detects threats where they actually happen: inside your product.

tirreno is a hand-written, few-dependency, "low-tech" PHP/PostgreSQL application. After a straightforward five-minute installation, you can ingest events through API calls and immediately access a dashboard.

Core components

  • SDKs & API Integrate tirreno into any product with SDKs. Send events with full context in a few lines of code.
  • Built-in dashboard Monitor and understand your product's security and risk events from a single interface. Ready for use in minutes.
  • Single user view Analyze behaviour patterns, risk scores, connected identities, and activity timelines for a specific entity.
  • Rule engine Calculate risk scores automatically with preset rules or create your own customized for your product.
  • Review queue Automatically suspend entities with risky events or flag them for manual review through threshold settings.
  • Field audit trail Track modifications to important fields, including what changed and when to streamline audit and compliance.

Preset rules

Account takeover Credential stuffing Content spam Account registration Fraud prevention Insider threat Bot detection Dormant account Multi-accounting Promo abuse API protection High-risk regions

Built for

  • Self-hosted, internal and legacy apps: Embed security layer to extend your security through audit trails, protect user accounts from takeover, detect cyber threats and monitor insider threats.
  • SaaS and digital platforms: Prevent cross-tenant data leakage, online fraud, privilege escalation, data exfiltration and business logic abuse.
  • E-commerce and online marketplaces: Detect payment fraud, account abuse, fake reviews, promotional code exploitation, inventory manipulation, and protect against credential stuffing and carding attacks.
  • Mission critical applications: Sensitive application protection, even in air-gapped deployments.
  • Industrial control systems (ICS) and command & control (C2): Protect, operational technology, command systems, and critical infrastructure platforms from unauthorized access and malicious commands.
  • Non-human identities (NHIs): Monitor service accounts, API keys, bot behaviors, and detect compromised machine identities.
  • API-first applications: Protect against abuse, rate limiting bypasses, scraping, and unauthorized access.

Live demo

Check out the live demo at play.tirreno.com (admin/tirreno).

Requirements

  • PHP: Version 8.0 to 8.3
  • PostgreSQL: Version 12 or greater
  • PHP extensions: PDO_PGSQL, cURL
  • HTTP web server: Apache with mod_rewrite and mod_headers enabled
  • Operating system: A Unix-like system is recommended
  • Minimum hardware requirements:
    • PostgreSQL: 512 MB RAM (4 GB recommended)
    • Application: 128 MB RAM (1 GB recommended)
    • Storage: Approximately 3 GB PostgreSQL storage per 1 million events

Docker-based installation

To run tirreno within a Docker container you may use command below:

curl -sL tirreno.com/t.yml | docker compose -f - up -d

Continue with step 4 of Quickstart.

Quickstart install

  1. Download the latest version of tirreno (ZIP file).
  2. Extract the tirreno-master.zip file to the location where you want it installed on your web server.
  3. Navigate to http://localhost:8585/install/index.php in a browser to launch the installation process.
  4. After the successful installation, delete the install/ directory and its contents.
  5. Navigate to http://localhost:8585/signup/ in a browser to create an administrator account.
  6. For cron job setup, insert the following schedule (every 10 minutes) expression with the crontab -e command or by editing the /var/spool/cron/your-web-server file:
*/10 * * * * /usr/bin/php /absolute/path/to/tirreno/index.php /cron

Using Heroku (optional)

Click here to launch heroku deployment.

Via Composer and Packagist (optional)

tirreno is published at Packagist and could be installed with Composer:

composer create-project tirreno/tirreno

or could be pulled into an existing project:

composer require tirreno/tirreno

SDKs

  • PHP
  • Python
  • NodeJS
  • WordPress

API reference

tirreno('…')` is tirreno's built-in API. It gives your own code the same building blocks the console uses: the current request and page, the ingested data, the rule engine, the tirreno('queries') builder, logging, and utilities. Use it to customize tirreno. The examples below show custom sections built with this API.

LLM bots

  • llm-bots.example.php
  • llm-bots.example.html

Risk users

  • risk-users.example.php
  • risk-users.example.html

Documentation

See the User guide for details on how to use tirreno, Developers documentation to customize your integration, Admin documentation for installation, maintenance and updates.

About

tirreno is an open-source framework for building sovereign security, compliance and fraud prevention applications.

The project started as a proprietary system in 2021 and was open-sourced (AGPL) in December 2024.

We solve real people's challenges through love in ascétique code and open technologies. tirreno is not VC-motivated. Our inspiration comes from the daily threats posed by organized cybercriminals, driving us to reimagine the place of security in modern organizations.

Why the name tirreno?

Tyrrhenian people may have lived in Tuscany and eastern Switzerland as far back as 800 BC. The term "Tyrrhenian" became more commonly associated with the Etruscans, and it is from them that the Tyrrhenian Sea derives its name, which is still in use today.

According to historical sources, Tyrrhenian people were the first to use trumpets for signaling about coming threats, which was later adopted by Greek and Roman military forces.

Download Tool