
 tc4dy/cve-2026-58048-poc-exploit

👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe Checker (audit/reporting), Weaponized (reverse shell, persistence, UDF RCE, deployment, file read/write, database operations, mass scan). w/Python. 🦾 Use Ethically, Stay Legal <3


ETHICAL USE ONLY – AUTHORIZED SECURITY TESTING
This repository provides tools for authorized security professionals, blue teams, and penetration testers only.
Unauthorized access to computer systems is illegal under CFAA (US), Computer Misuse Act (UK), TCK 243/244 (Turkey), and similar laws worldwide.
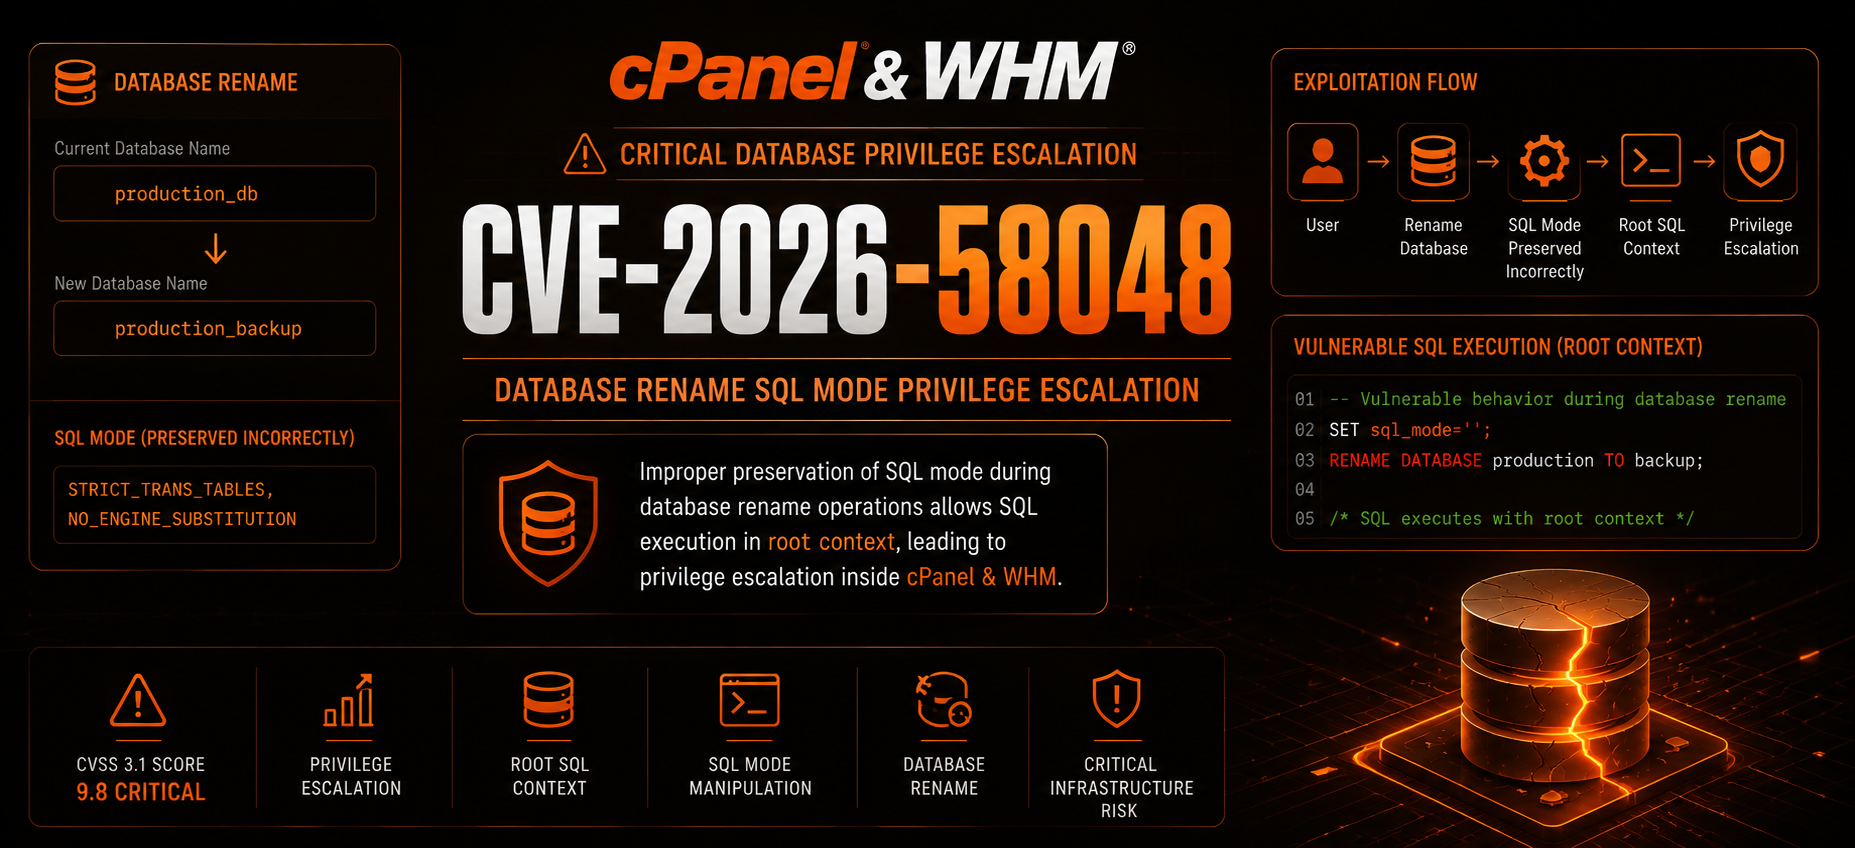
CVE‑2026‑58048 is a critical SQL injection vulnerability in cPanel & WHM versions 11.x that allows an authenticated cPanel user to execute arbitrary SQL commands with MySQL root privileges via the database rename functionality.
ANSI_QUOTES mode, which changes the parsing behavior.11.137.1.6| Tool | Purpose | Intended User |
|---|---|---|
exploit.py | Full weaponized toolkit with reverse shell, persistence, UDF RCE, file read/write, database operations, proxy support, and mass scanning. | Red teams / authorized pentesters |
safecheck.py | Non‑intrusive vulnerability checker that detects cPanel version and assesses risk without executing any malicious payload. Generates detailed reports. | Blue teams / security auditors |
| Feature | exploit.py | safecheck.py |
|---|---|---|
| Vulnerability detection | [+] | [+] |
| Version detection | [+] | [+] |
| MySQL root SQL injection | [+] | [-] |
| Reverse shell | [+] | [-] |
| Persistence (cPanel user creation) | [+] | [-] |
| UDF RCE (command execution) | [+] | [-] |
| File read/write | [+] | [-] |
| Database operations (any SQL) | [+] | [-] |
| Proxy support | [+] | [+] |
| Mass scanning (multi‑thread) | [+] | [-] |
| Interactive shell | [+] | [-] |
| Non‑intrusive (safe) mode | [-] | [+] |
| Verbose/Debug mode | [+] | [+] |
| SSL verification control | [+] | [+] |
| Custom User‑Agent | [+] | [+] |
| Request delay / retries | [+] | [-] |
| JSON / report output | [+] | [+] |
| Endpoint accessibility check | [-] | [+] |
| SQL mode leakage detection | [-] | [+] |
| Scenario | Recommended Tool |
|---|---|
| Blue Team – verifying if your cPanel installation is vulnerable | safecheck.py |
| Security Audit – non‑intrusive vulnerability assessment | safecheck.py |
| Red Team – authorized penetration testing with full exploitation | exploit.py |
| Bug Bounty – responsible disclosure testing | safecheck.py |
| Mass Scanning – checking multiple targets for vulnerability | exploit.py (detection only) |
| Incident Response – checking if systems are compromised | safecheck.py |
git clone https://github.com/tc4dy/CVE-2026-58048-PoC-Exploit
cd CVE-2026-58048
pip install -r requirements.txt
requests
urllib3
colorama
pymysql
exploit.py Parameters| Parameter | Description |
|---|---|
-t, --target | Target cPanel URL (e.g. https://cpanel.example.com:2083) |
-l, --target-file | File containing list of targets (one per line) for mass scanning |
-u, --mysql-user | cPanel/MySQL username |
-P, --mysql-pass | cPanel/MySQL password |
--mysql-port | MySQL port (default: 3306) |
-p, --port | Override cPanel port (default from URL or 2083) |
--threads | Number of threads for multi‑target (default: 10) |
-o, --output | Save results to file (single target) |
--log | Log file for detailed output |
-v, --verbose | Verbose output |
--proxy | HTTP/HTTPS proxy (e.g. http://127.0.0.1:8080) |
-ua, --user-agent | Custom User‑Agent |
--no-keep-alive | Do not keep session alive |
--delay | Delay between requests (default: 2.0s) |
--max-retries | Max retries (default: 3) |
--ssl-verify | Verify SSL certificates |
--cmd | Command to execute (prefix with sql: or udf: for specific) |
--inject | Custom SQL to inject (overrides other actions) |
--reverse-shell | Reverse shell IP:PORT (uses UDF) |
--passwd | Change root MySQL password |
--adduser | Create cPanel user (USER DOMAIN PASSWORD) |
--read | Read a file via LOAD_FILE |
-i, --interactive | Interactive shell after exploit |
--verify | Verify exploit success by attempting MySQL login |
--ping | Ping target before exploitation |
safecheck.py Parameters| Parameter | Description |
|---|---|
-t, --target | Target cPanel URL (e.g. https://cpanel.example.com:2083) |
-v, --verbose | Verbose output |
--proxy | HTTP/HTTPS proxy (e.g. http://127.0.0.1:8080) |
-ua, --user-agent | Custom User‑Agent |
--ssl-verify | Verify SSL certificates |
--timeout | Request timeout in seconds (default: 10) |
--log | Save report to file |
--json | Output results in JSON format |

