
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
overread — Simulates CVE-2023-4966 Citrix Bleed overread bug | Kitploit
Tools/GitHubGitHub/morganwdavis/overread
Memory ForensicsVulnerability AnalysisExploitationLearning & EducationBinary Exploitation
GitHubmorganwdavis/overread

overread

Simulates CVE-2023-4966 Citrix Bleed overread bug
View Repository
292 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share
cb_thumbnail

overread

Simulates CVE-2023-4966 Citrix Bleed overread bug

This is my final project for Harvard CS50 Cybersecurity 2023. It's about a bug. A small bug – with huge, ongoing consequences. In this presentation, I’ll be sharing the “bleeding insights” from one developer’s tiny mistake. A mistake that continues to cause big problems for potentially millions of people.

Video

Citrix Bleed Video on YouTube

Recorded December 4, 2023

Notes

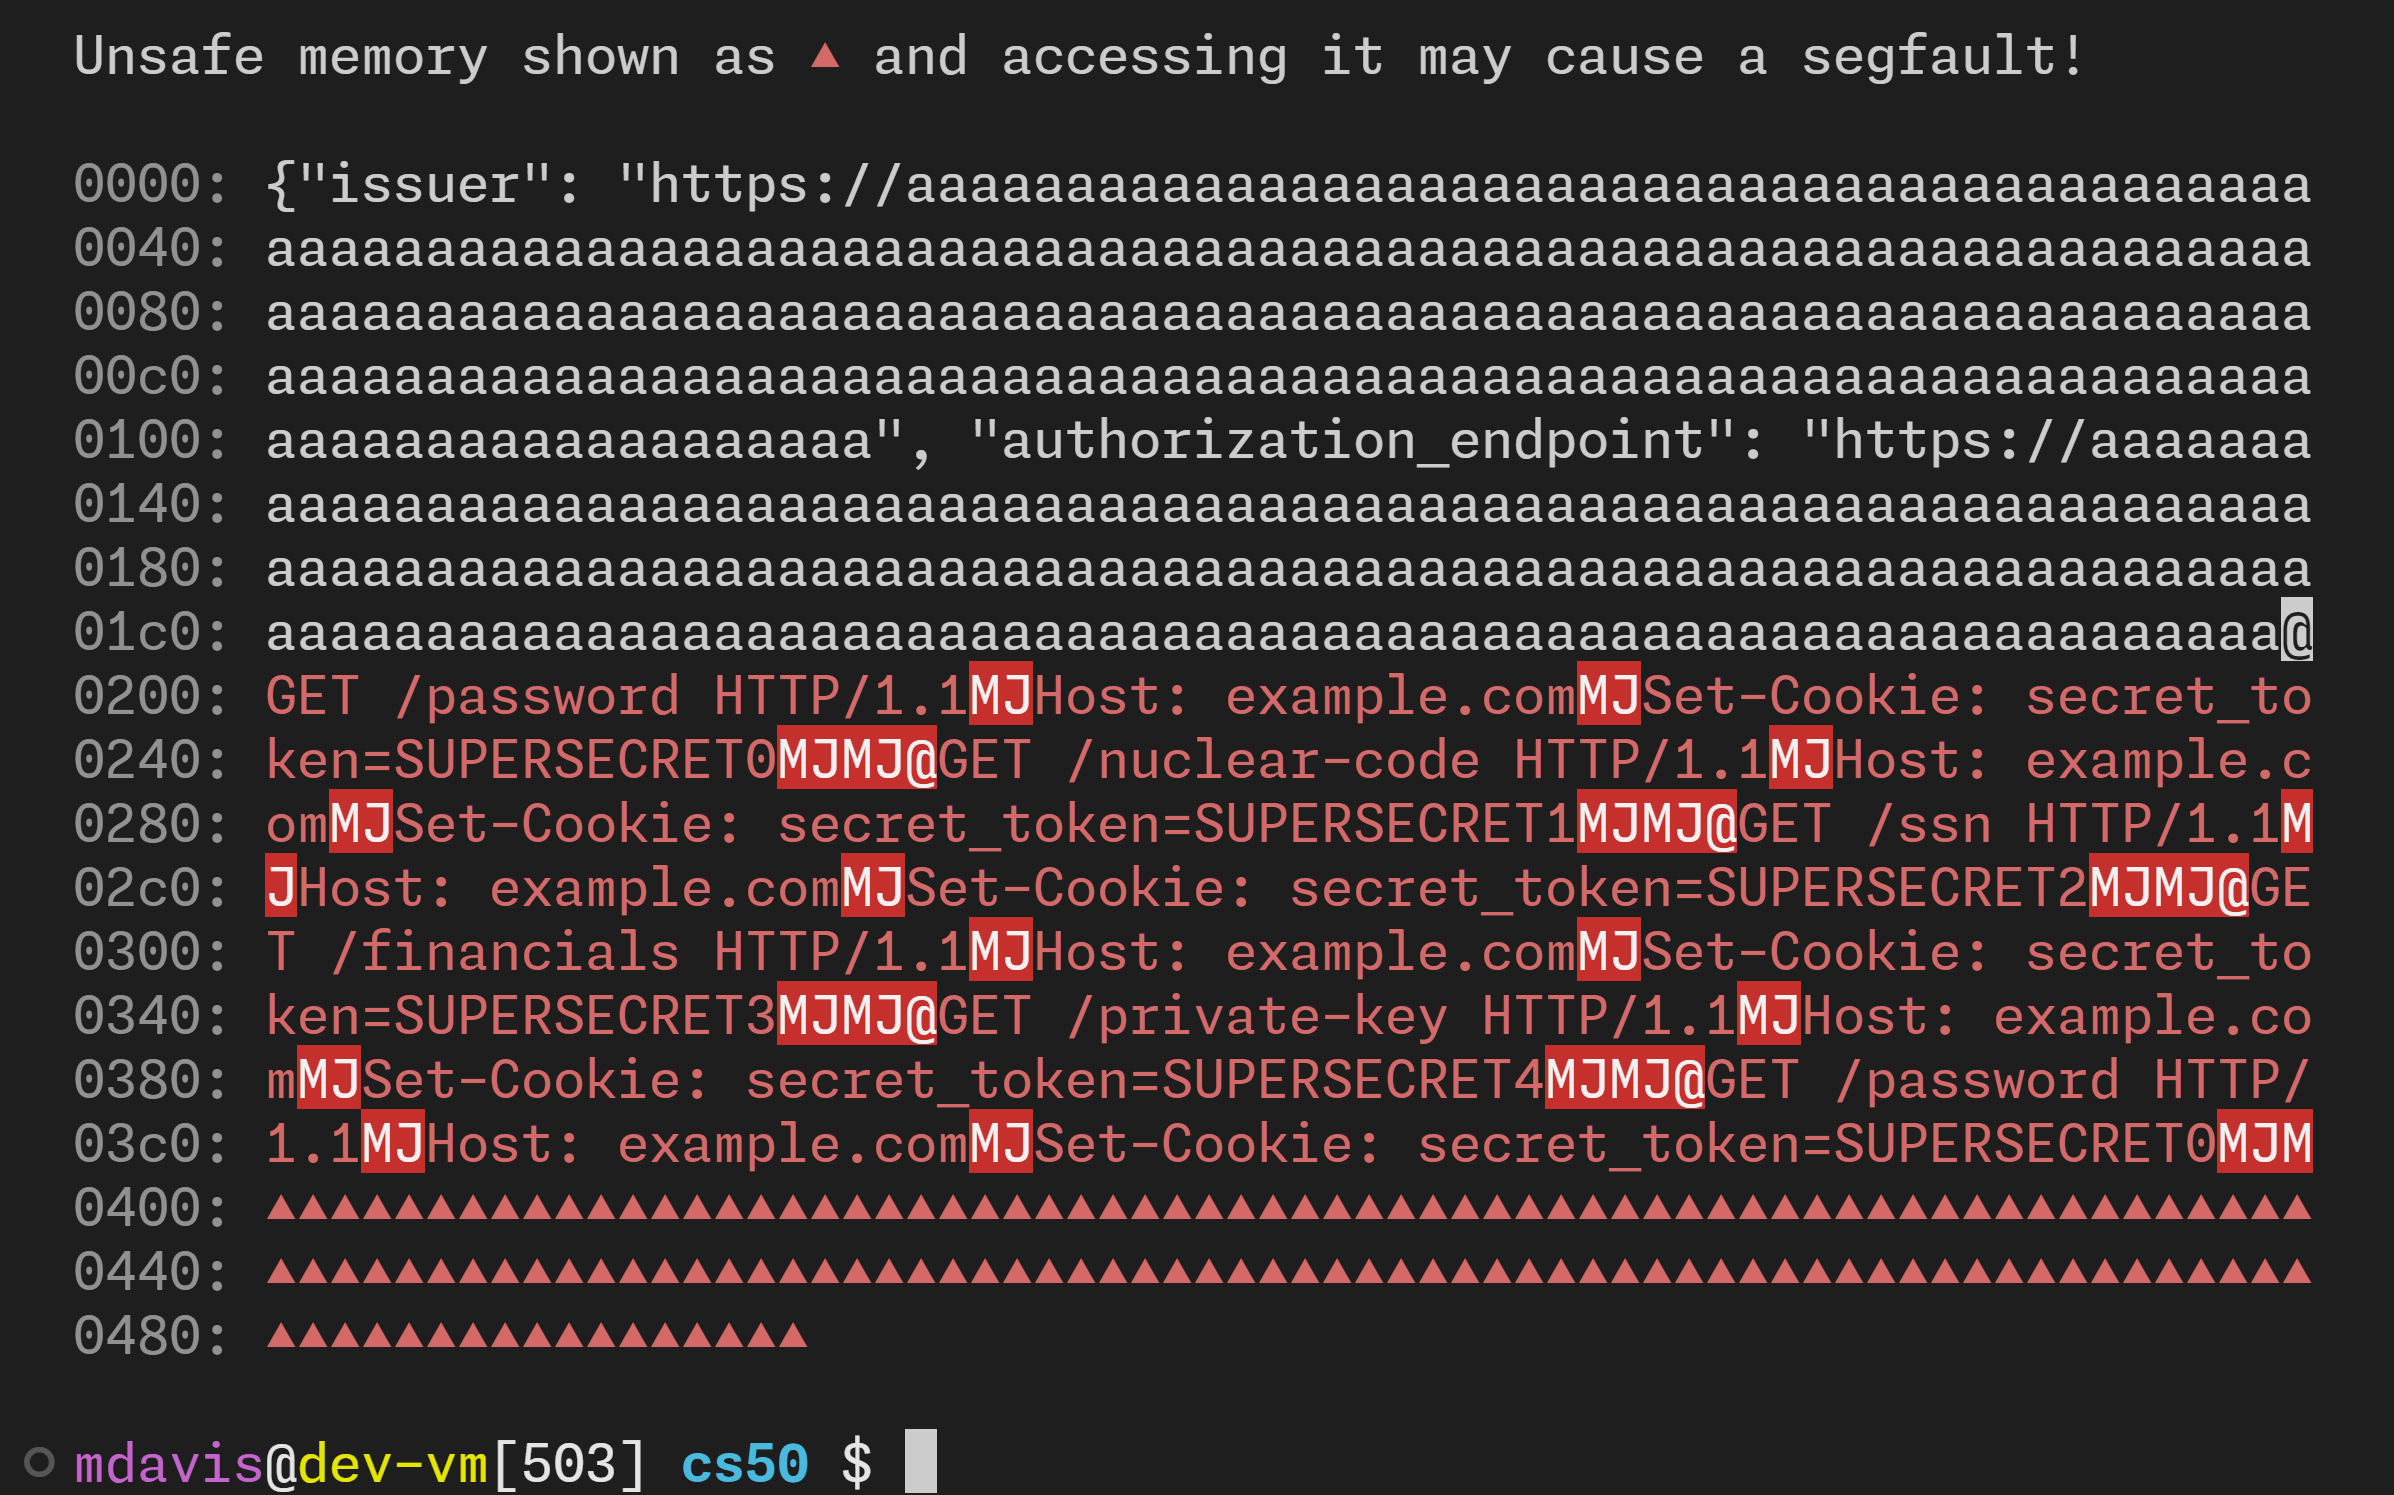
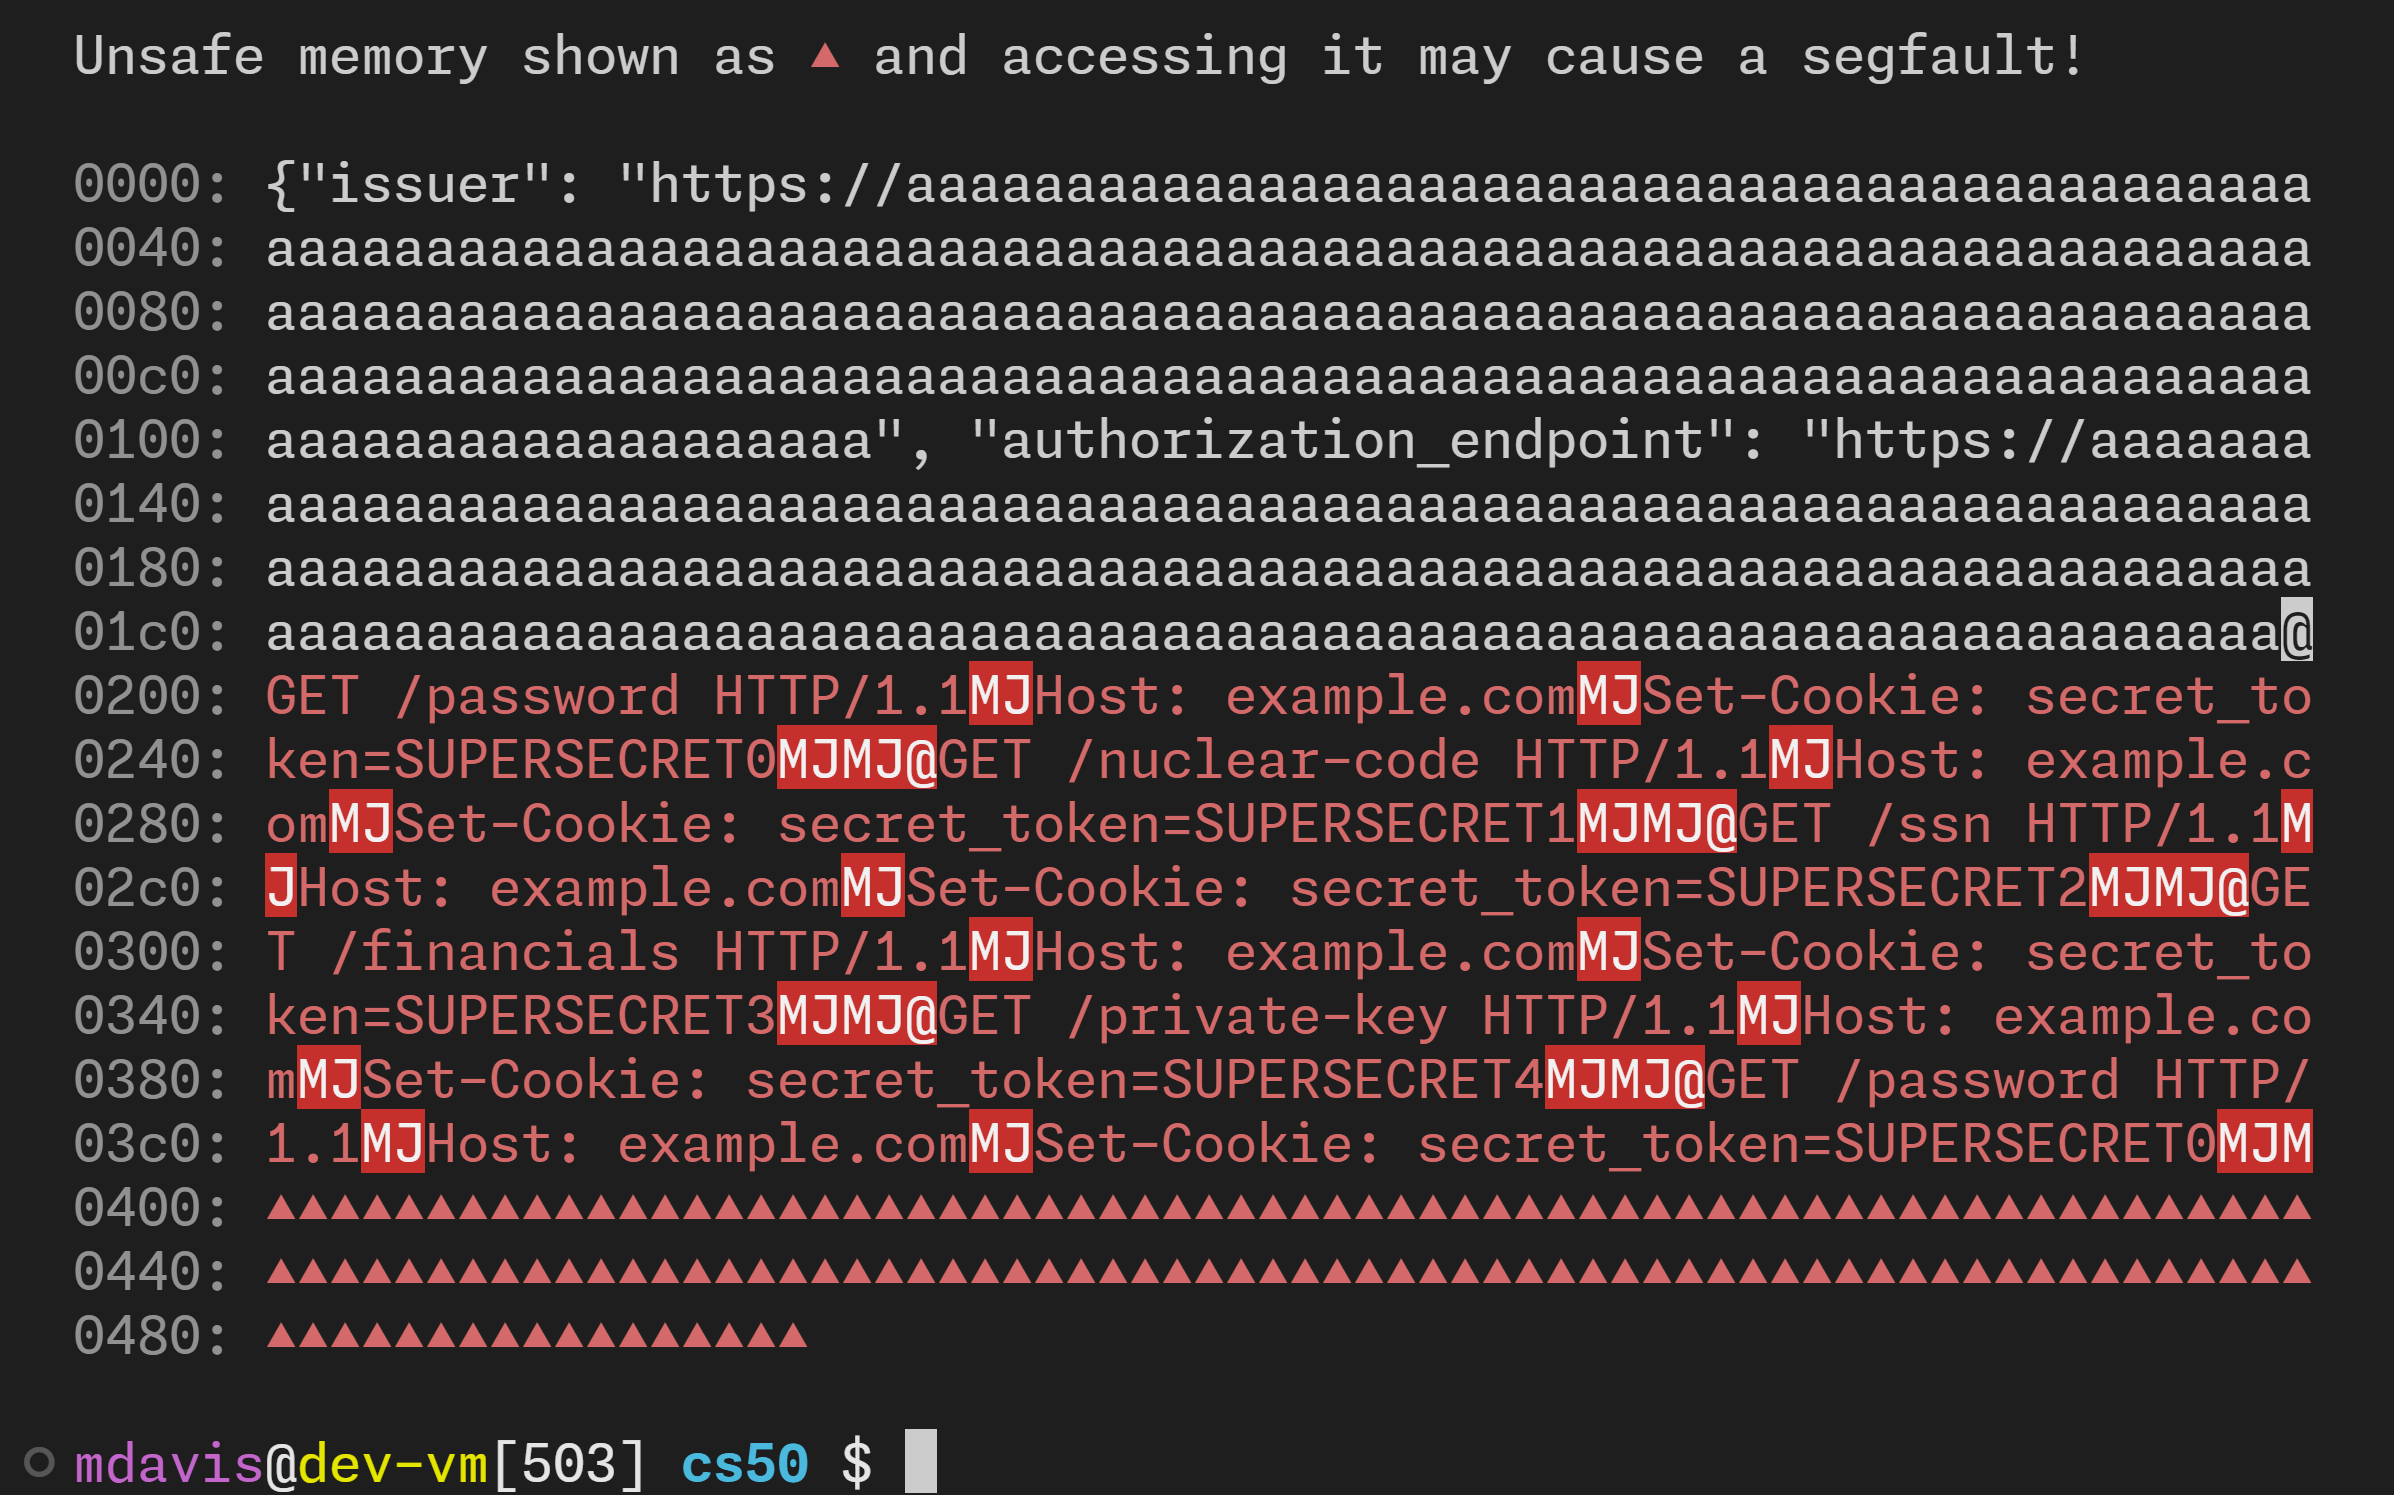
This demonstration program in C makes a call to snfprintf() in a way that forces it to truncate the output. It then attempts to actually overread a memory buffer to show how the CVE-2023-4966 exploit works.

Depending on your compiler and the size of the buffers used here, malloc() might introduce page-alignment padding which could break the demonstration. The constants I use are chosen so the output fits on one terminal display screen. Changing them can cause the results to differ and might not demonstrate the issue at all.
Output

Screenshot 2023-12-11 131451
Download Tool