OneAlert AI Security OS
Open-source autonomous cyber defense for industrial networks
AI agents that detect, investigate, hunt, and respond to threats across your OT/ICS infrastructure — with human approval gates and full audit trails.
Demo Setup ·
Features ·
Quick Start ·
Architecture


Try It Now
Live demo: https://onealert-demo.mangoglacier-b3ad215d.southeastasia.azurecontainerapps.io/app/
Pre-loaded with a realistic water treatment plant: 11 OT/IT assets, a multi-stage attack scenario (VPN compromise → lateral movement → PLC access attempt), AI-generated investigation case with MITRE ATT&CK mapping, and 15+ security events.
See It In Action

Security posture dashboard with KPIs, severity breakdown, and risk heatmap

AI-generated investigation case with MITRE ATT&CK mapping and attack timeline
|

MITRE ATT&CK coverage heatmap with technique search
|
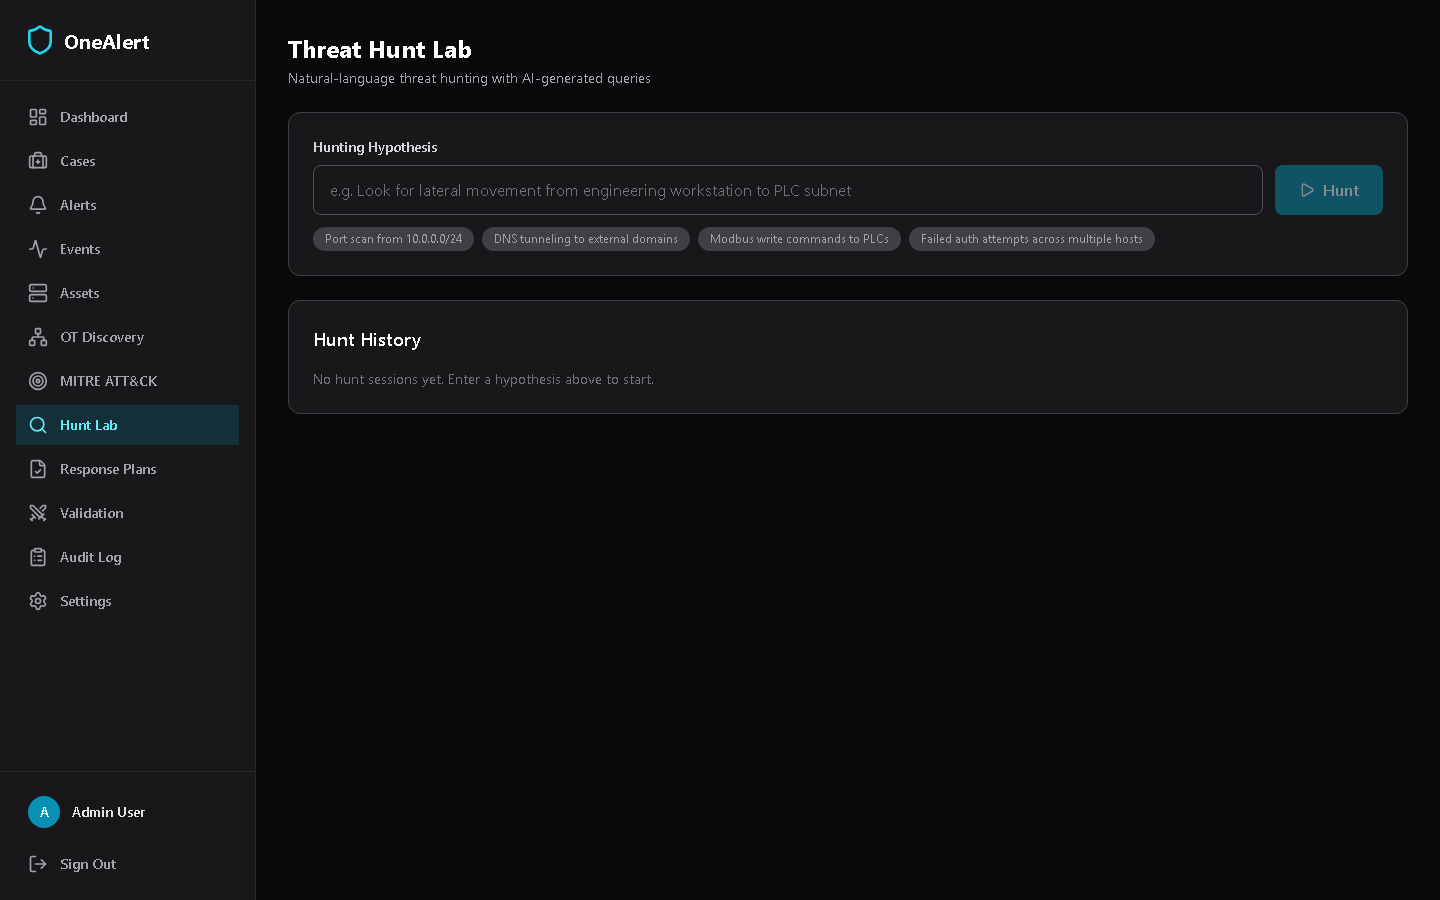
Natural-language threat hunting with AI-generated queries
|

Suricata/Zeek security events with severity filtering
|

CVE vulnerability alerts with AI remediation
|

OT/IT asset inventory with Purdue model classification
|
Why This Exists
Enterprise SOC tools cost $300K-$800K/yr. SMB manufacturers with PLCs, SCADA systems, and OT networks can't afford them — but they're increasingly targeted. OneAlert gives them an AI blue team that:
- Ingests Suricata/Zeek network telemetry
- Detects anomalies with AI agents (not just static rules)
- Correlates alerts into investigation cases with MITRE ATT&CK mapping
- Generates response plans with human approval gates
- Hunts for threats using natural language
- Enforces OT safety constraints (no autonomous actions on PLCs)
Features
AI Agent Pipeline
Six specialized agents working as a team:
| Agent | What It Does |
|---|
| Detect Agent | Analyzes event statistics for port scans, OT protocol anomalies, C2 patterns |
| Triage Agent | Correlates alerts + events into investigation cases with MITRE ATT&CK mapping |
| Hunt Agent | Takes natural-language hypotheses, generates SQL queries, outputs Sigma rules |
| Response Agent | Generates response plans with ordered containment actions |
| Purple Agent | Simulates ATT&CK techniques to validate detection coverage |
| Compliance Agent | Maps platform data to IEC 62443 and NIST CSF controls |
Governed Autonomy
- 5 autonomy levels (L0 read-only to L4 crisis mode)
- OT safety constraint: Purdue Level 0-3 assets always require human approval for containment
- Full agent ledger: Every AI decision logged with model, tokens, reasoning
- Policy engine: Action approval rules by zone, asset type, and autonomy level
- Approval workflow: Approve/reject response plans via REST API before execution
- Action executor: 12 action types (notify, block IP, isolate host, quarantine VLAN, etc.)
PII and Secret Redaction
- 8 pattern types: emails, SSNs, credit cards, API keys, bearer tokens, passwords, private keys, JWTs
- Integrated into event ingestion: secrets stripped before storage and LLM processing
- Preserves network observables: IPs, ports, domains, hostnames kept for security analysis
Purple-Team Validation
- Simulated ATT&CK testing: 8 technique categories with atomic test library
- Dry-run/lab/production modes: production mode requires explicit human approval
- Detection coverage metrics: per-technique detection rates and gap analysis
- Control result tracking: which detection rules fired, which missed
Semantic Search and Blast Radius
- Natural-language case search: TF-IDF ranking with zero external dependencies
- Similar incident retrieval: cosine similarity matching with shared MITRE technique highlighting
- Blast radius graph: entity relationship visualization (assets, IPs, MITRE techniques per case)
Security Event Ingestion
- Suricata EVE JSON parser (alerts, DNS, HTTP, TLS, flows)
- Zeek log parser (conn, dns, http, ssl, files, notice)
- Webhook receiver for Filebeat/Fluentd real-time ingestion
- File upload for offline analysis
MITRE ATT&CK Integration
- Enterprise + ICS matrix (16 tactics, 30+ techniques)
- Auto-mapping from Suricata signatures to techniques
- Detection coverage heatmap per tactic
- Searchable technique browser
Threat Hunt Lab
- Natural-language input: "Look for lateral movement from engineering workstation to PLC subnet"
- AI generates SQL queries against your event data
- Auto-generated Sigma detection rules from confirmed findings
- Read-only query safety validation (blocks INSERT/UPDATE/DELETE)
OT/ICS Vulnerability Management
- Multi-source CVE aggregation (NVD, CISA KEV, ICS-CERT, Cisco PSIRT, Microsoft MSRC)
- AI-powered OT-aware remediation (compensating controls for critical zones)
- EPSS exploit probability scoring
- SBOM analysis (CycloneDX/SPDX)
- Passive device discovery with Purdue model classification
Compliance-as-Code
- IEC 62443-3-3 (10 controls) + NIST CSF 2.0 (11 controls)
- Automated evidence collection from platform data
- Continuous compliance scoring
Multi-Tenancy and Billing
- Organization model with role-based access (admin/analyst/viewer)
- Stripe billing (Free, Starter $499, Pro $1,999, Enterprise $4,999/mo)
- SIEM integrations (Splunk, Sentinel, ServiceNow, PagerDuty)
Quickstart
One-Command Demo

 mangod12/onealert

