 kkamagui/napper-for-tpm
TPM vulnerability checking tool for CVE-2018-6622. This tool will be published at Black Hat Asia 2019 and Black Hat Europe 2019

                     ,----------------,              ,---------,
                ,-----------------------,          ,"        ,"|
              ," Napper v1.3 for TPM ," |        ,"        ,"  |
             +-----------------------+  |      ,"        ,"    |
             |  .-----------------Z  |  |     +---------+      |
             |  |               Z |  |  |     | -==----'|      |
             |  |   ︶     ︶ z   |  |  |     |         |      |
             |  |       -         |  |  |/----| ==== oo |      |
             |  |                 |  |  |   ,/| ((((    |    ,"
             |  `-----------------'  |," .;'/ | ((((    |  ,"
             +-----------------------+  ;;  | |         |,"
                /_)______________(_/  //'   | +---------+
           ___________________________/___  `,
          /  oooooooooooooooo  .o.  oooo /    \,"---------
         / ==ooooooooooooooo==.o.  ooo= /    ,`\--{-D)  ,"
         `-----------------------------'    '----------"

 Napper v1.3 for checking a TPM vulnerability, CVE-2018-6622 and unknown CVE
         Project link: https://github.com/kkamagui/napper-for-tpm
        Please contribute your summary report to the Napper project!
"Napper" is a new vulnerabliity checking tool for the discrete TPM and firmware TPM (Intel PTT). CVE-2018-6622 and unkown CVE are related to the S3 sleeping state or suspend of Advanced Configuration and Power Interface (ACPI). The attacker can subvert the TPM with the S3 sleep, and remote attestation and seal/unseal features that use Platform Configuration Registers (PCRs) can be neutralized. If you want the detailed information about CVE-2018-6622 and unknown CVE, please read our USENIX paper, A Bad Dream: Subverting Trusted Platform Module While You Are Sleeping and Black Hat Europe 2019 presentation BitLeaker: Subverting BitLocker with One Vulnerability.
Napper and CVE-2018-6622 were introduced at security conferences below.
An unknown CVE related to Intel Platform Trust Technology (PTT) was introduced at security conferences below.
You can watch the demo video below.
We always welcome your contributions. Napper's summary report that you contribute will make the world safe.
Napper has GPL v2 license.
Trusted Platform Module (TPM) is a tamper-resistant device and designed to provide hardware-based or firmware-based security functions. A TPM chip has a random number generator, non-volatile storage, encryption/decryption modules, and Platform Configuration Registers (PCRs), which can be utilized for various security applications such as BitLocker, DM-Crypt, Trusted Boot (tboot), and Open Cloud Integrity Technology (Open CIT).
TPM has been widely deployed in commodity devices to provide a strong foundation for building trusted platforms, especially in devices used in enterprise and government systems. Because TPM is the critical point in the trusted platform, many researchers have tried to find vulnerabilities in the TPM and concluded that it is hard to break it without physical access. However, this is not true anymore.
The vulnerabilities we found can subvert the TPM with Advanced Configuration and Power Interface (ACPI). ACPI in PCs, laptops, and servers provide six sleeping states (S0-S5) for reducing power consumption. When the system enters the sleeping state, CPU, device, and RAM are powered off. Since the system powers the components off including security devices, the system should reinitialize them while waking up and this could be the attack surface. We found vulnerabilities on this attack surface without physical access.
To mitigate the vulnerabilities, we also present countermeasures and a new tool, "Napper," to check the vulnerabilities of the TPM. Napper is a bootable USB device based-on Linux, and it has a kernel module and a vulnerability checking software. When you boot a system with the Napper, it makes your system take a nap to check the vulnerabilities and to report the result to you.
Napper consists of a special kernel module and customized tpm2 tools. Napper is based on Ubuntu 18.04, and we customized and tailored it to make a Live CD image. If you just want to check the TPM vulnerability and find an easy way for it, please move to Section 3.1 and use Napper Live CD image with your USB storage. Napper Live CD has not only a binary tool but also full source code of Napper. If you are using Ubuntu 18.04 now and want to build Napper from scratch, please move to Section 3.2 and build it.
Napper Live CD images are in the release page of Napper project.
If you are using Microsoft Windows operating system, use Win32 Disk Imager and write Napper Live CD image to your USB storage.
If you are using Linux or Mac OS X, use a dd command below.
# Please change sdX to your USB storage name.
$> sudo dd if=Napper-LiveCD.iso of=/dev/sdX bs=4096
$> sync
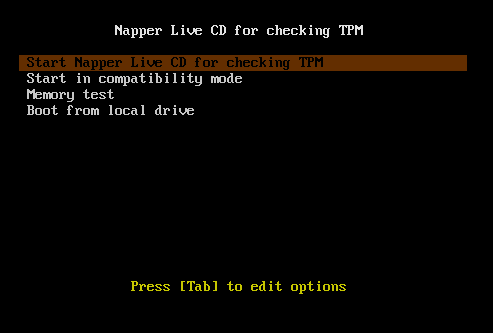
If you plug your USB storage and change a boot sequence to boot with it, you can see Napper's boot menu below and start Napper Live CD by selecting the first option.
After the boot sequence, you can see the README.txt file on the desktop and Napper tool icon on the left dock bar. To check your system, please click the top icon of the dock bar and type napper for the password. Napper tool's ID and password are set to napper. While Napper tests your system, it will sleep your system and wake up. Therefore, you need to type a keyboard to wake your system up from the ACPI S3 sleep state.
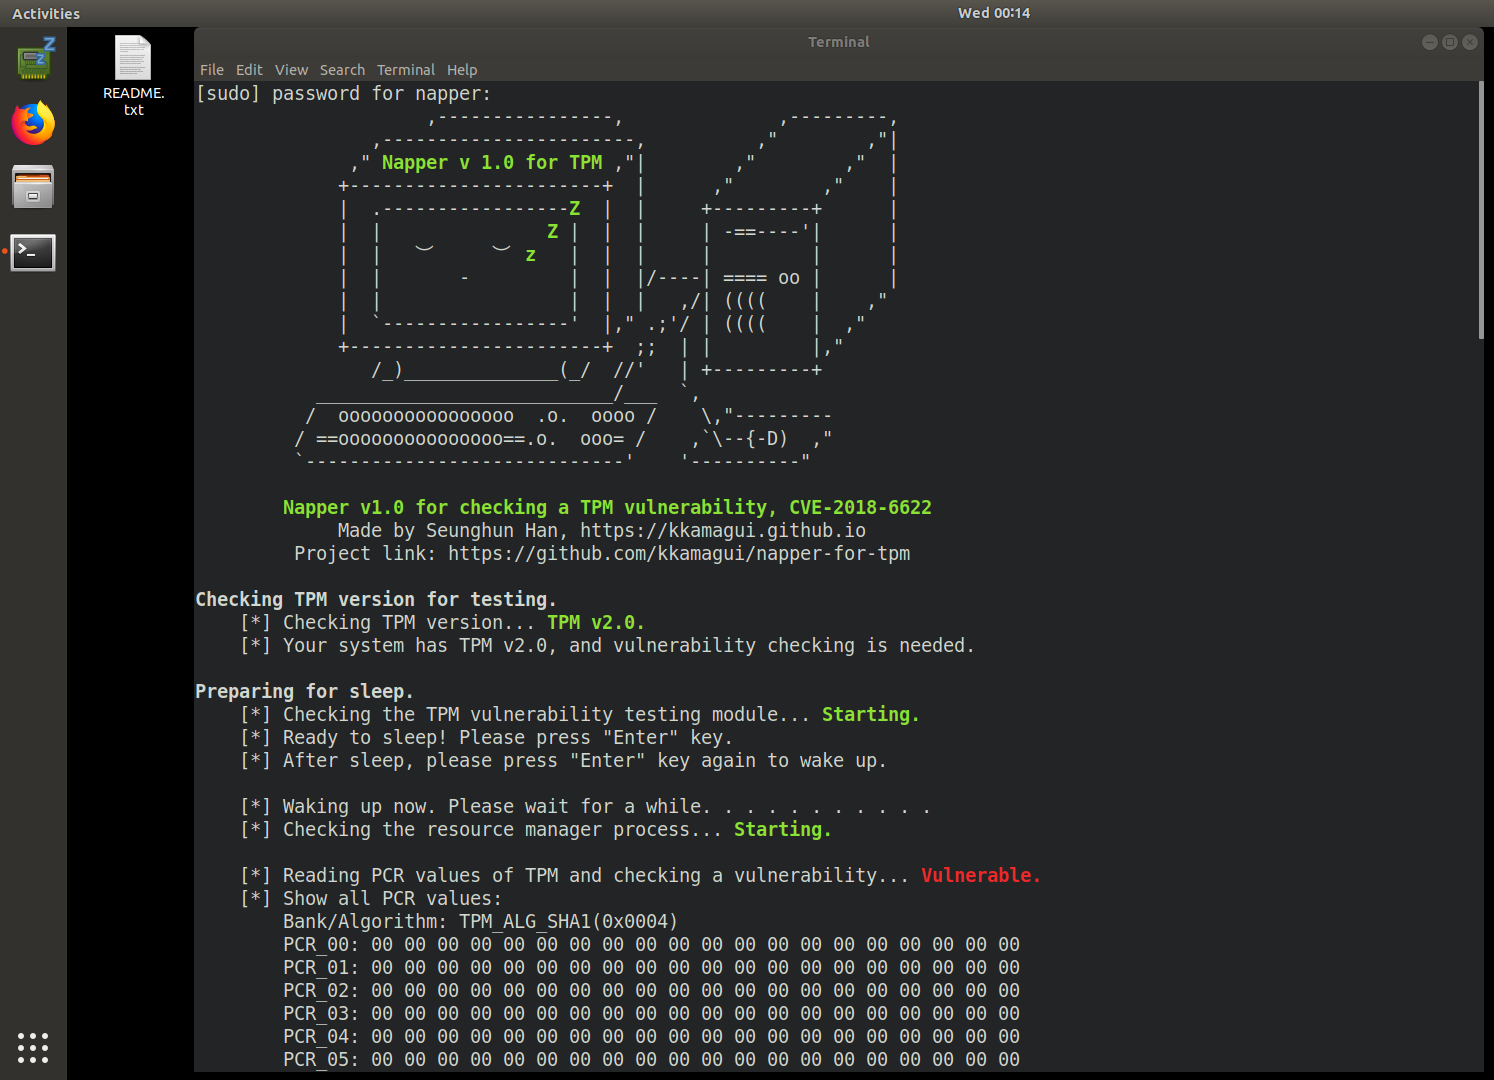
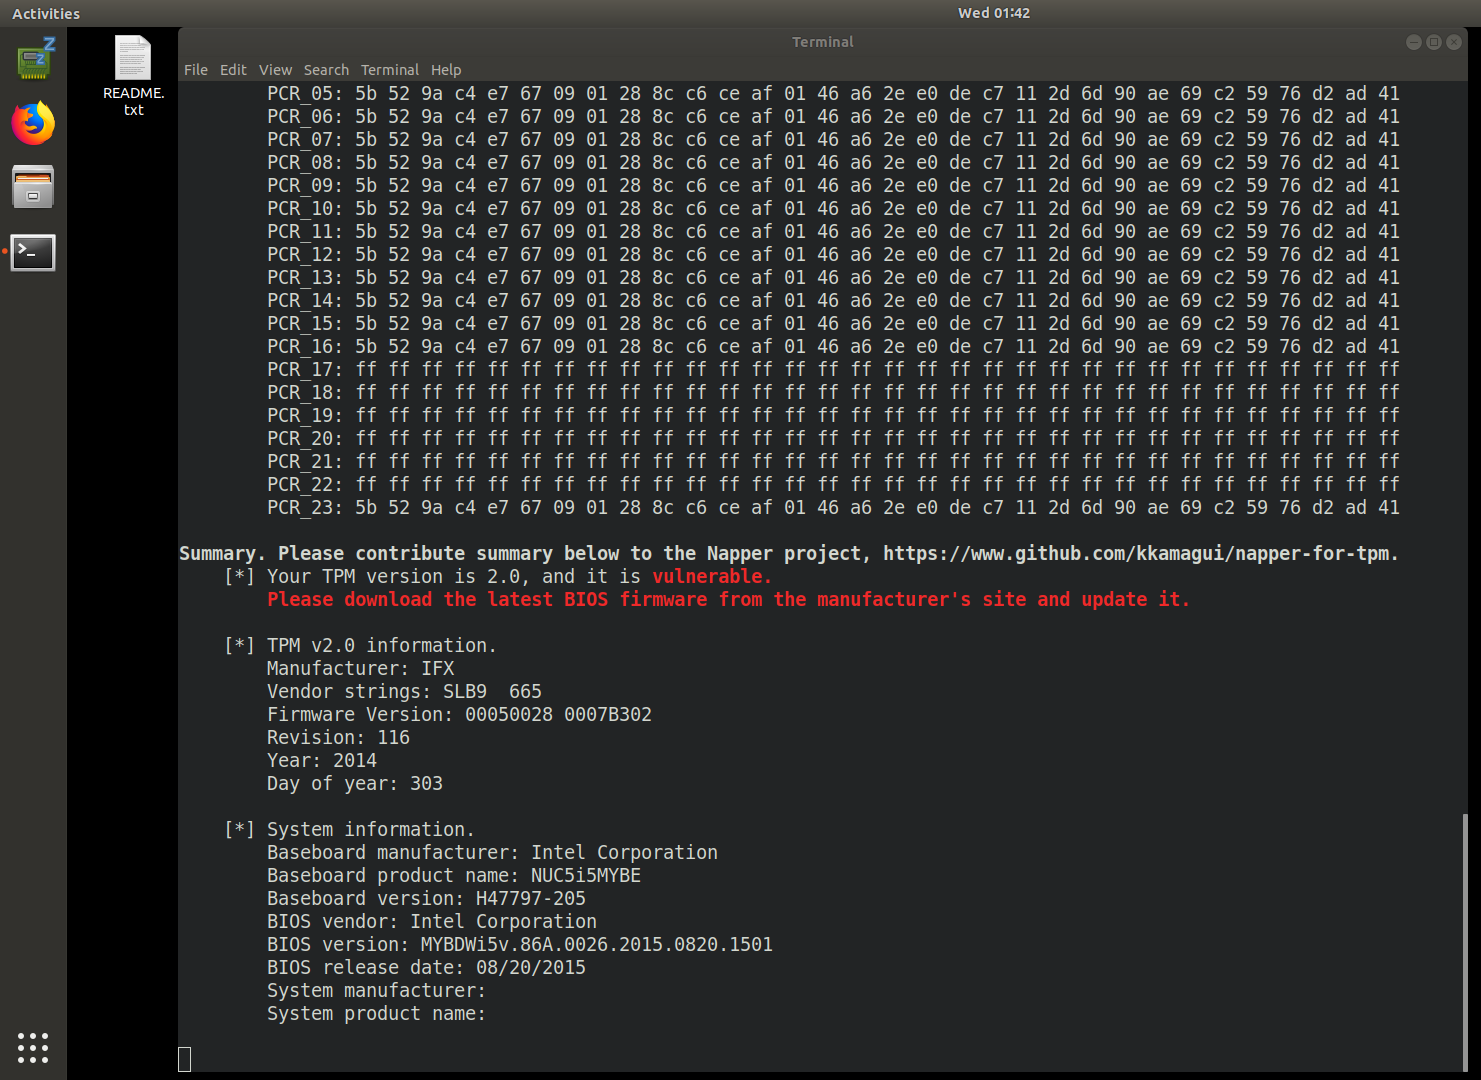
If your system has a TPM vulnerability, Napper will report a summary that your system is vulnerable below. If so, please move to Section 4 and share the summary to our project, Napper, through Issue Report of Napper project or Website.