
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
sniperscope β€” External attack surface management workstation that correlates DNS, certificate transparency, Shodan, CVEDB, TLS and OSINT data into risk-scored forensic reports. | Kitploit
Tools/GitHubGitHub/kamehameha-ctrl/sniperscope
OSINT (Open Source Intelligence)ReconnaissanceVulnerability AnalysisInformation GatheringWeb SecurityDigital ForensicsPenetration TestingThreat IntelligenceSubdomain EnumerationEmail HarvestingDNS Analysis
411819h 18m agoNot yet reviewed

Most Popular

View all β†’

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools β†’
Share
GitHub
kamehameha-ctrl/sniperscope

sniperscope

External attack surface management workstation that correlates DNS, certificate transparency, Shodan, CVEDB, TLS and OSINT data into risk-scored forensic reports.

View Repository

🎯 SniperScope v3.5 // Attack Surface Intelligence, Shodan CVEDB & Forensic EASM Platform

Version 3.5 FastAPI Python React 19 Tailwind CSS v4 Cytoscape OWASP 2025 Ready MIT License

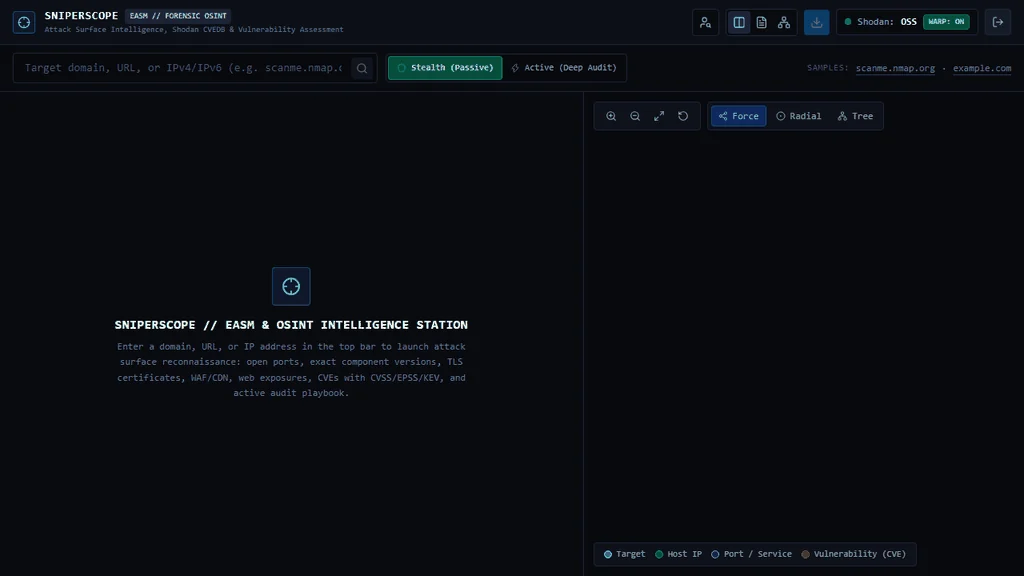
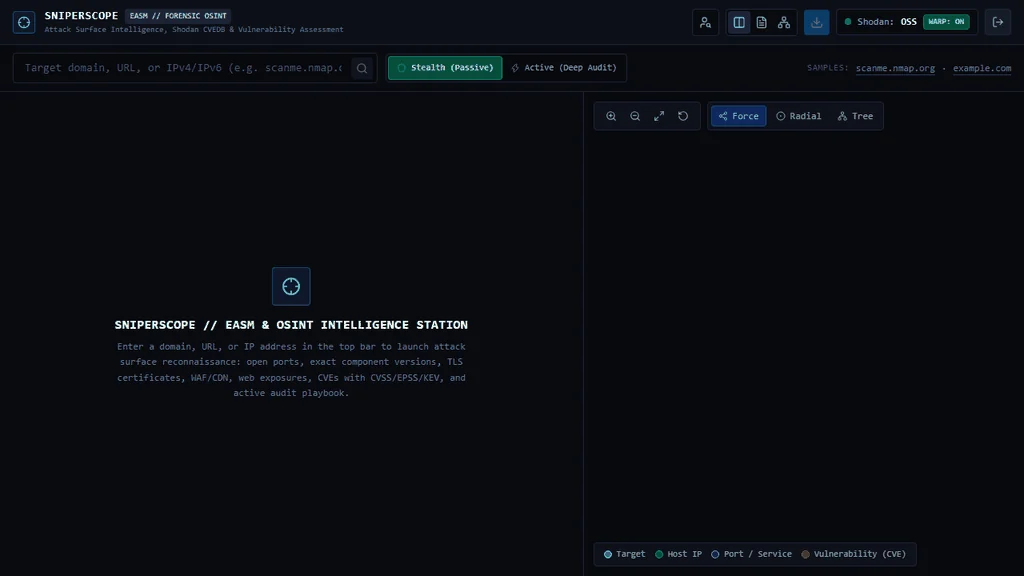
SniperScope Interactive Attack Surface Intelligence Demo

SniperScope is a high-performance External Attack Surface Management (EASM), passive/active OSINT intelligence, and forensic reporting workstation designed for cybersecurity auditors, SOC analysts, and penetration testers.

From a single target (domain name, full URL, or IPv4/IPv6 address), SniperScope orchestrates multiple intelligence engines in parallel:

  • Multi-record DNS zone enumeration with SPF/DMARC anti-spoofing and CAA issuer checking.
  • SSL/TLS Certificate Transparency logs (crt.sh) with automatic Origin IP resolution.
  • Official RDAP/WHOIS registry queries and BGP/ASN routing correlation.
  • Shodan Host API & InternetDB for open ports, software versions, CPEs, and raw service banners.
  • Deep vulnerability enrichment via Shodan CVEDB with real-time CVSS v3/v2, EPSS exploitation probability, CISA KEV (Known Exploited Vulnerabilities) status, and ransomware campaign associations.
  • Live TLS/SSL X.509 who.is-style crypto inspection (cipher suite, public key bits, serial number, trust chain, validity window, SANs).
  • Web uptime diagnosis, response latency, HTTP security headers, cookie flags (Secure, HttpOnly, SameSite), and CORS policies.
  • Software Composition Analysis (SCA) web technology detection (heuristic component engine) mapping front/back components to known CVEs and PoCs.
  • Digital Footprint Suite & Spain OSINT Hub: Real-time multi-platform username reconnaissance (400+ platforms via Server-Sent Events), phone forensics (CNMC Spain, spam DBs), email hunter (MX/SPF, Gravatar, breach dorks), and Spanish official gazettes and transparency registries.
  • 39-Command Active CLI Playbook mapped strictly to OWASP Top 10: 2025 categories.
  • Interactive Anti-Collision Cytoscape.js Topological Graph and multi-format Forensic Report Exporter (PDF, self-contained HTML, Markdown TLP:AMBER, and chronological RAW execution trace .log).

πŸ“ Architecture & Data Flow

flowchart LR
    subgraph Auth["πŸ” Operator Access (Gatekeeper)"]
        direction TB
        LoginScreen["πŸ”‘ LoginScreen\nHMAC-SHA256 Token\n(sniperadmin / Passphrase)"]
    end

    subgraph Frontend["πŸ–₯️ Frontend (React 19 + Vite 8 + Tailwind CSS v4)"]
        direction TB
        TargetInput["πŸ” TargetInput\n(Domain / IP / URL / OPSEC Mode)"]
        WarpToggle["πŸ›‘οΈ WARP / Proxy Egress Status\n(Active / Standby Β· Ping ms Β· Egress IP)"]
        FootprintStation["πŸ•΅οΈ Digital Footprint & Spain Hub\n(Usernames Β· Spain OSINT Β· Phone Β· Email)"]
        Dossier["πŸ“‹ IntelDossier\nKPIs Β· Ports Β· CVEDB Β· Web/TLS Β· SCA Β· CLI Playbook"]
        Cytoscape["πŸ•ΈοΈ GraphCanvas (Cytoscape.js)\nForce-Directed Β· Concentric Radial Β· Tree"]
        Exporter["πŸ“„ ForensicReportModal\nPDF Β· HTML Β· Markdown Β· RAW Trace (.log)"]
    end

    subgraph Backend["βš™οΈ Asynchronous Backend (FastAPI + Python 3.11+)"]
        direction TB
        Sanitizer["πŸ›‘οΈ Sanitizer & Target Normalizer\n(In-memory _SCAN_CACHE TTL 300s)"]
        ParallelEngine["πŸš€ Parallel Asyncio Engine\n(DNS / CT Logs / RDAP / HTTP / Shodan)"]
        OutboundProxy["🌐 Egress Proxy Handler\n(Cloudflare WARP 127.0.0.1:40000)"]
        RiskCalc["πŸ“Š Dynamic Risk Engine\n(Score 0-100 Β· Grades A-F Β· Weighted Findings)"]
        RawTrace["🧾 RAW Chronological Execution Trace\n(Command & Request Audit Log)"]
    end

    subgraph IntelSources["🌐 External Intelligence Providers"]
        direction TB
        DNS_Mod["DNS & CAA Anti-Spoofing\n(A, AAAA, MX, NS, TXT, CAA, SPF, DMARC)"]
        CRT_Mod["Certificate Transparency\n(crt.sh Logs + Origin IP Lookup)"]
        Shodan_Mod["Shodan Host & InternetDB\n(Ports, CPEs, Versions, Banners)"]
        CVEDB_Mod["Shodan CVEDB\n(CVSS, EPSS, CISA KEV, Ransomware)"]
        HTTP_Mod["Web Audit, TLS X.509 & SCA\n(Chain, SHA-256, Web Tech, WAF, CORS)"]
        RDAP_Mod["RDAP / ASN\n(Registrar, Netblock, BGP Routing)"]
        Footprint_Mod["SOCMINT & Spanish Public Gazettes\n(BOE, BORME, CENDOJ, Catastro, CNMC)"]
    end

    Auth --> Frontend
    TargetInput -->|GET /api/scan| Sanitizer
    WarpToggle -->|GET /api/health| OutboundProxy
    FootprintStation -->|SSE /api/sherlock/stream| Footprint_Mod
    Sanitizer --> ParallelEngine
    ParallelEngine --> OutboundProxy
    OutboundProxy --> IntelSources
    DNS_Mod & CRT_Mod & CVEDB_Mod & HTTP_Mod & RDAP_Mod --> RiskCalc
    RiskCalc --> RawTrace
    RawTrace -->|JSON Payload| Dossier
    RawTrace -->|Nodes & Edges| Cytoscape
    RawTrace -->|Trace & Findings| Exporter

🎯 Core Use Cases

  • πŸ›‘οΈ External Attack Surface Management (EASM): Continuously monitor perimeter exposures, shadow IT, expiring TLS certificates, dangling subdomains, and unexpected listening ports across enterprise assets.
  • 🎯 Red Team & Penetration Testing Reconnaissance: Conduct deep initial target enumeration without tripping client SOC alarms using Stealth Mode, then pivot to Active Mode with 39 pre-parametrized OWASP Top 10: 2025 commands.
  • 🚨 SOC & Incident Response Triage: Rapidly determine if an alert involves assets with actively exploited vulnerabilities in the wild (CISA KEV) or ransomware weaponization tags.
  • πŸ•΅οΈ OSINT & Identity Footprinting: Correlate public usernames, domains, and corporate records across 400+ platforms and official public registries.

πŸ› οΈ Technology Stack

Download Tool