halildeniz/vanguardhttp
High-performance cross-platform HTTP probing & deep fingerprinting desktop suite built with Go and Wails v2. featuring real-time streaming, tech detection, DNS/TLS inspection, Favicon MMH3 hashing, proxy routing, and multi-format reporting.

High-Performance Cross-Platform HTTP Probing & Deep Fingerprinting Desktop Suite



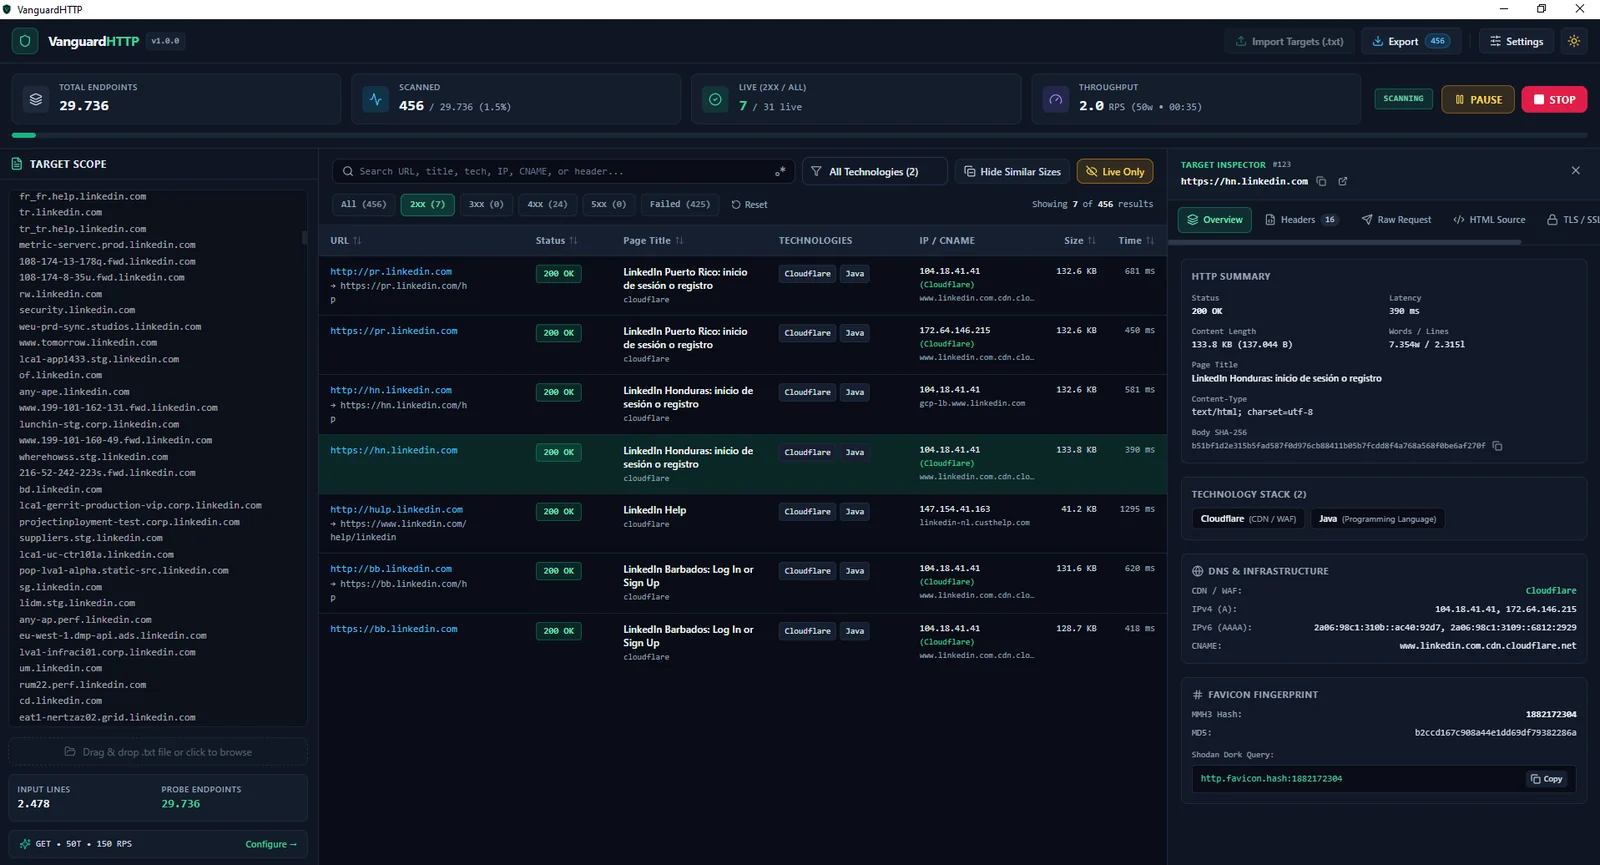
VanguardHTTP is a modern, cross-platform desktop reconnaissance and attack-surface discovery application built for security researchers, penetration testers, bug bounty hunters, and red teams.
Instead of parsing walls of terminal output or chaining multiple CLI scripts manually, VanguardHTTP streams live HTTP probing and deep fingerprinting telemetry directly into a responsive, filterable desktop workspace—compiled into a single standalone binary with minimal RAM overhead.
1 up to 1,000 worker threads.golang.org/x/time/rate) to enforce maximum Requests Per Second (RPS) and avoid WAF bans or target saturation.runtime.EventsEmit) with micro-batched UI rendering for smooth performance even at high RPS.https:// with seamless fallback to http:// (or probes both schemes concurrently) for bare domains and IPs.192.168.1.0/24) into individual host targets.80, 443, 8080, 8443, 3000, 8000, etc.)..txt, .lst, or .csv target lists with automatic deduplication and live endpoint preview counting.2xx, 3xx, 4xx, 5xx), page <title>, Server / X-Powered-By headers, content size, word/line counts, SHA-256 body hash, and latency (ms).go:embed) identifying Web Servers, CMSs, Frontend/Backend Frameworks, CDNs, WAFs, and DevOps panels with version extraction.A, AAAA, and CNAME lookups with automatic CDN/WAF provider attribution.MMH3) and MD5 digests for /favicon.ico and HTML-declared icons, generating ready-to-copy http.favicon.hash:<id> queries.GET, HEAD, POST, OPTIONS, PUT, PATCH, and DELETE with custom request bodies.Authorization, Cookie, X-Bug-Bounty) and toggle between a custom User-Agent or an automated multi-browser User-Agent pool.HTTP, HTTPS, SOCKS5, and SOCKS5H proxy support for seamless traffic inspection in Burp Suite or OWASP ZAP.Location header logging.nuclei/ffuf), or a standalone interactive HTML Security Report.1.22 or higher18+ (LTS)Install the Wails v2 CLI and verify your environment:
go install https://github.com/wailsapp/wails/v2/cmd/wails@latest
wails doctor
Linux Note (Ubuntu/Debian): Install GTK3 and WebKit2GTK development headers before building:
sudo apt update && sudo apt install -y build-essential libgtk-3-dev libwebkit2gtk-4.0-dev(On Ubuntu 24.04+, install
libwebkit2gtk-4.1-devand pass-tags webkit2_41towailscommands.)
git clone https://github.com/halildeniz/VanguardHTTP.git
cd VanguardHTTP
go mod tidy
wails dev
.exe):wails build -clean -platform windows/amd64 -ldflags "-s -w"
Output: build/bin/VanguardHTTP.exe
.app Universal Binary):wails build -clean -platform darwin/universal -ldflags "-s -w"
Output: build/bin/VanguardHTTP.app
wails build -clean -platform linux/amd64 -ldflags "-s -w"
Output: build/bin/VanguardHTTP
Contributions, feature ideas, and new technology fingerprint signatures are welcome!
git checkout -b feature/amazing-fingerprint
git commit -m "feat: add new WAF detection signatures"
git push origin feature/amazing-fingerprint
Have a suggestion, feature request, or encountered a bug?
VanguardHTTP is developed strictly for authorized security assessments, penetration testing, bug bounty programs, and educational research. Scanning networks or systems without explicit prior permission from the asset owner is illegal. The author assumes no liability for misuse or damage caused by this software.
Halil İbrahim Deniz