
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
PoC-CVE-2025-25200 — ReDoS explorando backtracking em regex, resultando em consumo excessivo de CPU e negação de serviço (DoS) em aplicações Node.js. | Kitploit
Tools/GitHubGitHub/dwictor0/poc-cve-2025-25200
Static AnalysisVulnerability AnalysisExploitationWeb Security
GitHubdwictor0/poc-cve-2025-25200

PoC-CVE-2025-25200

ReDoS explorando backtracking em regex, resultando em consumo excessivo de CPU e negação de serviço (DoS) em aplicações Node.js.

View Repository
287 months agoNot yet reviewed
Share

CVE-2025-25200

Context

  • Vulnerability: CVE-2025-25200

  • Type: Regular Expression Denial of Service (ReDoS)

  • Component: Kao >= 2.0.0, < 2.15.4 , >= 3.0.0-alpha.0, < 3.0.0-alpha.3 , >= 1.0.0, < 1.7.1, < 0.21.2

  • Description: This vulnerability presents quadratic time complexity O(n²) or, in more critical scenarios, exponential O(2ⁿ), meaning the time required to process the input grows with its size (backtracking). The origin of the problem lies in the mechanism of the regular expression engine called backtracking. When the input (token) does not match, the engine simply retreats to previous positions where it could choose an alternative path.
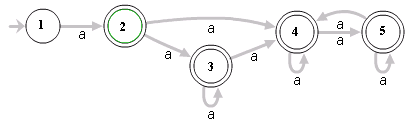
NFA

Impact and Severity

  • Impact Type: Denial of Service (DoS)
  • Attack Vector: Network
  • Score: 9.2 (High)

Possible Mitigations

  • Payload length validation.
  • Use a WAF rule to sanitize or reject headers containing patterns that could trigger ReDoS.
  • Implement request timeout limits to prevent long-duration requests from blocking the event loop indefinitely.

Responsible Disclosure

This vulnerability was handled following responsible disclosure practices.

PoC Test Node.js Koa CVE-2025-25200

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →






