
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2007-4559 — Proof-of-concept demonstrating CVE-2007-4559 path traversal in Python's tarfile module, allowing arbitrary file overwrite via malicious TAR archives. | Kitploit
Tools/GitHubGitHub/depers-rus/cve-2007-4559
Vulnerability AnalysisCode AnalysisExploitationSupply Chain SecurityLearning & Education
GitHubdepers-rus/cve-2007-4559

CVE-2007-4559

Proof-of-concept demonstrating CVE-2007-4559 path traversal in Python's tarfile module, allowing arbitrary file overwrite via malicious TAR archives.

View Repository
1281 year agoNot yet reviewed
Share

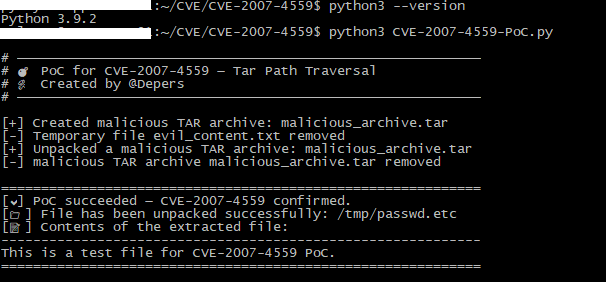
PoC or Exploit for CVE-2007-4559

A malicious TAR archive can include file paths like ../../../../etc/passwd, which try to "climb up" out of the intended extraction folder.

If a Python script uses tarfile.extract() or extractall() without checking the file paths, it will unpack files to those locations — even if they point outside the target directory.

That means a hacker could overwrite sensitive or system files, especially if the user runs the script with elevated permissions.

Vulnerable

As of 2025, both Debian 11–12 and Ubuntu 24 are still affected by this vulnerability. Other operating systems haven’t been tested, but these two are among the most widely used, so that alone is concerning. Even though this vulnerability dates back to 2007, it’s still present in LTS (long-term support) versions — and the vulnerable software isn’t patched automatically through a standard apt upgrade.

Proof

изображение

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    501
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    467
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    340
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    314
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    295

Explore all tools

Browse our collection of tools

View all tools →





