 completetech-security/vm2-nesting-check
Offline vm2 evidence checker for CVE-2026-92935. Sandbox package and nesting evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.





Offline evidence checker for CVE-2026-92935: vm2 array-shaped require nesting escape (alias GHSA-8hr7-r645-pc6w).
It compares explicitly supplied vm2 package versions with the reviewed advisory ranges and reports what that version evidence does and does not show. Python 3.10+, standard library only; the single executable vm2_nesting_check.py can be copied on its own. It never contacts websites, imports application code, runs a package manager, or executes exploit payloads.
potentially_affected is not exploitation. It means the reported version falls in the documented affected interval. Application preconditions and exploitability were not established, and every row retains exploitability: not_tested.fixed_version_reported is not a patch attestation. It only describes a version claim; it never attests installed patches or safety.unknown is neither clean nor a failure. Missing, conflicting, malformed, prerelease, qualified, and custom/vendor builds stay unknown, as does anything outside the reviewed ranges.74aa57ba5df05c34d17ae67912cd26ec2335201b, with package-specific range comparison and the mixed-whitespace CSV fix. No companion repository is needed.# Assess one reported version and print JSON
python vm2_nesting_check.py --version 3.11.7 --format json
# Assess the example inventory and save an HTML report
python vm2_nesting_check.py --inventory examples/inventory.example.json --format html --output report.html
# Assess a CSV inventory (CSV is the default format) and exit 1 on potentially_affected results
python vm2_nesting_check.py --csv-list inventory.csv --fail-on-finding
# Show every option, then run the local test suite
python vm2_nesting_check.py --help
python -m unittest -v
At least one of --version, --inventory, --csv-list or --source is required. --tool-version prints the checker version (currently 1.1.0).
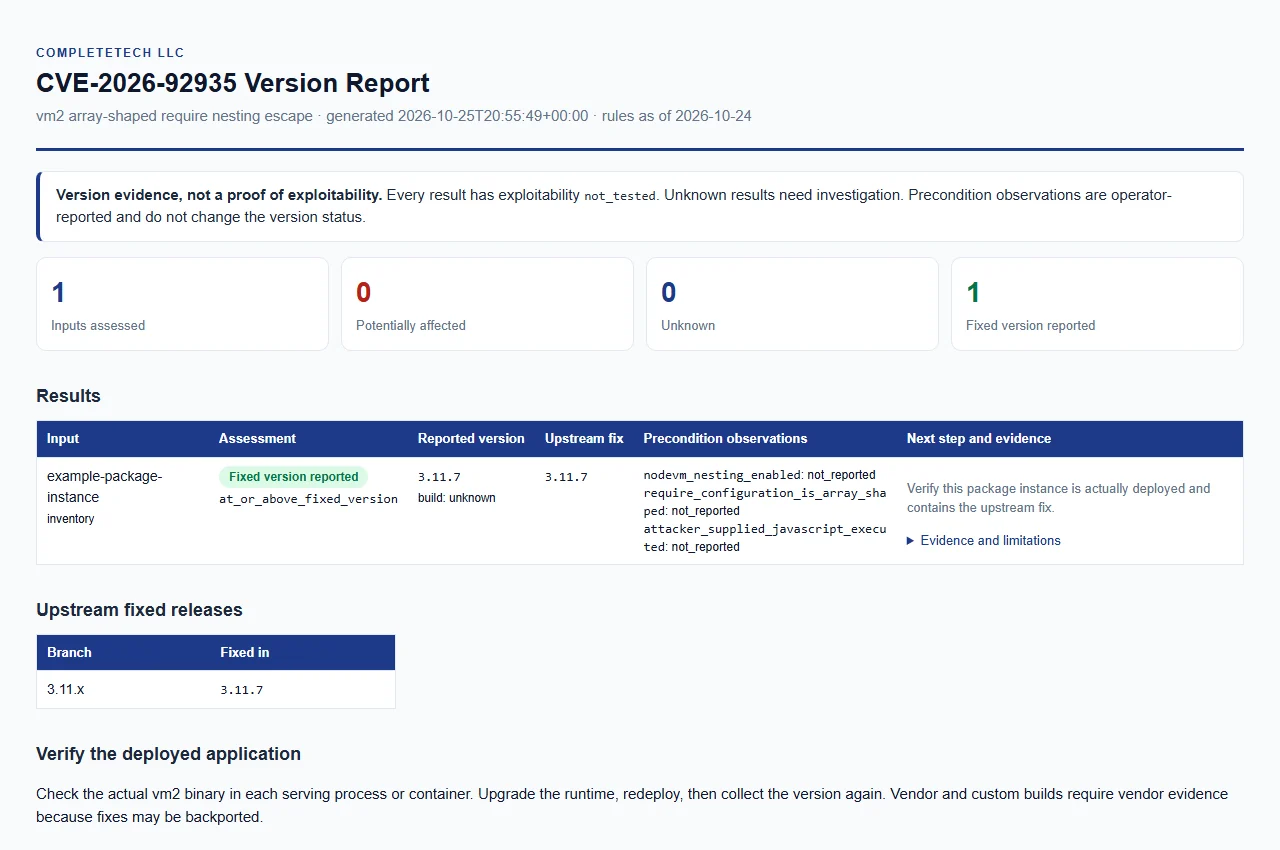
Open the synthetic example report. Example data only; this is not a live assessment.
Primary advisory and reviewed database retrieved 2026-10-24 (rules_as_of).
The documented affected interval is 3.11.4 through 3.11.6. The reviewed fixed release is 3.11.7, and the reviewed fixed line is 3.11.x.
| Example reported version | Result |
|---|---|
| 3.11.3 | unknown |
| 3.11.4 | potentially_affected |
| 3.11.6 | potentially_affected |
| 3.11.7 | fixed_version_reported |
| 3.11.8 | fixed_version_reported |
| 3.12.0 | unknown |
| 4.0.0 | unknown |
Notes on the boundaries:
v is accepted (v3.11.7). Missing, conflicting, malformed, prerelease, qualified, custom/vendor builds remain unknown.--build-source (or the build_source field) of blank, unknown (the default), upstream, official or official_upstream is compared as upstream. Any other value, such as a vendor name, yields unknown because it needs independent patch evidence.Each input value is a separate package instance; the checker does not reconcile evidence across entries for a single instance. Inputs can be combined in one run.
| Option | Input |
|---|---|
--version VERSION (alias --package-version) | Reported vm2 version; repeatable. |
--inventory FILE | JSON object or array of objects; repeatable. |
--csv-list FILE | CSV with a header row; repeatable. |
--source FILE | Explicit JS/TS file for lexical review (see Source review candidates); repeatable. |
--source-root DIR | Required with --source; evidence paths are relative to it. |
--build-source SOURCE | Provenance of the --version builds, at most 512 characters. Applies to CLI versions. |
--nodevm-nesting-enabled, --require-configuration-is-array-shaped, --attacker-supplied-javascript-executed (true or false) | Operator observations applied to CLI versions. |
JSON inventory. One object or an array of objects. Required: integer schema_version: 1 and string package_version. Optional: package: "vm2", label, build_source, and the observation keys below. Unknown or duplicate keys, wrong types, non-finite numbers and malformed inputs are rejected. See examples/inventory.example.json.
