 completetech-security/node-cve-2026-106070-check
Offline Node.js evidence checker for CVE-2026-106070: ZipFile invalid-header content substitution. Single-file Python; JSON/CSV/HTML reports; no exploit payloads.





Offline version-evidence checker for CVE-2026-106070, Node.js: ZipFile invalid-header content substitution. It compares Node.js runtime versions that you report against the fixed release named in the vendor advisory and writes a CSV, JSON or HTML triage report. Python 3.10+, standard library only; the executable can be copied alone.
Triage evidence, not an assessment of a deployed system. The checker reads versions you supply. It does not inspect the machine it runs on, run Node.js, or test exploitability, so a result never confirms exploitation or a verified patch.
This repository covers only CVE-2026-106070. The checker is deliberately conservative:
unknown. Unknown is never reported as safe.exploitability: not_tested.fixed_version_reported says the reported version is at or above the upstream fixed release. It does not attest that the deployed runtime is patched.Use it only for inventories you are authorized to assess. Developing or running the checker authorizes no scanning of real targets.
node_cve_2026_106070_check.py has no runtime dependencies and can be copied on its own; no companion repository is needed.--version values, a JSON inventory or a CSV list.# One runtime, JSON report on stdout
python node_cve_2026_106070_check.py --version 26.12.1 --format json
# JSON inventory to an HTML report file
python node_cve_2026_106070_check.py --inventory examples/inventory.example.json --format html --output report.html
# CSV list (CSV is the default format), exit 1 on potentially_affected or unsupported_runtime
python node_cve_2026_106070_check.py --csv-list inventory.csv --fail-on-finding
# All options
python node_cve_2026_106070_check.py --help
--version is repeatable; each value describes a separate runtime. JSON, CSV and HTML reports are built from the same evidence. Without --output the report goes to stdout.
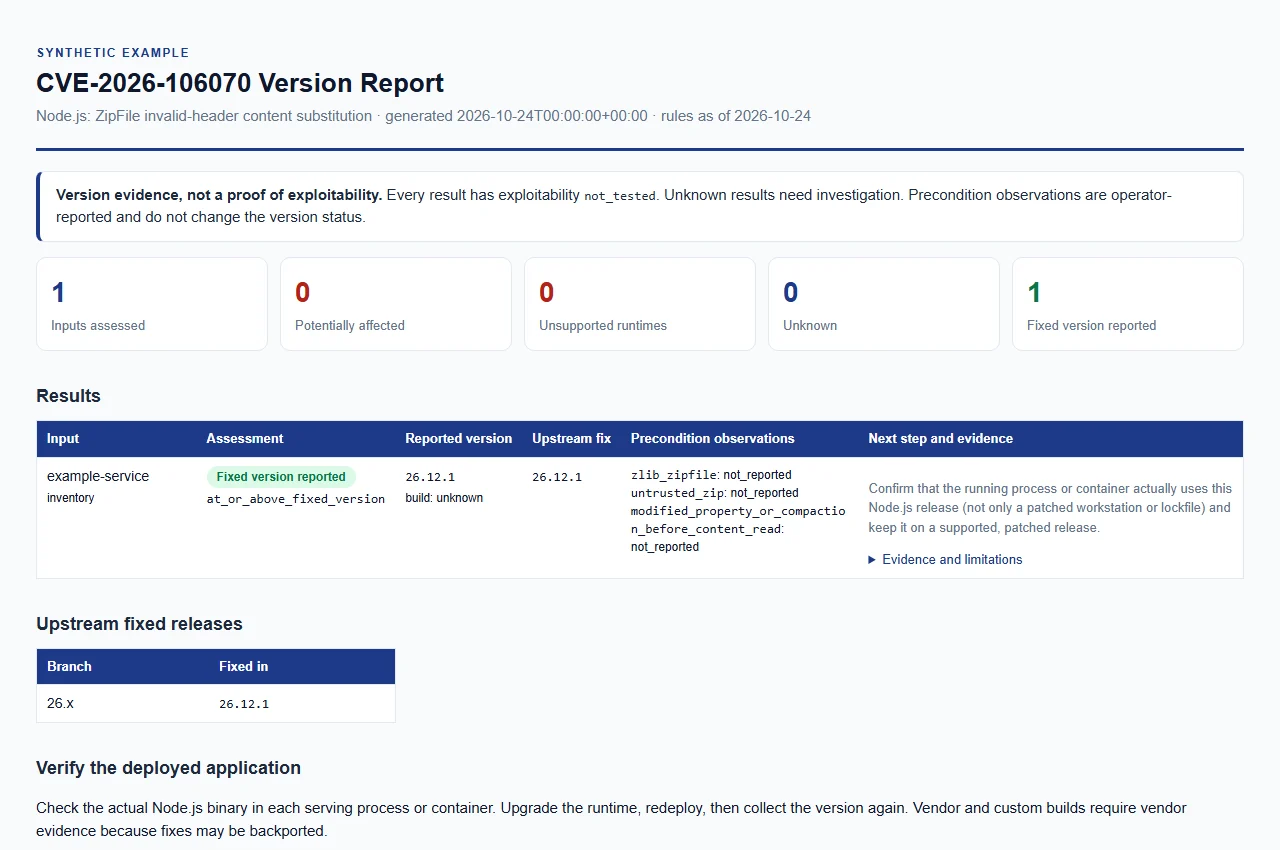
Open the synthetic example report. Example data only; this is not a live assessment.
A run needs at least one of --version, --inventory or --csv-list; you can combine them and repeat each. Inputs must be regular UTF-8 files within the limits. Synthetic examples are in examples/ and docs/example-report.html.
A version is normalized by stripping ASCII whitespace and at most one leading v. Only a plain stable release (MAJOR.MINOR.PATCH, no leading zeros) is compared. Prereleases, nightly or rc builds, package suffixes, partial versions such as 26.12 and anything longer than 128 characters are unknown.
One object or an array of objects. Unknown keys, duplicate keys, non-finite numbers and invalid types are rejected.
| Field | Required | Notes |
|---|---|---|
schema_version | yes | Integer 1 |
node_version | yes | String |
runtime | no | Only "node" is accepted |
label | no | Shown in reports; defaults to <file name without extension>:<position> |
build_source | no | Build provenance, see Build source |
| Observation keys | no | The three keys below; each boolean or null |
[
  {
    "schema_version": 1,
    "label": "example-service",
    "runtime": "node",
    "node_version": "26.12.1",
    "build_source": "unknown",
    "zlib_zipfile": null,
    "untrusted_zip": null,
    "modified_property_or_compaction_before_content_read": null
  }
]
The header row must include node_version and have no duplicate columns. Optional columns are label, build_source and the observation keys; any other column is rejected, including schema_version and runtime. Observation cells are exactly true, false or blank. Rows must have the same number of fields as the header, and quotes inside unquoted cells, text after a closing quote, unterminated quotes and NUL characters are rejected.
build_source records where the runtime build came from. An empty value, unknown, upstream, official and official_upstream (compared case-insensitively) are treated as an upstream build, so the default unknown is compared as upstream. Any other value is treated as a vendor, distribution or custom build. Its result is unknown because an upstream version number does not show which patches or backports that build contains.
Each record may carry three observations. They are operator-supplied, unverified, and never change the version result or establish reachability.
| Observation key | Advisory precondition |
|---|---|
zlib_zipfile | zlib zipfile |
untrusted_zip | untrusted zip |
modified_property_or_compaction_before_content_read | modified property or compaction before content read |
Reports show each as reported_true, reported_false or not_reported.
