 0xrawsec/whids
Windows EDR with Gene-based detection engine, real-time artifact collection, Sysmon integration, and REST API for managing endpoints, rules, and incident response workflows.

IMPORTANT: this README and other documentation is not updated to reflect the changes made to latest beta releases (as a lot of changes happened). All this will be updated in time when a stable version will be released (see Roadmap until next release). Feel free to run beta releases on your own and ask questions if you need help.


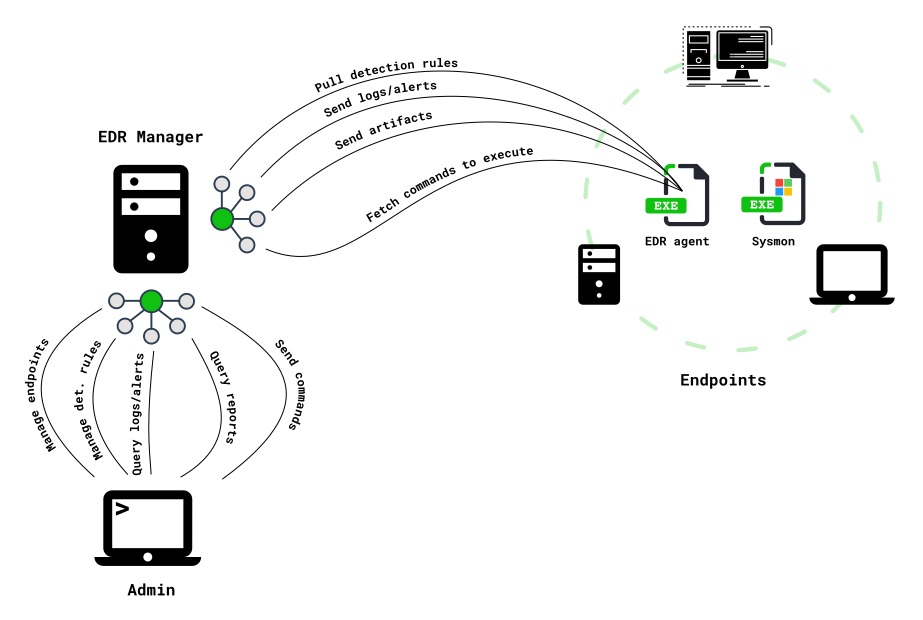
EDR with artifact collection driven by detection. The detection engine is built on top of a previous project Gene specially designed to match Windows events against user defined rules.
It means that an alert can directly trigger some artifact collection (file, registry, process memory). This way you are sure you collected the artifacts as soon as you could (near real time).
All this work has been done on my free time in the hope it would help other people, I hope you will enjoy it. Unless I get some funding to further develop this project, I will continue developing it on a best effort basis. I will make all I can to fix issues in time and provide updates. Feel free to open issues to improve that project and keep it alive.
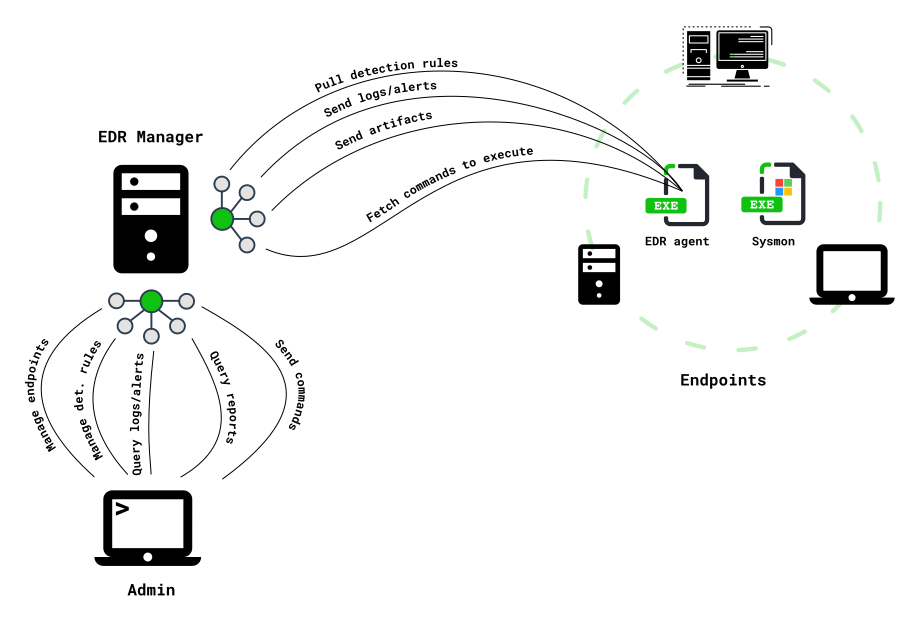
NB: the EDR agent can be ran standalone (without being connected to an EDR manager)
NB: event filtering can be done at 100% with Gene rules so do not bother creating a complicated Sysmon configuration.
In order to get the most of WHIDS you might want to improve your logging policy.
Computer Configuration\Windows Settings\Security Settings\Advanced Audit Policy Configuration\System Audit Policies\System\Audit Security System Extension -> EnableComputer Configuration\Windows Settings\Security Settings\Advanced Audit Policy Configuration\System Audit Policies\Object Access\Audit File System -> EnableSelect a principal (put here the name of the user/group you want the audit for). Put group Everyone if you want to log access from any user.Apply this to is used to select the scope of this audit policy starting from the folder you have selectedBasic permissions select the kinds of accesses you want the logs to be generated forSecurity log channelMicrosoft-Windows-Windows Defender/Operational monitored by the EDR.This section covers the installation of the agent on the endpoint.
manage.bat as administratormanage.bat or using your preferred text editormanage.bat or just reboot (preferred option otherwise some enrichment fields will be incomplete leading to false alerts)NB: At installation time the Sysmon service will be made dependent of WHIDS service so that we are sure the EDR runs before Sysmon starts generating some events.
The EDR manager can be installed on several platforms, pre-built binaries are provided for Windows, Linux and Darwin.
