 0xblackash/cve-2026-46331
CVE-2026-46331

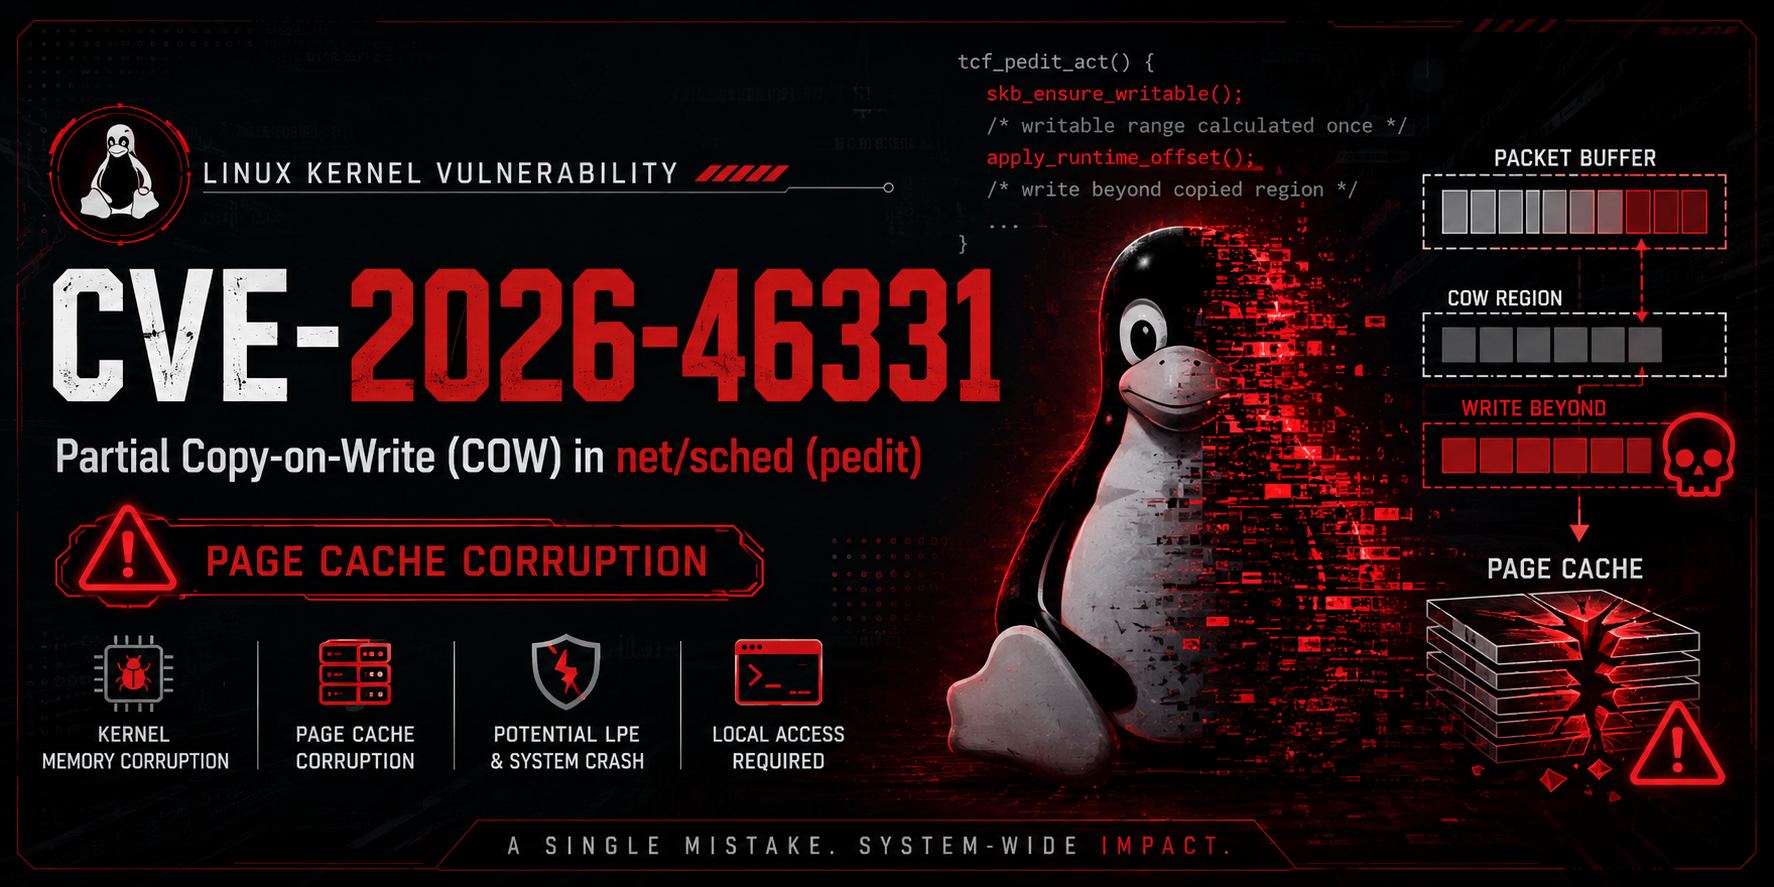
net/sched Partial Copy-on-Write (COW) Page Cache Corruption

A Linux kernel vulnerability caused by incorrect Copy-on-Write (COW) handling in the traffic control (tc) packet editing subsystem.
CVE-2026-46331 is a Linux kernel vulnerability affecting the net/sched packet editing (act_pedit) subsystem.
The vulnerability occurs because the kernel calculates the writable Copy-on-Write (COW) range before the actual packet-edit offset is known. When runtime header offsets are applied, portions of memory may remain writable without being copied, resulting in page cache corruption.
Under specific conditions, this corruption can become a powerful primitive for local privilege escalation (LPE) or kernel instability. :contentReference[oaicite:0]{index=0}
Linux Kernel
└── net/
    └── sched/
        └── act_pedit.c
Affected function:
tcf_pedit_act()
Problem:
skb_ensure_writable()
        │
        ▼
Calculates writable range only once
        │
        ▼
Runtime header offsets change later
        │
        ▼
Memory outside COW region is modified
        │
        ▼
Page Cache Corruption
The vulnerable implementation:
tcfp_off_max_hint.This creates a partial Copy-on-Write condition that can corrupt cached kernel pages. :contentReference[oaicite:1]{index=1}
Possible consequences include:
An attacker generally requires:
tc)CAP_NET_ADMIN (directly or through an unprivileged user namespace, depending on system configuration)No remote attack vector has been described in the official advisory. :contentReference[oaicite:3]{index=3}
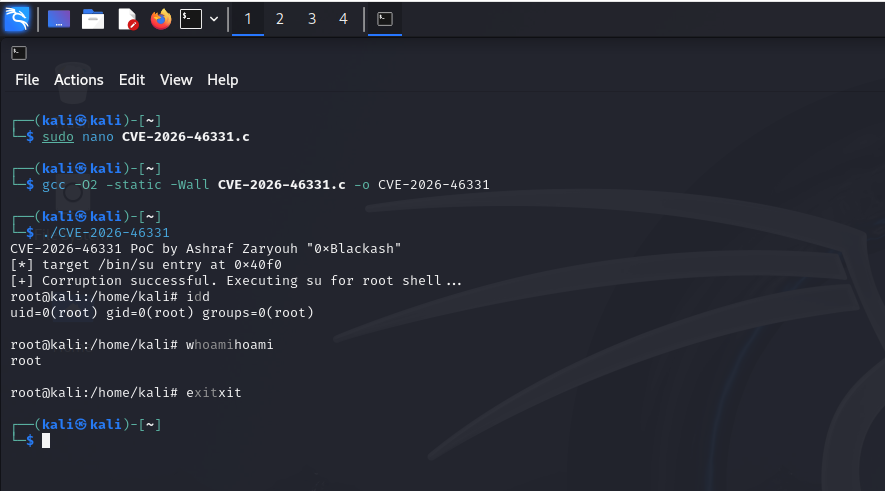
Traffic Control (tc)

        │

 act_pedit

        │

 tcf_pedit_act()

        │

 skb_ensure_writable()

        │

 Partial COW

        │

 Page Cache Corruption
The upstream kernel patch:
skb_ensure_writable() inside the per-key processing loop.skb_cow() for negative offsets.INT_MIN). :contentReference[oaicite:4]{index=4}CAP_NET_ADMIN.tc packet-edit rules.| Field | Value |
|---|---|
| CVE | CVE-2026-46331 |
| Component | Linux Kernel net/sched |
| Module | act_pedit |
| Vulnerability | Partial Copy-on-Write |
| Impact | Page Cache Corruption |
| Possible Result | Kernel Memory Corruption / Potential LPE |
| Attack Vector | Local |
| Privileges Required | Typically CAP_NET_ADMIN |
| Fix Available | ✅ Yes |
Kernel vulnerabilities evolve rapidly.
Always keep your Linux kernel updated with the latest stable security patches.

