
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-11645 β€” CVE-2026-11645 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-11645
Vulnerability AnalysisExploitationWeb SecurityThreat IntelligenceLearning & EducationIncident Response
GitHub0xblackash/cve-2026-11645

CVE-2026-11645

CVE-2026-11645

View Repository
1275 months agoNot yet reviewed
Share

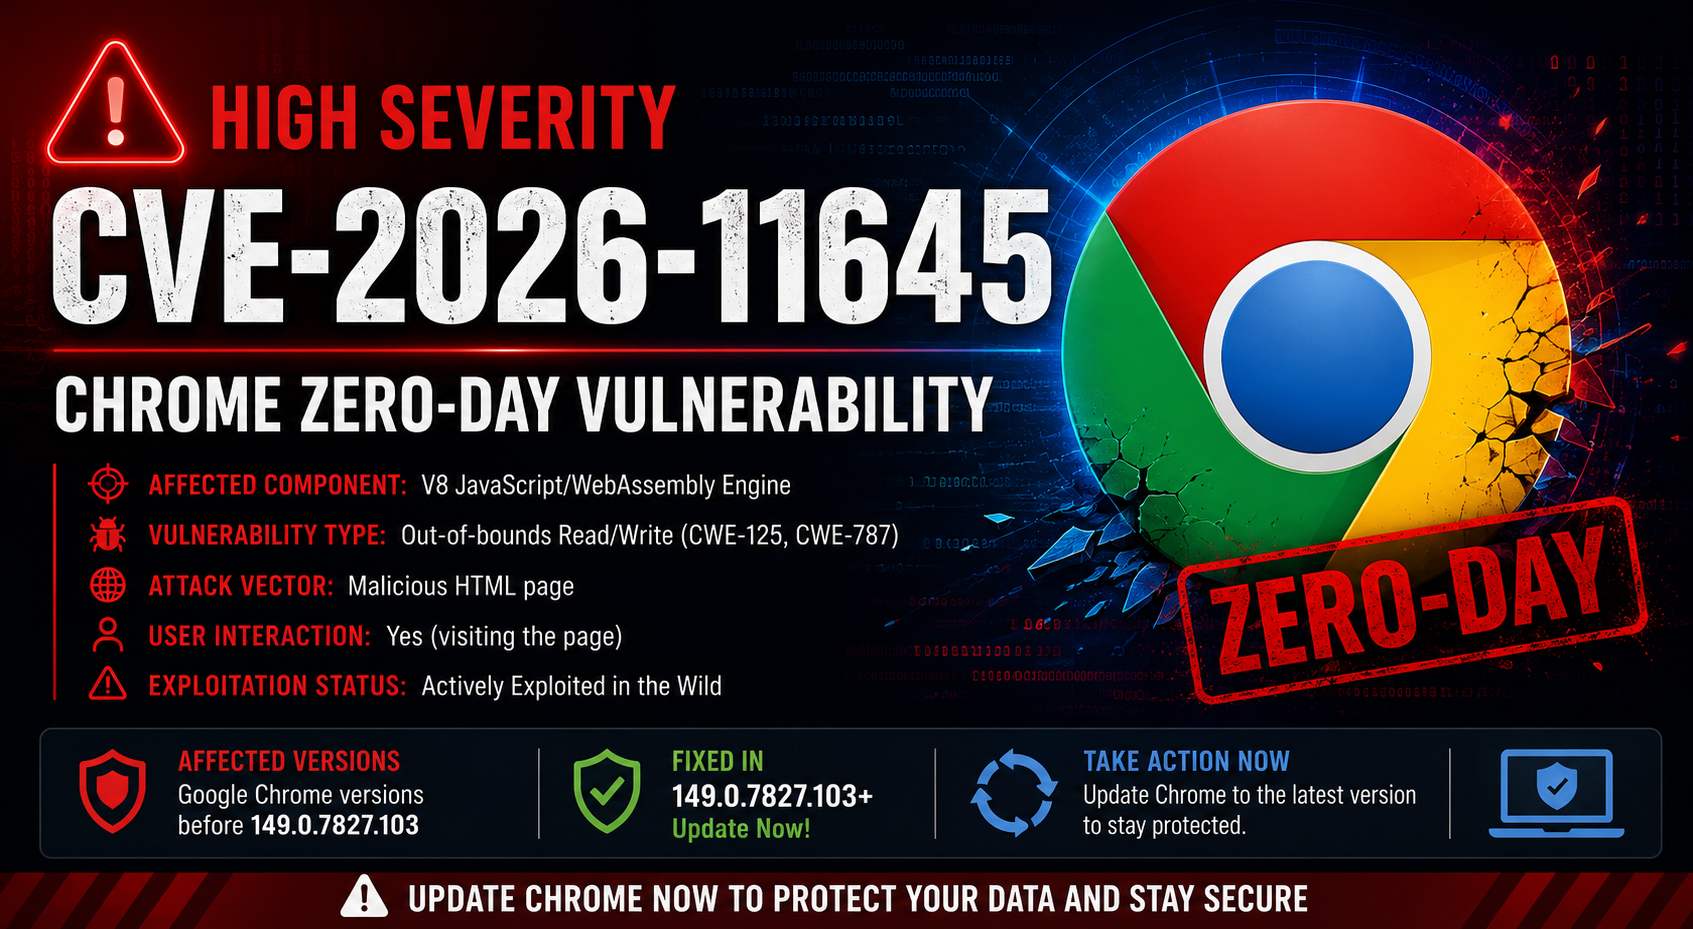
🚨 CVE-2026-11645 🚨

🌐 Google Chrome V8 Zero-Day Memory Corruption Vulnerability

ChatGPT Image Jun 11, 2026, 04_25_47 PM

Severity CVSS Status Chrome

πŸ”₯ Actively Exploited Zero-Day

⚑ V8 Engine Memory Corruption

πŸ›‘οΈ Patch Immediately


πŸ“– Overview

⚠️ CVE-2026-11645 is a high-severity zero-day vulnerability affecting the Google Chrome V8 JavaScript engine. The flaw allows attackers to trigger an Out-of-Bounds Read/Write condition that may lead to Remote Code Execution (RCE).


🎯 Vulnerability Information

🏷️ FieldπŸ“‹ Value
CVECVE-2026-11645
πŸ”₯ SeverityHigh
πŸ“Š CVSS8.8
🏒 VendorGoogle
🌐 ProductChrome
🧩 ComponentV8 Engine
πŸ’₯ TypeOut-of-Bounds Read/Write
⚠️ ExploitedYes
🎯 ImpactRemote Code Execution

🧠 Technical Summary

The vulnerability exists within Chrome's V8 JavaScript engine.

An attacker can craft a malicious webpage that:

  • 🎯 Triggers memory corruption
  • πŸ“– Reads unintended memory regions
  • ✍️ Writes outside allocated boundaries
  • πŸ’» Executes arbitrary code
  • πŸ”“ Assists exploitation chains
  • 🚨 Causes browser crashes

βš”οΈ Attack Chain

🌐 Victim Opens Malicious Website
                β”‚
                β–Ό
πŸ“œ Crafted JavaScript Payload
                β”‚
                β–Ό
🧩 V8 Engine Vulnerability Triggered
                β”‚
                β–Ό
πŸ’₯ Out-of-Bounds Memory Access
                β”‚
                β–Ό
⚑ Remote Code Execution
                β”‚
                β–Ό
🚨 Browser Compromise

🎯 Affected Versions

❌ Vulnerable

Chrome < 149.0.7827.103
CVE-2026-11645

βœ… Fixed

πŸͺŸ Windows : 149.0.7827.102+
🍎 macOS   : 149.0.7827.103+
🐧 Linux   : 149.0.7827.102+

πŸ’₯ Potential Impact

ImpactRisk
⚑ Remote Code ExecutionπŸ”΄ High
πŸ” Information DisclosureπŸ”΄ High
πŸ’£ Browser Crash🟠 Medium
πŸ”— Exploit Chaining🟠 Medium
🏒 Enterprise RiskπŸ”΄ High

πŸ”Ž Detection Opportunities

Monitor for:

🚨 Indicators:
  - Unexpected browser crashes
  - Suspicious JavaScript activity
  - Exploit-kit traffic
  - Malicious domain visits
  - Unusual Chrome child processes
  - Browser memory anomalies

πŸ›‘οΈ Mitigation

πŸš€ Immediate Actions

chrome://settings/help

βœ… Recommendations

  • πŸ”„ Update Chrome immediately
  • πŸ›‘οΈ Enable automatic updates
  • πŸ”’ Restrict untrusted extensions
  • πŸ“‘ Monitor browser telemetry
  • 🚨 Review EDR alerts
  • πŸ“Š Track threat intelligence feeds

πŸ“ˆ Risk Assessment

Likelihood  : β–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆ  HIGH
Impact      : β–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆβ–ˆ  HIGH
Overall     : 🚨 CRITICAL 🚨

πŸ“š References

  • 🌐 Google Chrome Security Advisory
  • πŸ›οΈ NIST National Vulnerability Database
  • πŸ”¬ Chromium Security Updates

⚠️ Disclaimer

This repository is provided for:

  • πŸŽ“ Security Education
  • πŸ” Vulnerability Research
  • πŸ›‘οΈ Defensive Security
  • πŸ“Š Patch Management

❌ No exploit code is included.


⭐ Stay Updated β€’ Patch Early β€’ Hunt Smart ⭐

πŸš€ Cyber Threat Intelligence Repository πŸš€

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    930
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    349
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools β†’