
keyhog v0.5.47
Open-source secret scanner in Rust


Website · Documentation · Architecture · Vyre GPU engine
KeyHog: GPU-accelerated secret scanner for code, cloud, and CI
KeyHog is an open-source secret scanner in Rust that finds and verifies leaked API keys, tokens, passwords, and credentials across source code, Git history, containers, cloud storage, browser assets, collaboration content, and running systems.
Most secret scanners stop at CPU regex matches in a repository checkout. KeyHog combines 934 service-specific detectors, decode-through for concealed credentials, context-aware evidence and suppression, live provider verification, and first-class CUDA, Metal, and WGPU execution through Vyre. Calibration measures every eligible pure-Rust CPU, Hyperscan/SIMD, and GPU backend. Automatic routing then uses the fastest parity-proven route for the exact host and workload class.
| GPU is a real backend | Scan the actual attack surface | Separate signal from noise | Act on the result |
|---|---|---|---|
| CUDA, native Metal, and WGPU are measured peers, not a silent fallback chain. | Scan Git history, Docker layers, archives, cloud buckets, source maps, WASM, HAR captures, hosted Git collections, and whole systems. | Decode base64, hex, URL, protobuf, multiline, and structured configuration before applying evidence, example suppression, and baselines. | Verify eligible credentials with provider APIs, emit SARIF or structured envelopes, and preserve exact coverage and exit semantics. |
cargo install --locked keyhog
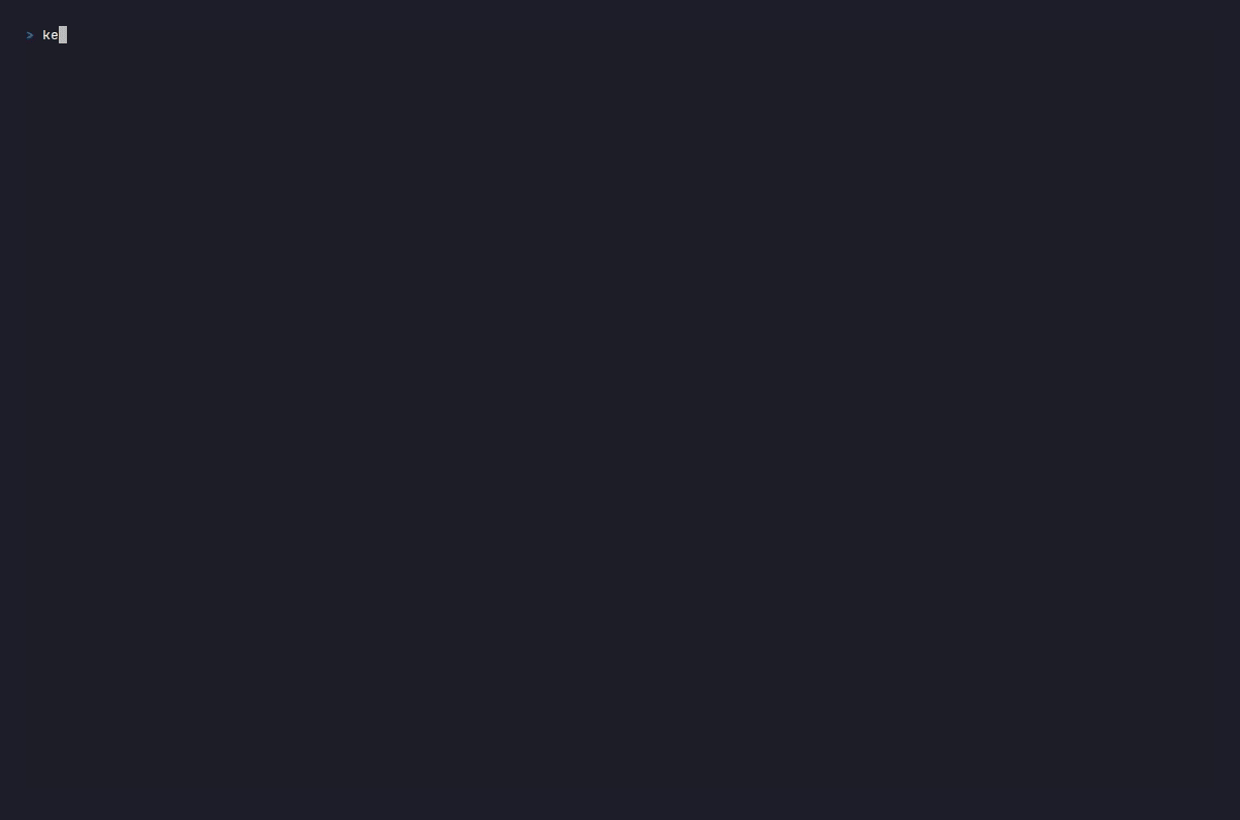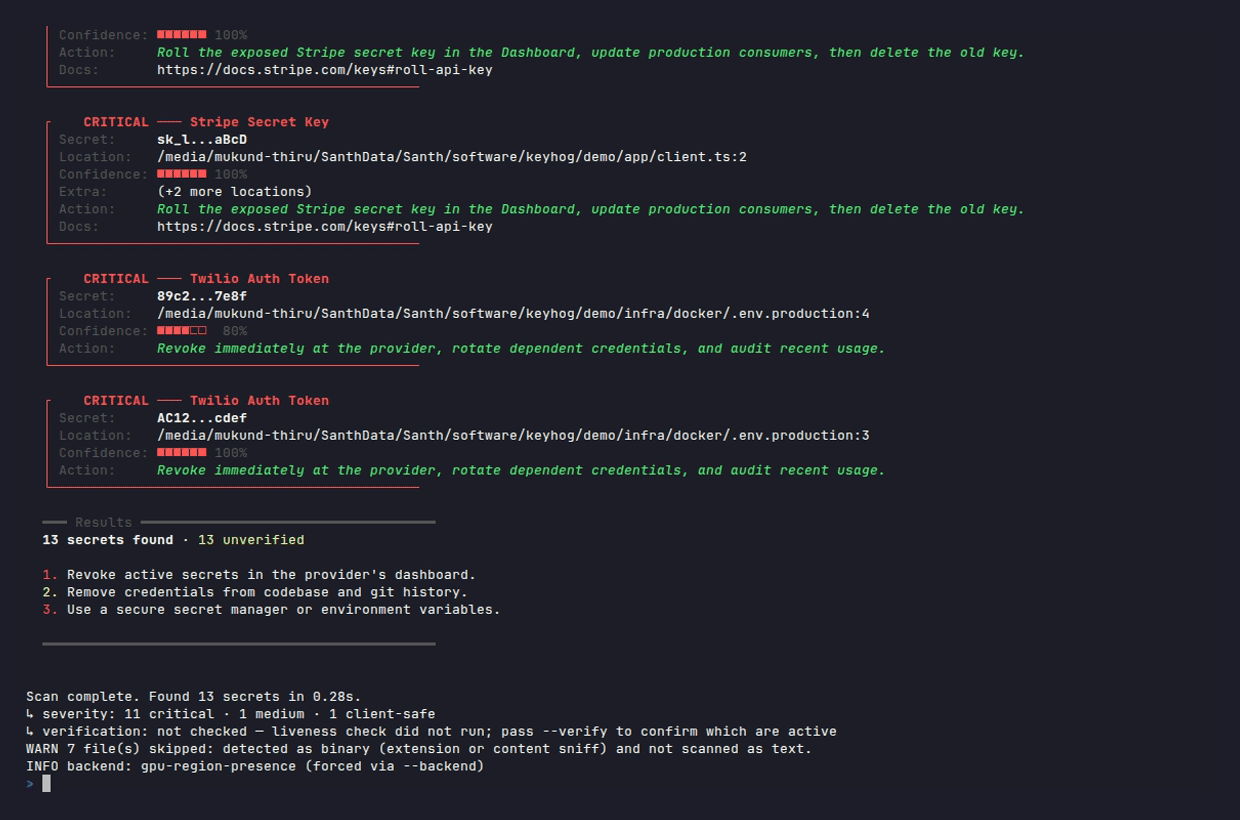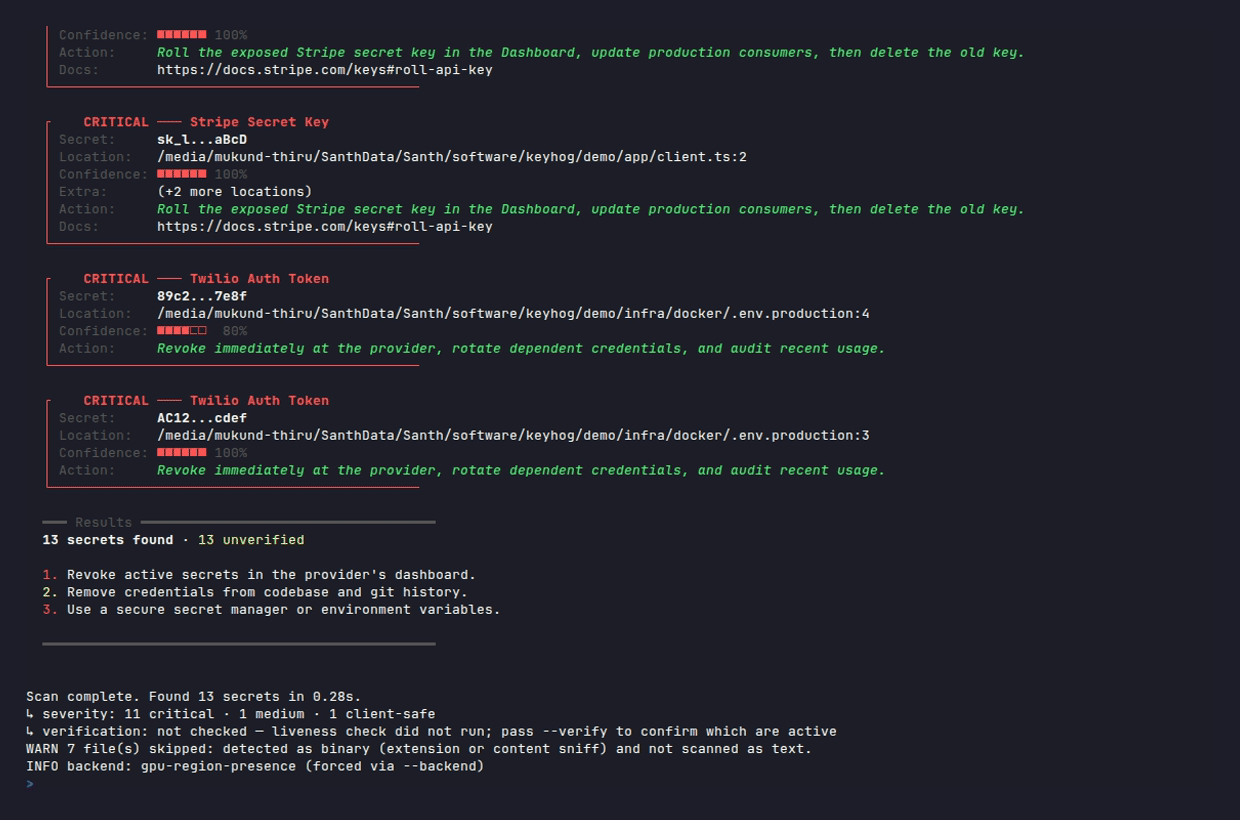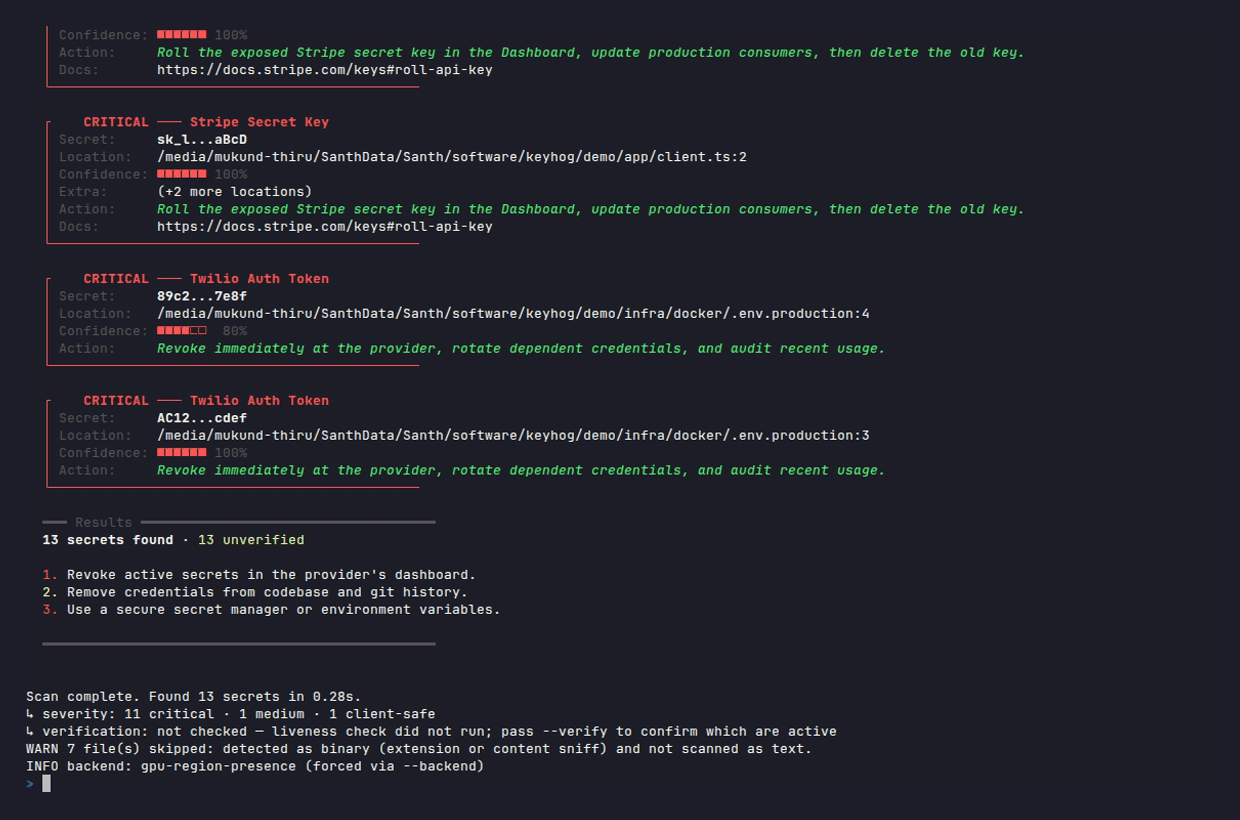
keyhog scan .
A secret scanner built around the GPU
KeyHog does not hand a few regular expressions to a generic compute shader. Its GPU path is built on Vyre, a Rust GPU compute substrate developed alongside KeyHog. Detector triggers compile into immutable GPU-resident tables. Bounded source batches produce complete match positions for the same confirmation, suppression, evidence, and reporting pipeline used by CPU and Hyperscan routes.
- Three physical GPU peers. CUDA, native Metal, and portable WGPU are acquired, measured, and reported independently.
- Exact result parity. Calibration rejects a candidate whose finding identity differs from the reference route. A faster wrong answer never enters the routing table.
- Persistent route evidence. KeyHog records the binary, detector corpus, configuration, workload class, host, accelerator, driver, and measured timing evidence. Normal scans do not benchmark in the hot path.
- Resident execution. Daemon workers keep compiled detector and accelerator state warm for repeated file, archive, history, remote, and cloud batches.
- No hidden CPU escape hatch. An explicitly selected accelerator that cannot initialize or dispatch fails visibly instead of returning CPU findings under a GPU label.
The default crates.io install uses the portable pure-Rust CPU route so it works on a clean Rust host. Enable the three GPU peers without acquiring Hyperscan:
cargo install --locked keyhog --no-default-features --features portable,gpu
Enable the Hyperscan or Vectorscan SIMD regex peer:
cargo install --locked keyhog --no-default-features --features portable,simd
Run the production backend diagnostic, then inspect the measured route:
keyhog backend --self-test
keyhog calibrate-autoroute --policy all
keyhog backend --autoroute --json
The backend guide documents the resident tables, bounded dispatch model, parity contract, and reproducible crossover evidence.
Get started
Install and run your first scan
The two commands above install the latest crates.io release and scan the current tree with the portable pure-Rust route.
Pin a CI environment to one exact release with
cargo install --locked --version '=0.5.86' keyhog. KeyHog requires Rust 1.89
or newer. See the installation guide
for GPU, Hyperscan, CI, portable, and source-build profiles.
KeyHog exits 1 when a finding blocks the active evidence policy. The default
policy blocks likely and confirmed findings while keeping review findings
visible with exit 0; --evidence-policy paranoid blocks every tier. Review
each finding's exact evidence tier, reason code, file, line, detector, and
remediation. Other nonzero codes describe input, system, verification, or
coverage failures; see the
exit-code reference.
The complete process contract is:
| Exit | Meaning |
|---|---|
0 success | No finding blocks the active evidence policy, and no coverage failure occurred. Review-tier findings can remain visible under the default policy. |
1 blocking findings | At least one finding blocks the active evidence policy, but none were confirmed live. |
2 operator error | Fix the arguments, configuration, detector corpus, or operator-correctable input. |
3 system error | Repair or retry the runner. This includes low-level I/O, fatal daemon service, incremental-cache, and explicitly selected SIMD failures. |
4 health/self-test failure | A doctor or backend --self-test health check was unhealthy. |
10 live credentials | At least one credential was confirmed live. |
11 scanner panic | Discard the scan result because scanner state is not trustworthy. |
12 required GPU failure | An explicitly selected or required GPU path could not execute. |
13 incomplete coverage | A requested source failed or input coverage was incomplete, and no finding outcome took precedence. |
130 interrupted | SIGINT or Ctrl-C interrupted the process. |
Filter, format, gate:
Create a baseline before using it as a filter:
keyhog scan . --create-baseline .keyhog-baseline.json
keyhog scan . --baseline .keyhog-baseline.json --format json-envelope --output keyhog.json