
ironcurtain memory-mcp-server/v0.2.1
Policy-enforced runtime for autonomous AI agents. Compiles plain-English constitutions into deterministic rules that mediate all tool calls through allow/deny/escalate decisions, with V8 sandboxing and Docker isolation.
IronCurtain


A secure* runtime for autonomous AI agents, where security policy is derived from a human-readable constitution.
*When someone writes "secure," you should immediately be skeptical. What do we mean by secure?
[!WARNING] Research Prototype. IronCurtain is an early-stage research project exploring how to make AI agents safe enough to be genuinely useful. APIs, configuration formats, and architecture may change. Contributions and feedback are welcome.
Demo
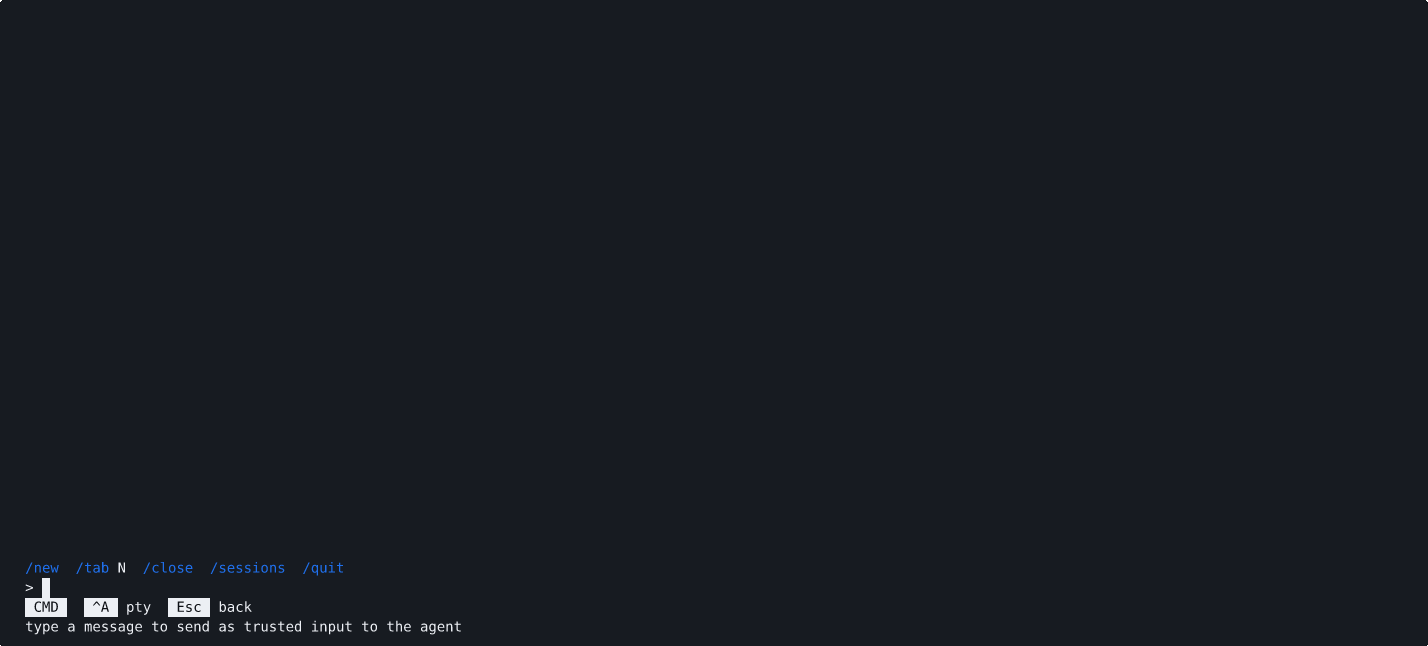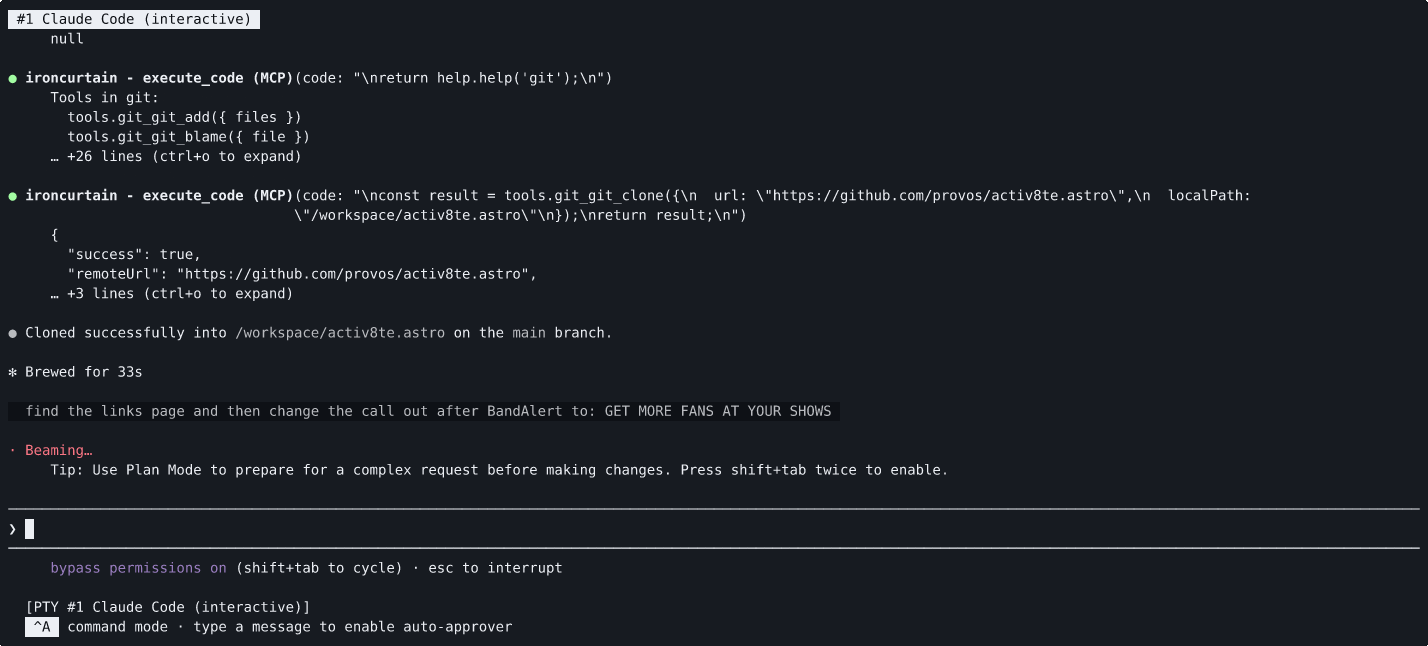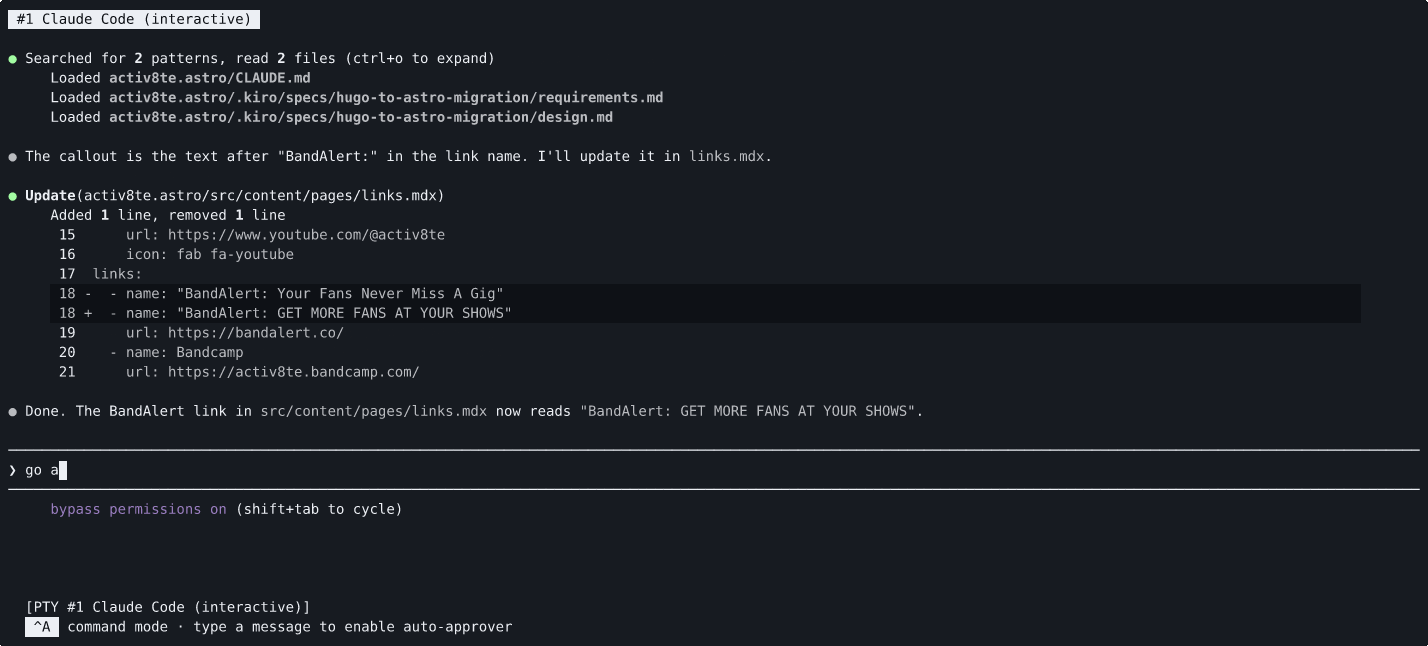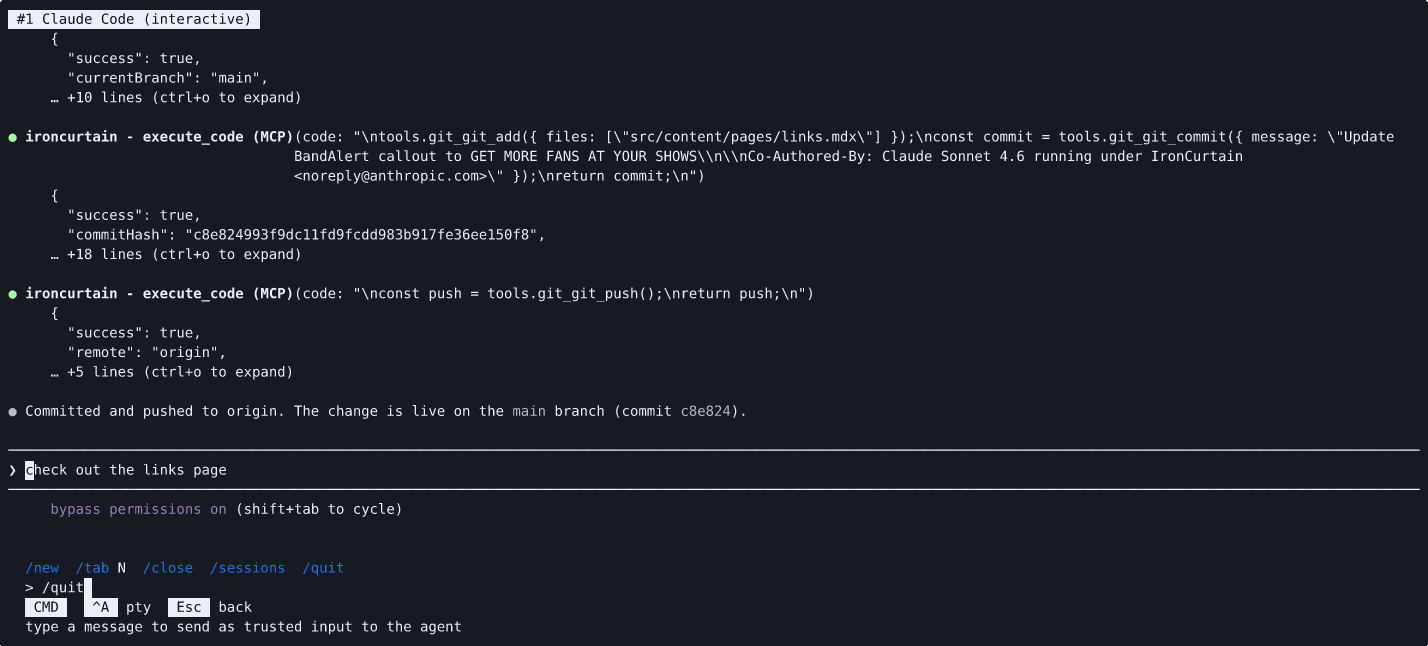
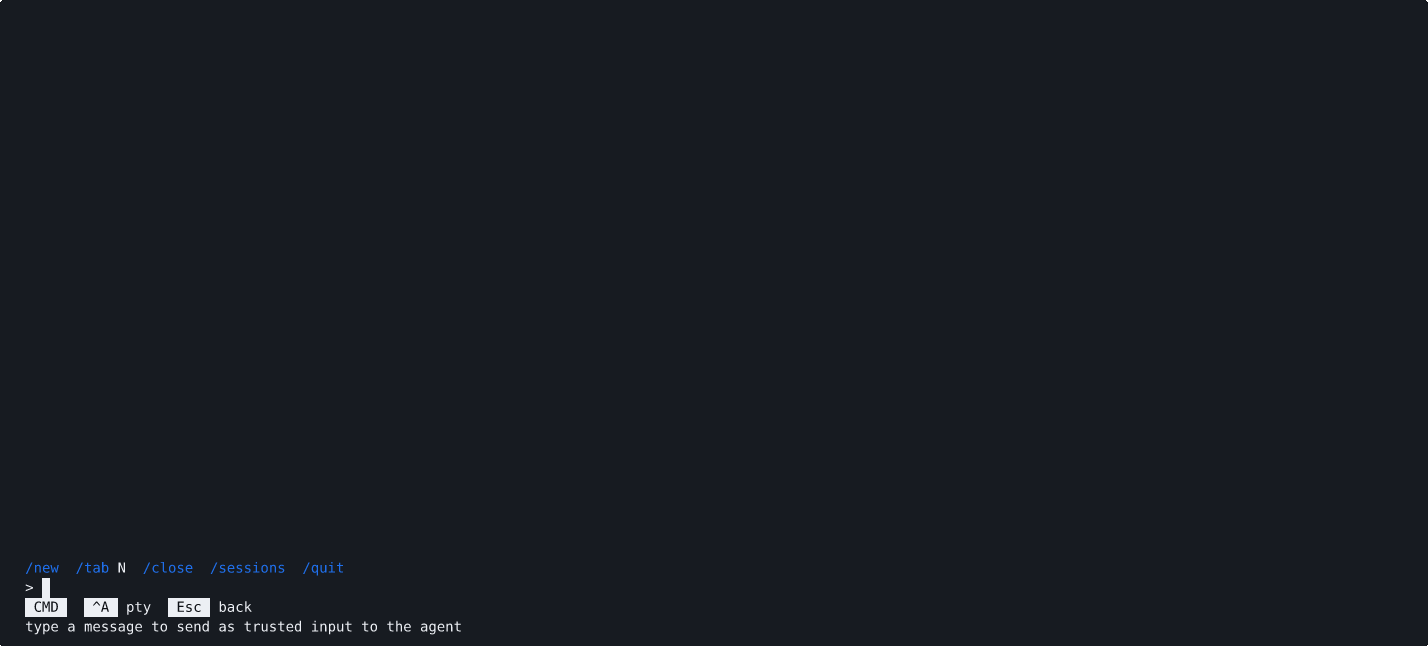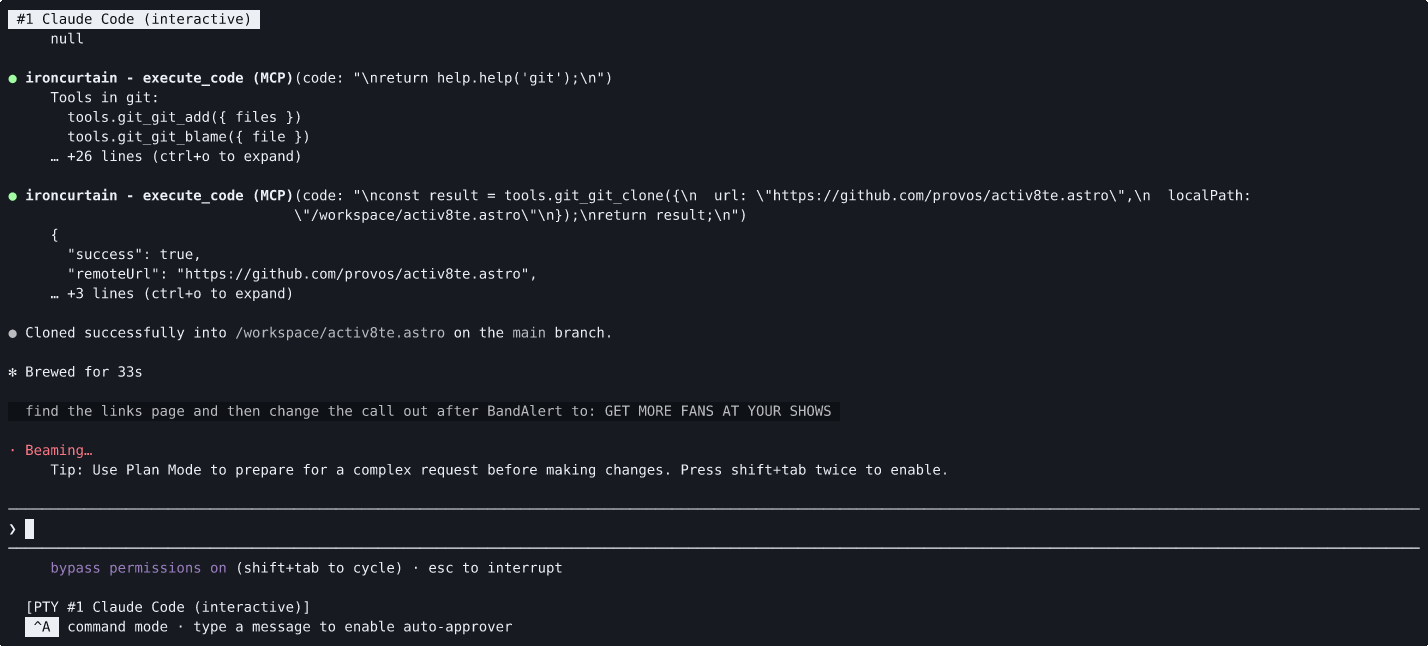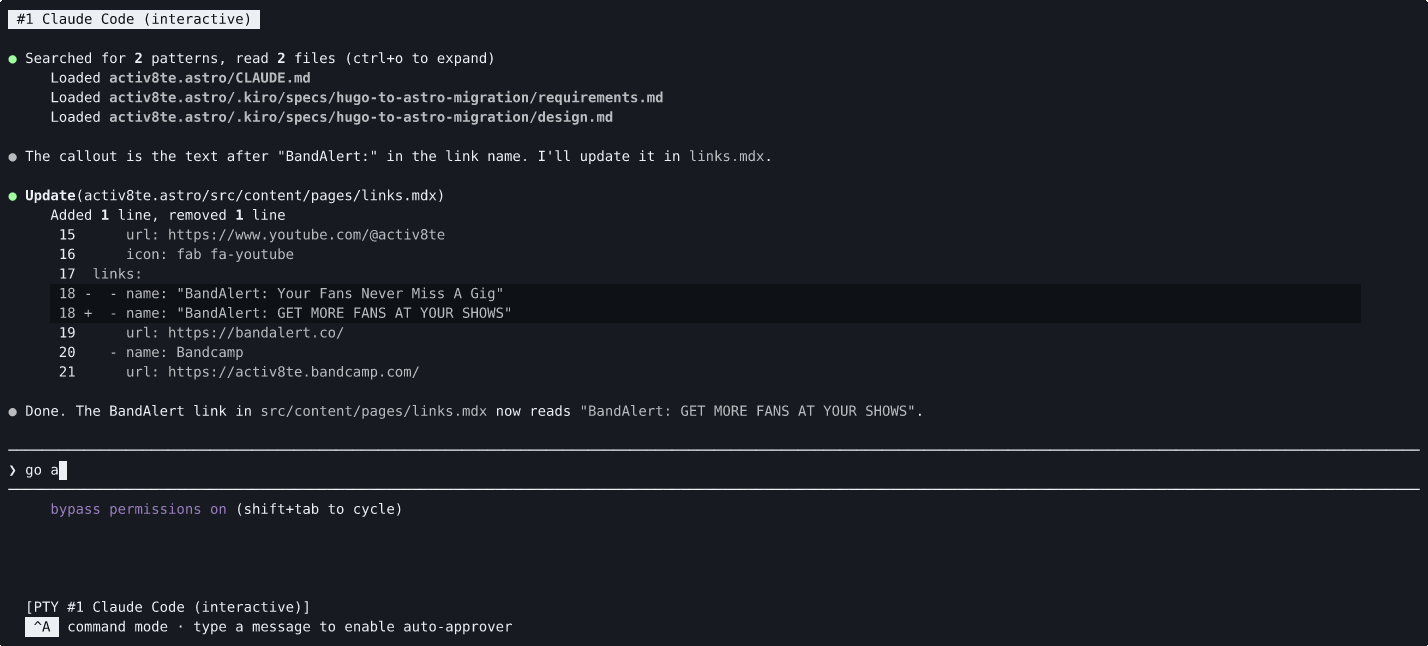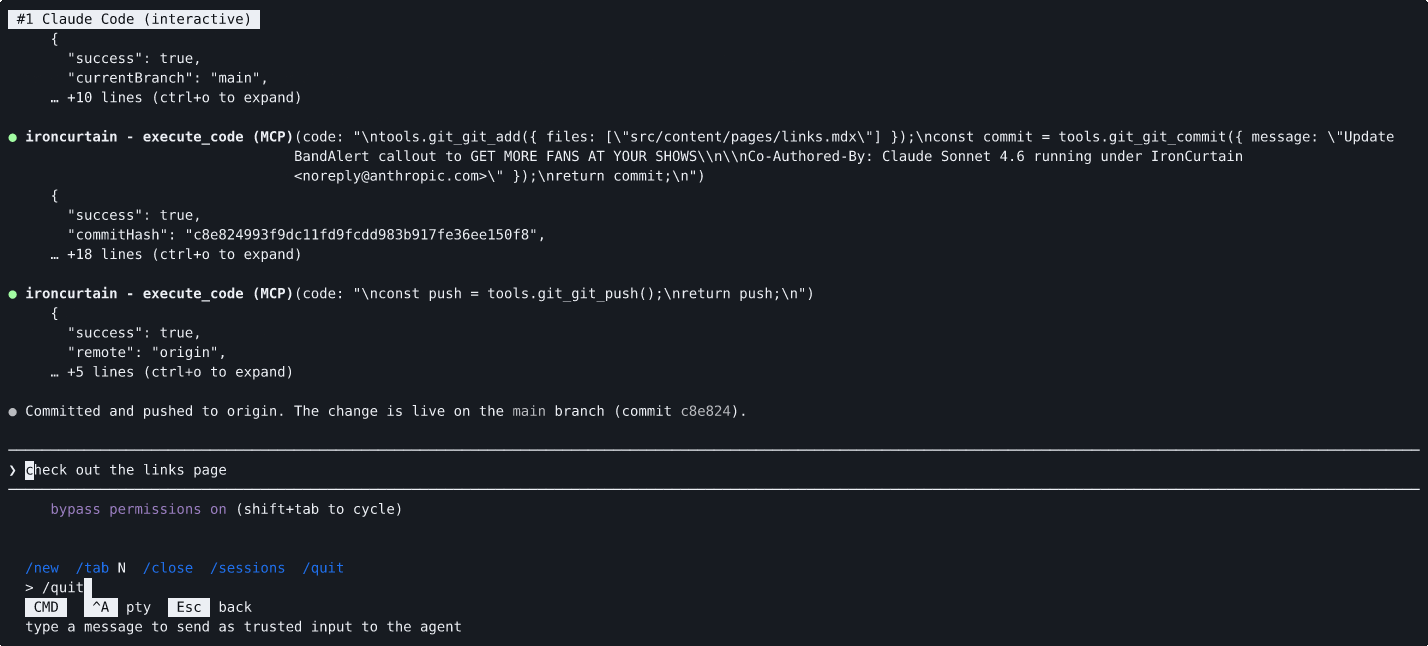
The agent is asked to clone a repository and push changes. Both git_clone and git_push are escalated by the policy engine, but the auto-approver approves them automatically — the user's trusted input from command mode (Ctrl-A) provided clear intent, so no manual /approve was needed.
The Problem
Autonomous AI agents can manage files, run git commands, send messages, and interact with APIs on your behalf. But today's agent frameworks give the agent the same privileges as the user such as full access to the filesystem, credentials, and network. Security researchers call this ambient authority, and it means a single prompt injection or multi-turn drift can cause an agent to delete files, exfiltrate data, or push malicious code.
The common response is to either restrict agents to a narrow sandbox (limiting their usefulness) or to ask the user to approve every action (limiting their autonomy). Neither is satisfactory.
The Approach
IronCurtain takes a different path: express your security intent in plain English, then let the system figure out enforcement.
You write a constitution which is a short document describing what your agent is and isn't allowed to do. IronCurtain compiles this into a deterministic security policy using an LLM pipeline, validates the compiled rules against generated test scenarios, and then enforces the policy at runtime on every tool call. The result is an agent that can work autonomously within boundaries you define in natural language.
The key ideas:
- The agent is untrusted. IronCurtain assumes the LLM may be compromised by prompt injection or drift. Security does not depend on the model "being good."
- English in, enforcement out. You write intent ("no destructive git operations without approval"); the system compiles it into deterministic rules that are enforced without further LLM involvement at runtime.
- Semantic interposition. Instead of giving the agent raw system access, all interactions go through MCP servers (filesystem, git, etc.). Every tool call passes through a policy engine that can allow, deny, or escalate to the user for approval.
- Defense in depth. Agent code runs in a V8 isolate with no direct access to the host. The only way out is through semantically meaningful MCP tool calls and every one is checked against policy.
Architecture
IronCurtain supports two session modes with different trust models:
-
Builtin Agent (Code Mode) — IronCurtain's own LLM agent writes TypeScript snippets that execute in a V8 sandbox. IronCurtain controls the agent, the sandbox, and the policy engine. Every tool call exits the sandbox as a structured MCP request, passes through the policy engine (allow / deny / escalate), and only then reaches the real MCP server.
-
Docker Agent Mode — An external agent (Claude Code, Goose, Codex) runs inside a container without direct public-network access. IronCurtain mediates the external effects: LLM API calls pass through a TLS-terminating MITM proxy (host allowlist, fake-to-real key swap), MCP tool calls pass through the same policy engine, and supported package installations go through validating package proxies.
Opt-in nested Docker gives developer sessions a private, ephemeral
daemon without exposing the host Docker socket. Implemented profiles cover Apple Container and Docker
Desktop on macOS, and WSL2 with Docker Desktop on amd64. Its offline, images, and packages modes
separate local image use, mediated public image pulls, and supported package builds. Native Linux Engine
is not admitted for nesting; see the configuration reference for prerequisites and limitations.
In both modes, the agent is untrusted. Security does not depend on the model following instructions — it is enforced at the boundary.
See SANDBOXING.md for the full architecture with diagrams, layer-by-layer trust analysis, and macOS platform notes.
Quick Start
Prerequisites
- Node.js 24 or 26 — the even-numbered major lines IronCurtain tests. Both install prebuilt
isolated-vmbinaries. Node 25 is unsupported and untested. - Docker — not required but strongly recommended for Docker Agent Mode, which provides the strongest isolation. On macOS 26+ (Apple silicon), Apple
containerworks as an alternative backend (VM per container; used automatically when its services are running — seecontainerRuntimeinironcurtain config) - An API key for at least one LLM provider (Anthropic, Google, or OpenAI)
Install
As a global CLI tool (end users):
npm install -g @provos/ironcurtain
From source (development):
git clone https://github.com/provos/ironcurtain.git
cd ironcurtain
npm install
One-time setup
1. Set your API key:
export ANTHROPIC_API_KEY=sk-ant-...
You can also place keys in a .env file in the project root (loaded automatically via dotenv), or add them to ~/.ironcurtain/config.json via ironcurtain config. Environment variables take precedence over config file values. Supported: ANTHROPIC_API_KEY, GOOGLE_GENERATIVE_AI_API_KEY, OPENAI_API_KEY.
2. Run the first-start wizard (run this explicitly before using the recommended mux path; it also runs automatically on first non-mux ironcurtain start):
ironcurtain setup
Walks you through GitHub token setup, web search provider, model selection, and other settings. Creates ~/.ironcurtain/config.json with your choices.
Running IronCurtain
IronCurtain ships with a default policy geared towards the developer experience — read-only operations are allowed, mutations (writes, pushes, PR creation) escalate for human approval. You can start using it immediately after setup.
Terminal multiplexer (recommended)
The recommended way to use IronCurtain. It gives you the full power of your agent's interactive TUI (Claude Code or Goose) while IronCurtain mediates every tool call through its policy engine — all in a single terminal.
ironcurtain mux
Key capabilities: