
dscanner — Updated!
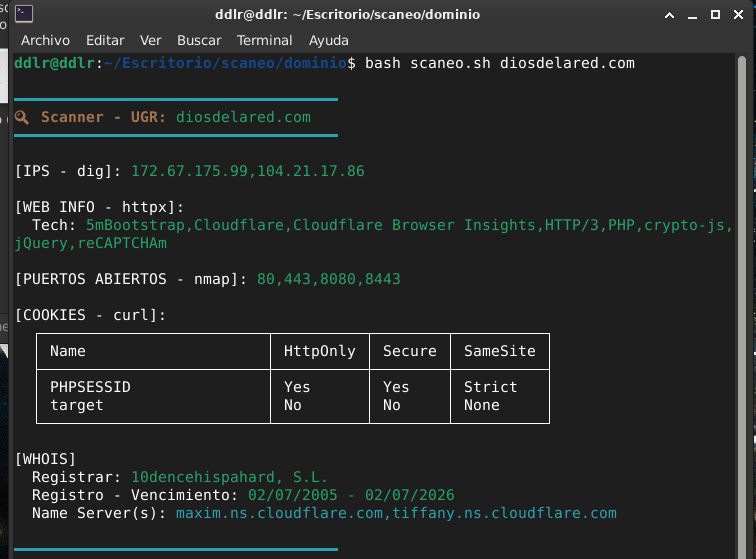
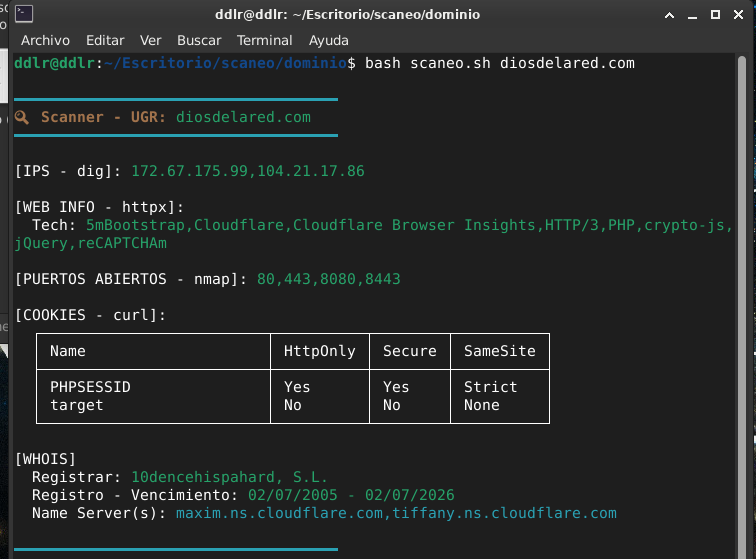
DScanner es una herramienta en bash que automatiza la fase de reconocimiento en auditorías de seguridad web, integrando múltiples utilidades (dig, nmap, httpx, curl, whois) en un único scan que identifica IPs, puertos abiertos, tecnologías, y cookies , con output formateado y exportable.
dScanner 🔍
Automated web reconnaissance tool for security audits
Description
dScanner consolidates multiple reconnaissance tools into a single command for the initial phase of web pentesting.
Only use with authorized systems!!!!
🚀 Installation
Required dependencies: curl dnsutils nmap whois httpx
Tool conceptualized and designed to automate web reconnaissance in security audits. Developed in bash with assistance from Claude AI for technical implementation and optimization.
Features:
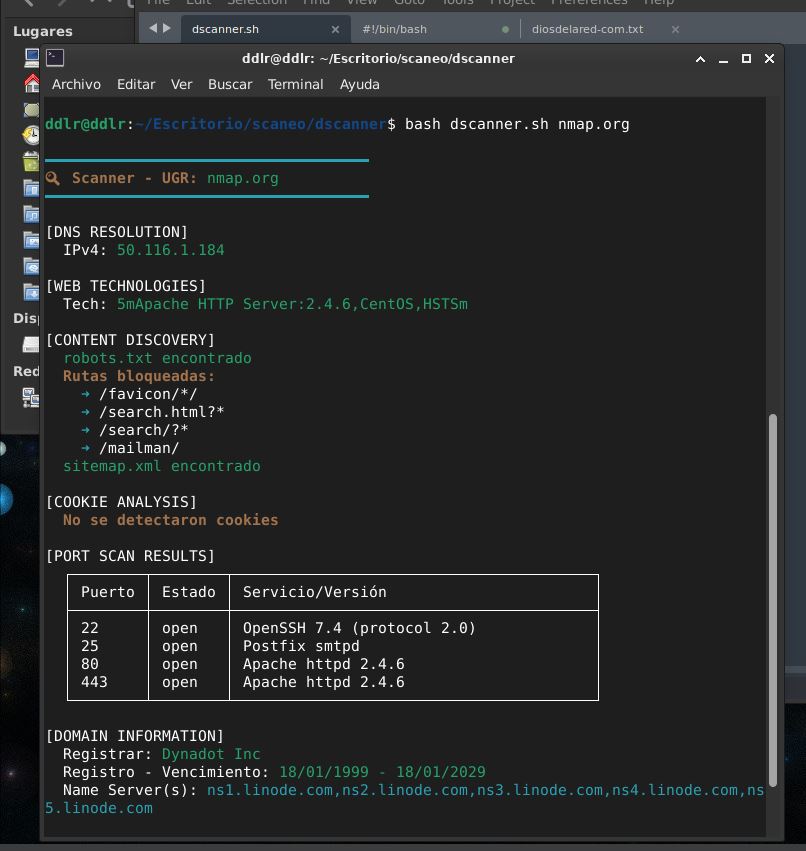
- ✅ DNS resolution with subdomain detection
- ✅ Common port scanning (nmap)
- ✅ Technology detection (httpx/curl)
- ✅ Cookie security analysis
- ✅ WHOIS information (root domains)
- ✅ robots.txt & sitemap.xml analysis
- ✅ Cookie analysis (
- ✅ TXT export with vulnerability analysis
- ✅ Simple analysis of DMARC, DKIM,.. configuration
- ✅ Zone-Transfer analysis
Architecture
| Module | Tool | Purpose |
|---|---|---|
| DNS | dig | Resolve domain to IPs |
| Web | httpx/curl | Detect technologies and server |
| Ports | nmap | Scan open ports |
| Cookies | curl | Analyze security attributes |
| Registration | whois | Registrar information |
Installation
Basic scan
sudo python3 dscanner.py example.com
Versions
06/18/2026 - v2.0
- Changed the code to Python
- SSL detection
- Simple Platform detection
- Improved interface and speed
- DMARC DKIM ETC. monitoring
- Zone Transfers
11/15/2025 - v1.5
- Added scraping of robots.txt, sitemap.xml
- Changed the nmap configuration to -sV so more information can be seen for each port
- Now resolves to IPv6
10/12/2025 - v1.0
- First version of dscanner
Example output:
Version v2:
version 1:
vibecoded with claude