
 #1
Tools for auditing, testing, and securing Wi-Fi, Bluetooth, and RFID systems.
Kitploit recommended
 tw-d/wifi-pineapple-mk7_rest-client
WiFi Hacking Workflow with WiFi Pineapple Mark VII API
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
 jjjjjjjj987/cve-2023-45866-py
Python-based proof-of-concept for CVE-2023-45866, a Bluetooth vulnerability, demonstrating exploitation techniques for security research and testing.
 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 uthrasri/cve-2023-28588_system_bt
system_bt_CVE-2023-28588
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
 halildeniz/macmaster
Advanced Network Interface Management and Monitoring
 pybluez/pybluez
Python extension module providing Bluetooth access: device inquiry, SDP service browsing, RFCOMM/L2CAP sockets, and experimental BLE scanning and…
 ets-polito/esp32-sniffer
ESP32 firmware that sniffs PROBE REQUEST packets sent by smartphones searching for Wi-Fi connection to extract different types of information
 ricardojoserf/wifi-pentesting-guide
WiFi Penetration Testing Guide
 oblique/create_ap
[NOT MAINTAINED] This script creates a NATed or Bridged WiFi Access Point.
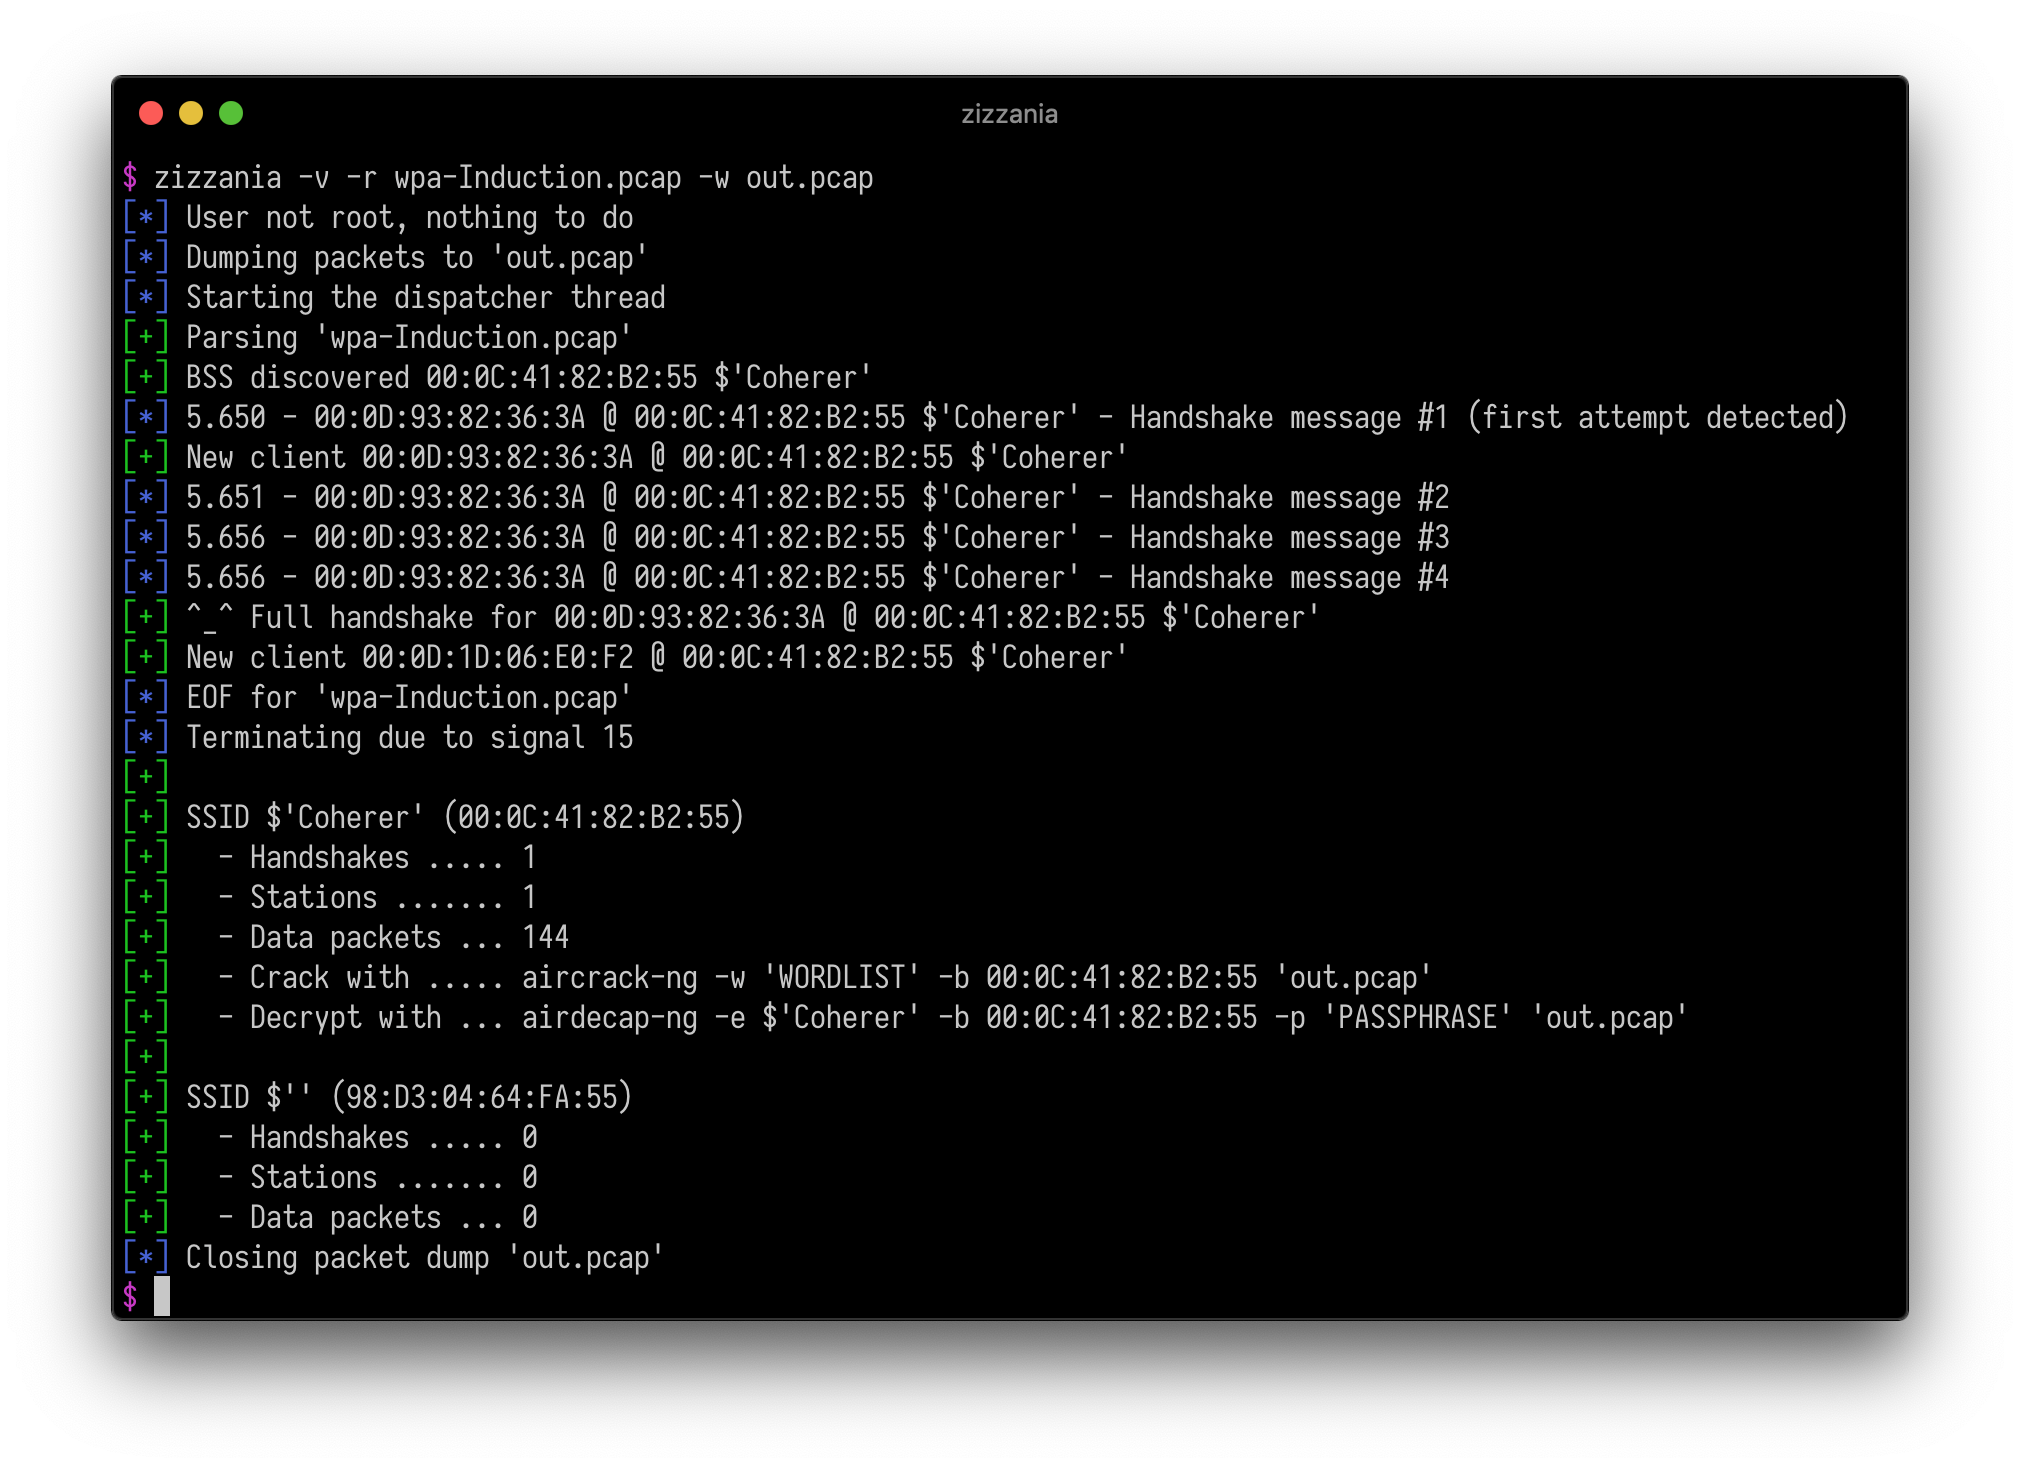 cyrus-and/zizzania
Automated DeAuth attack
 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 aprkr/cve-2023-48034
Weak encryption in Acer Wireless Keyboard SK-9662 allows attacker in physical proximity to both decrypt wireless keystrokes and inject wireless…
 xchwarze/ar150-wifipineapple
Converting your AR150 to a Wifi Pineapple NANO
 xchwarze/wifi-pineapple-cloner-builds
Build repo from Universal Wifi pineapple hardware cloner








