
 #1
Tools for auditing, testing, and securing Wi-Fi, Bluetooth, and RFID systems.
Kitploit recommended

 s0lst1c3/eaphammer
Targeted evil twin attacks against WPA2-Enterprise networks. Indirect wireless pivots using hostile portal attacks.

 amirasaiyad/ble-tpms
CVE-2024-39081. BLE TPMS data manipulation over bluetooth communication.
 avishekdhakal/cve-2023-45866_exploits
Exploits Tested in Mi A2 Lite and Realme 2 pro
 fj016/cve-2024-41992-poc
PoC for the CVE-2024-41992 (RCE on devices running WiFi-TestSuite-DUT)
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 uthrasri/system_bt_cve-2024-0030
 ynwarcs/cve-2023-23388
poc for CVE-2023-23388 (LPE in Windows 10/11 bthserv service)
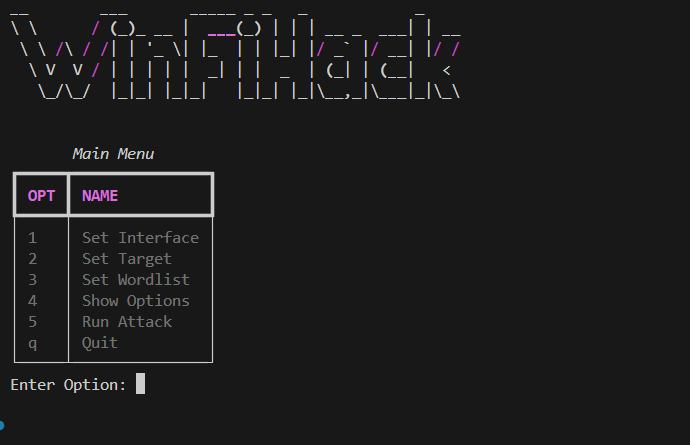 morpheuslord/winfihack
A windows Wifi Brute forcing utility which is an extremely old method but still works without the requirement of external dependencies.
 phuchaudeveloper/badblue
CVE-2024-21306 BadBlue implementation (Using DuckyScript)
 sgxgsx/blueborne-cve-2017-1000251
Linux Kernel < 4.13.1 - BlueTooth Buffer Overflow (PoC) BlueBorne - Proof of Concept - Unarmed/Unweaponized - DoS (Crash) only
 cisnarfu/bluepop
Bluetooth Classic HID injection exploit for CVE-2023-45866, enabling unauthenticated keystroke injection against vulnerable BlueZ-based Linux systems.
 uthrasri/frameworks_opt_net_wifi_cve-2021-0466
 uthrasri/frameworks_opt_net_wifi_cve-2021-0390
Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.
 uthrasri/system_connectivity_wificond_cve-2021-0392
Exploit for CVE-2021-0392 targeting Android's wificond system service for privilege escalation via a connectivity vulnerability.
 chapoly1305/cve-2023-46870
Detailed analysis and proof-of-concept for CVE-2023-46870, a local privilege escalation in Nordic Semiconductor nRF Sniffer for Bluetooth LE due to…
 d3adp3nguin/cve-2023-33105-transient-dos-in-wlan-host-and-firmware
This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…








