
 #1
Automated tools for detecting common web application flaws (e.g., XSS, SQLi).
Kitploit recommended
 0xinfection/logmepwn
A fully automated, reliable, super-fast, scanning and validation toolkit for the Log4J RCE CVE-2021-44228 vulnerability.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
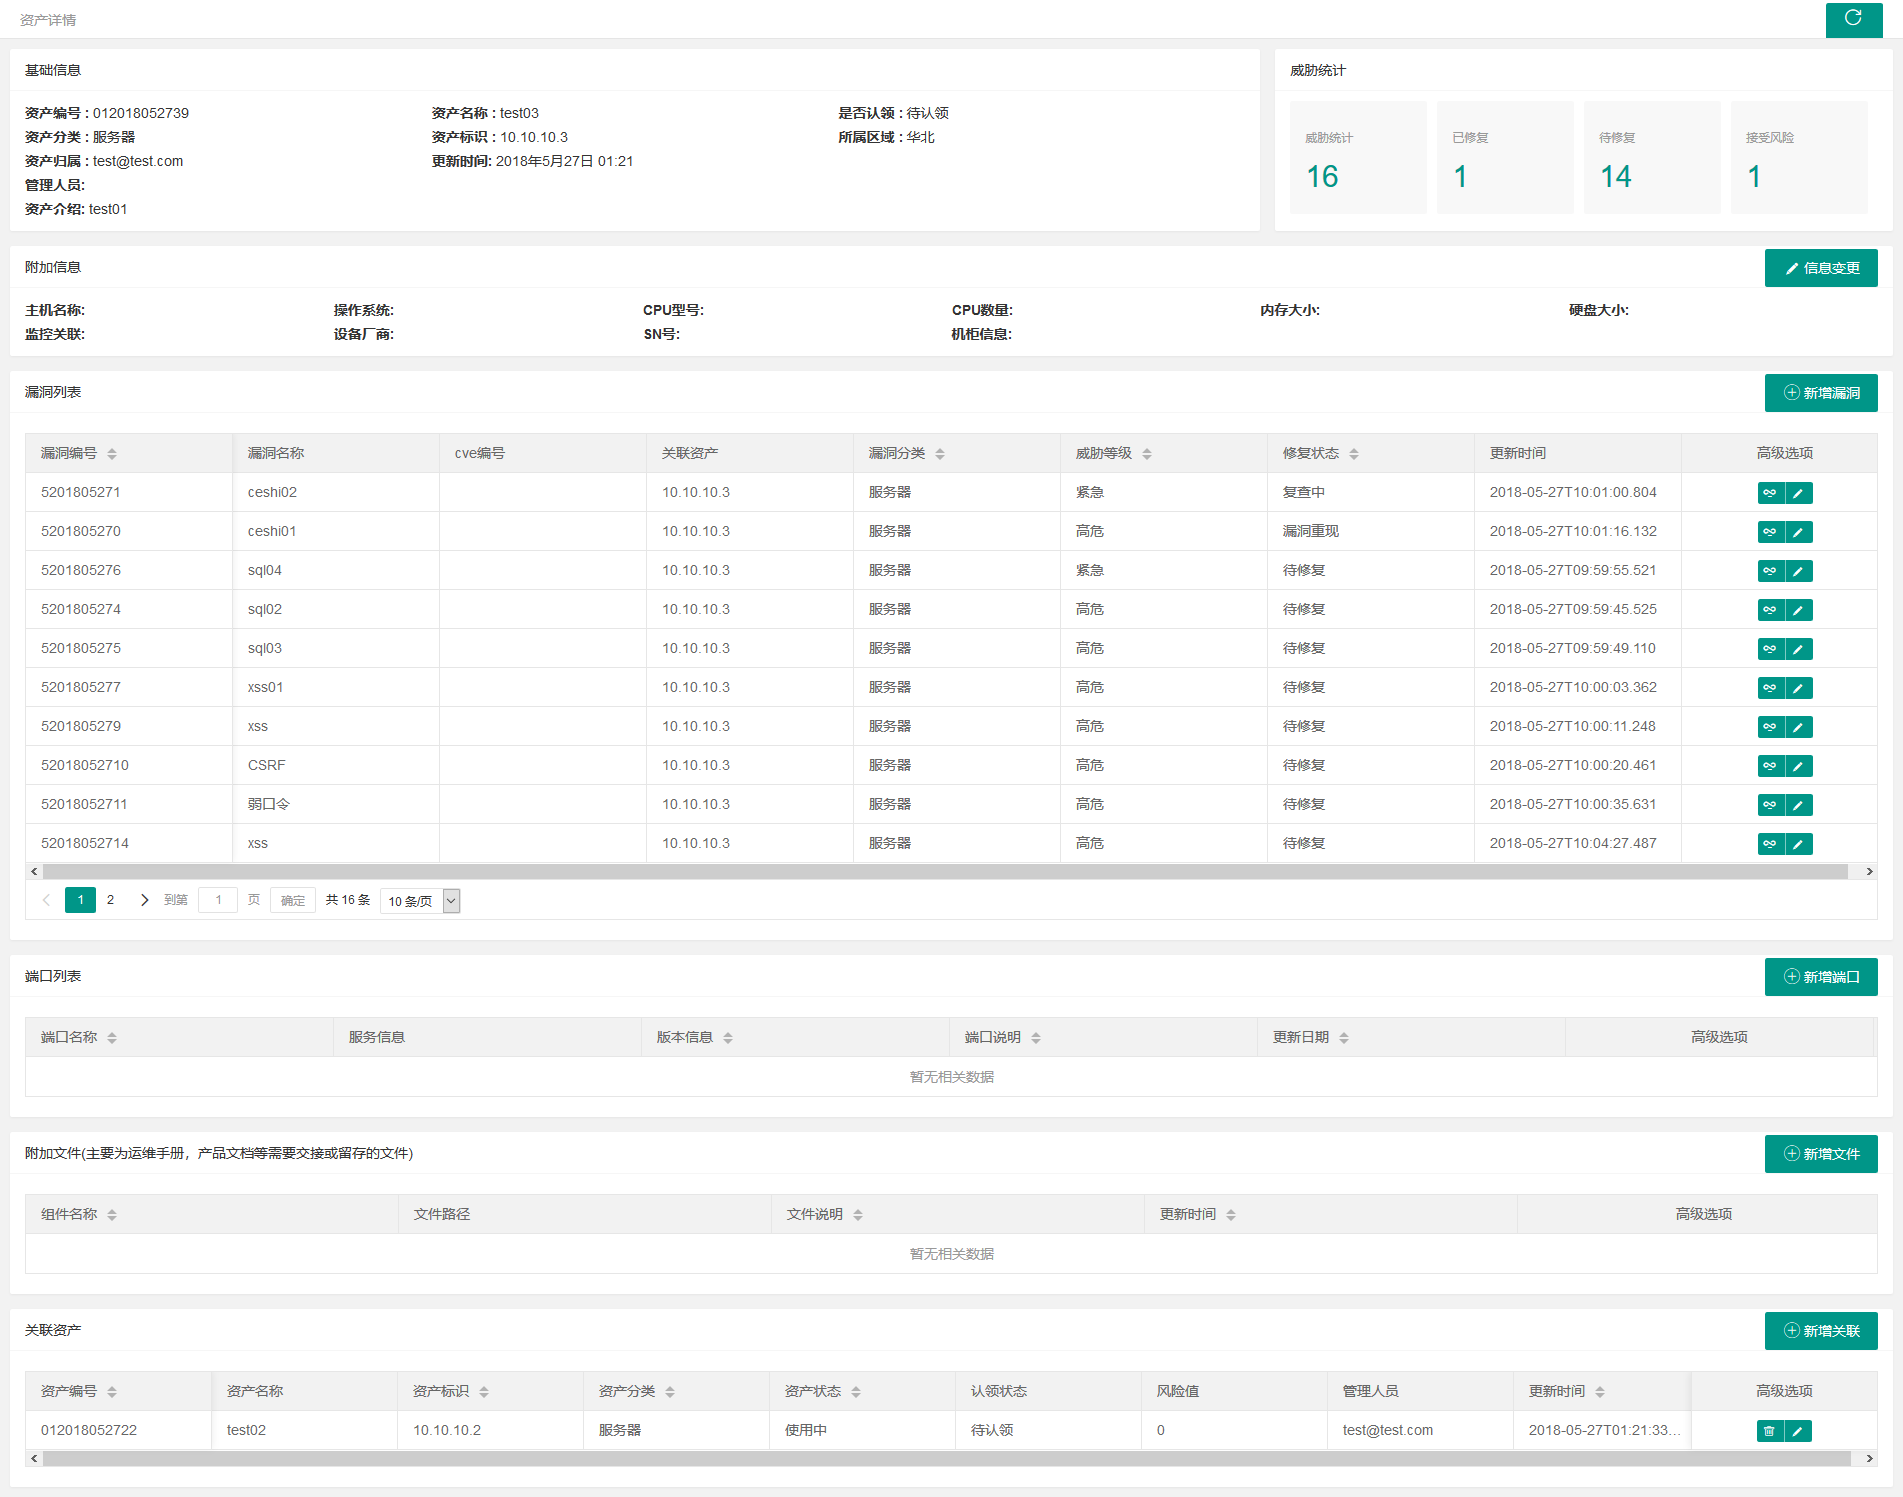 we1h0/securitymanageframwork
Security Manage Framwork is a security management platform for enterprise intranet, which includes asset management, vulnerability management,…
 dzonerzy/gowapt
Go Web Application Penetration Test
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 xnl-h4ck3r/xnlreveal
A Chrome/Firefox browser extension to show alerts for reflected query params, show Wayback archive links for the current path, show hidden elements…
 hood3drob1n/bingoo
BinGoo! A Linux bash based Bing and Google Dorking Tool
 gbrindisi/xsssniper
An automatic XSS discovery tool
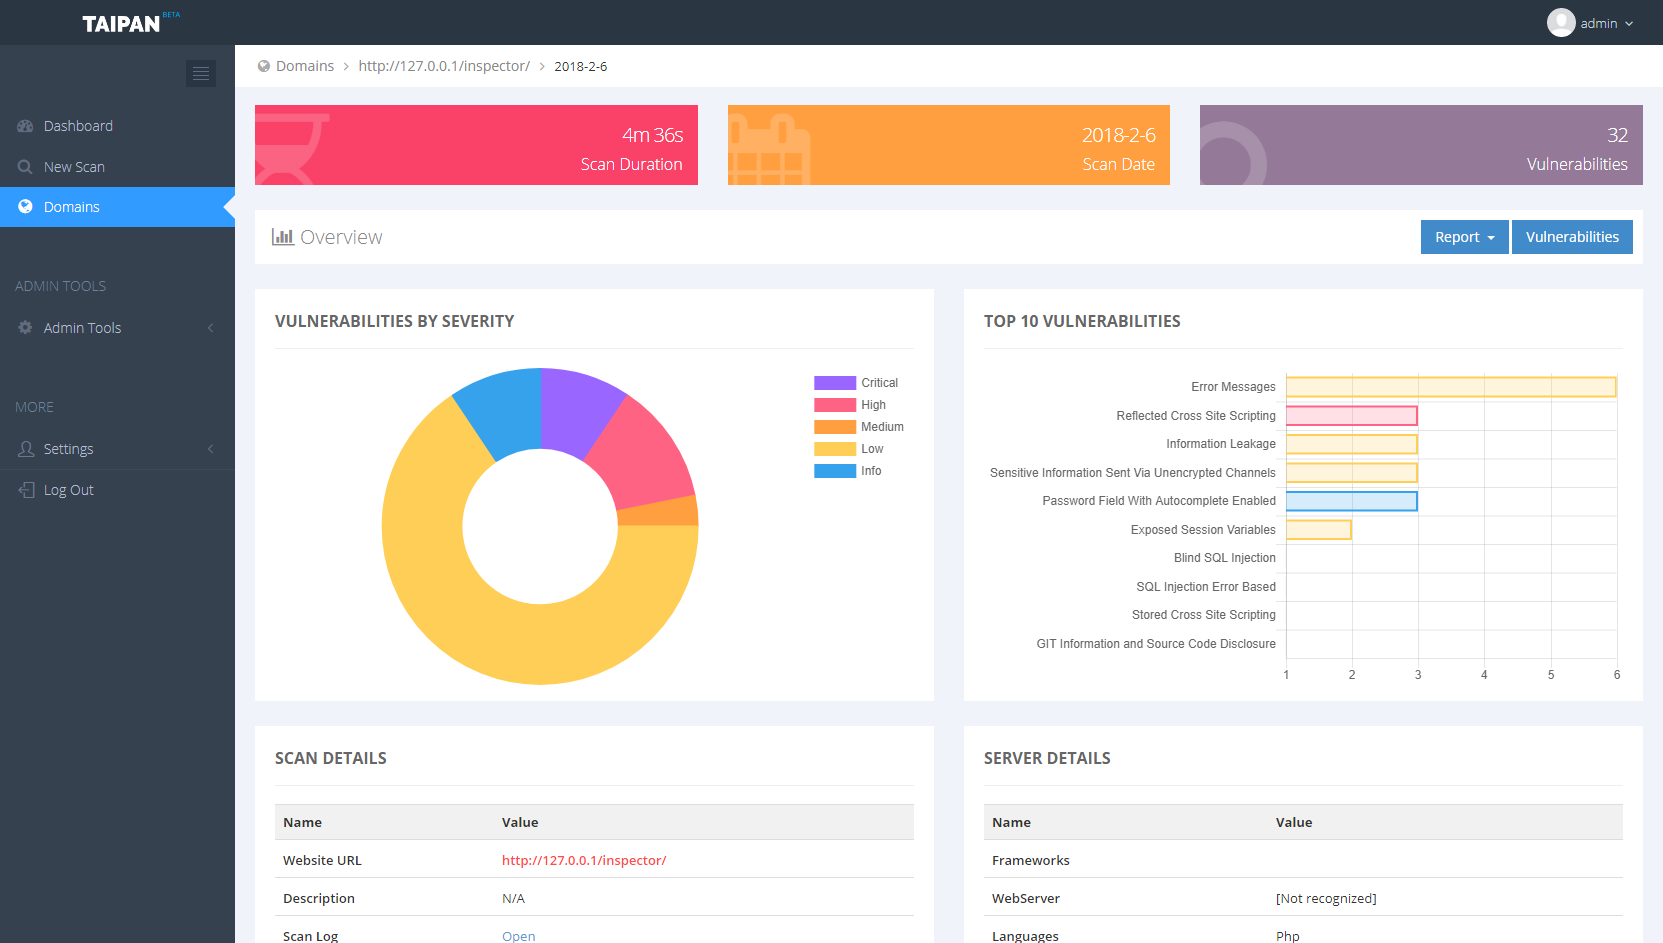 enkomio/taipan
Web application vulnerability scanner
 noptrix/lulzbuster
A multithreaded, very fast and smart HTTP(S) directory and file bruteforcer written in C on top of libcurl
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
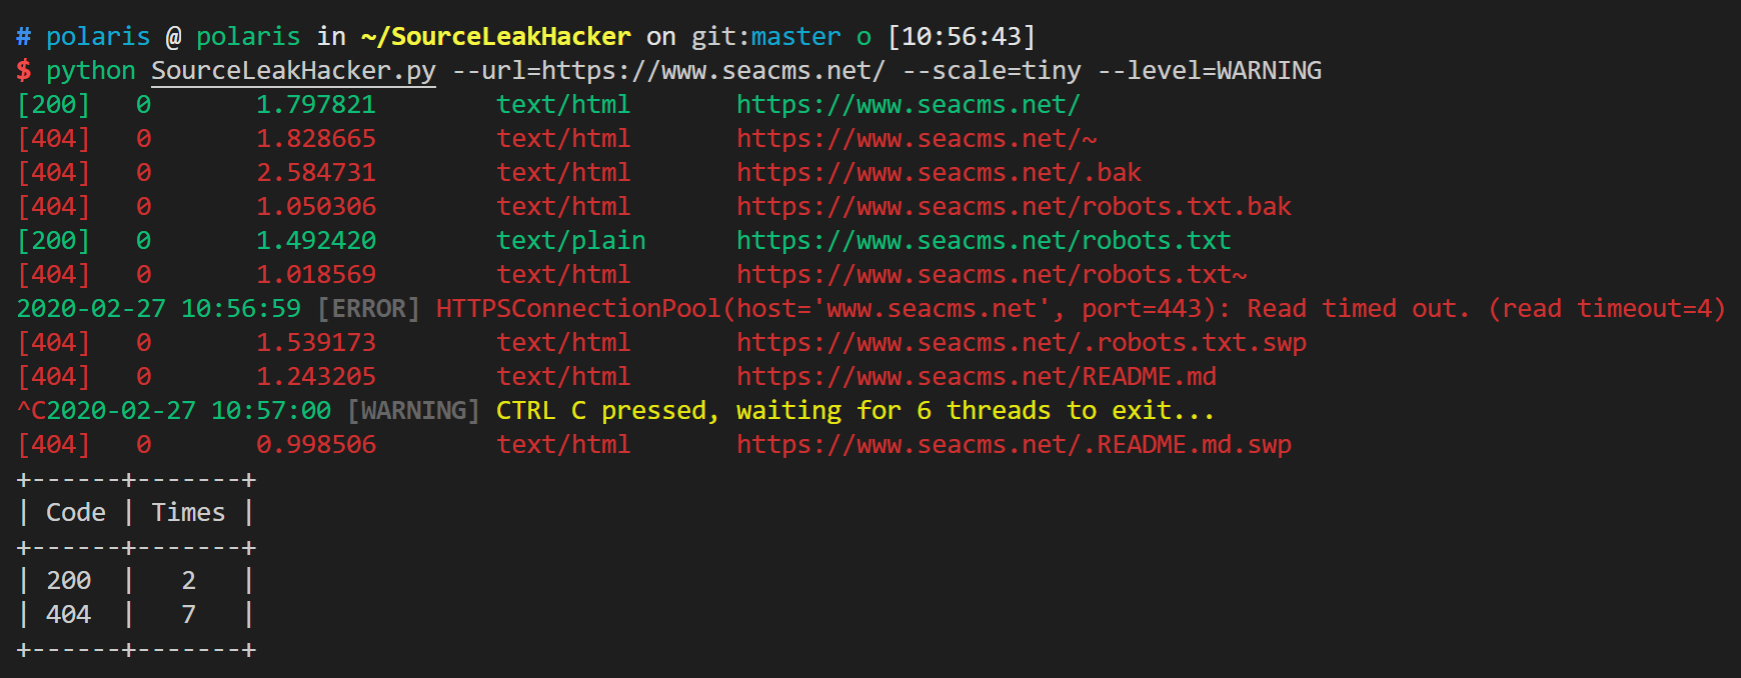 wangyihang/sourceleakhacker
:bug: A multi threads web application source leak scanner
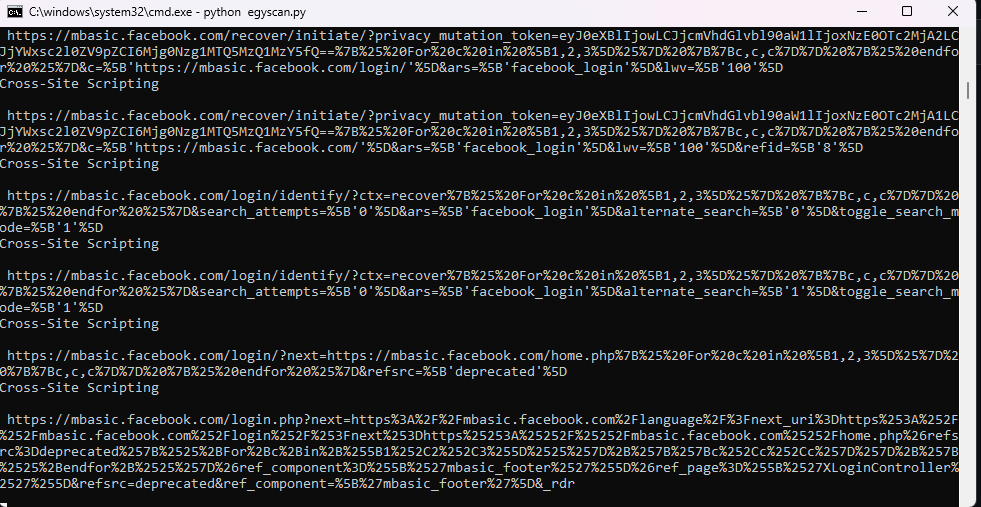 dragonked2/egyscan
Egyscan The Best web vulnerability scanner; it's a multifaceted security powerhouse designed to fortify your web applications against malicious…
 rxerium/rxerium-templates
Nuclei scripts created by @rxerium for zero days / actively exploited vulnerabilities.
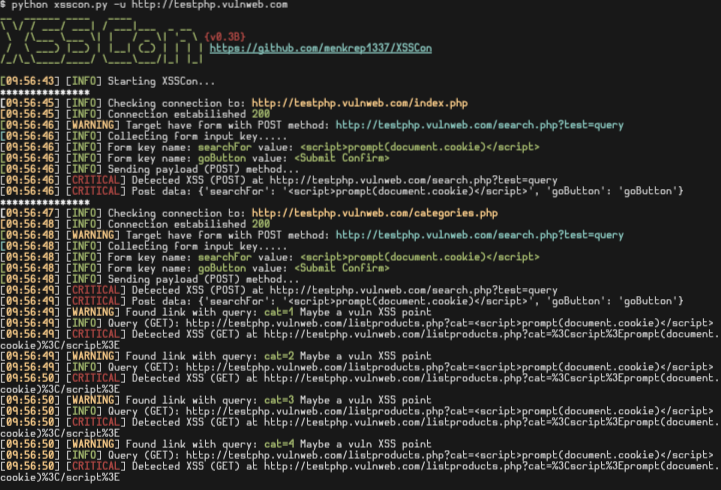 menkrep1337/xsscon
XSSCon: Simple XSS Scanner tool
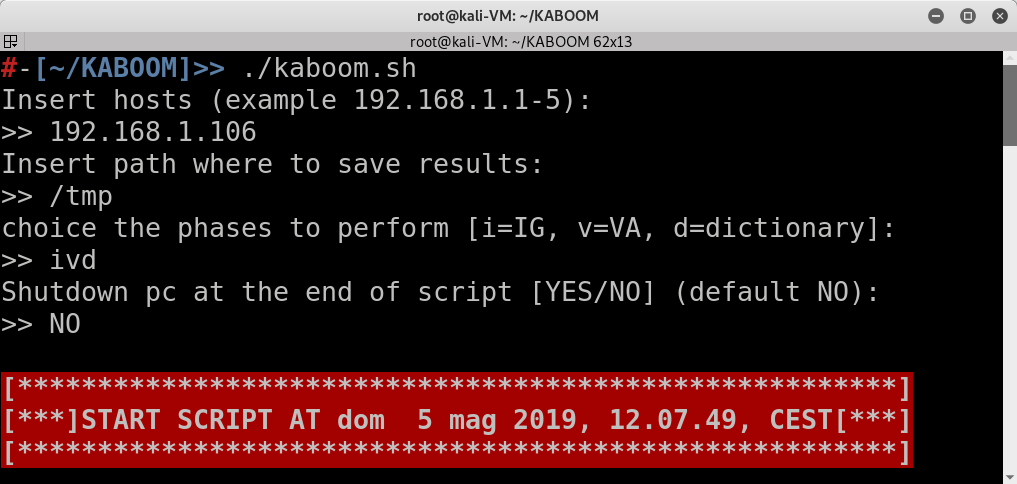 leviathan36/kaboom
A tool to automate penetration tests
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…








