
 #1
Automated tools for detecting common web application flaws (e.g., XSS, SQLi).
Kitploit recommended
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 urbanadventurer/whatweb
Next generation web scanner
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 sabri-zaki/easy_hack
Hack the World using Termux
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
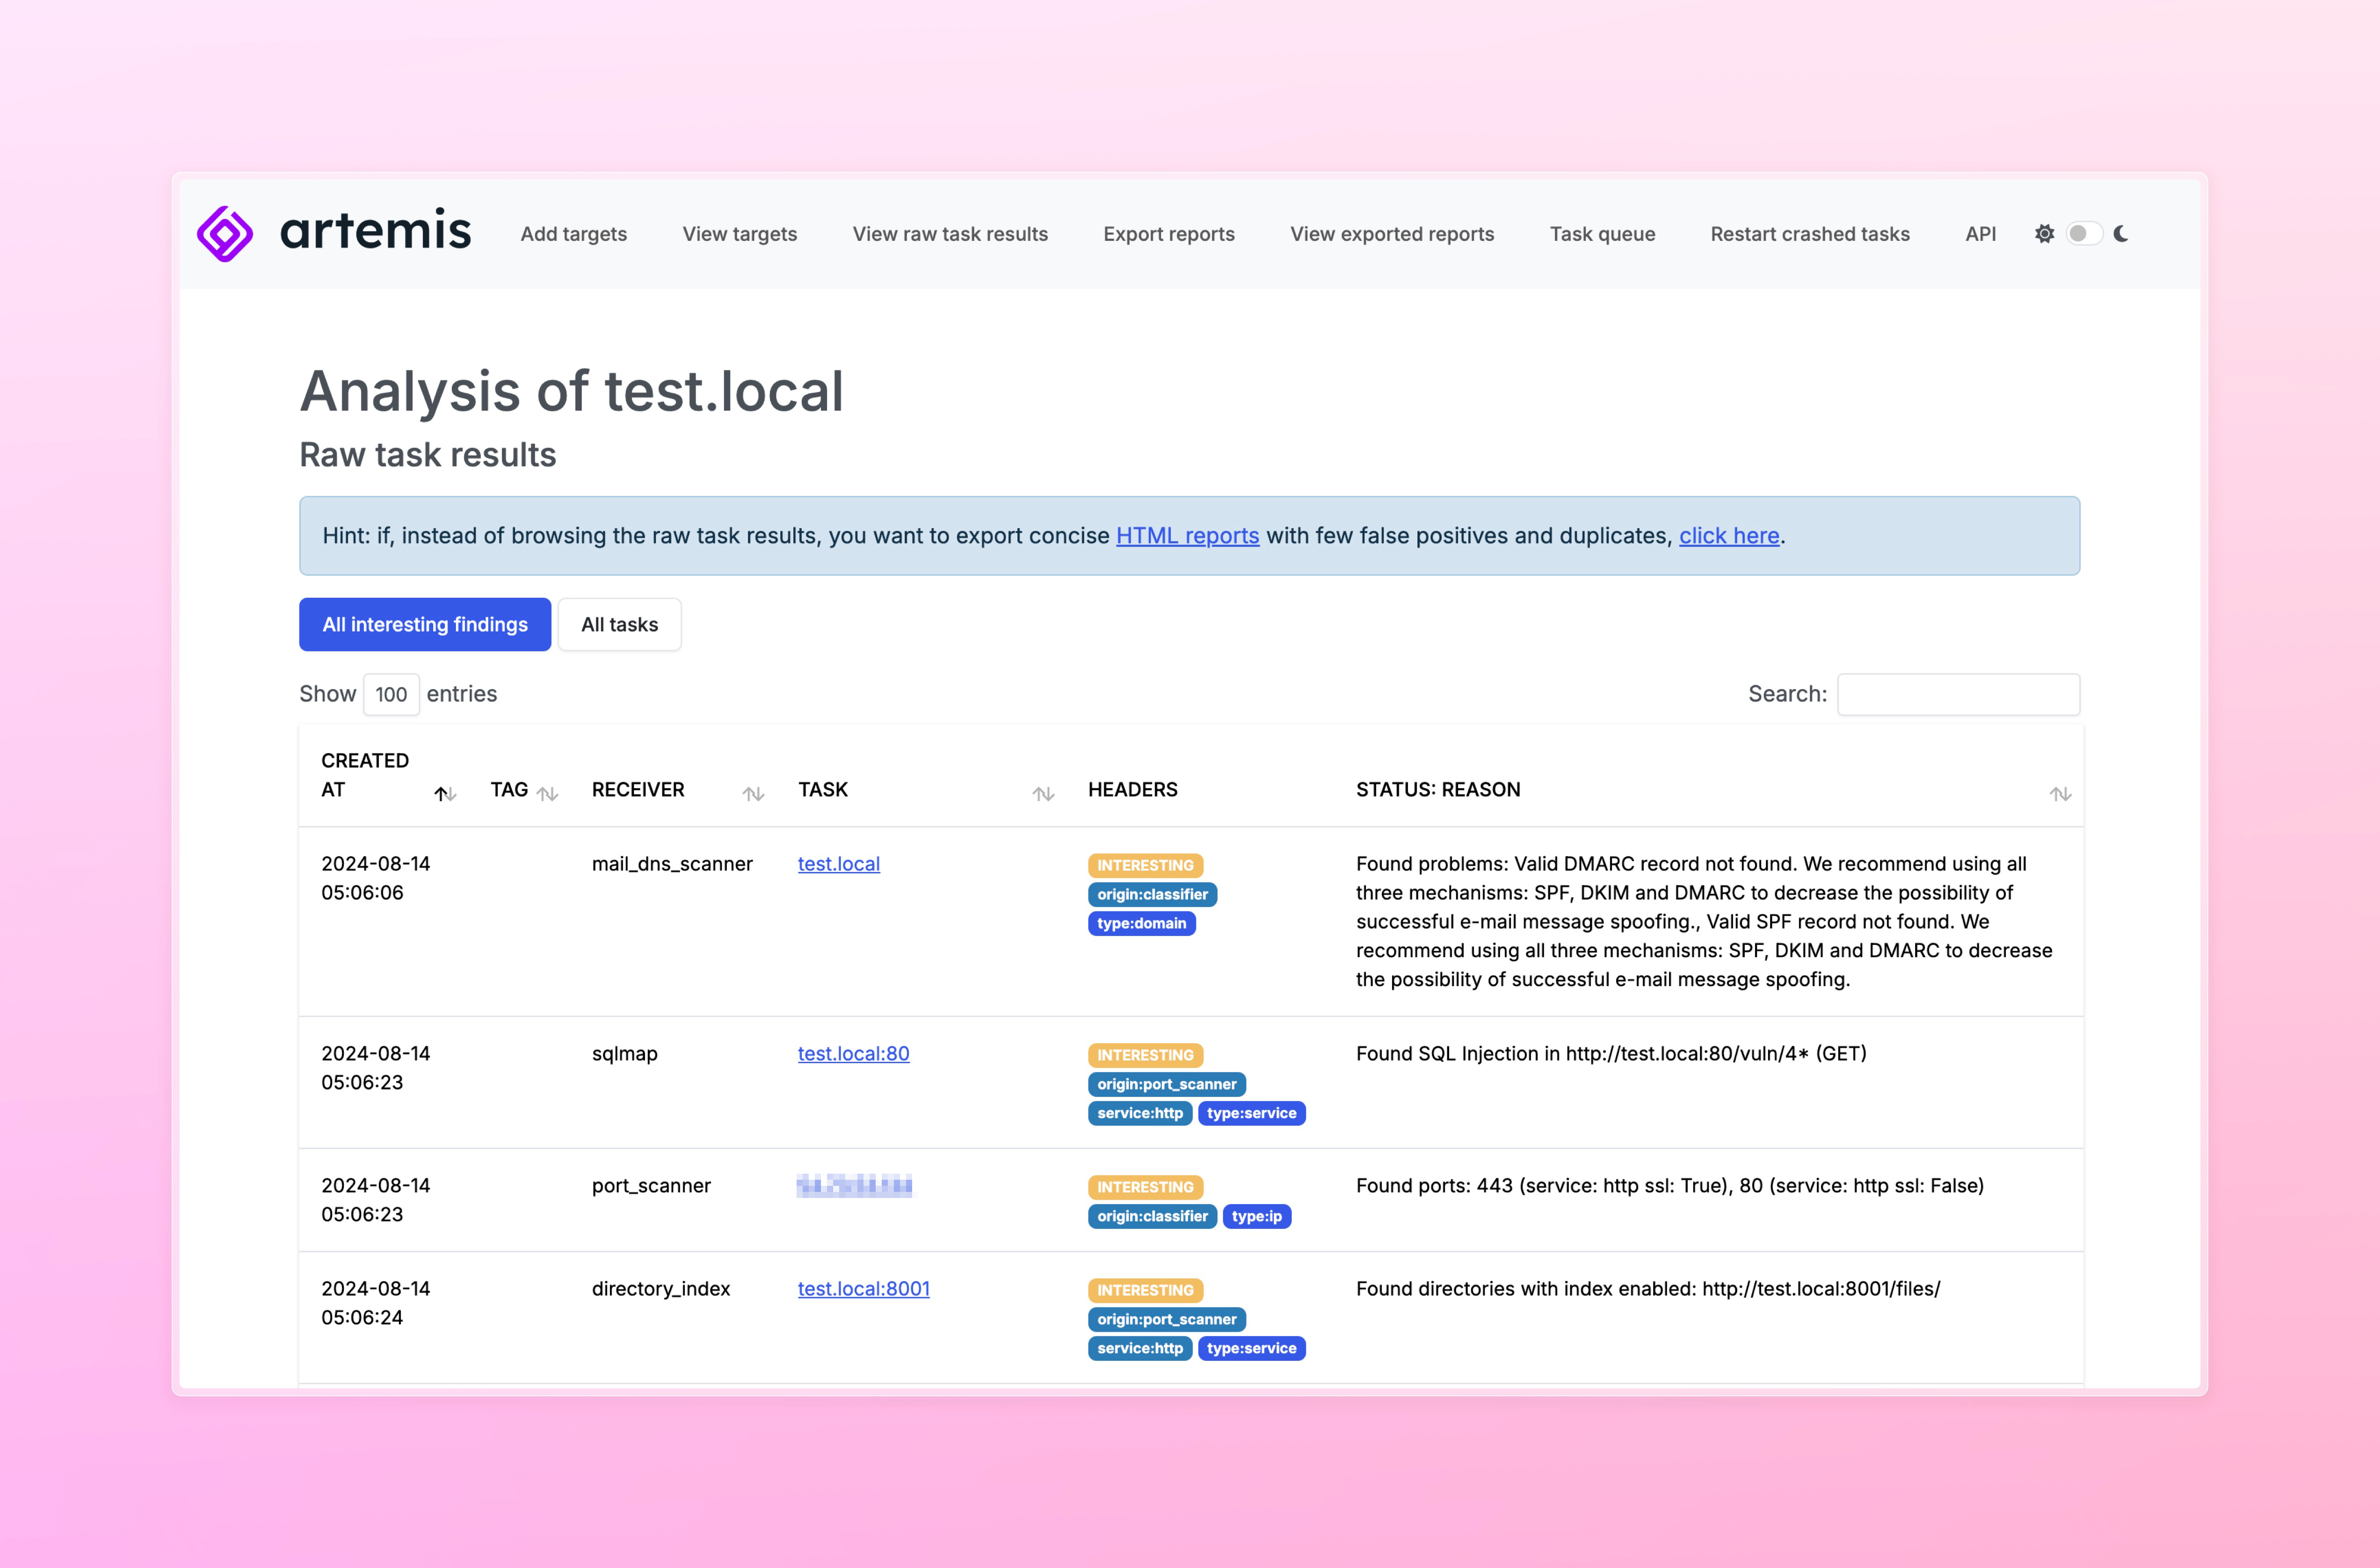 cert-polska/artemis
A modular vulnerability scanner with automatic report generation capabilities.
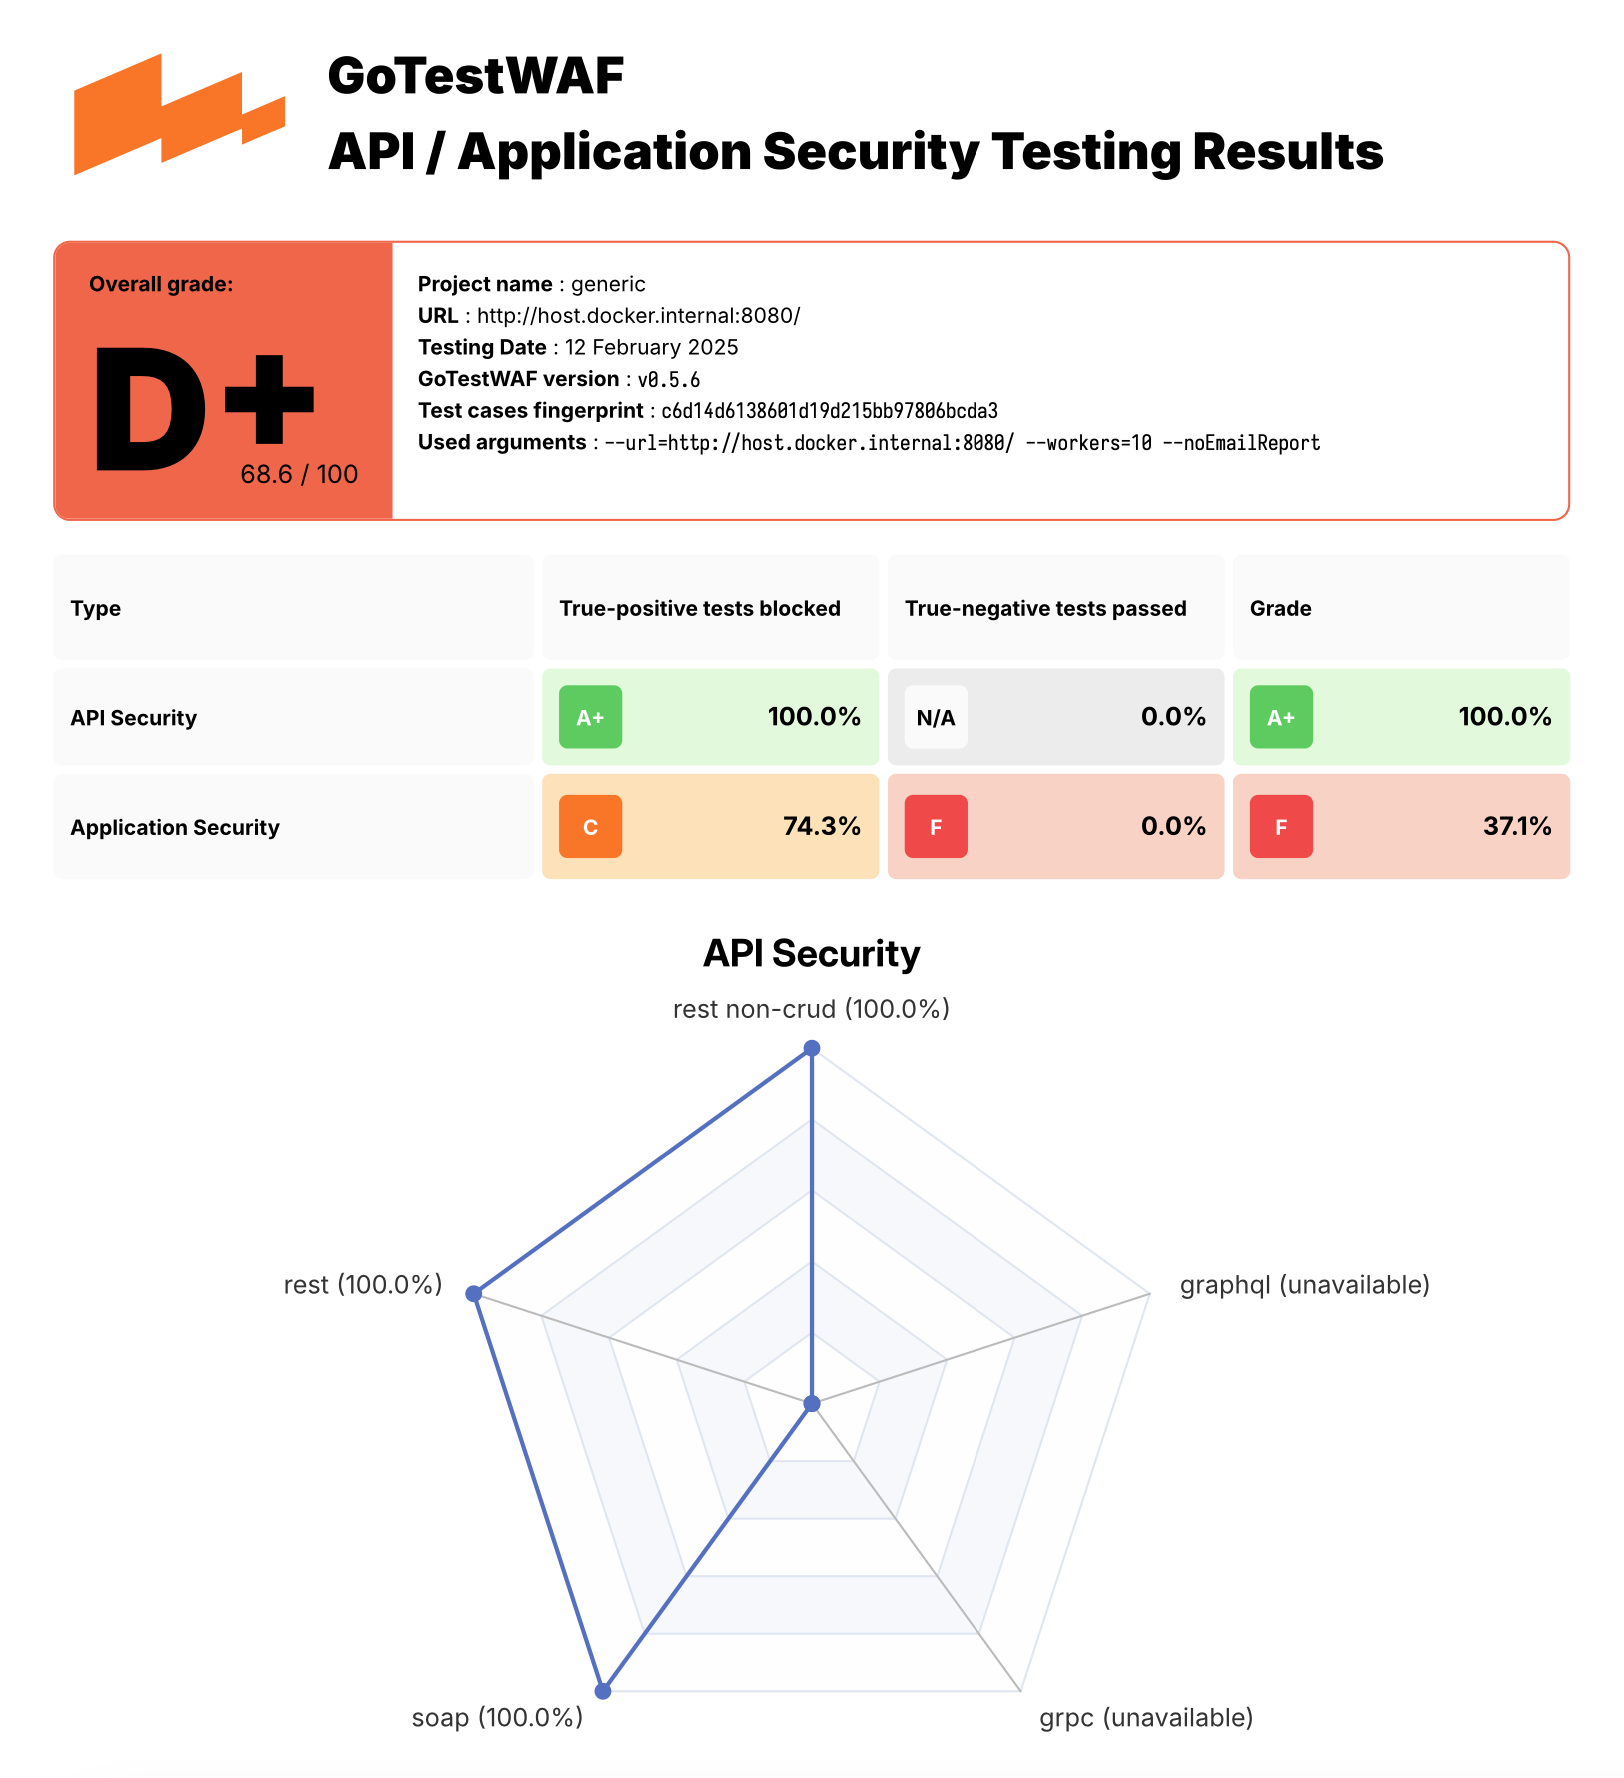 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses







