
 #1
Tools for intercepting, analyzing, and modifying web traffic for security testing.
Kitploit recommended
 mthbernardes/houseproxy
Protect your parents from phishing
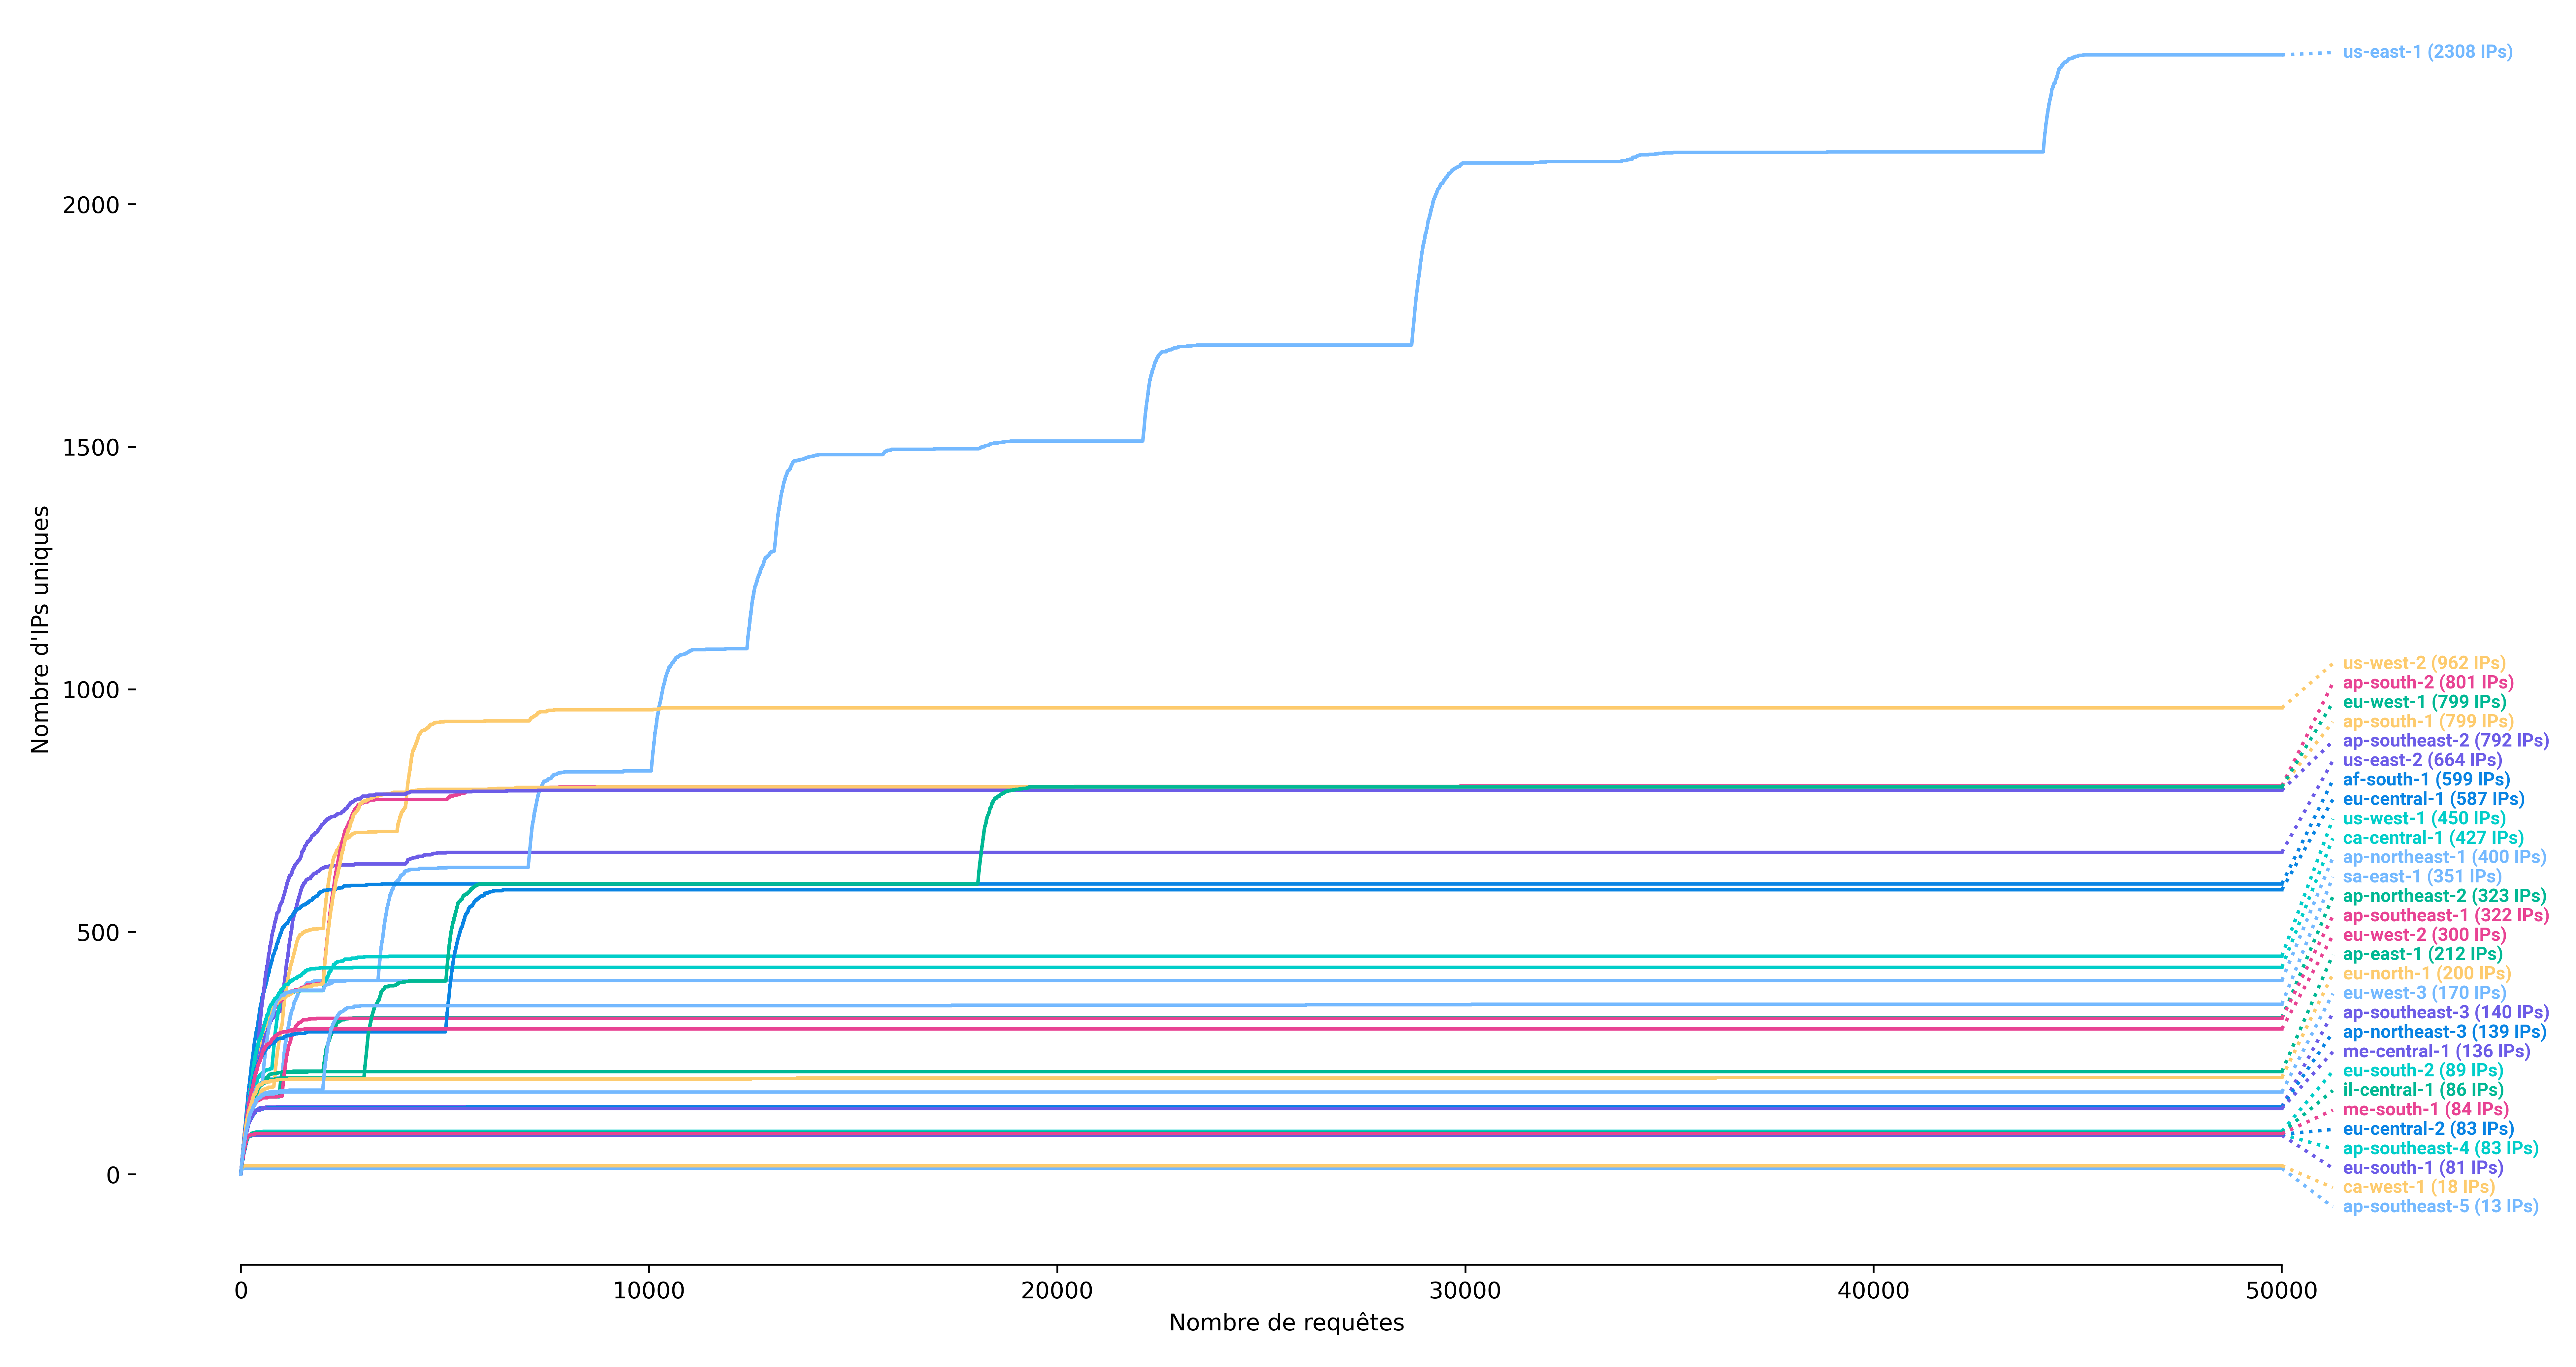 synacktiv/ipspinner
IPSpinner works as a local proxy that redirects requests through external services.
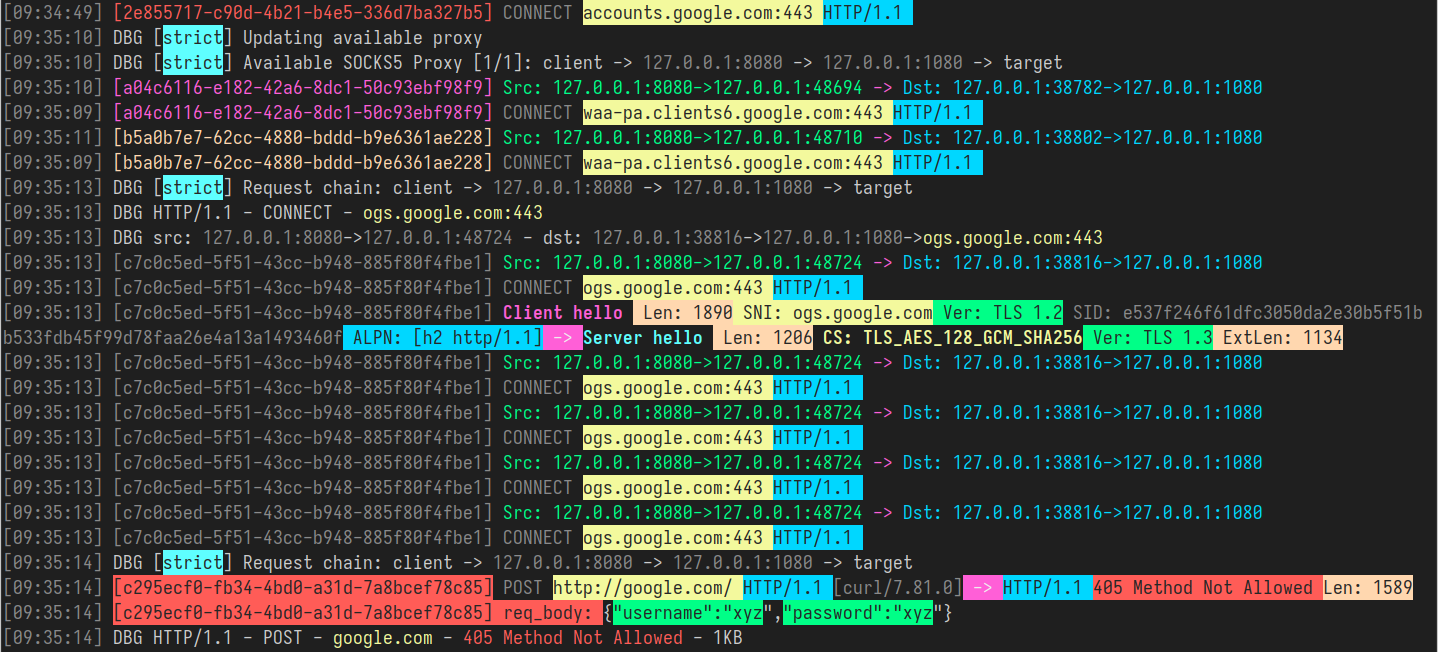 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 joanbono/gurp
Burp Commander written in Go
 johndoe31415/ratched
Ratched is a transparent Man-in-the-Middle TLS proxy intended for penetration testing
 ytkoka/impersonate-proxy
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…
 ipopov/starttls-mitm
A starttls-capable transparent man-in-the-middle proxy
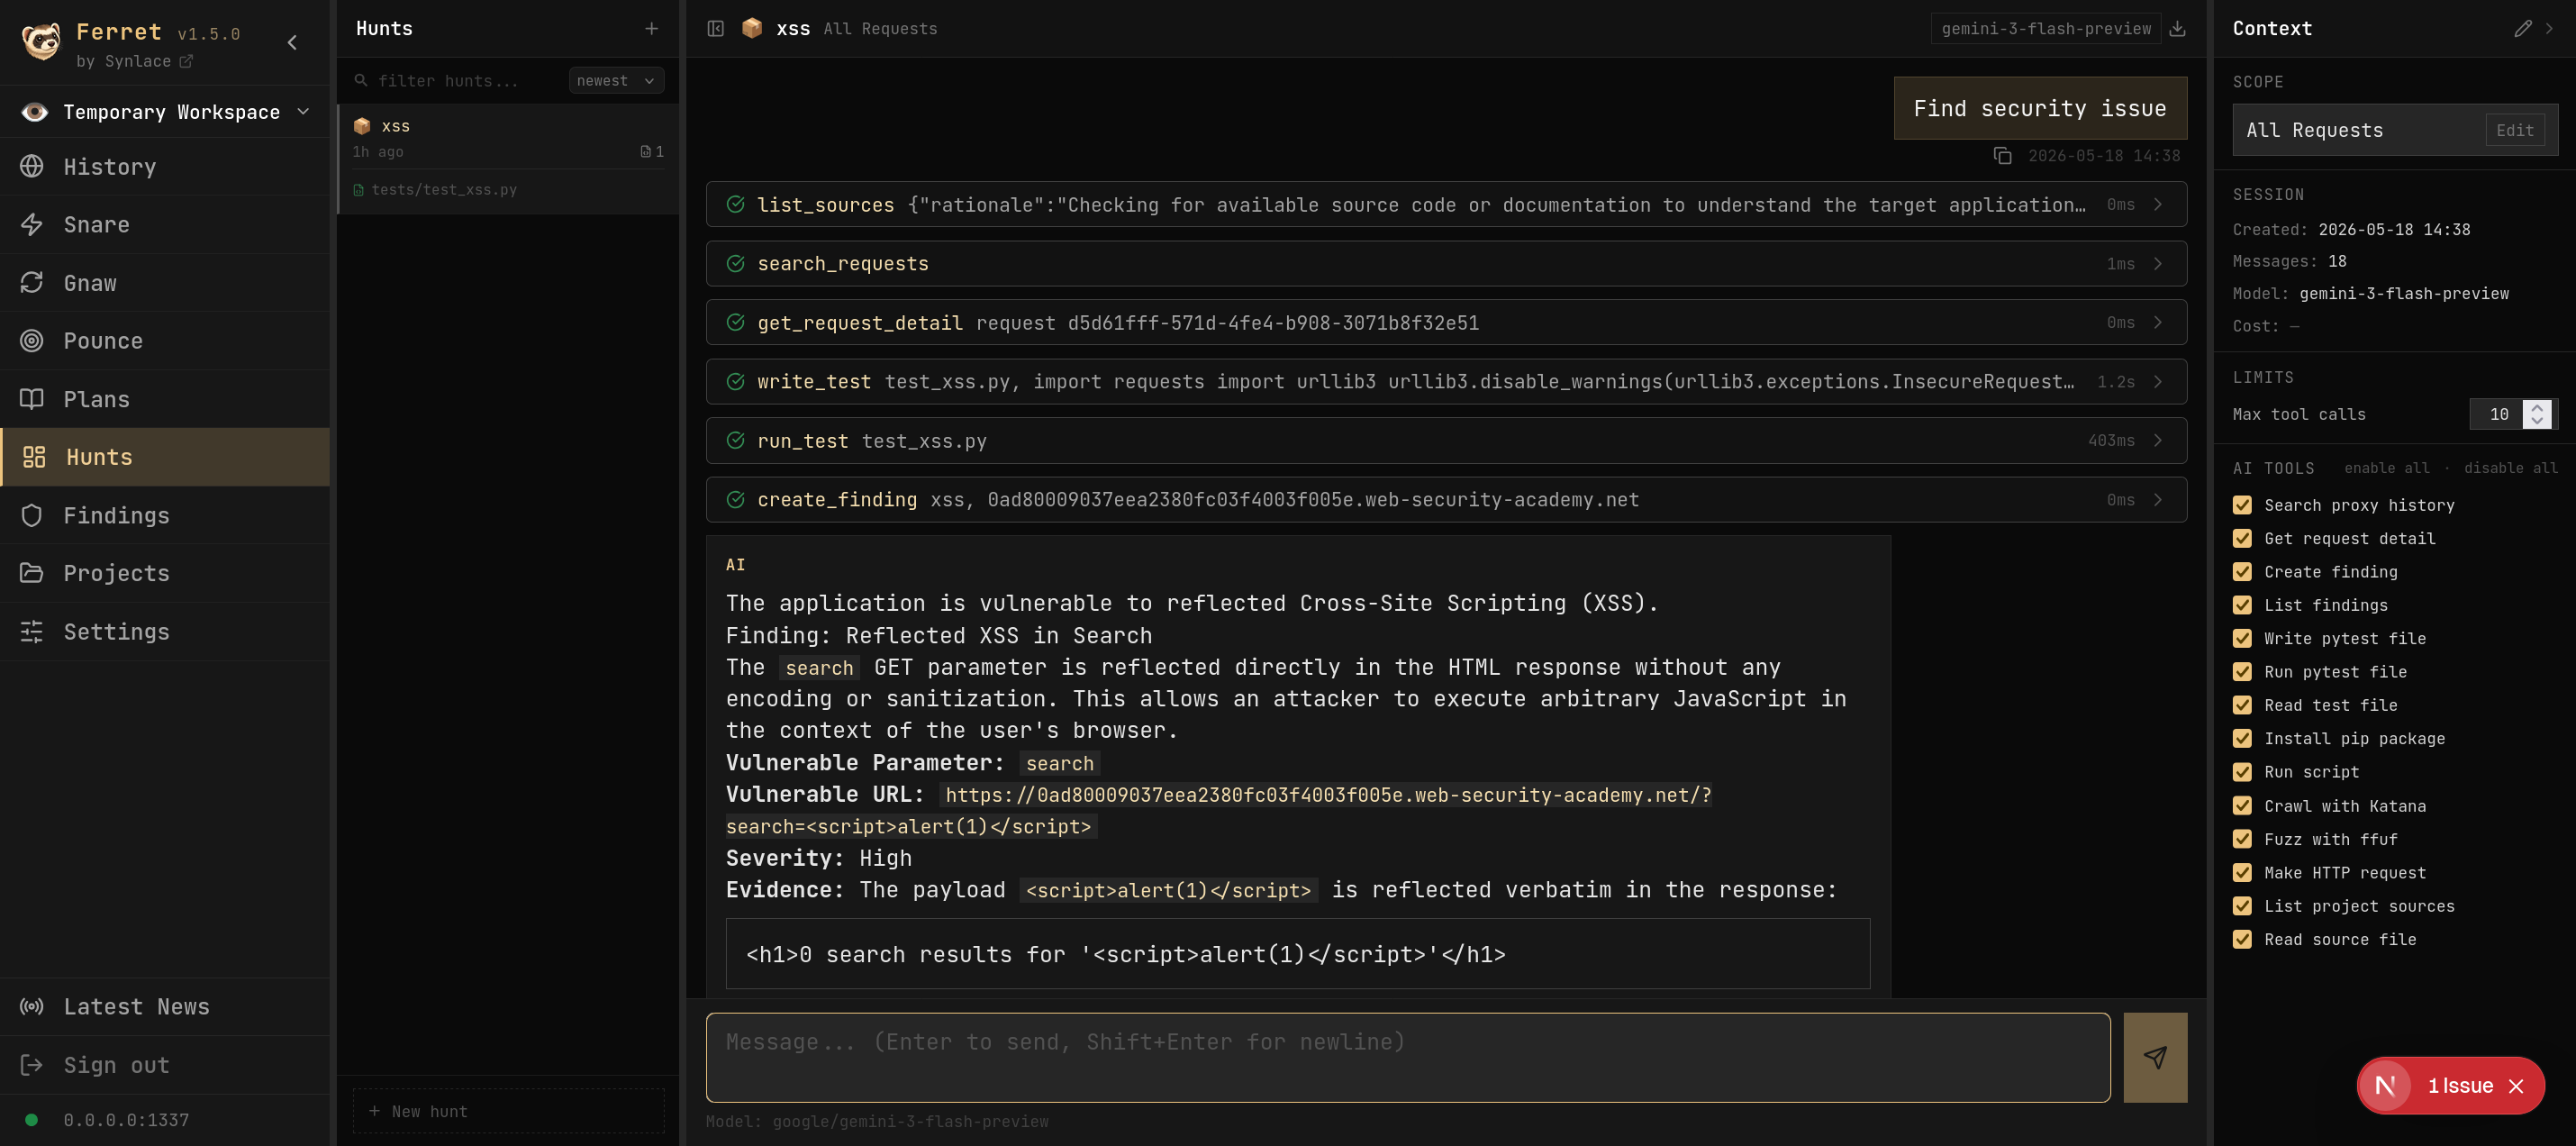 synlace/ferret
The collaborative web app pentest suite
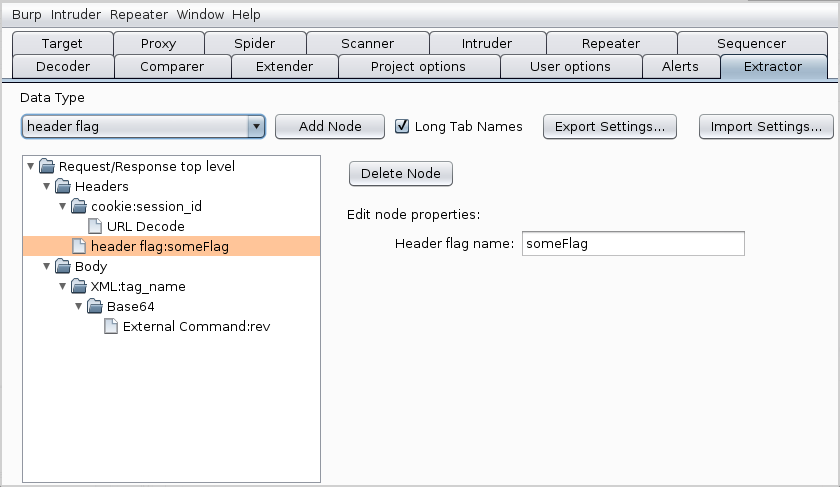 nccgroup/extractor
Extension adds a new tab in Burp Suite called Extractor
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
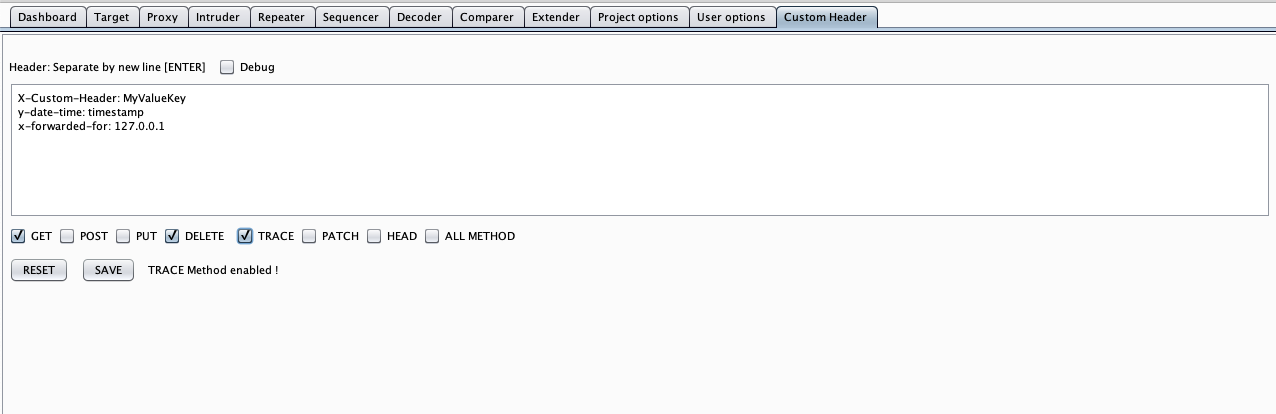 mirfansulaiman/customheader
This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
 icecubesandwich/caddysmith
Generate Caddy redirector configs from Cobalt Strike or Sliver C2 profiles.
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 mike01/pypacker
:package: The fastest and simplest packet manipulation lib for Python
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
 mrschyte/socksmon
Monitor arbitrary TCP traffic using your HTTP interception proxy of choice








