#1
Tools for intercepting, analyzing, and modifying web traffic for security testing.
Kitploit recommended
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
wkeeling/selenium-wireExtends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua
 justmao945/mallory
HTTP/HTTPS proxy over SSH
 nyamisty/ssl-kill-switch3
Next Generation SSLKillSwitch with much more support!
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 zu1k/good-mitm
Rule-based MITM engine. Rewriting, redirecting and rejecting on HTTP(S) requests and responses, supports JavaScript rule.
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
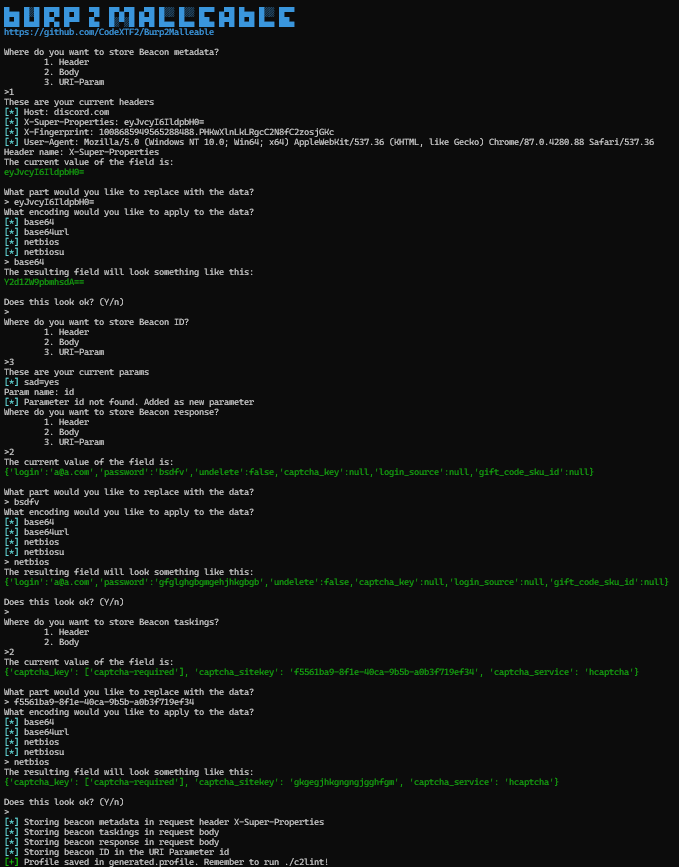 codextf2/burp2malleable
Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
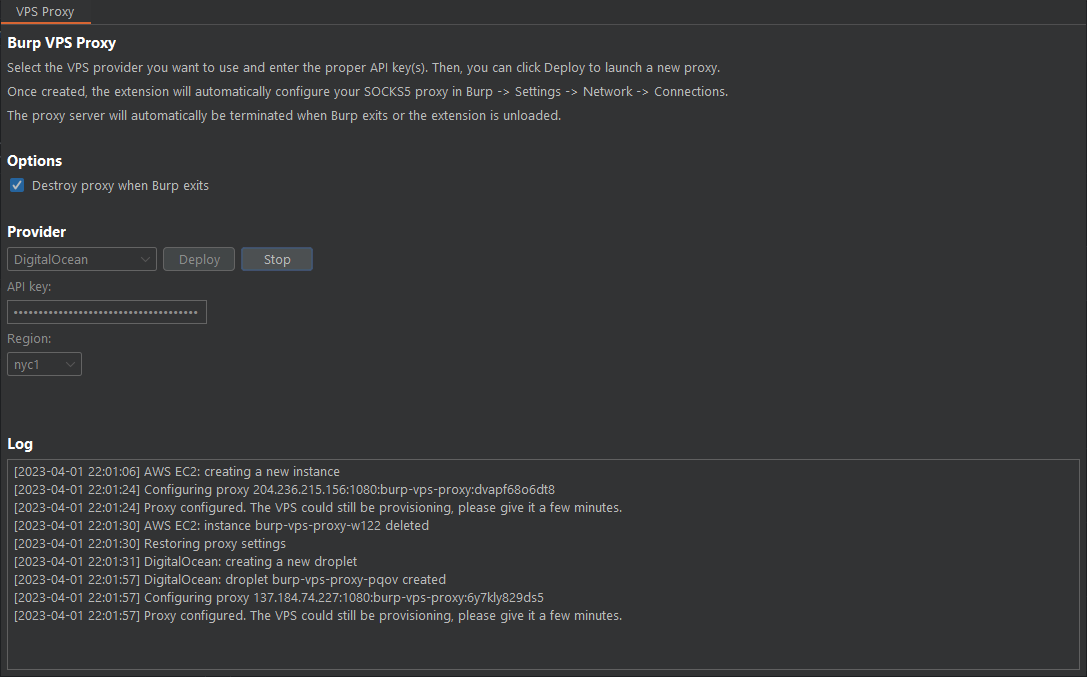 d3mondev/burp-vps-proxy
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
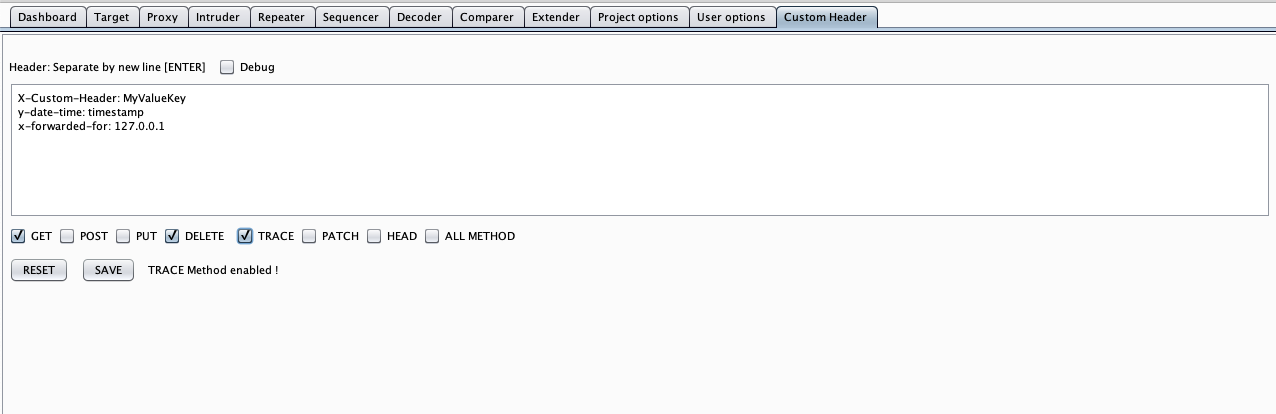 mirfansulaiman/customheader
This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…
 nccgroup/autochrome
This tool downloads, installs, and configures a shiny new copy of Chromium.
 barre/privaxy
Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…
 threatexpress/cs2modrewrite
Convert Cobalt Strike profiles to modrewrite scripts
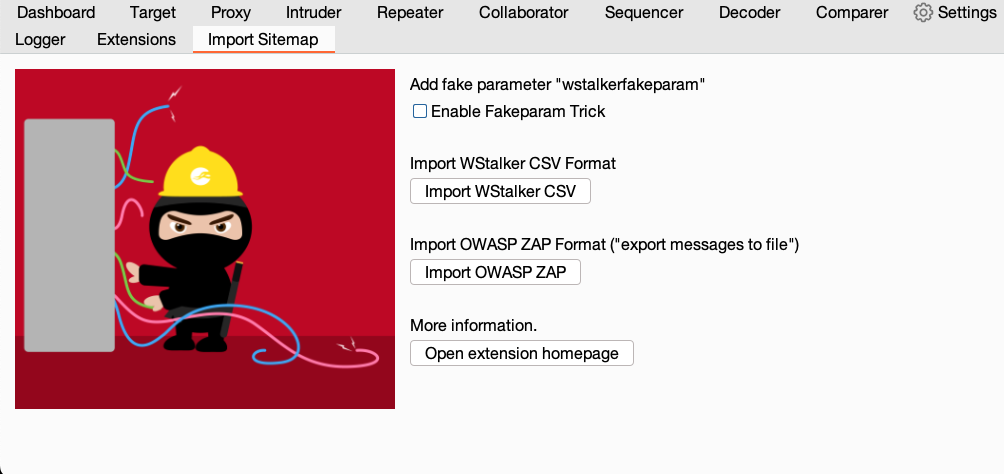 nccgroup/burpimportsitemap
Import To Sitemap is a Burp Suite Extension to import wstalker CSV file or ZAP export file into Burp Sitemap
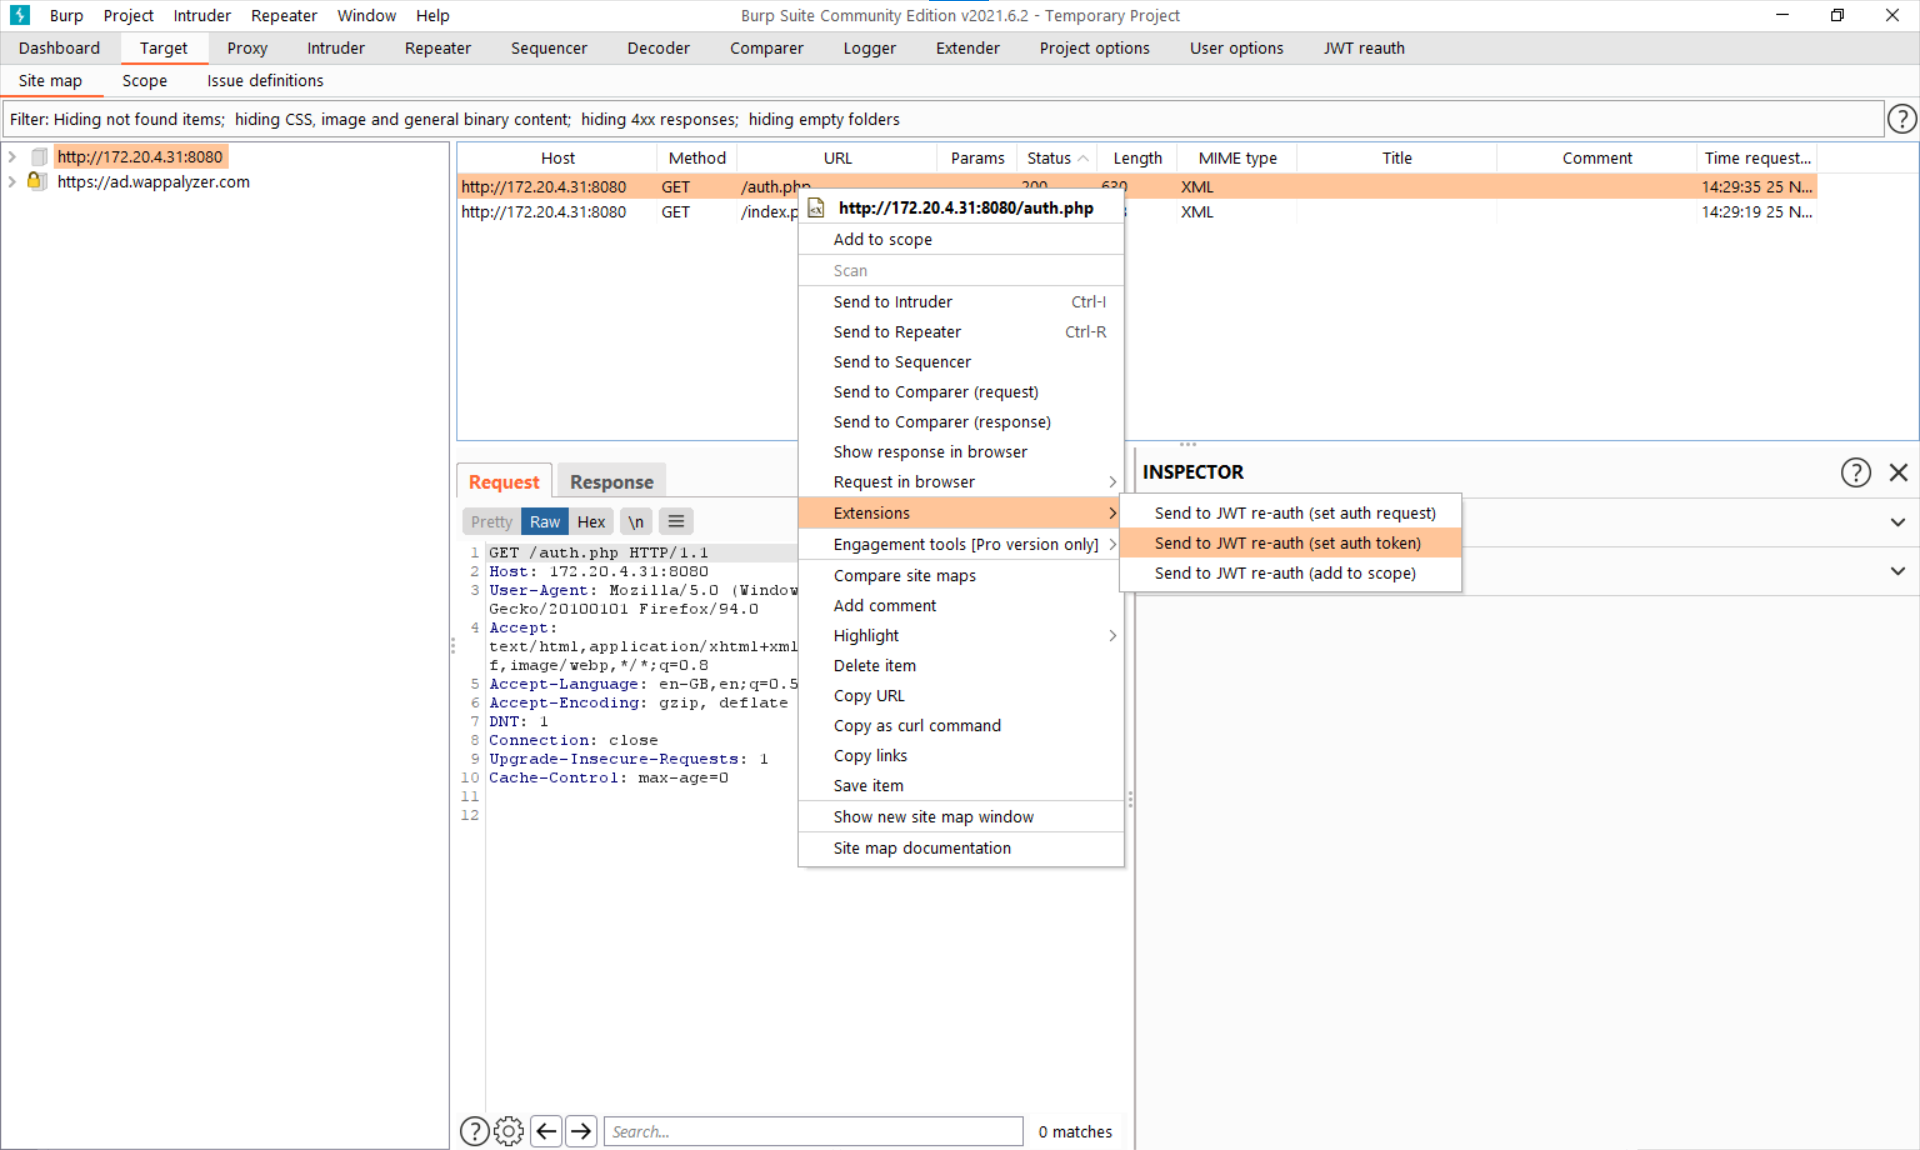 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 keith-amateur/cve-2022-1040
Save the trouble to open the burpsuite...