
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 msanft/cve-2025-55182
PoC exploit for CVE-2025-55182, demonstrating remote code execution in React Server Functions via prototype pollution and a crafted Flight Protocol…
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 adrmxr/kithack
Hacking tools pack & backdoors generator.
 1n7erface/poclist
Vulnerability-specific PoC scripts for discovering and exploiting RCE, SQLi, XXE, SSRF, and unauthorized-access flaws in enterprise web apps and…
 yeswehack/vulnerable-code-snippets
Twitter vulnerable snippets
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 veracode-research/rogue-jndi
A malicious LDAP server for JNDI injection attacks
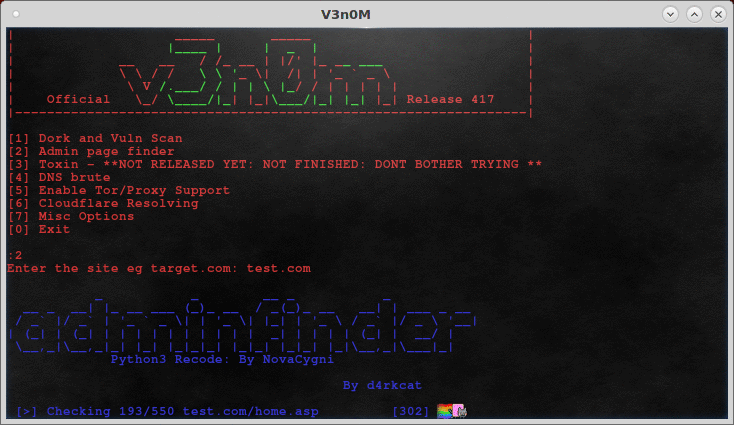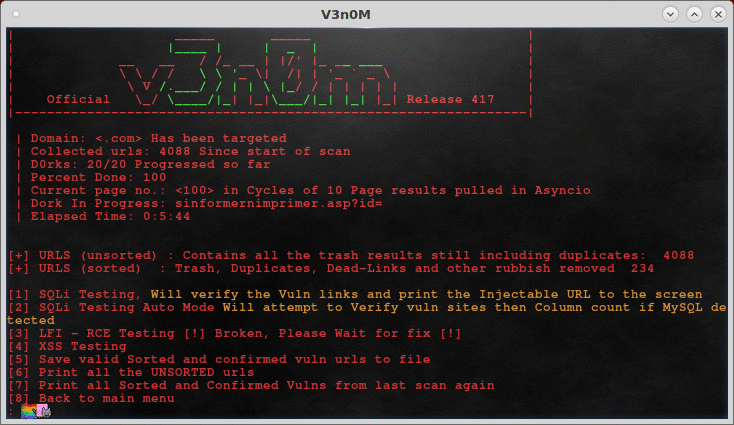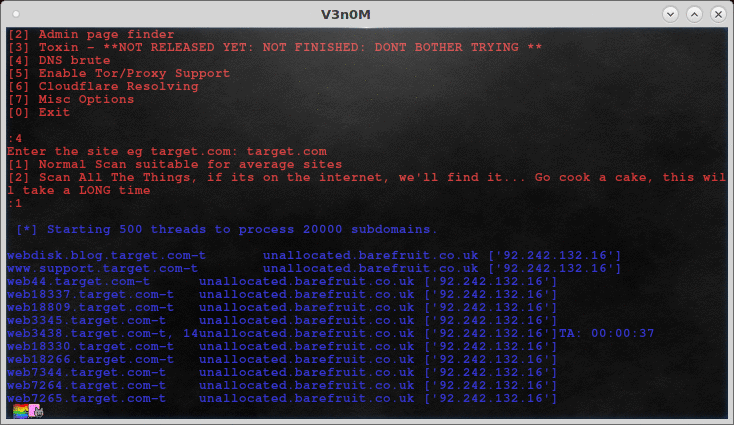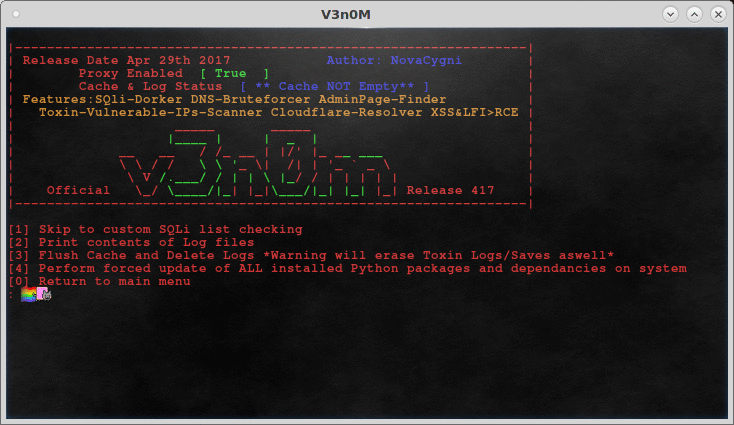 v3n0m-scanner/v3n0m-scanner
Popular Pentesting scanner in Python3.6 for SQLi/XSS/LFI/RFI and other Vulns
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 mubix/shellshocker-pocs
Collection of Proof of Concepts and Potential Targets for #ShellShocker
 wireghoul/htshells
Self contained htaccess shells and attacks








