
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 thewhiteh4t/cve-2020-10977
GitLab 12.9.0 Arbitrary File Read
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 petrusviet/cve-2021-39115
Template Injection in Email Templates leads to code execution on Jira Service Management Server
 sunlight-rim/sqlbit
A script for automatize boolean-based blind SQL injections (MVP).
 smokeintheshell/cve-2023-20198
CVE-2023-20198 Exploit PoC
 34zy/microsoft-office-word-mshtml-remote-code-execution-exploit
Exploits CVE-2021-40444 in Microsoft Office Word to achieve remote code execution through the MSHTML engine by injecting malicious content into a…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 fsecurelabs/n1qlmap
The tool exfiltrates data from Couchbase database by exploiting N1QL injection vulnerabilities.
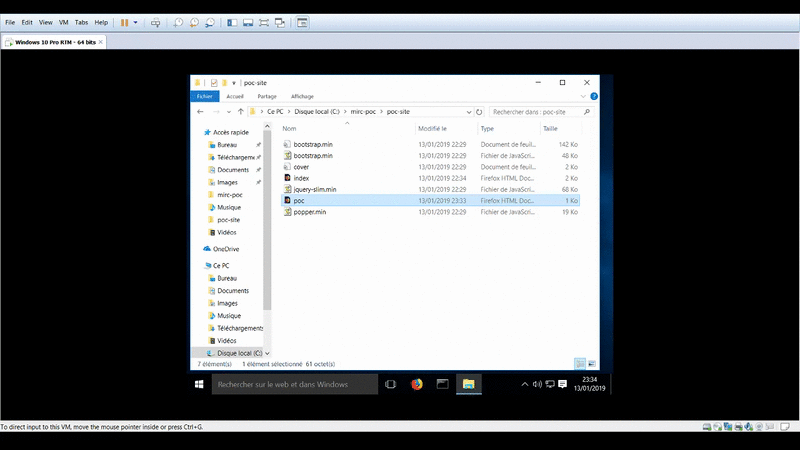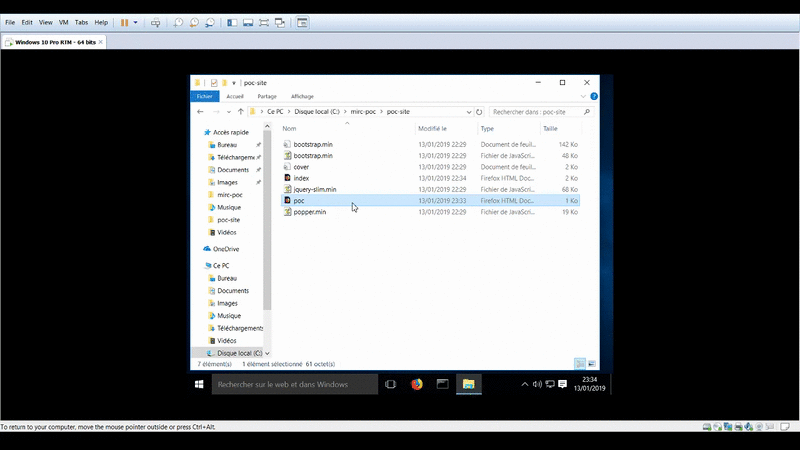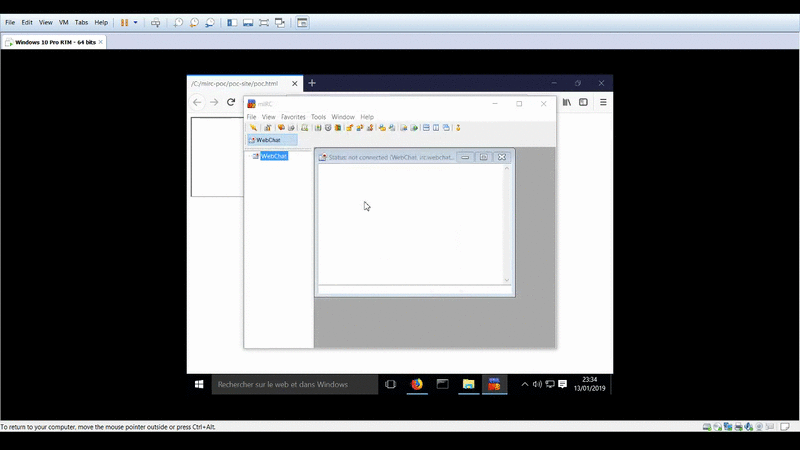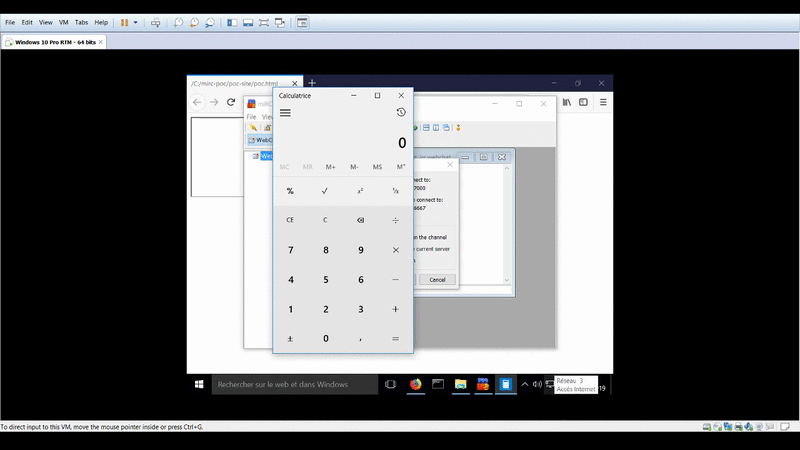 proofofcalc/cve-2019-6453-poc
Proof of calc for CVE-2019-6453
 sfewer-r7/cve-2023-34362
CVE-2023-34362: MOVEit Transfer Unauthenticated RCE
 jiansiting/cve-2019-2725
Exploit for CVE-2019-2725 targeting WebLogic WLS remote code execution vulnerability, enabling unauthenticated attackers to execute arbitrary…
 jas502n/cve-2020-2551
Proof-of-concept exploit for CVE-2020-2551, demonstrating remote code execution in Oracle WebLogic Server via the IIOP protocol. Includes default…
 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 jas502n/jackson-cve-2020-8840
FasterXML/jackson-databind 远程代码执行漏洞
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 horizon3ai/cve-2023-27350
Proof-of-concept exploit for PaperCut CVE-2023-27350, chaining authentication bypass with built-in scripting abuse to achieve remote code execution…
 hdce-inc/cve-2023-38831
CVE-2023-38831 PoC (Proof Of Concept)








