
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 imjdl/cve-2019-11510-poc
Proof-of-concept exploit for CVE-2019-11510 targeting pre-authentication arbitrary file read in Pulse Secure SSL VPN. Enables extraction of sensitive…
 synacktiv/ps4-webkit-exploit-6.xx
Webkit exploit that give arbitrary R/W on 6.XX PS4 firmwares
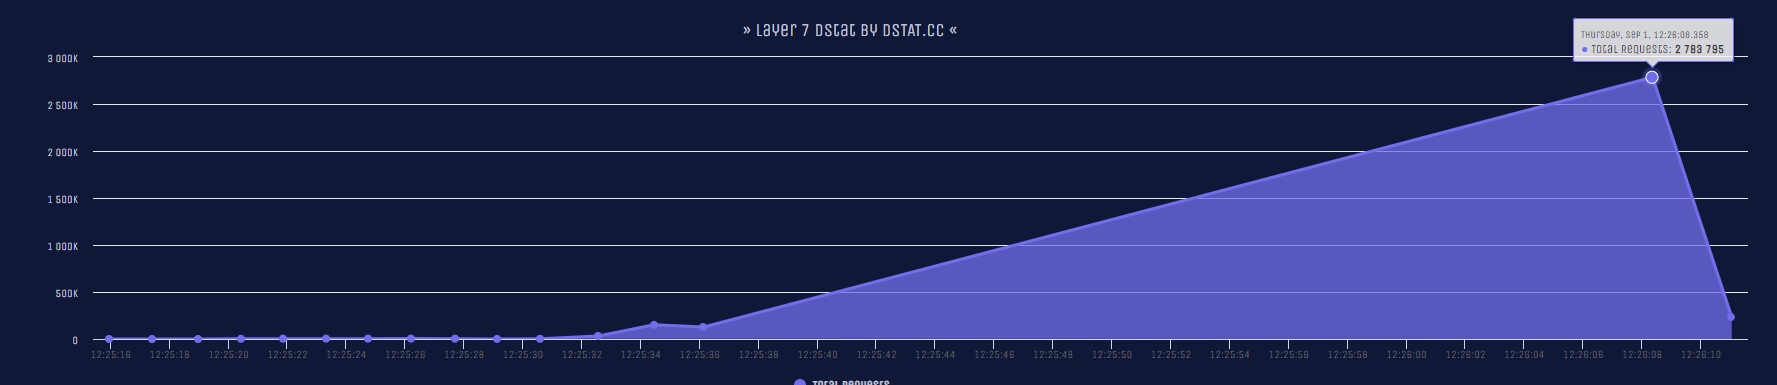 nayumidev/cc-ddos
Một tập lệnh Python để DDOS một trang web bằng phương pháp nhiều phương pháp HTTP Flood, một trang web bình thường chỉ cần 5s để sập hoàn toàn!
 wuhan005/cve-2022-30781
🍵 Gitea repository migration remote command execution exploit.
 pyn3rd/cve-2018-3252
CVE-2018-3252-PoC
 synacktiv/cve-2024-45409
Ruby-SAML / GitLab Authentication Bypass (CVE-2024-45409) exploit
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.
 gh1mau/masta-cve-2026-48907
Single-file Python scanner for CVE-2026-48907 (Joomla JCE Editor RCE). Detects Joomla/JCE, performs intrusive math-verified payload test, supports…
 sherlocksecurity/cve-2022-1388-exploit-poc
PoC for CVE-2022-1388_F5_BIG-IP
 watchtowrlabs/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for CVE-2024-55591, demonstrating authentication bypass in FortiOS management interfaces via WebSocket race condition to…
 hakaioffsec/cve-2025-49113-exploit
Proof of Concept demonstrating Remote Code Execution through insecure deserialization in Roundcube (CVE-2025-49113).
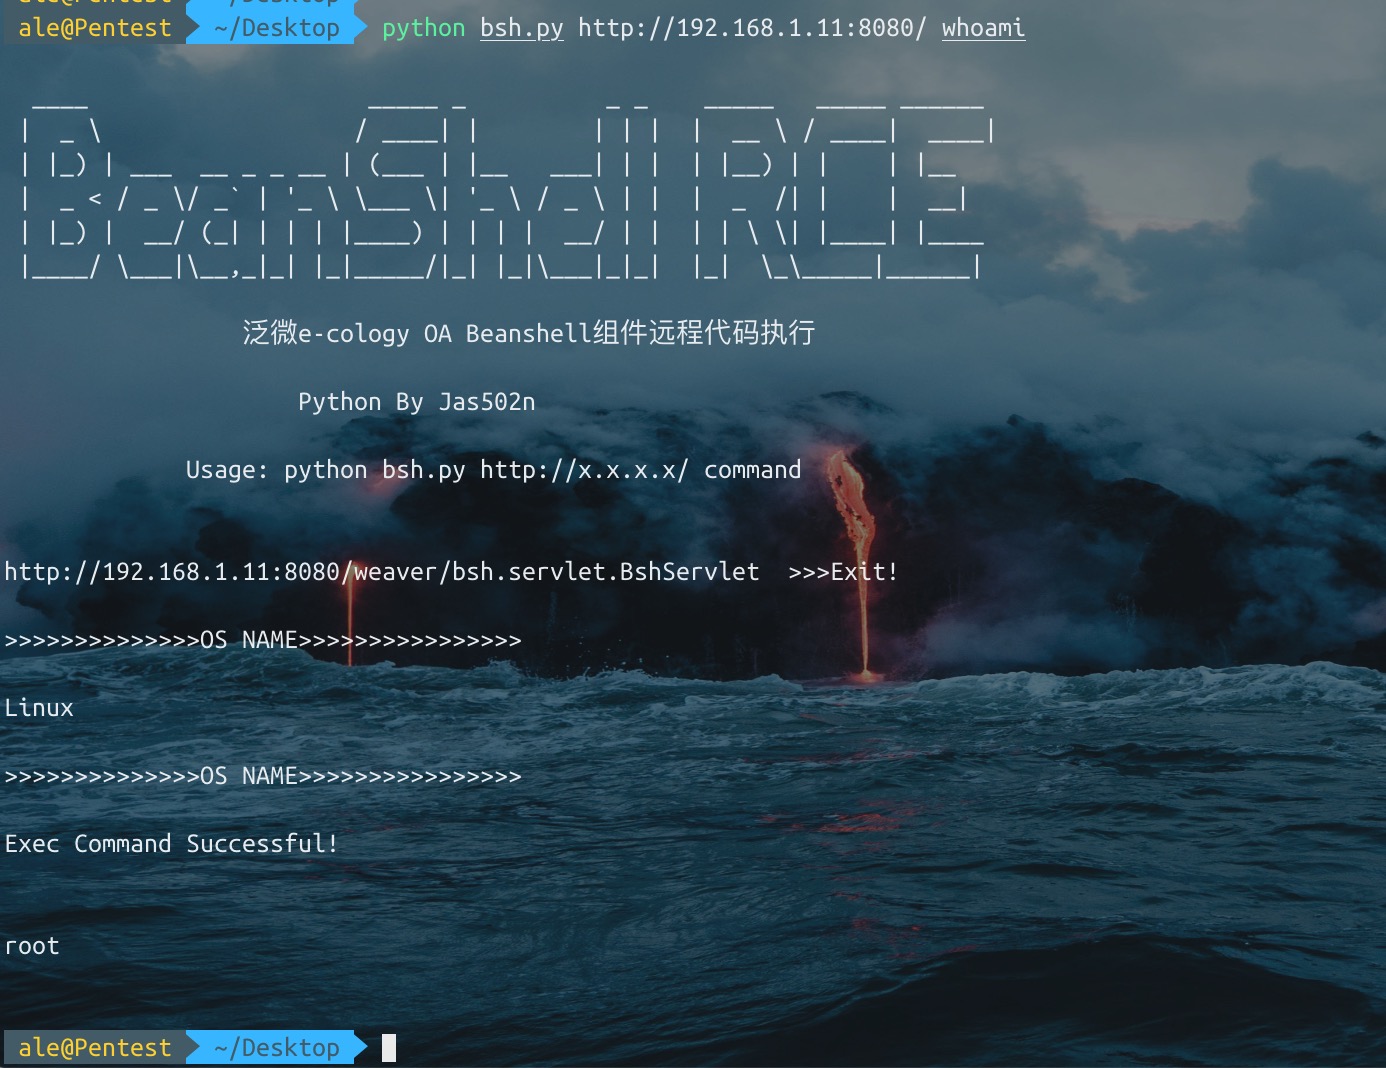 jas502n/e-cology
e-cology OA_Beanshell_RCE
 kaist-hacking/cve-2023-6702
Chrome Renderer 1day RCE via Type Confusion in Async Stack Trace (v8ctf submission)
 caveeroo/cve-2026-111497-wordpress-poc
CVE-2026-111497 RCE PoC for one pinned Docker Official Image for WordPress
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 sourceincite/cve-2021-24085
Proof-of-concept exploit for CVE-2021-24085: CSRF-based elevation of privilege in Microsoft Exchange Server via msExchEcpCanary token forgery,…
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications
 0xf4n9x/cve-2023-0669
CVE-2023-0669 GoAnywhere MFT suffers from a pre-authentication command injection vulnerability in the License Response Servlet due to deserializing…








