
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 mandatoryprogrammer/sonar.js
A framework for identifying and launching exploits against internal network hosts. Works via WebRTC IP enumeration combined with WebSockets and…
 wyatu/cve-2018-20250
exp for https://research.checkpoint.com/extracting-code-execution-from-winrar
 harsh-bothra/securityexplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…
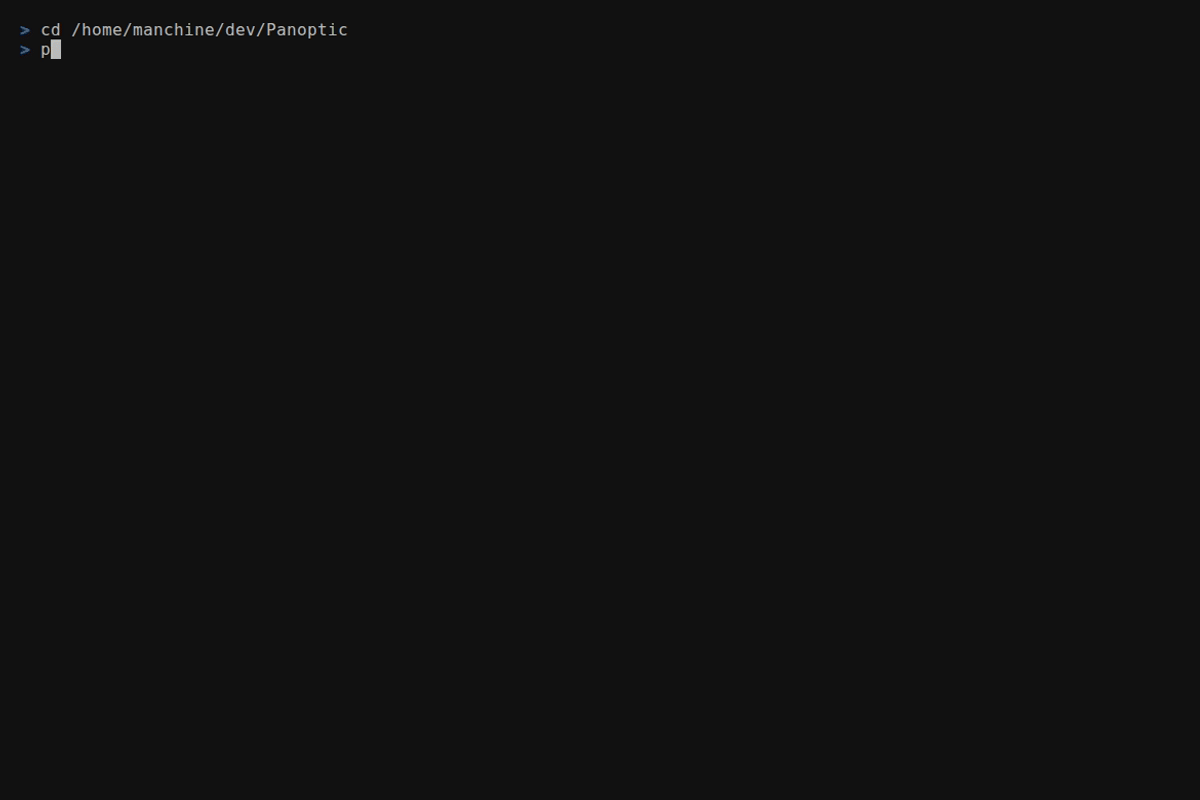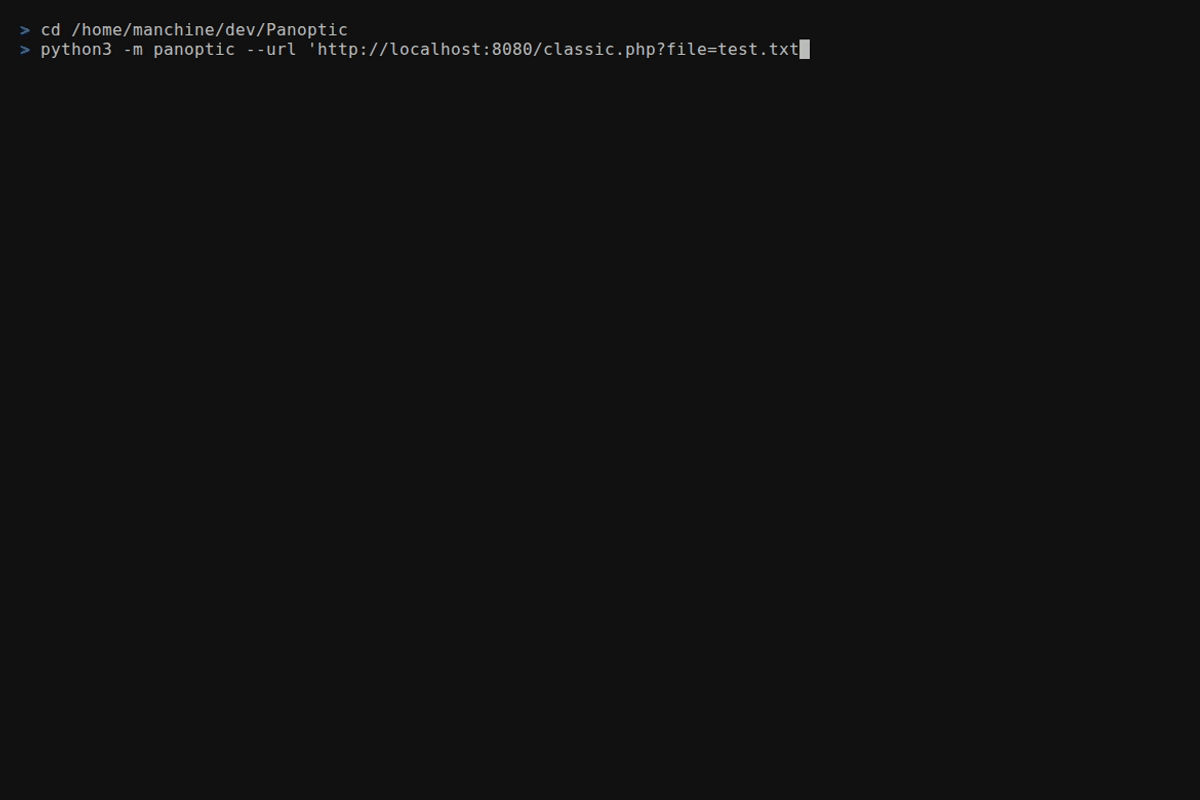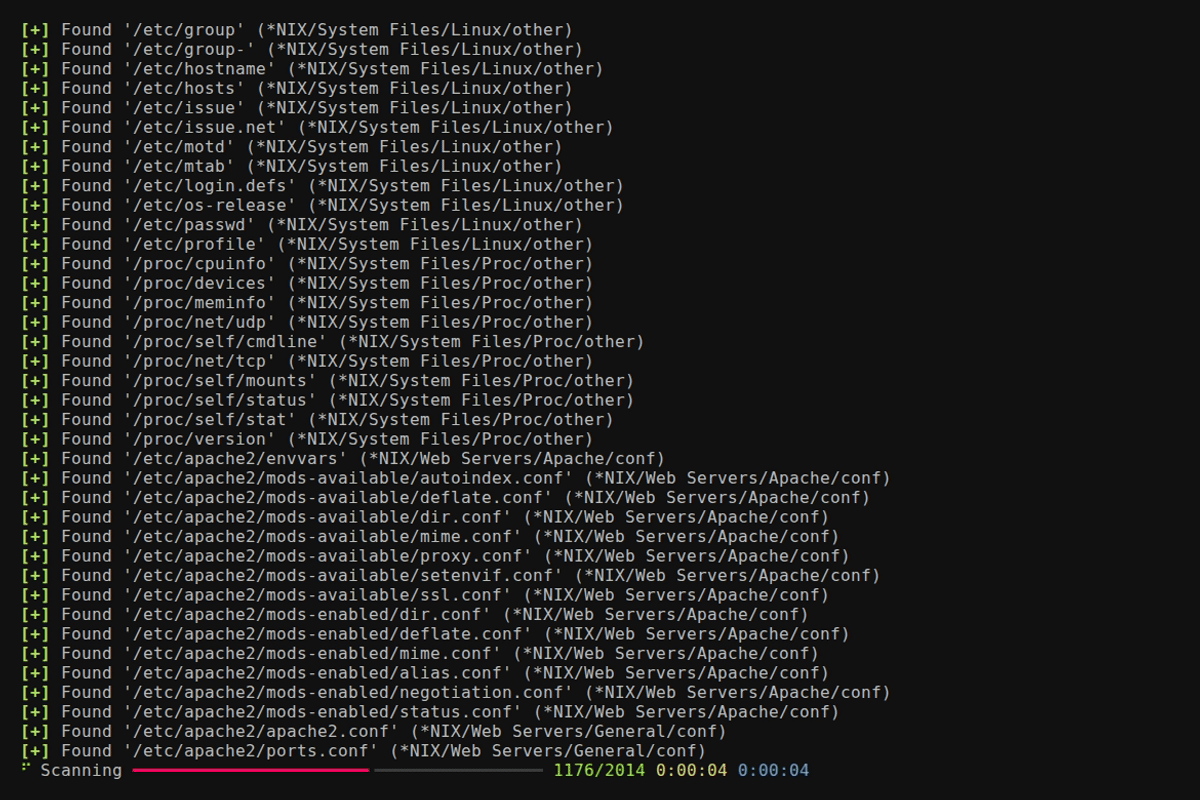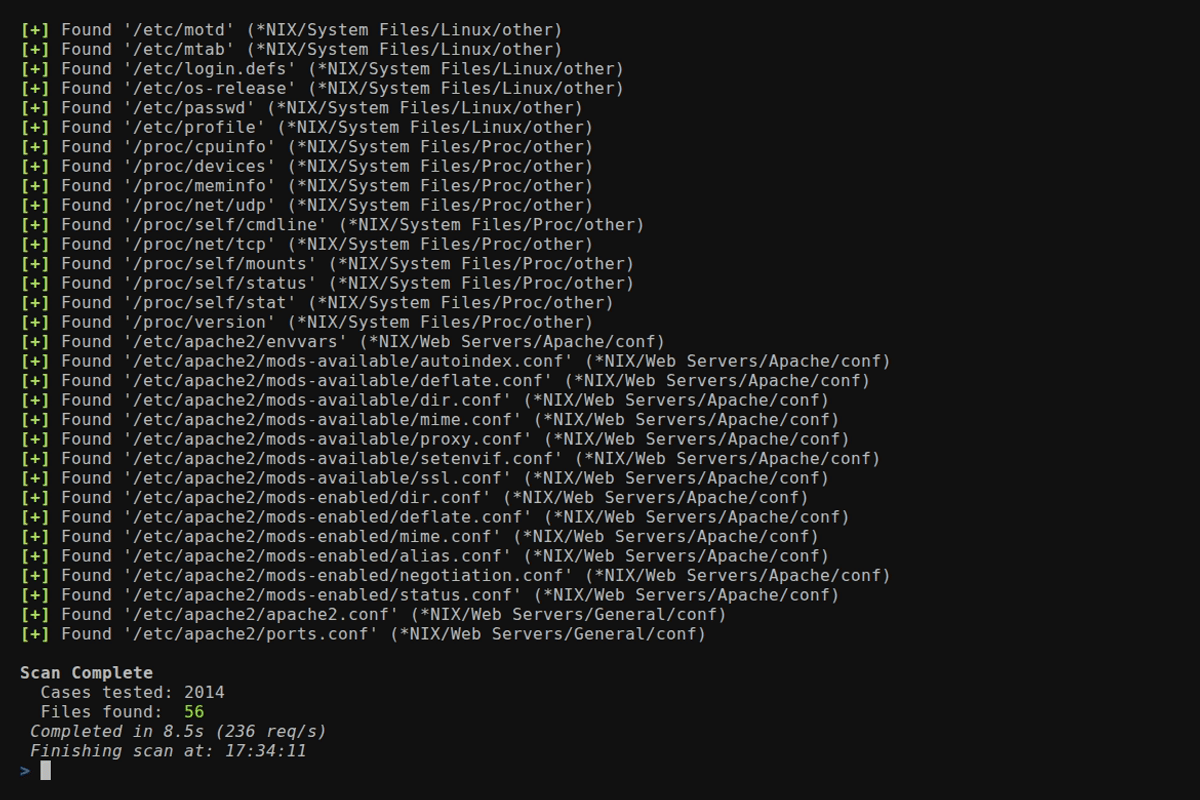 lightos/panoptic
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…
 ktecv2000/proxyshell
Proof-of-concept exploit for Microsoft Exchange Server Remote Code Execution via ACL bypass, privilege escalation, and arbitrary file write…
 star-sg/cve
A collection of proof-of-concept exploit scripts written by the STAR Labs team for various CVEs that they discovered or found by others.
 papamica/waf-checker
Tests your WAF with +160 payloads
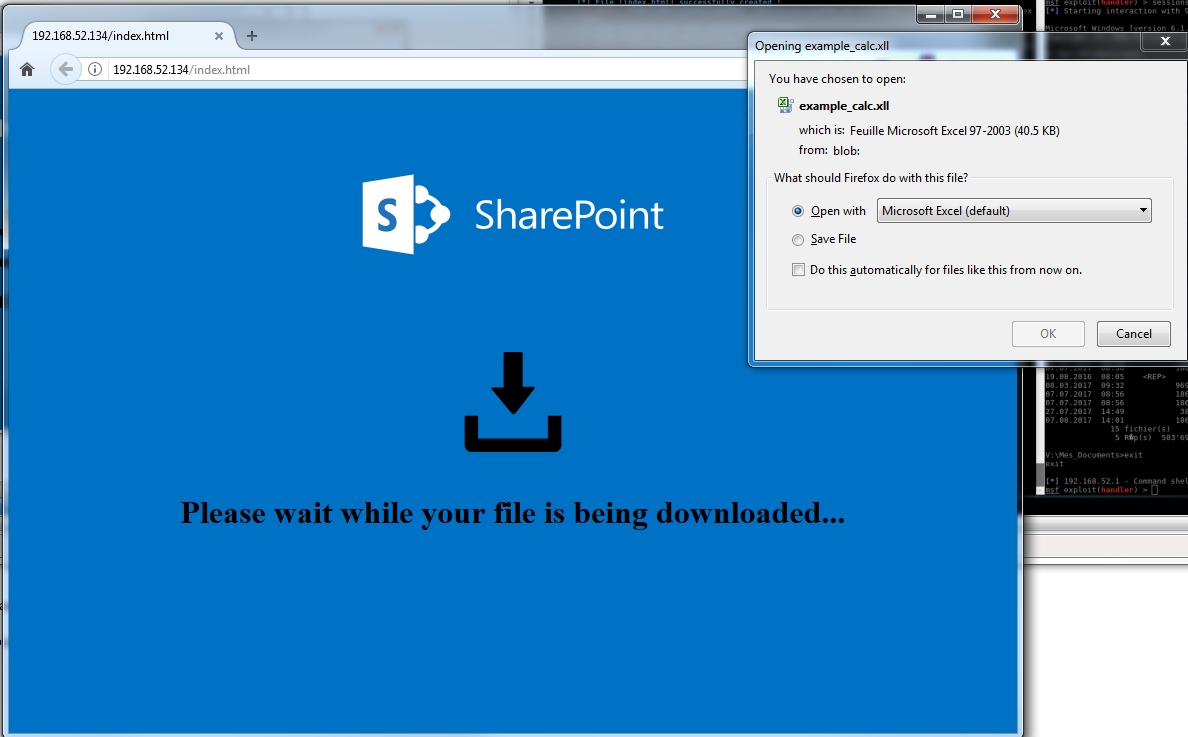 arno0x/embedinhtml
Embed and hide any file in an HTML file
 d4vinci/pyflooder
A http flood python script that could stop a normal website in 10s
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
 rizemon/exploit-writing-for-oswe
Tips on how to write exploit scripts (faster!)
 brannondorsey/dns-rebind-toolkit
A front-end JavaScript toolkit for creating DNS rebinding attacks.
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
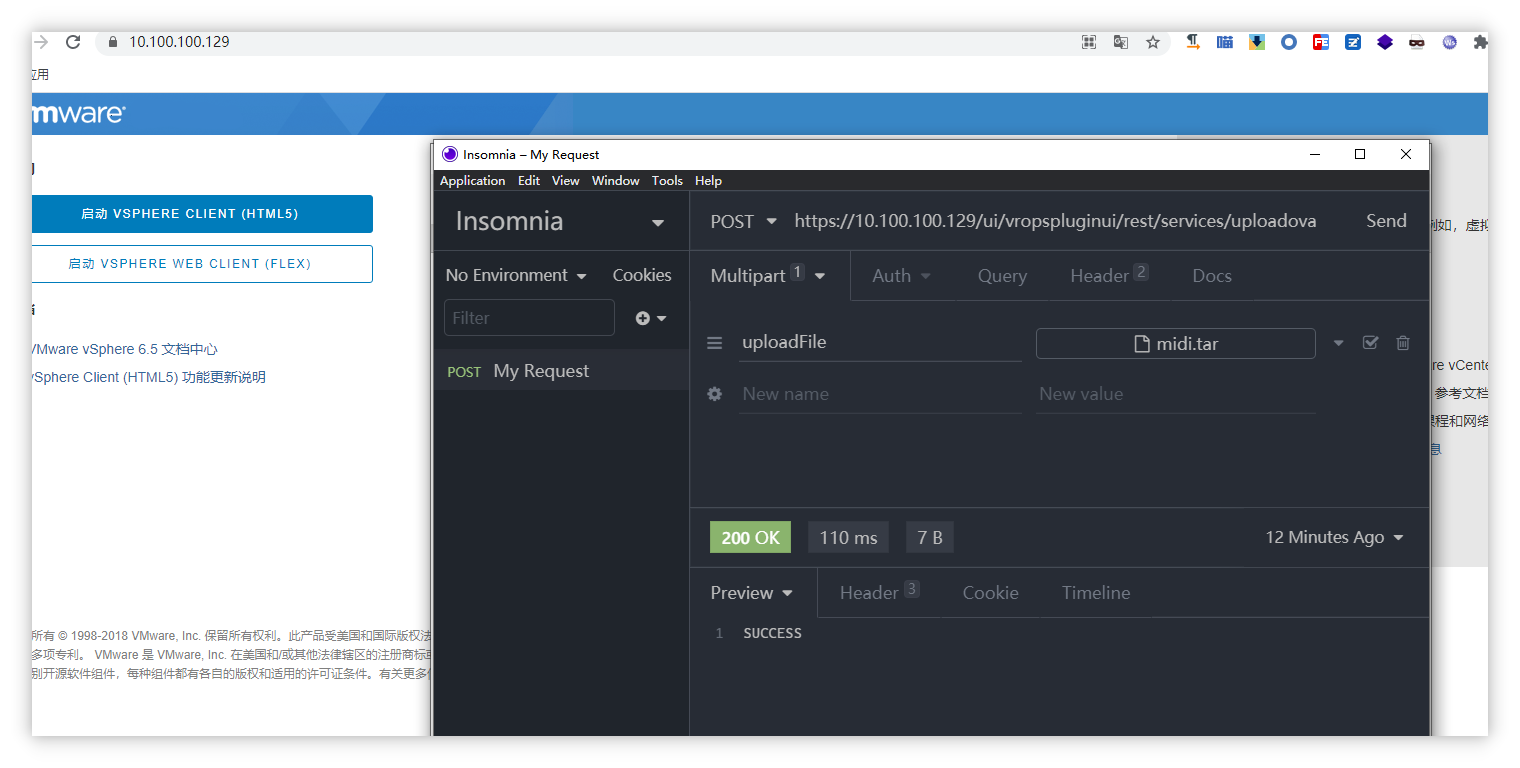 ns-sp4ce/cve-2021-21972
CVE-2021-21972 Exploit
 edr4/xss-bypass-filters
Curated XSS payload collection and filter-bypass cheat sheet: WAF-specific evasion, JS/HTML injection vectors, encoding tricks, DOMPurify and…








